ExfilSquad: A New “Data extortion group” Player Claiming High-Profile Breaches Across the US, UK, and Beyond
August 6, 2026
Overview
ExfilSquad is a newly emerged threat actor in the cybercriminal landscape, claiming responsibility for alleged breaches of 15 high-profile victims across multiple countries as of the time of writing this report. The alleged victims span the United States (9 victims), the United Kingdom (3 victims), Sweden (1 victim), and Nigeria (1 victim). The group maintains a dedicated onion-based Data Leak Site (DLS) where victims are listed alongside ransom deadlines, claimed breach sizes, revenue figures, country of origin, and sample files in .7z format or torrent links as proof of compromise (POC).
Notably, all listed victims share an identical ransom payment deadline of 05.08.2026, suggesting a coordinated and simultaneous extortion campaign rather than a series of independent intrusions.
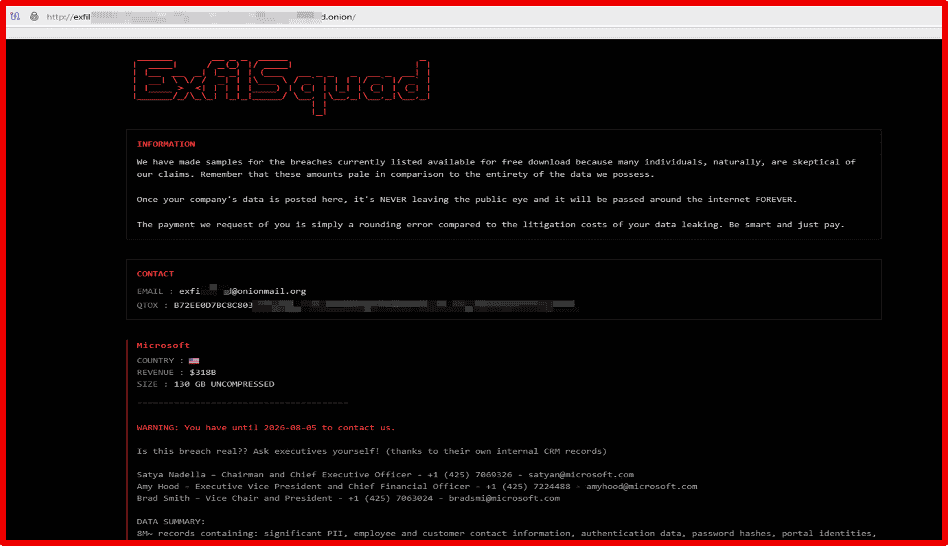
ExfilSquad can be identified and monitored through DarkOwl Vision, as captured in Screenshot below.
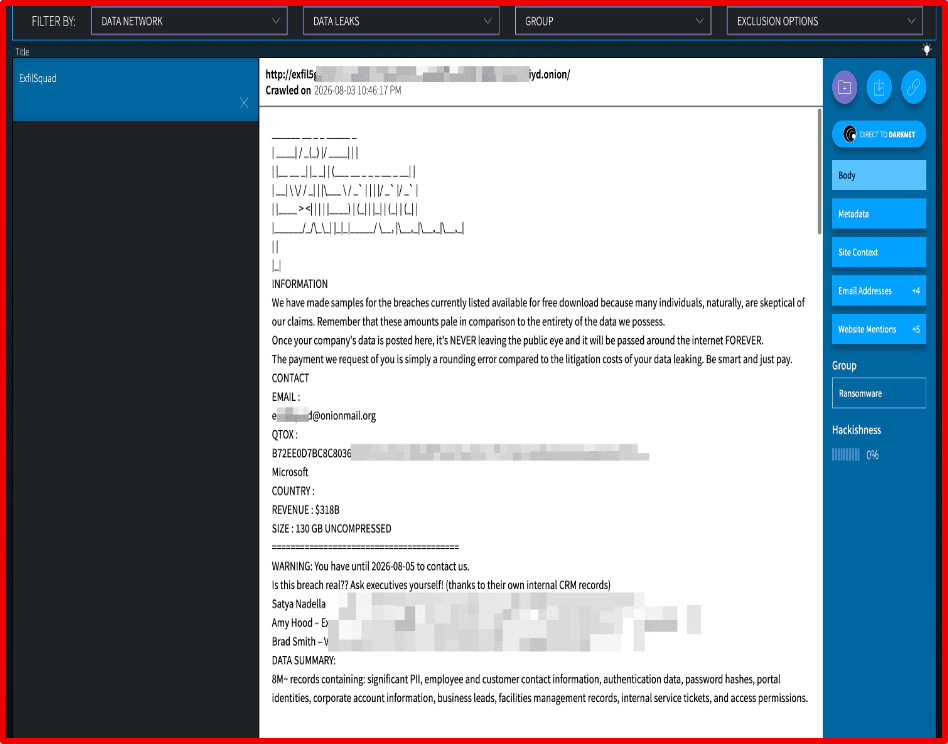
Alleged Victims
The following entities are listed on ExfilSquad’s DLS as of the time of writing:
- Microsoft
- Wesco International
- UK Department for Education (education.gov.uk)
- Police National Legal Database
- Allstate
- TaylorMade & Sun Day Red Golf
- Frontier Airlines
- Zenith Bank Plc
- District of Columbia Public Schools (dcps.dc.gov)
- Newcastle University (ncl.ac.uk)
- Viavi Solutions
- City of Houston (houstontx.gov)
- City of Atlanta (atlantaga.gov)
- Bonava, the Swedish residential real estate development company headquartered in Stockholm, Sweden.
A Confirmed Breach: UK Police National Legal Database
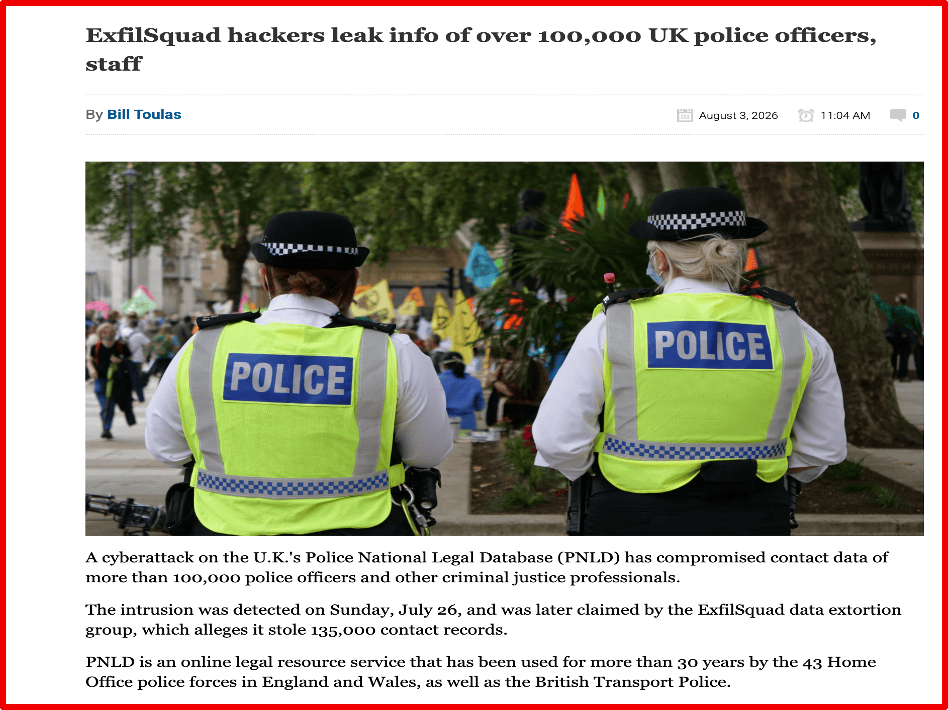
What elevates several of these claims beyond typical unverified dark web listings is that the UK Police National Legal Database (PNLD) has publicly confirmed that police, government, and customer contact information was compromised and published by the ExfilSquad group, with over 100,000 UK police officers and staff affected. This confirmation lends credibility to the group’s broader list of claimed victims and warrants serious consideration by all allegedly affected entities.
Contact Infrastructure
The group listed two contact methods on their DLS, an onionmail and a QTOX ID:
OnionMail — a free, anonymous email service designed for privacy, featuring automatic PGP encryption, native Tor network access (.onion), and requiring no personal data or phone numbers to register.
QTox — a free, open-source, and secure instant messaging and video calling client that uses the decentralized Tox Protocol, featuring end-to-end encryption, zero central servers, and no advertisements.
The use of both OnionMail and qTox reflects a deliberate operational security posture, leveraging decentralized and encrypted communication channels to minimize attribution risk.
Dark Web Forum Activity
Beyond their dedicated DLS, DarkOwl researchers observed an actor operating under the same handle “exfilsquad” promoting two of the alleged breaches — both from the United Kingdom — across two dark web forums: Spear and PwnForums.
Spear Forum
Spear is an English-language dark web forum that emerged in early 2026 and has gained traction among cybercriminal communities as a platform for advertising sensitive data, network access, and geopolitically motivated listings. The forum operates on both a clearnet domain and an onion domain. On July 25, 2026, at 04:06 AM, the actor operating under the handle “exfilsquad” initiated a thread on Spear titled “UK POLICE NATIONAL LEGAL DATABASE”, sharing sample data and a link to their DLS.
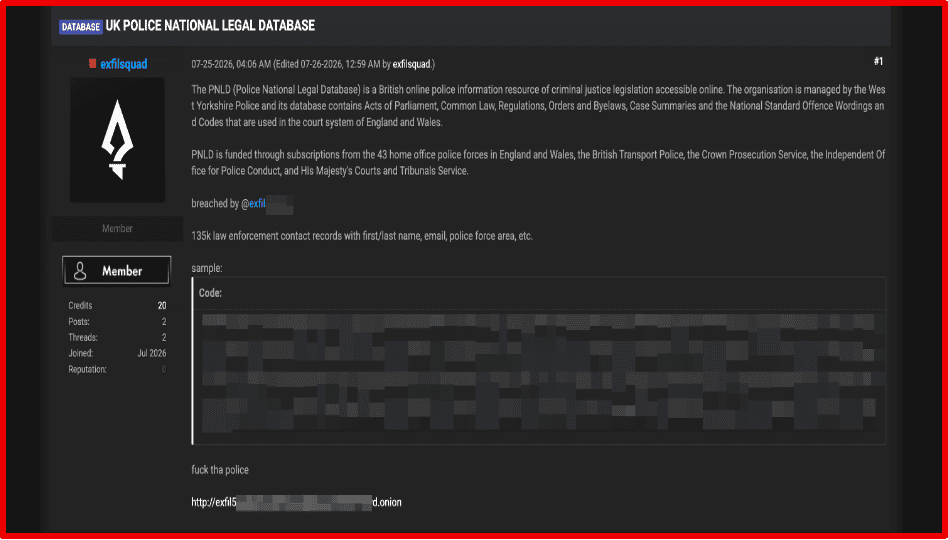
The actor’s claim on Spear forum was crawled the same day on July 25, 2026 and was accessible on DarkOwl ‘s Vision.
Three minutes later, on July 25, 2026, at 04:09 AM, the same actor initiated a second thread titled “UK DEPARTMENT FOR EDUCATION”, again sharing sample data and the same DLS link.
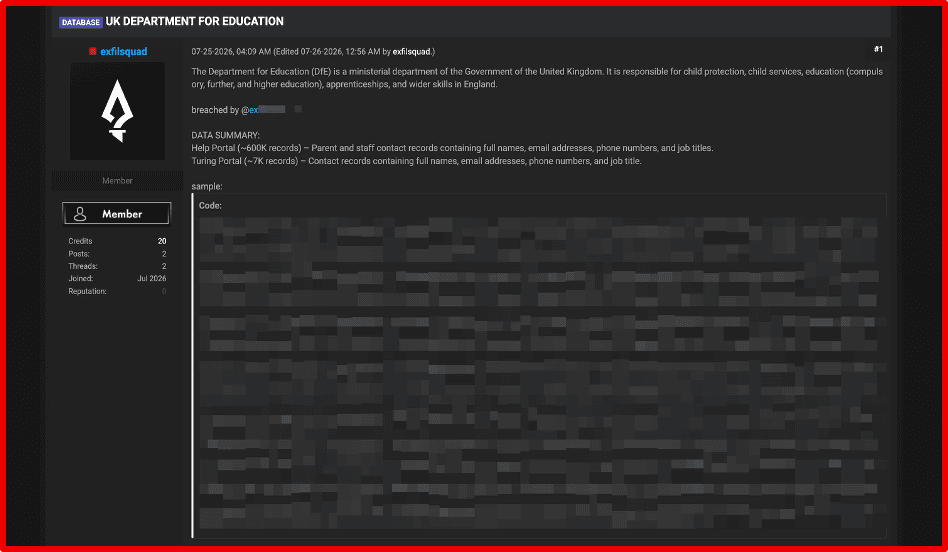
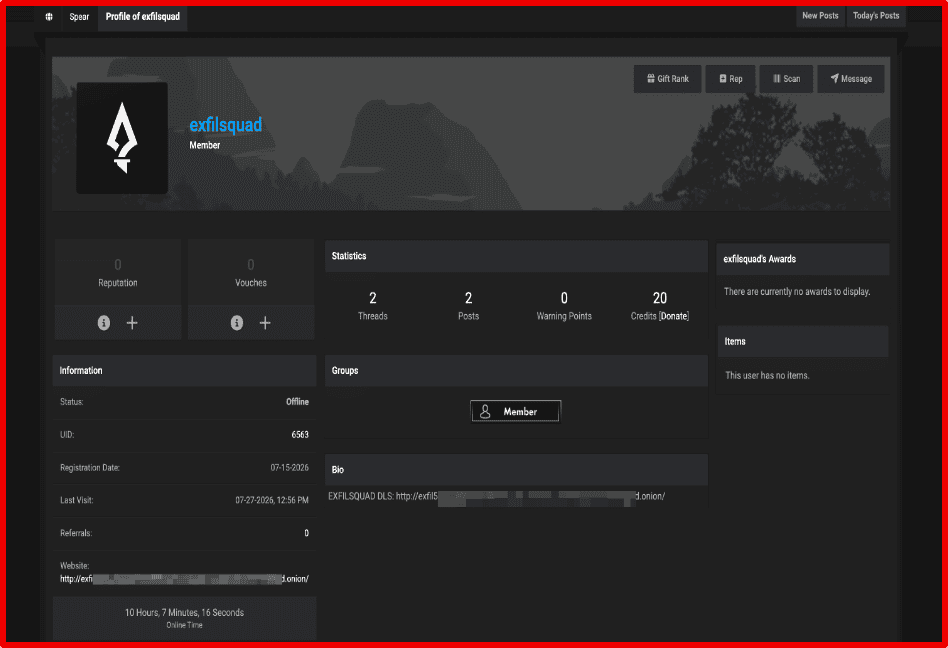
DarkOwl researchers identified that the ExfilSquad account on Spear, joined the forum on July 15, 2026, has initiated 2 threads and 2 posts since joining, and listed the ExfilSquad DLS onion address in the website section of their profile. The account has remained inactive since July 27, 2026, at 12:56 PM as of the time of writing this report.
PwnForums
PwnForums is an English-language cybercriminal forum that serves as a platform for a broad range of illicit activities, including the advertisement and sale of stolen databases, network access, and sensitive government and military data. The forum operates on both a clearnet domain and an onion domain.
On July 25, 2026, at 02:56 AM, the actor operating under the handle “exfilsquad” initiated a thread on PwnForums titled “UK POLICE NATIONAL LEGAL DATABASE”, sharing sample data and a link to the ExfilSquad DLS.
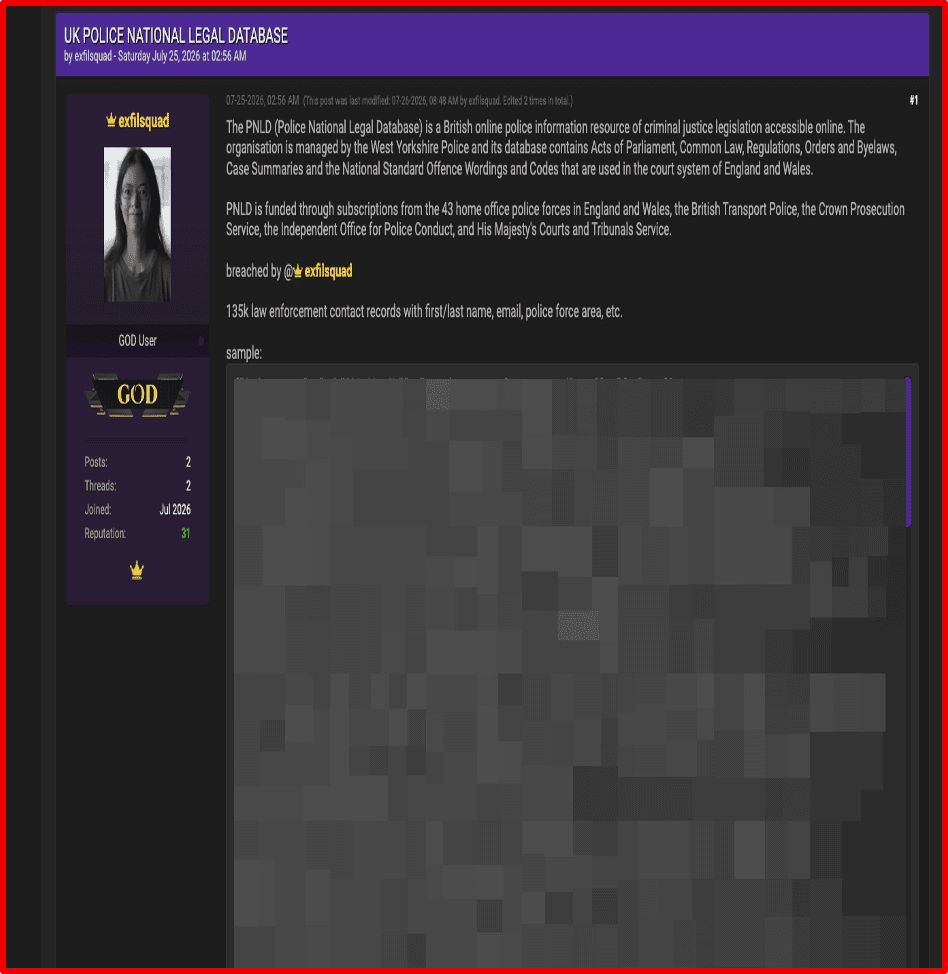
The actor’s claim on Pwnforums was crawled the same day on July 25, 2026, and was accessible on DarkOwl ‘s Vision.
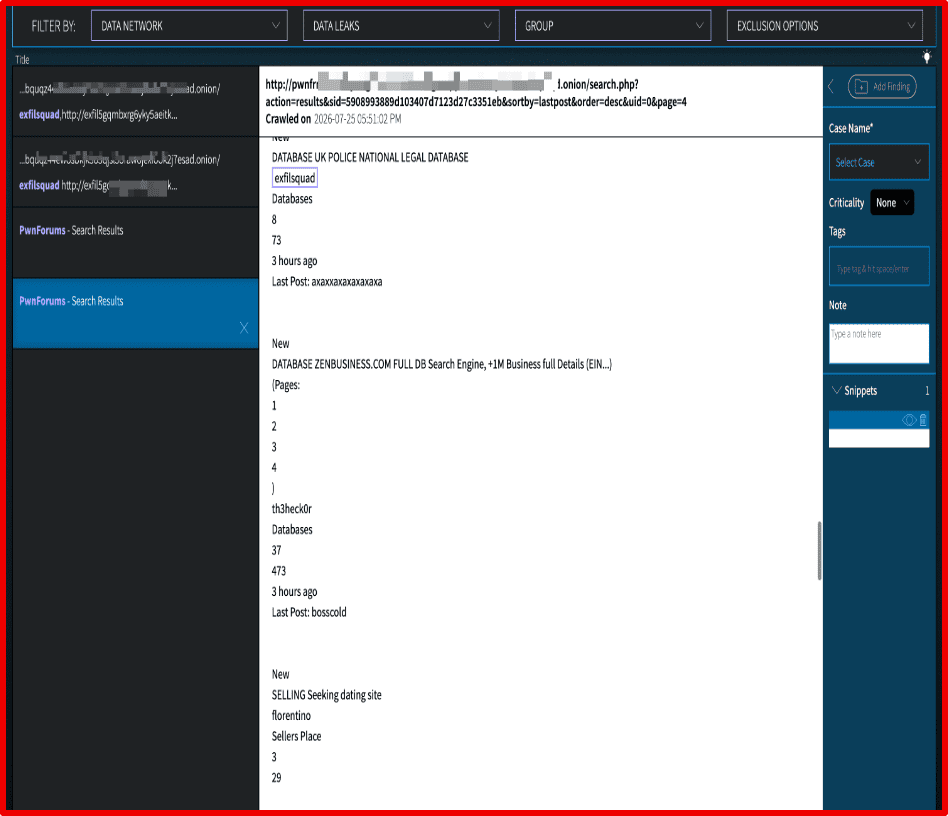
On July 25, 2026, at 03:41 AM, the same actor initiated a second thread titled “UK DEPARTMENT FOR EDUCATION”, sharing sample data, details of the alleged breach, and the onion address of their DLS.
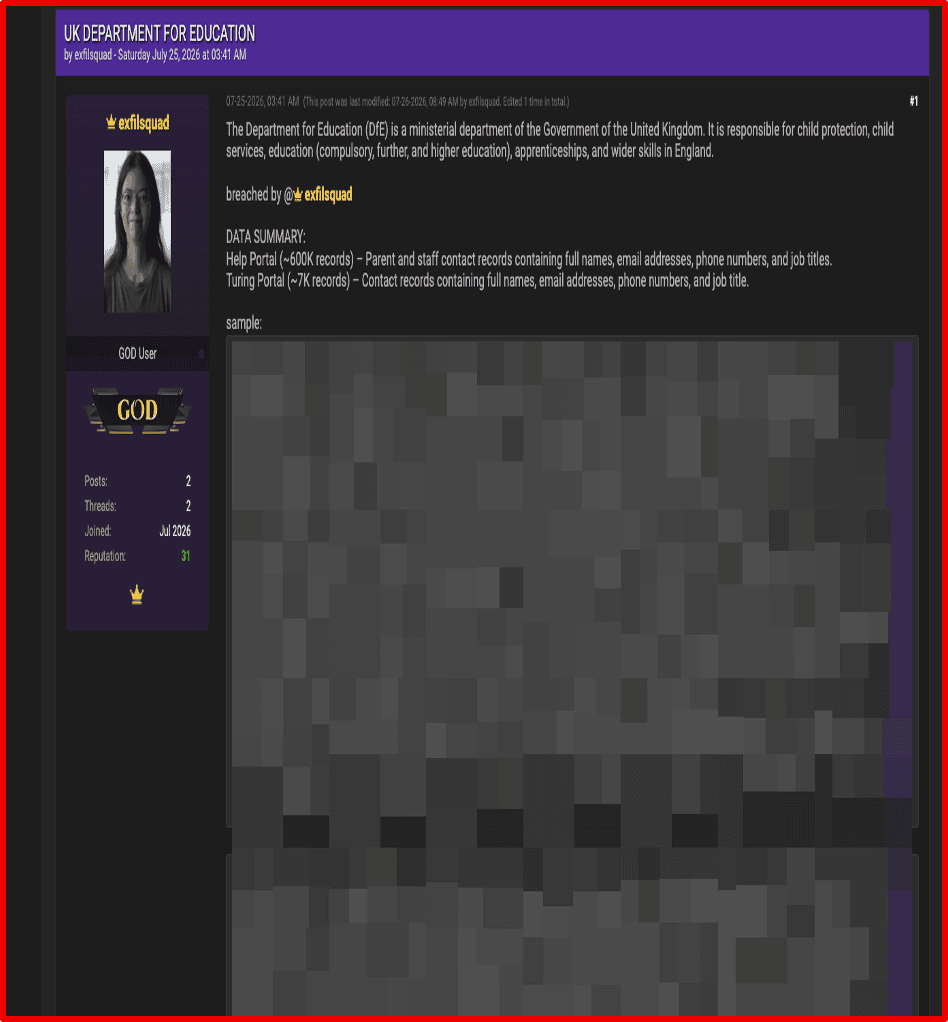
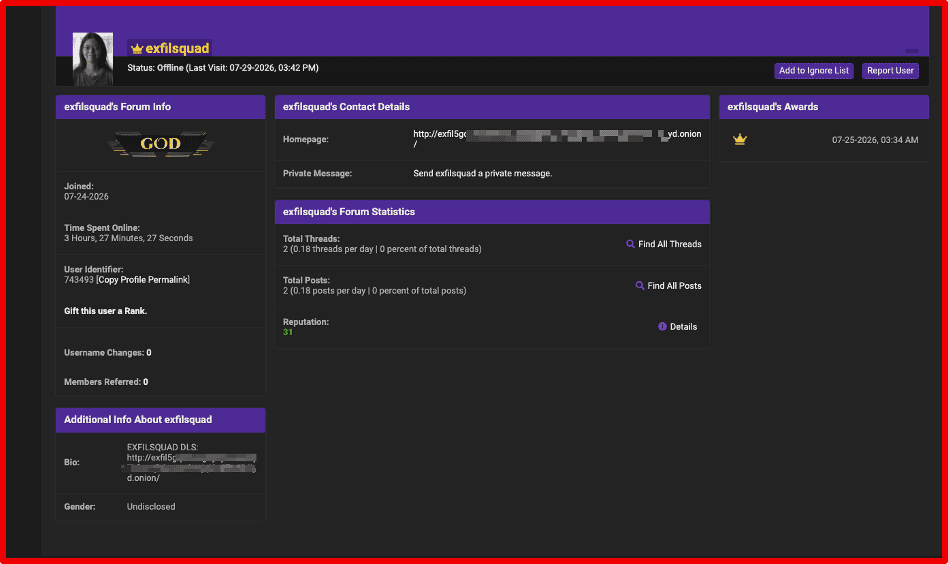
DarkOwl researchers identified that the ExfilSquad account on PwnForums, joined the forum on July 24, 2026, has initiated 2 threads and 2 posts since joining, and listed the ExfilSquad onion address in the Homepage section of their profile.
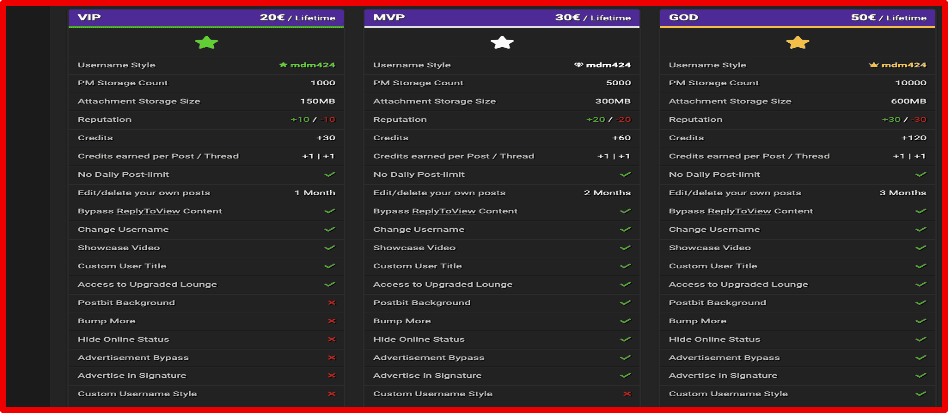
Notably, the actor holds a GOD member status on PwnForums — a paid membership tier available for €50 lifetime, which grants the holder +30 reputation, +120 credits, the ability to edit and delete their own posts for 3 months, and additional forum features.
Assessment
ExfilSquad represents a notable new entrant in the data extortion landscape, distinguishing itself through a simultaneously broad victim portfolio, a confirmed breach of a sensitive law enforcement database, and active cross-platform promotion across multiple dark web forums. The group’s operational security posture — leveraging OnionMail, qTox, and a dedicated onion DLS — reflects a degree of technical sophistication consistent with an actor seeking to establish credibility and longevity within the cybercriminal ecosystem.
The confirmation by the UK Police National Legal Database of a genuine compromise lends material weight to ExfilSquad’s broader claims and warrants urgent attention from all allegedly affected organizations. DarkOwl will continue to monitor ExfilSquad’s activity across dark web and open-source channels as the situation develops.
DarkOwl does not endorse, promote, or amplify the content of any threat actors referenced herein. The authenticity of all advertised breach claims referenced in this report, beyond those independently confirmed by affected entities, has not been verified by DarkOwl.


