FBI Allegedly Hacked by ShinyHunters
September 25, 2026
Introduction
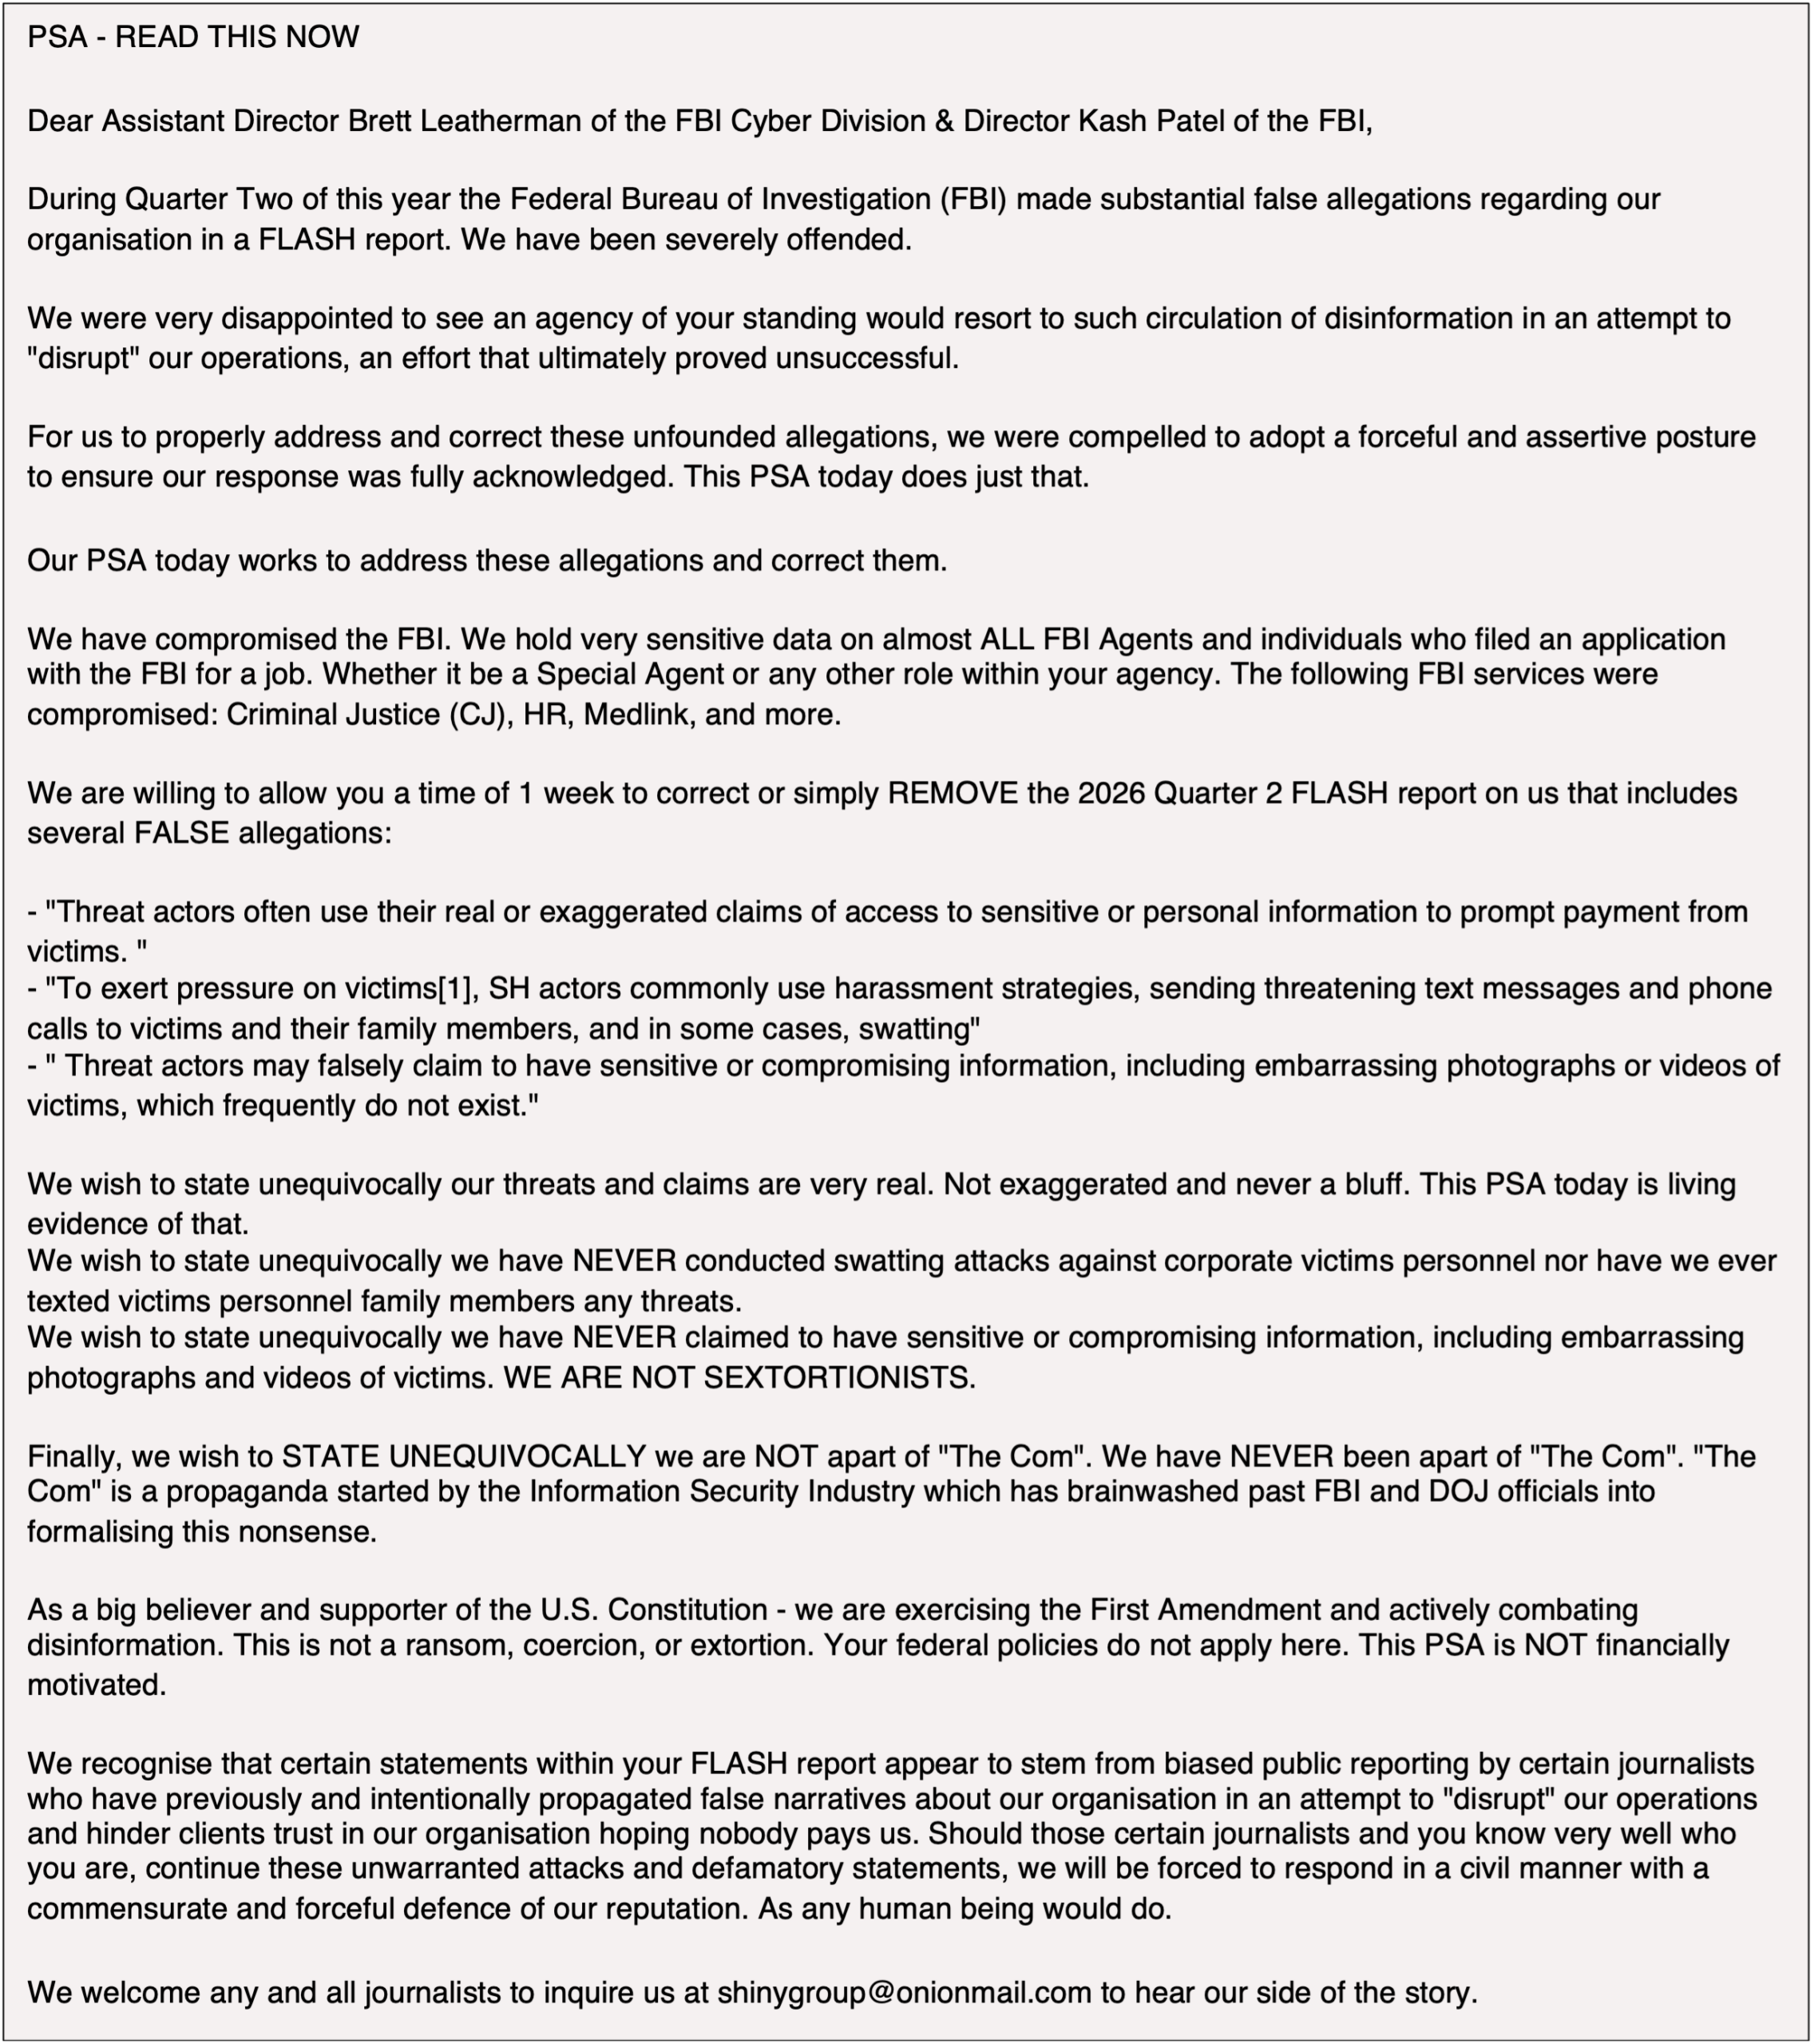
On 22 September the group ShinyHunters announced on their leak site they had accessed data from the FBI and that they would release this in a week if the FBI did not negotiate. They claimed that they had information on around 38,000 FBI staff. The post claims “We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job”.
The FBI have announced they are actively investigating the allegations.
Who are ShinyHunters?
ShinyHunters is thought to be a financially motivated data-theft and extortion group that has been active since 2019. The name comes from “shiny” Pokémon. The group do not deploy ransomware, its model is to steal large datasets, then extort the victim or sell and leak the data on both their leak site and on popular darkweb forums such as BreachForums, which they are also reported to be the admins of.
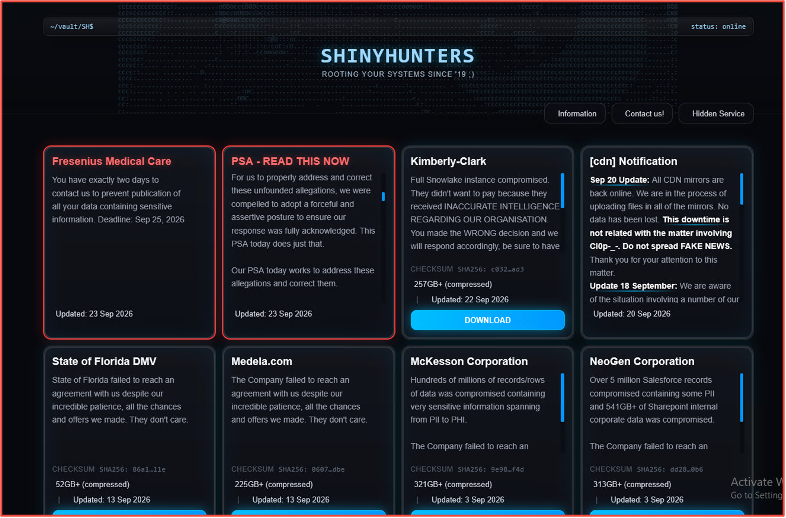
The group have been particularly active in the last 12 months, although they have successfully breached many large-scale companies since they emerged in 2019. In their early period they conducted mass database theft and sales on RaidForums and later BreachForums. Victims included Tokopedia, Wattpad, Microsoft’s GitHub repos, Nitro PDF and AT&T. In 2024 the group were linked to the Snowflake customer-tenant thefts, including Ticketmaster, Santander and a second AT&T breach, plus PowerSchool.
In 2025 the group moved to large-scale campaigns against SaaS platforms, mainly Salesforce, along with Oracle PeopleSoft and third-party integrations. Victims included Qantas, Kering/Gucci, the European Commission and several Ivy League universities. The group maintain a darkweb leak site where they make the stolen data available, usually providing a timeline in which the victim has a chance to negotiate and pay the group to prevent the data being shared before sharing it in full.
In 2026 victims have included Panera, Harvard/UPenn, Rockstar Games, McGraw-Hill, and Canvas/Instructure. The infrastructure attack led to an FBI IC3 advisory in May. The group claim that their recent targeting of the FBI is in reaction to this advisory which they stated they were deeply offended by.
As well as this attack the group have also claimed to have breached rival Cl0p’s leak site through a Grav CMS file-upload flaw and defaced it. It’s demanding an eight-figure sum and threatening to expose Cl0p’s paying victims, which could mean a second round of extortion for them.
How They Attack
The group are reported to use several different methods to target victims. One of the main techniques used is Voice phishing where callers pose as IT support and steer staff to lookalike SSO pages (Okta, Entra). An operator will then relay the stolen credentials and MFA codes to the real login page in real time. Another technique they have used which has been successful against multiple victims is exploitation of Salesforce Experience Cloud where they conduct scans for misconfigured guest-user profiles with too many API permissions, using a modified AuraInspector tool. They have also stolen tokens from integrators’ GitHub environments, which then gives access to many of their customers’ environments at once. As well as this they use their dark web leak site to pressure victims into paying to avoid their data being shared.
Affiliations
The group are reported to have overlaps with Scattered Spider and Lapsus$ under the “Scattered Lapsus$ Hunters” (SLSH) banner, which is assessed to be part of the wider “The Com” ecosystem. Although the group in their PSA to the FBI deny any affiliation with the COM.
What happened?
Shiny Hunters announced on their leak site, in what they described as a PSA, that they had stolen information from the FBI recruitment website and were able to obtain data relating to 38,000 members of staff and potential recruits. They claimed that they had agent’s names, role, badge number, home address, phone numbers and spouse information.
It was further reported that the fbi.careers.gov website briefly included a defacement message stating that the site had been seized showing the ShinyHunters name and the Pokémon character associated with the name. This appears to mimic the FBI seizure site notices which have appeared on many darkweb sites following law enforcement action, including BreachForums which is linked to Shiny Hunters.
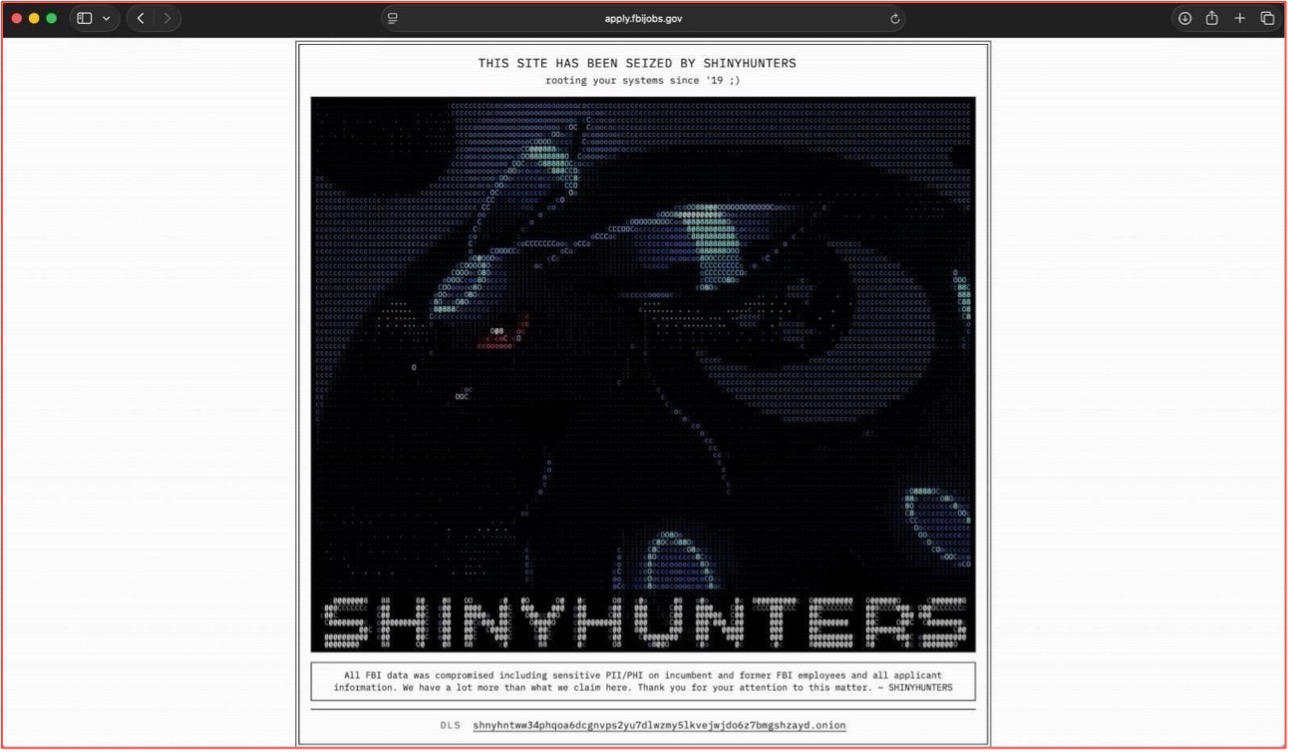
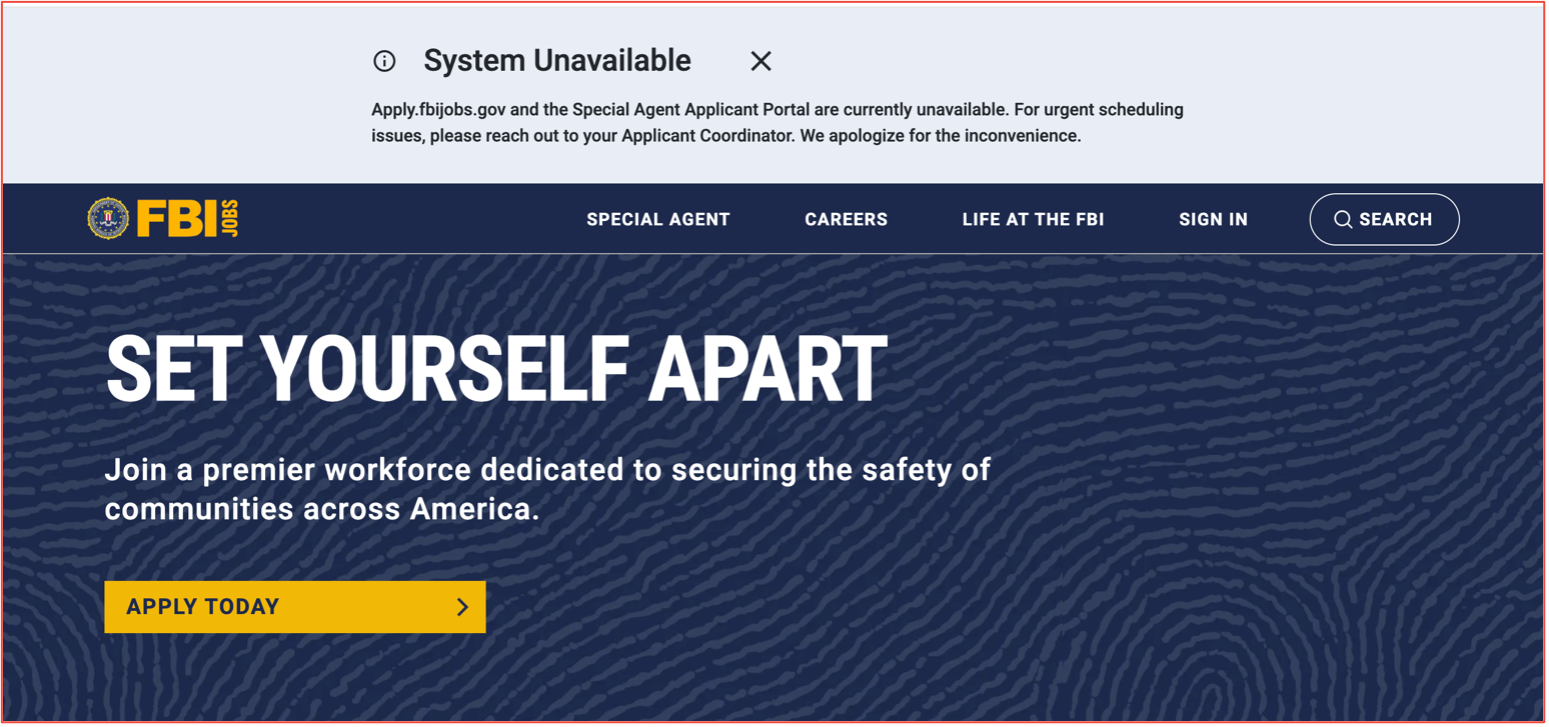
According to The Register, a ShinyHunters spokesperson said the group exploited a new Oracle PeopleSoft zero-day to gain remote code execution and deface the FBI’s jobs website with a “This site has been seized by ShinyHunters” banner. The site the displayed a scheduled maintenance message, which was updated to say that the system is currently unavailable.
The PSA, which was shared to their leak site, addressed the Assistant Director of the FBI Cyber Division and the Director directly. The message stated that they had taken action against the FBI due to “false allegations” made by the FBI in relation to the group in a FLASH report. They stated that they were “severely offended” by these allegations. The announcement went on to state the exact accusations in the report that they were not happy with. They seemed particularly annoyed that the FBI had advised victims not to pay. They requested that this report be removed.
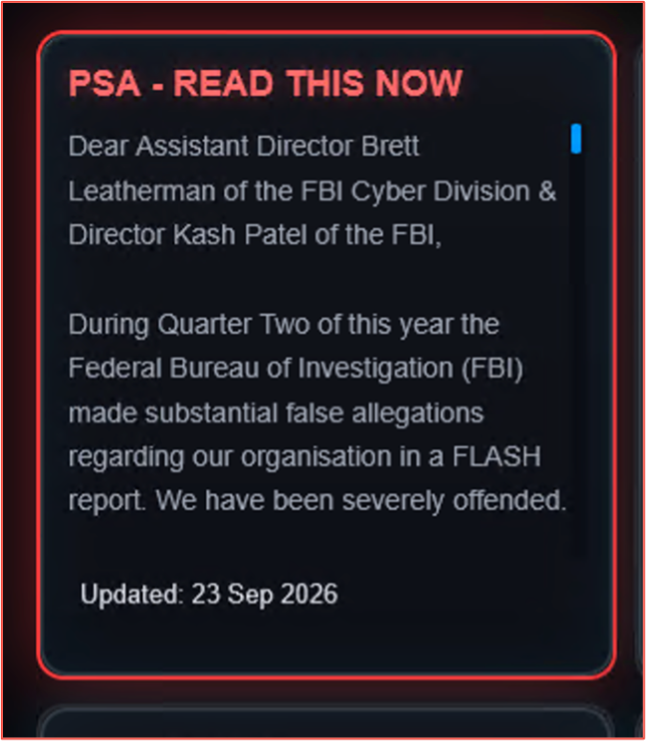
The full version of their PSA is shown below.
The message also encouraged journalists to reach out to the group direct. From reporting it appears that they group have shared sample data with journalists which they stated appeared to be legitimate.
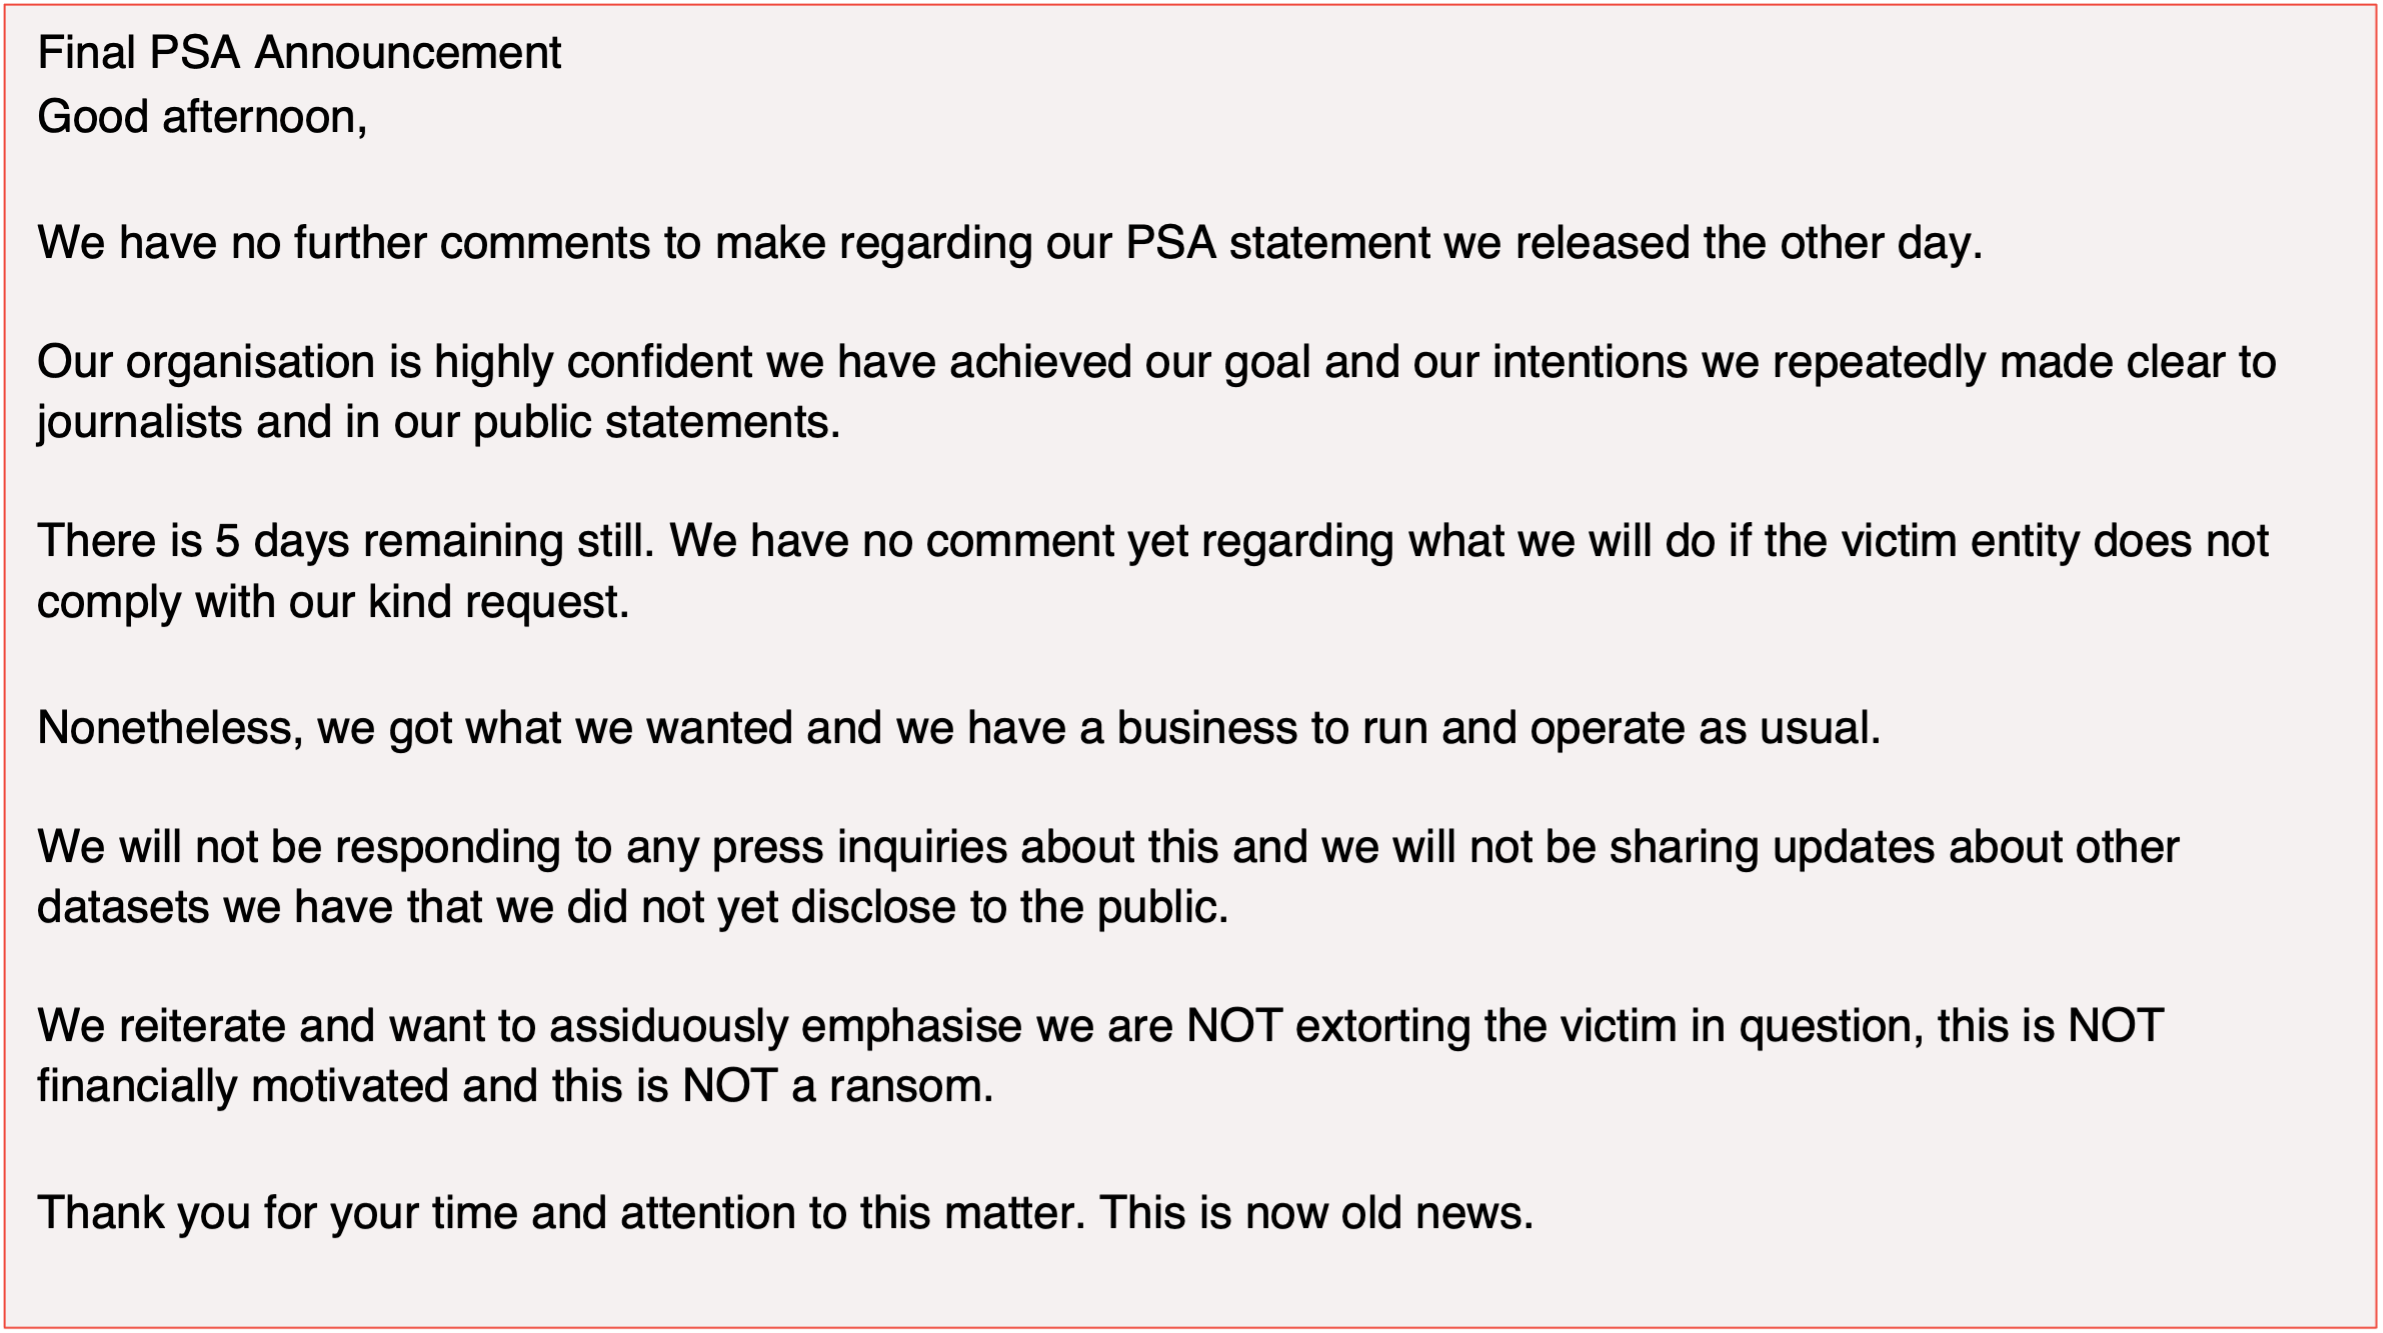
On September 24 the group shared a further message on their site which they claimed was a “final statement re PSA.”
In this message they indicated that they are not extorting the FBI and are not requesting money. It appears their main motivation is for the FBI to remove the FLASH directive that they had previously issued. The group also stated that they would no longer deal with any press enquiries relating to this matter and that there were 5 days left for the FBI to react and they would not state what they would do at the end of this period. They would continue other operations as usual.
The full statement can be seen below:
Conclusion
If this data was obtained, this represents a serious breach of FBI personnel data which could be used for targeting purposes. This appears to be an escalation in activity for the group who have previously targeted organizations for financial reasons, whereas they claim that this was not financially motivated.
The reasoning for targeting also highlights that they group monitor information that is shared about them and take issue with some of the analysis that has been conducted. Targeting the FBI could have serious ramifications for the group, with some members having already been subject to prosecution, the group were already on the radar of law enforcement.
It remains to be seen if the data will be released at the end of the 5 day timeline, DarkOwl will continue to monitor for updates.
Keep up with the latest. Follow us on LinkedIn.


