NoName057(16) Telegram Activity Assessment
November 5, 2026
NoName057(16) is a pro-Russian hacktivist group that conducts coordinated cyberattacks against countries and organizations supporting Ukraine. They are very active on Telegram where they often post claims of DDoS (Denial of Service) attacks on their victims. The group formed in March 2022, shortly after Russia’s full-scale invasion of Ukraine. They are known to target government websites, financial institutions, transport hubs, and media outlets in Ukraine, the US, Taiwan, and European NATO countries.
They form a collective of other hacktivist groups supporting Russia and often share posts from other groups as well as appearing in other group’s posts as supporting their efforts. Unlike traditional centralized hacker groups, NoName057(16) recruits volunteer supporters through messaging apps like Telegram. Volunteers download a proprietary crowd-sourced attack tool called DDoSia onto their computers, which automatically floods targeted websites with traffic. Active participants are often rewarded with cryptocurrency. This often provides a list of victims to be targeted.
The group operates across multiple Telegram languages in several languages for maximum impact.
Telegram Activity: An Overview
DarkOwl analysts reviewed the English-language Telegram channel operated by NoName057(16) (“NNM057(16) eng vers”), covering the channel’s creation on 27 October 2025 through 30 September 2026.
- The export contains 2,825 messages, of which 1,228 are text posts authored by the group and 230 are distinct posts forwarded from other channels.
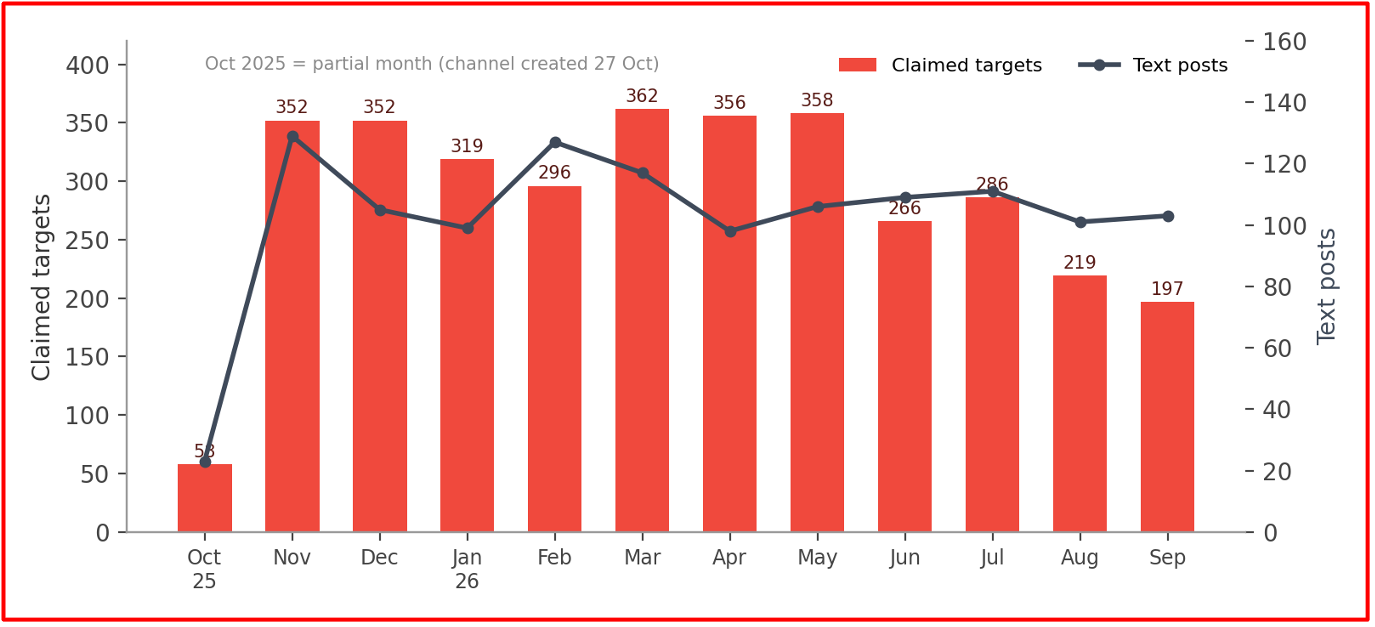
- The channel posted on 338 of 339 days, averaging 100–130 text posts per month with a weekday-heavy pattern concentrated between 07:00 and 12:00 UTC (10:00–15:00 Moscow time).
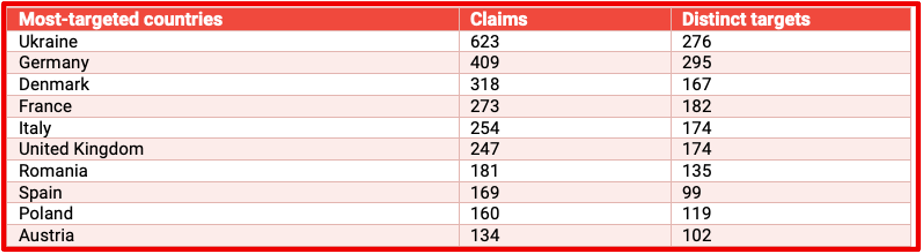
- The group made 666 DDoS claim posts and list 3,421 alleged targets (≈2,200 unique), averaging roughly 70 claimed targets per week. Ukraine, Germany, Denmark, France, Italy and the United Kingdom are the most targeted countries.
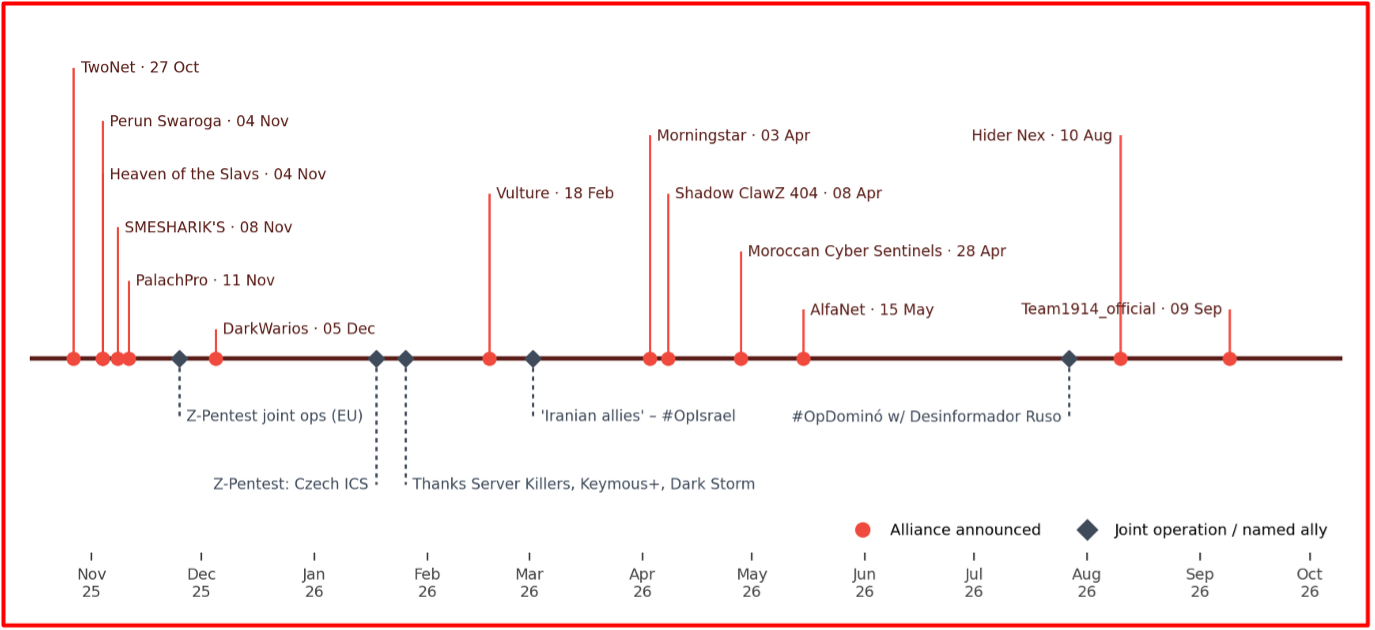
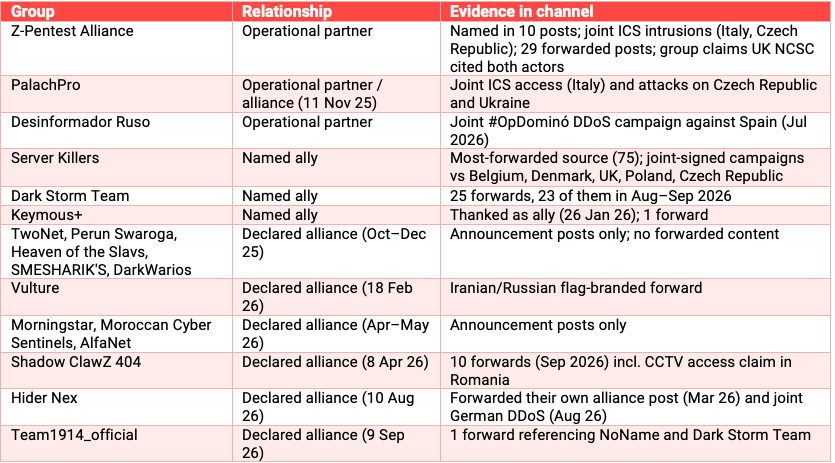
- NoName057(16) publicly announced 13 alliances during the period and named Z-Pentest Alliance, PalachPro and Desinformador Ruso as operational partners in joint attacks.
- Growing amplification forwarding of other groups’ content rose sharply in August–September 2026 (36 and 49 posts respectively), driven by Server Killers, Dark Storm Team, BD Anonymous and Shadow ClawZ 404, signaling deepening ties with pro-Palestinian and Global-South hacktivist networks.
- Beyond DDoS, the group increasingly claims intrusions into industrial control systems (ICS) and CCTV (45 posts tagged #BrokenByte), runs a paid TOR tip platform, and publishes a “Tribunal” list of named foreign individuals.
Scope and Methodology
DarkOwl parsed every message, from of the group’s English-language channel, for timestamp, text, hashtags, links, media type and forward origin. Alleged victims were extracted from the group’s standard claim format — each target is prefixed with a ❌ marker and usually accompanied by a check-host.net report used as “proof” of downtime. Country attribution relies on the group’s own #Op campaign hashtags.
All victim figures represent claims made by the threat actor and have not been independently verified. Some listed targets are described by the group as “closed by geo” or “behind a stub”, indicating geo-blocking or DDoS mitigation rather than an outage. Unique-target counts are approximate because the same organisation is frequently described with different wording across posts.
Posting Activity
NoName057(16) operates its English channel with near-industrial regularity. Following a short partial month at launch, output stabilised at 98–129 text posts per month and never dropped materially, even during periods of reported law-enforcement pressure and channel takedowns. Posting occurs on almost every day of the period, typically 2–5 posts per day and at most 10.
• Weekday focus: Wednesday (222 posts) and Tuesday (206) are the busiest days; Saturday and Sunday volume drops by roughly half (129 and 104).
• Working-hours pattern: over 80% of posts are published between 07:00 and 13:00 UTC, consistent with a staffed schedule in Moscow time rather than ad-hoc volunteer activity.
• Consistent messaging: 1,020 posts carry the group’s signature hashtags #FuckEastwood and #TimeOfRetribution, a reference to Europol’s July 2025 Operation Eastwood takedown against the group.
Alleged Victims
The group’s core output is DDoS claim posts. Across the period DarkOwl identified 666 claim posts listing 3,421 alleged targets, a median of five targets per post. After normalisation, approximately 2,200 distinct organisations are named, of which around 650 were claimed on more than one occasion. Claim volume held steady at 300–360 targets per month from November 2025 through May 2026 before tapering to about 200 per month in August and September 2026, a decline that coincides with the rise in forwarded partner content.
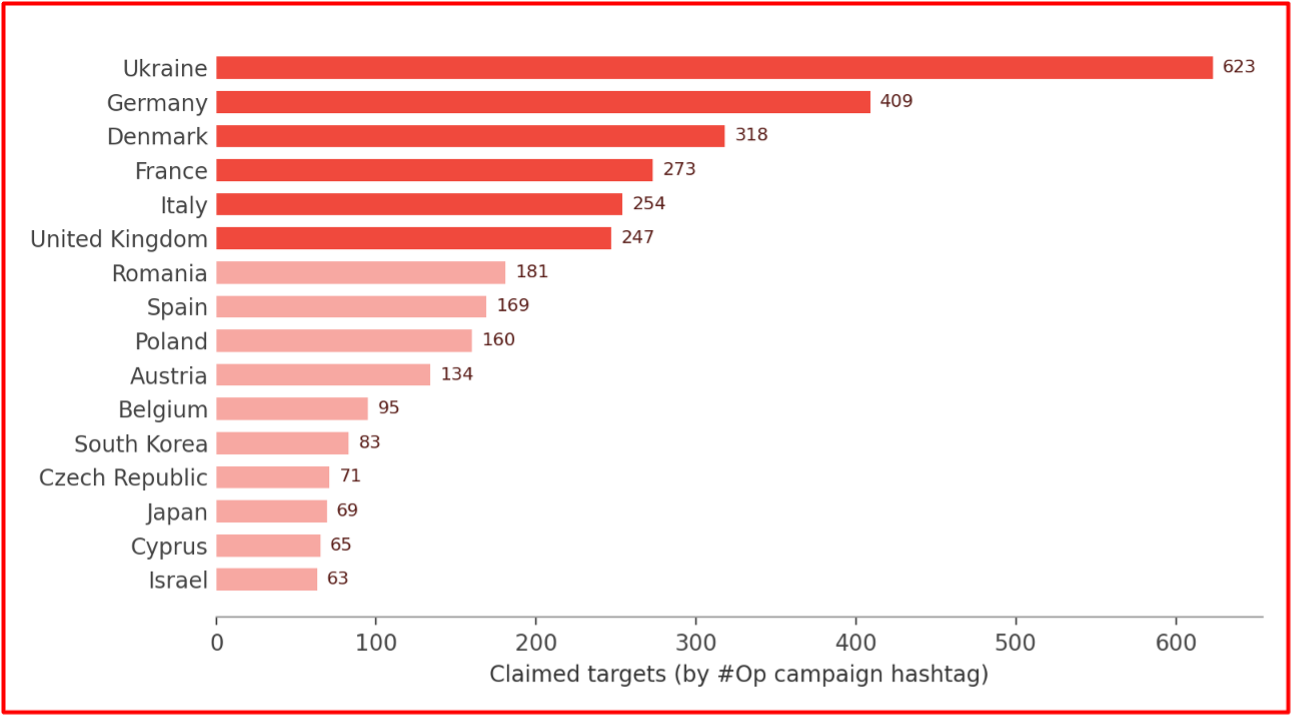
Target selection appears to be tightly coupled to geopolitical triggers. Most claim posts open with a news item on military aid to Ukraine, sanctions or anti-Russian statements, followed by a list of targets in the relevant country. Government portals, municipalities, transport (airports, ports, metro systems), energy utilities, telecoms, banking and defence-industrial firms dominate the target set. Ukrainian defence-industrial and infrastructure organisations are repeatedly re-targeted; the most frequently claimed individual targets include Ferrexpo, AvtoKrAZ, Amstor Retail Group and the Sumy regional ISP SKM.
Intrusion and ICS Claims
In addition to DDoS, NoName057(16) increasingly publicises claims of unauthorised access to operational technology, often in collaboration with Z-Pentest Alliance, PalachPro and its own DDoSia Project volunteers. Examples include an Italian poultry-farm control system, an 850 kW industrial boiler in the Czech Republic, the Centrale Chalmazel hydroelectric plant in France and CCTV at a German water-treatment facility. Forty-five posts carry the #BrokenByte campaign tag introduced for this activity.
Affiliations, Alliances and Forwarded Content
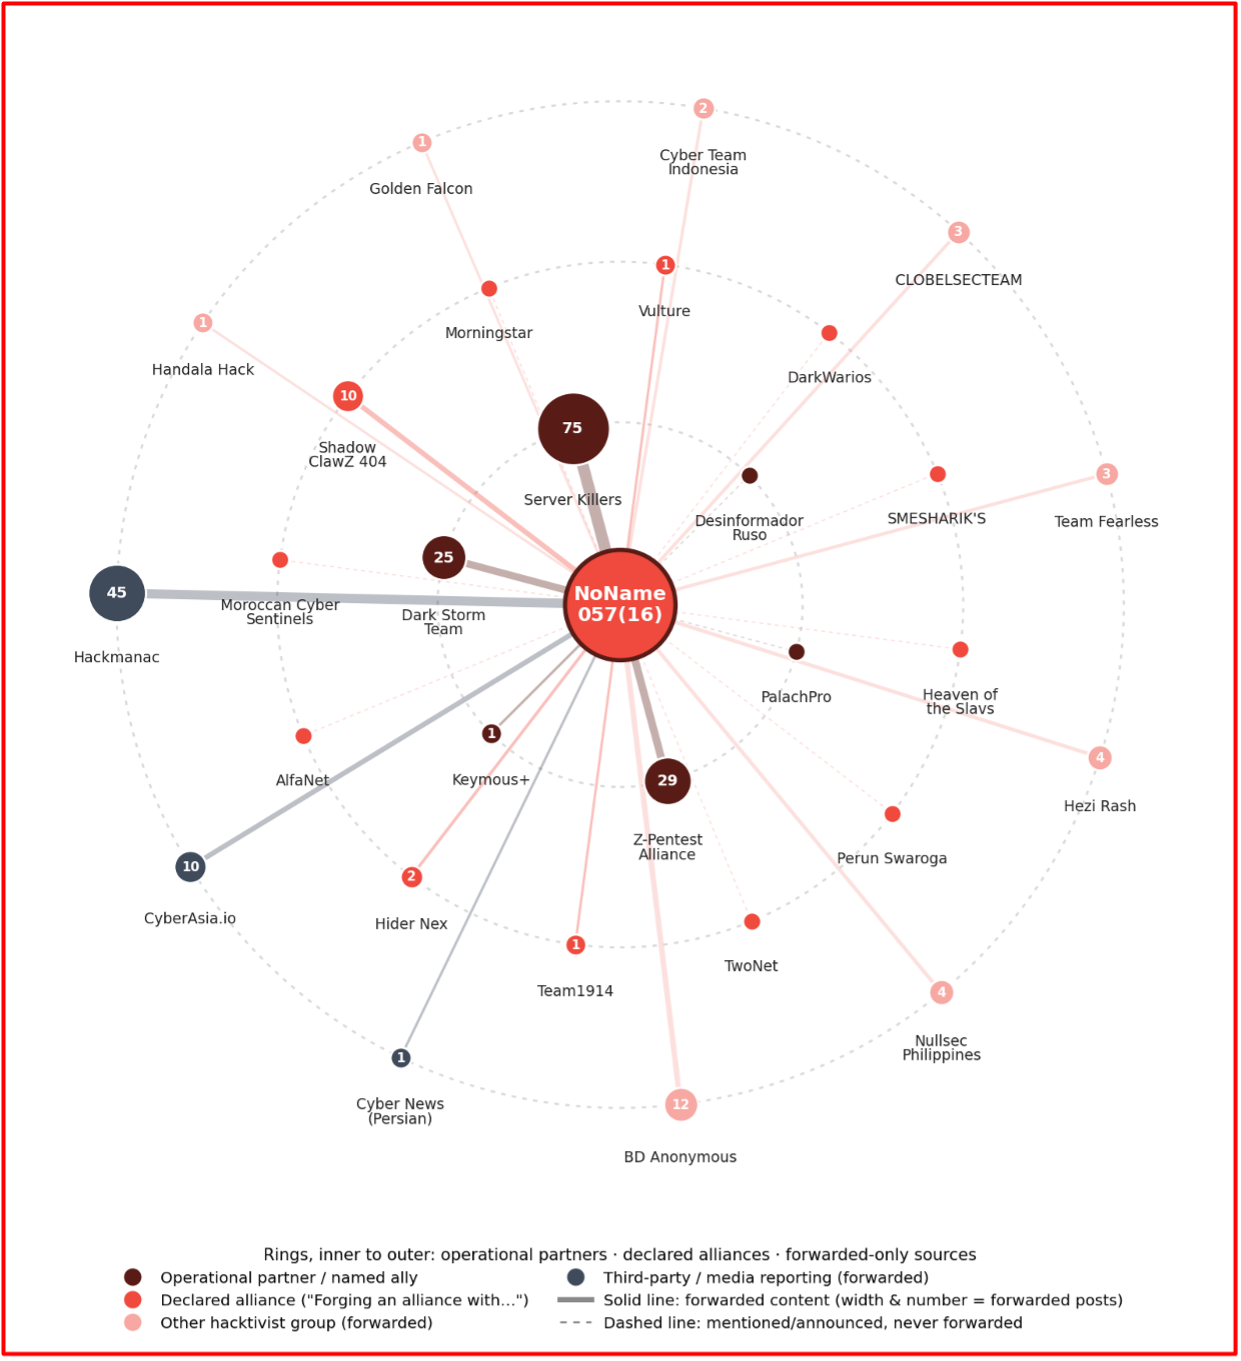
NoName057(16) uses its channel as a hub for a wider hacktivist ecosystem. DarkOwl identified three distinct types of relationship:
- Named operational partners with which the group claims joint attacks;
- Formally declared alliances, announced with a standard “Forging an alliance with… The more of us, the stronger we are!” post; and
- Groups and outlets whose content is forwarded without a declared alliance.
The channel also forwards third-party threat-intelligence reporting (notably Hackmanac’s weekly “Hack Tuesday” rankings) as a form of self-promotion.
Declared Alliances
Thirteen alliances were announced during the period. Early announcements (October–December 2025) were almost entirely with Russian-speaking collectives; from February 2026 onward the group courted non-Russian actors, including Iranian-aligned Vulture, North-African Moroccan Cyber Sentinels, and Hider Nex, reflecting a deliberate internationalisation of its coalition.
Forwarded Content Over Time
Forwarding volume was modest from October 2025 to July 2026 (typically 4–26 posts per month) and dominated by Server Killers, Hackmanac and Z-Pentest Alliance. Z-Pentest forwards stop after April 2026. A marked shift occurs in August–September 2026, when forwards rise to 36 and 49 per month and the mix broadens to Dark Storm Team, BD Anonymous, Shadow ClawZ 404 and third-party outlet CyberAsia.io.
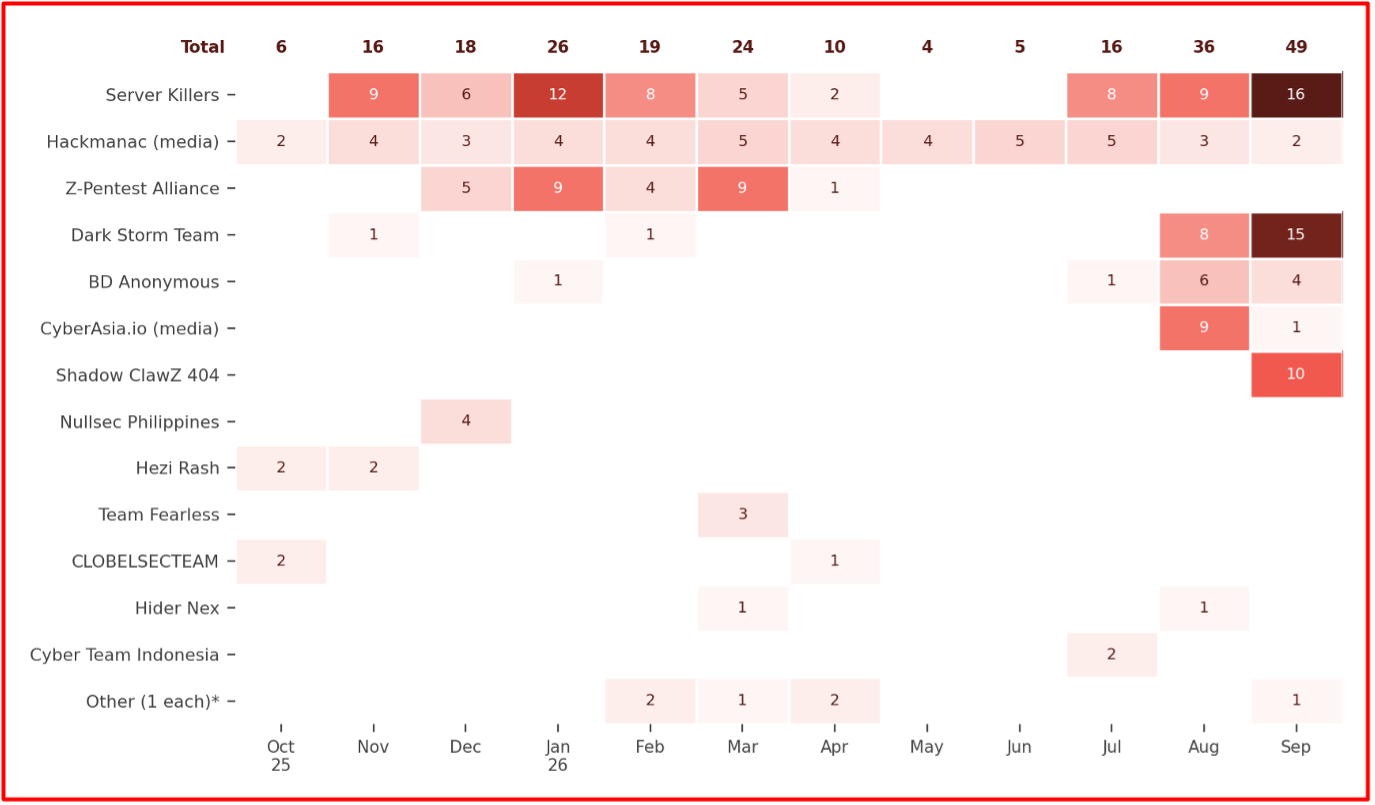
Forwarded hacktivist sources span a broad ideological range. Alongside pro-Russian collectives, NoName057(16) amplifies pro-Palestinian and Global-South actors, BD Anonymous (Bangladesh), Nullsec Philippines, Cyber Team Indonesia, Team Fearless, Hezi Rash, CLOBELSECTEAM and Iranian-aligned personas such as Golden Falcon and Handala Hack. In March 2026 the group explicitly attacked Israeli targets “in solidarity with our Iranian allies”.
Other Notable Activity
• DDoSia Project recruitment: 107 posts promote the group’s crowdsourced DDoS tool and volunteer program, including periodic results summaries.
• TOR “Secure Share” platform: repeated calls (Mar–Jul 2026) for insiders to submit sensitive information on “countries hostile to Russia” in exchange for payment.
• “Tribunal” list: a campaign (#NoName05716_Tribunal) naming foreign individuals the group accuses of acting against it, and offering rewards for personal information about them, in some cases extending to their families.
• Channel resilience: frequent references to Telegram takedowns, replacement channels (e.g., a new Spanish channel on 20 May 2026) and a backup bot launched on 17 September 2026, alongside language-specific channels in Russian, Italian and Spanish.
• Offline influence: volunteers distributing NoName057(16) stickers in European cities and campaigns in support of a detained associate.
Assessment
NoName057(16) remains one of the most prolific hacktivist actors observed, sustaining a steady tempo of DDoS claims against NATO and EU states supporting Ukraine despite the July 2025 Operation Eastwood disruption. DarkOwl assesses with moderate confidence that the group is evolving from a standalone DDoS brand into a coalition hub: the late-2026 surge in forwarded partner content, the steady cadence of alliance announcements, and the pivot toward ICS and CCTV intrusion claims all point to a strategy of amplifying reach through allied groups while shifting its own messaging toward higher-impact operations.
Organizations in the most-targeted countries, particularly public-sector, transport, energy and defense-industrial entities, should expect continued short-duration DDoS campaigns timed to political announcements on Ukraine support, and should review internet-exposed OT/HMI and CCTV interfaces given the growing number of intrusion claims by NoName057(16) and its partners.


