What is Encryption?
September 24, 2026
Cybersecurity might as well have its own language. There are so many acronyms, terms, and sayings that unless you are deeply knowledgeable, have experience in the security field, or have a keen interest, one may not know what they mean. Understanding these terms is the first step to developing a thorough understanding of cybersecurity and, in turn, better protecting yourself, clients, and employees.
In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, push bombing, web application attacks, man-in-the-middle attacks, ransomware leak sites, and the CIA Triad. In this edition, we dive into encryption.
Encryption 101
At its core, encryption is the cryptographic process of encoding plain text or raw data into an unreadable format, known as ciphertext. Only authorized parties who possess the corresponding decryption key can translate that ciphertext back into its original, legible form. Put simply, encryption helps ensure that if unauthorized individuals gain access to data, they cannot simply read it. The National Institute of Standards and Technology (NIST) defines encryption as the process of transforming plaintext into ciphertext using a cryptographic algorithm and key.
Encryption is used throughout modern technology. It can protect files stored on a computer, information saved in a database, messages sent between devices, online transactions, and communications traveling across a network.
Encryption ensures data confidentiality and integrity—two core pillars of the CIA Triad. Without encryption, sensitive corporate communications, credentials, credit card details, and personal health information would travel across local networks and the open web in plain, easily readable text.
How Does Encryption Work?
Encryption relies on two primary components: an algorithm and a key.
An encryption algorithm is the mathematical process used to transform plaintext into ciphertext. The key is a piece of information that controls that transformation. Without the appropriate key, the ciphertext should be extremely difficult to convert back into its original form. The strength of an encryption system depends on several factors, including the algorithm, key management, implementation, and how securely the keys themselves are protected. This last point is particularly important. Even strong encryption can be undermined if an attacker gains access to the keys used to decrypt the information.
Symmetric vs. Asymmetric Encryption
There are two primary types of encryption: symmetric and asymmetric encryption.
- Symmetric Encryption: Uses a single, shared secret key to both encrypt and decrypt data. Algorithms like AES-256 (Advanced Encryption Standard) are exceptionally fast and computationally efficient. They are routinely used for bulk data protection, such as hard disk encryption and secure database storage.
- Asymmetric Encryption: Uses a pair of mathematically linked keys—a public key for encryption and a private key for decryption. RSA and ECC (Elliptic Curve Cryptography) are common examples. While computationally heavier than symmetric keys, asymmetric protocols eliminate the risky requirement of sharing a single key across unsecured networks.
Encryption in the Real World
Encryption itself is neutral technology—it simply enforces privacy and access control. Because of this, it serves as a critical defense for legitimate enterprises while simultaneously acting as a primary weapon for threat actors operating in darknet ecosystems.
Protective Security Measures
For enterprise organizations, end-to-end encryption (E2EE) and transport layer security (TLS) safeguard sensitive traffic from Man-in-the-Middle (MitM) interception. Furthermore, encrypting data at rest ensures that even if an unauthorized user breaches a corporate database, the stolen files remain unusable without the corresponding keys.
Darknet Privacy & Anonymity
Darknet networks like Tor and I2P rely on multi-layered encryption (often described as “onion routing”) to conceal IP addresses, server locations, and user identities. Security researchers and threat intelligence analysts use tools like Pretty Good Privacy (PGP) and encrypted Linux utilities to communicate safely and store sensitive datasets gathered during darknet investigations.
Malware and Ransomware Weaponization
Threat actors frequently turn encryption against their targets:
- Ransomware-as-a-Service (RaaS): Cybercriminals deploy malicious payloads to systematically encrypt a victim company’s critical files and network drives, demanding a extortion payment in exchange for the decryption key.
- Intermittent Encryption: To evade security detection tools, modern ransomware operators often encrypt only select portions of a file rather than the entire disk. This emulates normal administrative system processes and drastically speeds up the encryption process before defenders can respond.
- Information Stealers: Advanced infostealers incorporate an Encryption Module. Ironical as it is, malicious actors use algorithms like AES to encrypt credentials and system tokens before exfiltrating them back to Command and Control (C2) servers. This hides the stolen data from network monitoring tools and security analysts.
Encryption and the Darknet
Encryption also plays an important role in the underground ecosystem. Threat actors use encryption and other privacy-enhancing technologies to communicate, exchange stolen information, and conceal aspects of their activities. Encrypted communications can make it more difficult for organizations and investigators to determine what threat actors are discussing or planning.
However, encryption does not necessarily make criminal activity invisible.
Threat actors frequently leave behind other forms of information, including usernames, aliases, email addresses, cryptocurrency addresses, domains, malware advertisements, stolen credentials, and discussions of specific targets. Connecting these seemingly separate pieces of information can help security teams build a more complete picture of a threat actor or campaign.
Ransomware provides a particularly visible example.
During a ransomware attack, threat actors can encrypt files or systems belonging to a victim organization, preventing the organization from accessing its own data. The attacker then demands payment in exchange for a decryption key or other means of restoring access.
Encryption itself is not malicious. The difference lies in how it is used and who controls the keys.
This distinction is important when investigating compromised data. Encrypted information found during an investigation may not be immediately readable, but it can still provide valuable context about an attack, the systems involved, or the threat actors behind it.
Plaintext vs. Encrypted Data: What Appears on the Dark Web?
When darknet market vendors and ransomware groups leak compromised databases on underground forums, the state of the data often dictates its market value:
- Plaintext Credentials: Cleartext email-and-password combinations are the most easily exploited digital goods. They are immediately usable for credential stuffing, account takeover (ATO), and network intrusion.
- Hashed and Salted Passwords: When companies properly implement cryptographic hashing algorithms (such as SHA-256 or bcrypt), leaked database dumps contain cryptographic hashes rather than raw passwords. Threat actors must perform resource-heavy offline cracking routines to revert these hashes back to plain text.
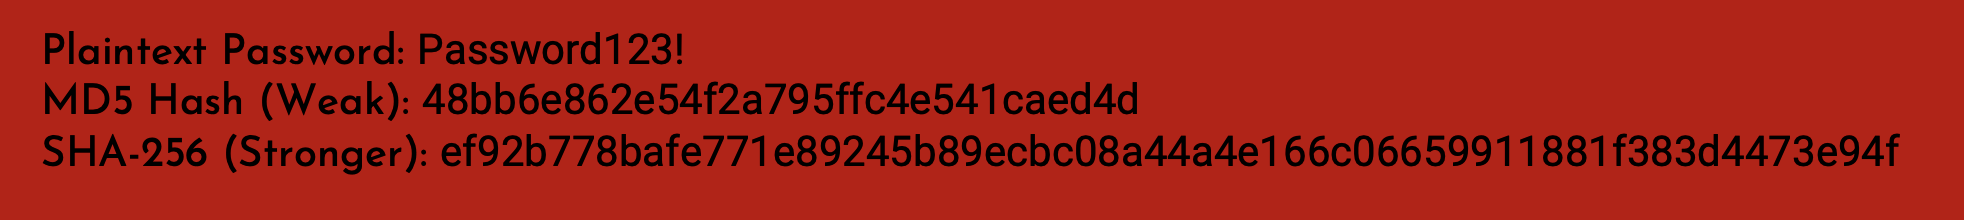
While legacy algorithms like MD5 and SHA-1 remain surprisingly common across darkweb breach dumps, darknet intelligence shows a growing transition toward stronger SHA-256 and SHA-512 hashes as organizations update their authentication standards.
Why Is Encryption Important?
Encryption plays a critical role in protecting sensitive information from unauthorized disclosure.
Without encryption, intercepted or stolen data may be immediately readable.
Consider a laptop containing sensitive customer information. If the device is stolen and its stored data is encrypted, an attacker may have possession of the physical hardware without automatically gaining access to the information stored on it.
The same principle applies to data traveling across networks. Encryption can help prevent unauthorized parties from simply reading intercepted communications.
Encryption is therefore an important component of protecting:
- Personally identifiable information (PII)
- Financial information
- Healthcare information
- Intellectual property
- Authentication credentials
- Corporate communications
- Customer data
- Government and critical infrastructure information
However, encryption is not a standalone security solution.
It does not prevent every type of cyberattack. An attacker who compromises an authorized user’s account may be able to access information after it has been legitimately decrypted. Likewise, encryption does not prevent phishing, malware, credential theft, insider threats, or vulnerabilities in applications.
Encryption protects the confidentiality of data, but organizations still need layered security controls to protect the systems, identities, applications, and users that interact with that data.
Best Practices for Enterprise Encryption
Implementing robust encryption is essential to maintaining strong data governance and mitigating risk:
- Enforce Strong Standard Algorithms: Phase out legacy cryptographic algorithms (such as DES, MD5, or SHA-1) in favor of modern standards like AES-256, SHA-256, and RSA-2048+.
- Key Management Discipline: Storing encryption keys on the same server as the encrypted data defeats the purpose of cryptography. Use Hardware Security Modules (HSMs) or centralized, access-controlled key management vaults.
- Protect Data in Transit and at Rest: Ensure TLS 1.3 is enforced for all external endpoints and full-disk encryption is mandatory across all enterprise endpoints, remote worker laptops, and cloud storage buckets.
- Monitor Darknet Exposure: Even strong internal encryption cannot prevent third-party vendor leaks or endpoint infostealer infections. Utilizing specialized darknet monitoring enables organizations to detect exposed API keys, internal credentials, and database dumps early—before threat actors can exploit them.
Curious to learn more about dark web monitoring? Contact us.


