Author: DarkOwl Content Team

What is Ransomware as a Service?

March 19, 2026

Cybersecurity might as well have its own language. There are so many acronyms, terms, sayings that cybersecurity professionals and threat actors both use that unless you are deeply knowledgeable, have experience in the security field or have a keen interest, one may not know. Understanding what these acronyms and terms mean is the first step to developing a thorough understanding of cybersecurity and in turn better protecting yourself, clients, and employees. 

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, and credential stuffing. In this edition, we dive into Ransomware as a Service.

Ransomware has become one of the most disruptive cyber threats affecting organizations worldwide. What was once a technically complex attack carried out by a small number of sophisticated hackers has evolved into a scalable criminal ecosystem. Today, ransomware can be purchased, deployed, and monetized through a model known as Ransomware-as-a-Service (RaaS). It is a business model for cybercriminals to hire ransomware operators to launch ransomware attacks on their behalf.

DarkOwl research and analysis shows how ransomware groups operate like structured businesses on darknet forums and marketplaces—recruiting affiliates, sharing tools, and dividing profits. Understanding how this ecosystem works is critical for organizations seeking to defend against it.

RaaS is a business model in which ransomware developers create malware and infrastructure, then lease it to affiliates who carry out attacks. In turn, the developers get a percentage of the ransom earnings from the affiliates. Typically, the affiliate keeps 70-80%, while the developer takes a 20-30% “licensing fee.” This model lowers the barrier to entry and this model of cybercrime is now the driving force behind the global surge in extortion attacks. Individuals with limited technical skills can participate in ransomware campaigns simply by purchasing access to a RaaS toolkit.

Ransomware groups often operate similarly to legitimate businesses, complete with recruitment processes, internal management tools, and operational dashboards used to track victims and ransom payments. DarkOwl analysts often find “starter kits” for sale on darknet forums. These kits include everything a criminal needs: the malware, a user manual on how to infect a target, and even 24/7 technical support from the developers. It is a professionalized industry where reputation and “customer service” matter to the criminals.
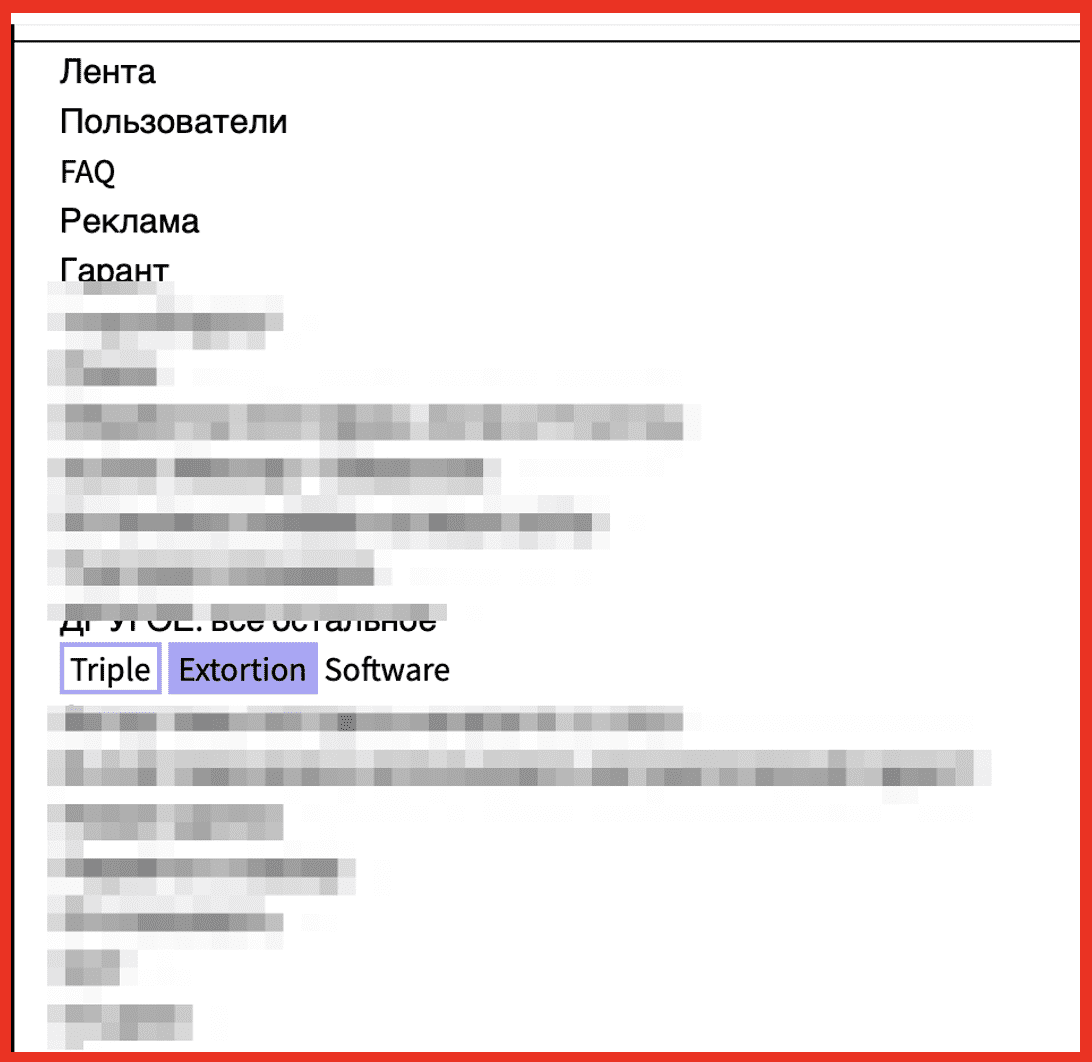
Figure 1: Post on criminal market XSS offers triple extortion software for purchase; Source: DarkOwl Vision

RansomHub 

The group RansomHub first appeared in February 2024, with an announcement on the Russian forum RAMP. The group operates a ransomware-as-a-service (RaaS) model, targeting multiple platforms, including Windows, Linux, and ESXi.  A user named “koley” made the announcement and invited others to join their affiliate program. RansomHub quickly became one of the most active ransomware groups, claiming 593 victims by the end of the year. RansomHub’s affiliate program has been prolific over taking established groups, such as LockBit, in the number of victims they have. Notably, RansomHub was responsible for a significant breach of the U.S. healthcare payment system in 2024. 

Hive

First observed in 2021, Hive operated as a RaaS platform with affiliates targeting organizations worldwide. The group notably targeted healthcare organizations and used double-extortion tactics—encrypting systems while also threatening to release stolen data. In 2023, an international law-enforcement operation seized Hive’s infrastructure after the group had already impacted more than 1,500 organizations globally.

Conti

Conti was one of the most prolific ransomware operations in the world. Internal chat logs leaked in 2022 revealed a highly organized operation that included employee-like roles, development pipelines, and operational dashboards used to track victims and payments. Although the group officially shut down, many of its members dispersed into other ransomware operations, continuing the ecosystem under new names.

BlackCat

Also known as ALPHV, BlackCat emerged in 2021 and quickly gained attention for being written in the Rust programming language. The group implemented a public data-leak site that indexed stolen files, increasing pressure on victims to pay ransom demands.

Ransomware is an efficient criminal operation yielding high profit for minimal work. Due to pseudo-anonymous technology, using the dark web for ransomware operations and cryptocurrency for payments, as well as email and VPN services that do not track physical location, ransomware groups will continue their activities because the risk of punishment is minimal, and the operations are profitable.

As always, DarkOwl recommends practicing cyber hygiene at work and home.

  1. The 3-2-1 Backup Rule: Keep three copies of your data, on two different media types, with one copy stored completely offline. By using multiple storage types and locations, it helps you avoid having a single point of failure.
  2. Enable Multi-Factor Authentication (MFA): Turn on MFA for every account. It adds a second proof (app prompt, code, or security key) so a stolen password alone won’t grant access.
  3. Patches and Updates: Keep everything current—laptops, phones, browsers, and even routers/IoT. Updates patch known flaws attackers actively exploit. Criminals look for “holes” in outdated software.
  4. Phishing Awareness & Training: Most RaaS attacks start with a simple phishing email. Slow down on links and attachments. Verify unusual requests on a separate channel and report suspicious emails/messages to IT.

Ransomware is not only a problem for those directly affected. Awareness of events among your own or your customers’ supplier ecosystems can help you stay aware of potential vectoring threats. The DarkOwl Ransomware API is designed to answer the essential question: Has an organization I monitor been extorted or compromised in a cybersecurity incident?

Leveraging the world’s leading and continuously updated darknet data index, you can gain insight into potential risk by conducting targeted ransomware searches. Ransomware API enables users to safely query continuously sourced and updated ransomware sites, primarily but not exclusively hosted in TOR and Telegram, run by criminal gangs, and threat actors to detect mentions of criminal activity against an organization.

Search parameters enable queries by company website, company name, contact name, or other proximity indicators such as products, brands, or other intellectual property.  Automated monitoring and alerting ensure continuous vigilance to a dynamic list of sources continually updated by DarkOwl.

Curious to learn more about Ransomware API? Contact us.

Threat Intelligence RoundUp: February

March 02, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. Mandiant Finds ShinyHunters-Style Vishing Attacks Stealing MFA to Breach SaaS Platforms – The Hacker News

On January 31, Mandiant reported a newly identified expansion in threat activity involving tactics similar to those used by ShinyHunters. These attacks employ voice phishing (vishing) and credential-harvesting websites that impersonate targeted organizations, enabling attackers to obtain single sign-on (SSO) credentials and multi-factor authentication (MFA) codes to gain unauthorized access to victim environments. Mandiant’s threat intelligence team said it is monitoring the activity across several clusters, UNC6661, UNC6671, and UNC6240 (ShinyHunters), to account for the possibility that these groups are evolving their tactics or imitating previously observed methods. Read full article.

2. Hackers exploit SolarWinds WHD flaws to deploy DFIR tool in attacks – BleepingComputer

CISA flagged a critical SolarWinds Web Help Desk (WHD) vulnerability, CVE-2025-40551, that is now being exploited by unknown hackers. Using legitimate tools, such as Zoho ManageEngine, threat actors were able to target organizations and maintain persistent, hands-on access to compromised environments. Following initial access, attackers installed the Zoho ManageEngine Assist agent from an MSI hosted on the Catbox file-sharing platform, configured it for unattended access, and registered the affected host with a Zoho Assist account created using an anonymous Proton Mail address. Article here.

On January 28, it was discovered the FBI had seized RAMP, a Russian cybercrime forum, that advertised malware and hacking services. Both the forum’s Tor site and its Clearnet domain, ramp4u[.]io, have been taken offline and now show a seizure banner declaring, “The Federal Bureau of Investigation has seized RAMP.” According to the notice, “This action has been taken in coordination with the United States Attorney’s Office for the Southern District of Florida and the Computer Crime and Intellectual Property Section of the Department of Justice,” indicating a multi-agency effort behind the takedown. RAMP administrator “Stallman” acknowledged the takedown in a message on XSS, adding that he has no plans to create a successor platform. Read more here.

Chinese state hacking group, UNC6201, is believed to be behind a zero-day exploitation of  in Dell RecoverPoint for Virtual Machines, tracked as CVE-2026-22769. The high-risk vulnerability has been exploited since May 2024 and shows persistent access of the malware SLAYSTYLE and BRICKSTORM. Additionally, UNC6201 deploys a newly identified malware called Grimbolt, which leverages a technique that is faster and more difficult to analyze than BRICKSTORM. Google Threat Intelligence Group (GTIG) has not confirmed an initial access vector, but previous attacks connected to UNC6201 indicate a possible target of edge appliances for initial access. Read here.

5. Reynolds Ransomware Embeds BYOVD Driver to Disable EDR Security Tools – The Hacker News

Researchers have identified a new ransomware family, Reynolds, which embeds a built-in Bring Your Own Vulnerable Driver (BYOVD) component within its payload to evade security defenses. The technique BYOVD abuses legitimate flaws in driver software that disables Endpoint Detection and Response (EDR) making it possible for malicious activity to go undetected. While similar techniques have been observed in prior attacks, the Reynolds campaign specifically drops a vulnerable NsecSoft NSecKrnl driver and terminates processes associated with multiple security programs. Learn more.

6. One threat actor responsible for 83% of recent Ivanti RCE attacks – BleepingComputer

Recent threat intelligence observations link one threat actor to two critical vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM). According to GreyNoise Threat Research team, between February 1st and 9th the EPMM experienced 417 observed exploitation sessions. Of those 417, 83% of observed exploitation can be tracked to a single IP address (193.24.123.42) on bulletproof infrastructure. The activity is designed to trigger a DNS callback to a unique subdomain controlled by the tester. This approach allows threat actors to confirm that their command was successfully executed without needing a direct response from the target system. Read full article.

7. Sandworm hackers linked to failed wiper attack on Poland’s energy systems – BleepingComputer

In late December 2025, the Russian state sponsored hacking groups, Sandworm, attempted to deploy a destructive “data-wiping malware” called DynoWiper against Poland’s power grid. Polish officials have claimed the attack “targeted two combined heat and power plants as well as a management system used to control electricity generated from renewable sources such as wind turbines and photovoltaic farms.” Officials also stated that their current “systems in place” were able to prevent the attack but gave minimal additional information. Read full article.

8. China-Linked Amaranth-Dragon Exploits WinRAR Flaw in Espionage Campaigns – The Hacker News

Throughout 2025, Amaranth-Dragon, a China-linked threat actor has been connected with new cyber espionage campaigns targeting government and law enforcement in Southeast Asia. Threat actors abused a now-patched security vulnerability (CVE-2025-8088) in RARLAB WinRAR, which permits arbitrary code execution upon opening a specially crafted archive.  Although the exact method of initial access is still unclear, the highly targeted nature of the campaigns and the use of customized lures tied to regional political, economic, or military events strongly suggest spear-phishing. In these attacks, emails likely delivered archive files hosted on trusted cloud services such as Dropbox, helping attackers appear legitimate and evade traditional perimeter defenses. Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Difference Between Information Security and Cybersecurity

February 18, 2026

In an era of data breaches and constant headlines focused on “security” topics, “security” has become a catch-all term. While the terms cyber security and information security are often used interchangeably, it is important to acknowledge that they focus on different areas – they are related, but their scope differs. In this blog, we will explore how they differ in scope, focus, and application.

To start, information security (infosec) can be thought of as an umbrella term, while cybersecurity is a specialization underneath that umbrella. Using the terms interchangeably can lead to gaps in your defense strategy as cyber security focuses on the digital realm, while information security protects data in all forms.

Information Security

Information Security is the broad practice of protecting information and information systems from unauthorized access, use, disclosure, disruption, modification, or destruction. This includes both data in the digital realm, as well as physical data (think of a file on your computer and a file in your filing cabinet). The goal of information security is to protect the CIA Triad (note that since cybersecurity is a subset of information security, these goals align to cybersecurity as well – the scope is just more specific). The CIA Triad stands for confidentiality, integrity, and availability:

  • Confidentiality: is your sensitive information only accessible to those authorized to see it?
    • Common Threats: phishing, man in the middle attacks, human error
  • Integrity: is your data authentic, accurate, and reliable?
    • Common Threats: man in the middle attacks, human error, malware, hardware/software glitches
  • Availability: are the systems, networks, and data up and running whenever authorized users need them?
    • Common Threats: distributed denial of service attacks, hardware failure, ransomware, natural disaster

Examples of information security would be the practice of shredding sensitive paper documents, office keycard systems, and encryption policies. Threats against strong information security include theft, natural disasters, and physical breaches.

Cybersecurity

Cybersecurity is the practice of defending computers, servers, mobile devices, electronic systems, networks, and data from malicious digital attacks. If it involves the internet or a digital network, it’s cybersecurity. In the example above, cybersecurity is the data in the digital realm – a file on your computer (and the systems, networks, and hardware that house it). The goal in cybersecurity is to protect against cyber attacks – hacking, malware, phishing – to name a few. Examples of cybersecurity would be firewalls, antivirus software, and securing “Internet of Things” (IoT) devices. Threats against secure cybersecurity include cyber warfare, hacking, and data breaches.

Security is a holistic culture, not just a software update. Information security and cybersecurity work together in creating overlapping layers of defense. You cannot have a robust security policy without incorporating both: the physical and digital layers of defense and policies covering both.

For example, infosec would set the overall policy of protecting and encrypting data (business level decision based on risk), while the cybersecurity division would implement the tech to do so (firewalls, encryption, multi-factor authentication, etc). In a situation where a breach or attack does happen, the two have distinct roles but cannot be successful without the other:

  • Information Security
    • Determines the data that was stolen
    • Manages the legal and regulatory fallout (GDPR/HIPAA notifications)
    • Initiates the Business Continuity Plan to ensure the company stays operational during the cleanup
  • Cyber Security
    • Identifies the threat details
    • Isolates the issue and stops it from continuing
    • Patches the vulnerability that the hacker used

In short, cybersecurity handles the threats (hackers, viruses, bots) while information security handles the risks (legal compliance, physical safety, data integrity).

With so many of us working from home, it is important to practice good daily security hygiene to make sure that not only the digital data of your company is safe, but potential physical risks are minimized as well. Below is a checklist covering the digital and physical bases to ensure your data stays private and your hardware stays safe:

Digital Checklist (Cybersecurity):

Protect your devices and network from remote attacks.

  • Secure the Router:
    • Change the default admin password
    • Enable WPA3 (or WPA2-AES) encryption
    • Turn off WPS (Wi-Fi Protected Setup
  • Segment Your Wi-Fi:
    • Set up a “Guest Network” specifically for your work laptop
      • This keeps your work data separate from “unsecure” items like an Amazon Alexa or gaming console
  • Enable MFA/2FA:
    • Use an authenticator app (like Google Authenticator or Authy) on every account
  • Automate Updates:
    • Set your OS (Operating System) and browser to “Auto-Update” so you get security patches immediately
  • VPN for Public Use:
    • Use a reputable VPN to create an encrypted “tunnel” for your data

InfoSec Checklist:

Protect the physical environment and the data itself.

  • Full Disk Encryption:
    • Ensure BitLocker (Windows) or FileVault (Mac) is on
  • The “Clear Desk” Policy:
    • Don’t leave passwords on sticky notes
    • Shred any documents containing client names, addresses, or account numbers before throwing them away
  • Visual Privacy:
    • Use a privacy screen filter on your monitor
  • Secure Backup (3-2-1 Rule):
    • Keep 3 copies of your data:
      • 2 different types of media (laptop and an external drive)
      • 1 copy stored off-site (encrypted cloud storage like Backblaze or iCloud)
  • Webcam Cover:
    • Have a physical slide cover for your camera is the only 100% guarantee against “cam-fecting”
  • Lock your computer when you step away

Q4 2025: Product Updates and Highlights

February 04, 2026

As we have wrapped up Q4, we’re excited to share major updates to our DarkOwl Vision product suite. Below we highlight some of the most exciting feature updates and launches. These enhancement and net new features reflect our commitment to providing continued value to our partner, clients, and the cybersecurity community. We look forward to what is in store in Q1 of 2026!

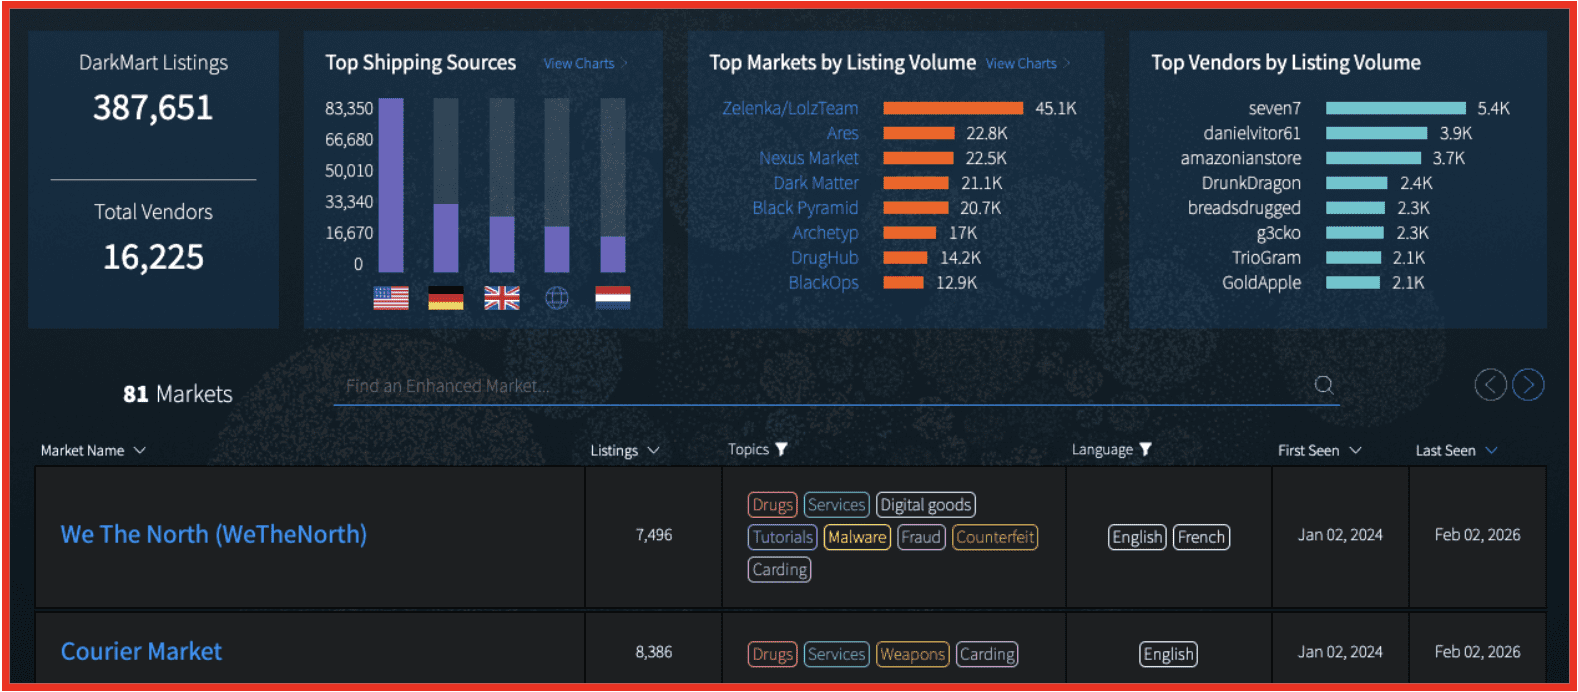
Understanding darknet marketplaces is critical for identifying emerging threats, monitoring illicit activity, and staying ahead of the evolving cyber‑risk landscape. DarkOwl’s Market Explore feature delivers an intuitive experience to dive deep into our enhanced darknet marketplace dataset. We now have 81 markets, with more than 387,651 listings and 16,225 vendors in our enhanced market listing DarkMart database.

At the top of the Market Explore page, you’ll find a set of visualizations that help you quickly understand: 

  • Overall listing volume and vendor activity 
  • Top shipping sources by listing count 
  • Darknet markets and vendors with the highest activity levels 

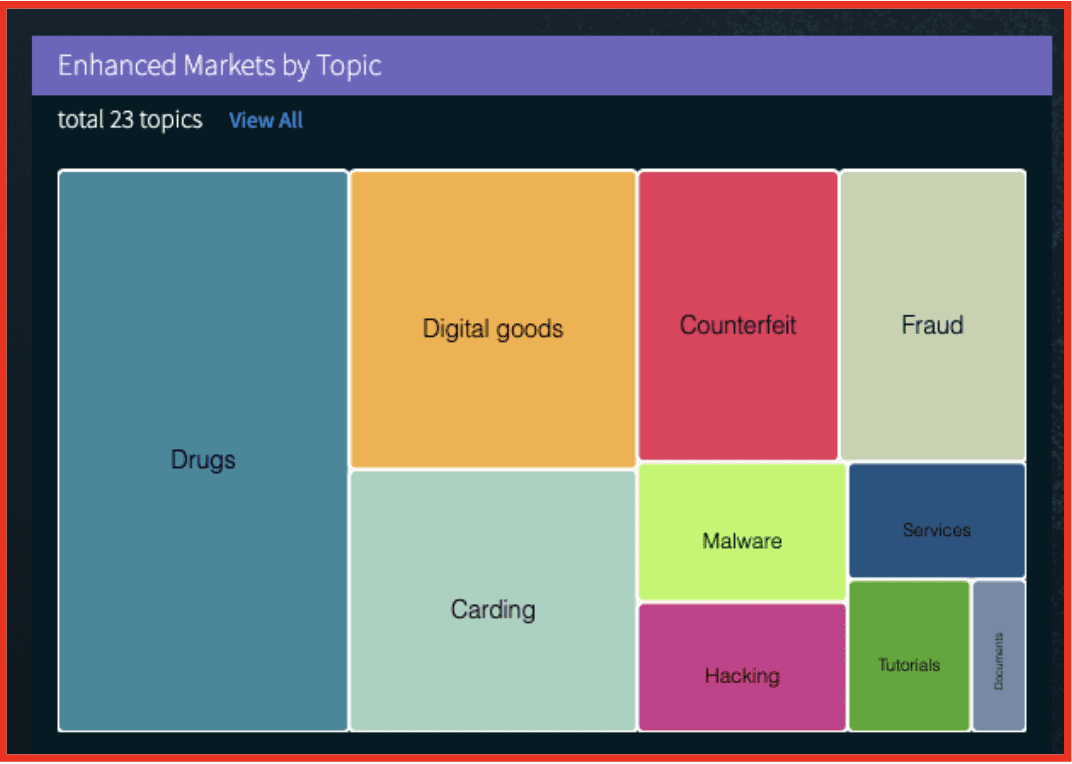
Selecting View Charts expands the charts into a full‑screen visualization experience, where you can explore trends like: 

  • Enhanced Markets by Topic 
  • New Listings Over Time 
  • Shipping Sources Across the Entire Dataset 

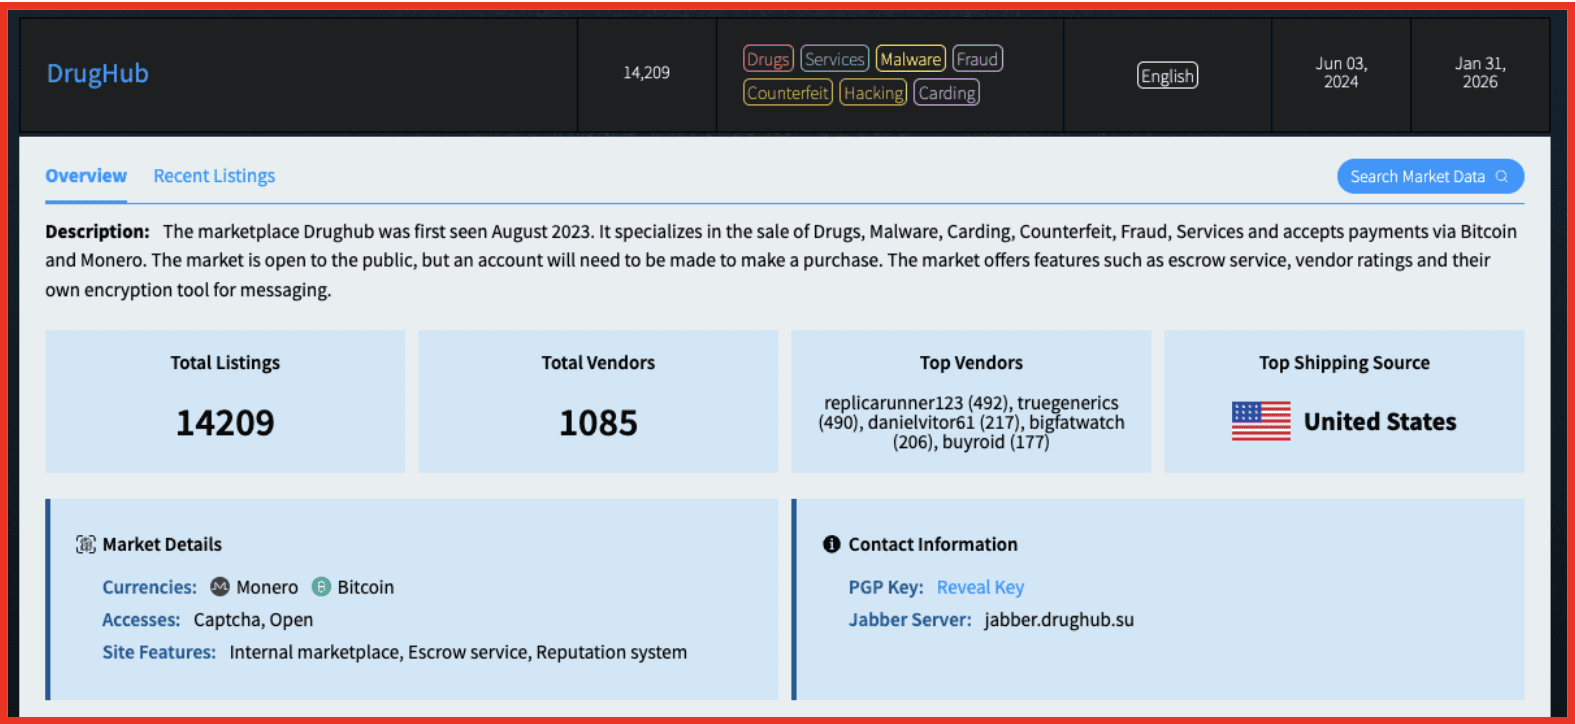
Each market’s Overview page provides a snapshot of marketplace activity: 

  • Total Listings: Unique listings available within our dataset 
  • Total & Top Vendors: Overall vendor count and top vendors ranked by listing volume 
  • Top Shipping Source: The region shipping the highest volume of listings 
  • New Listings Over Time: Daily/weekly/monthly visual trends 
  • Shipping Sources Map: Color‑coded visualization from highest volume to lowest 

Additional analyst‑curated information may include Market Descriptions, Currencies Accepted, Admin Handles, Contact Information (emails, Jabber servers, PGP keys). If a PGP key exists, users can reveal and copy it with a single click. You can also jump directly from the Overview into the Markets Research section to further investigate specific listings. 

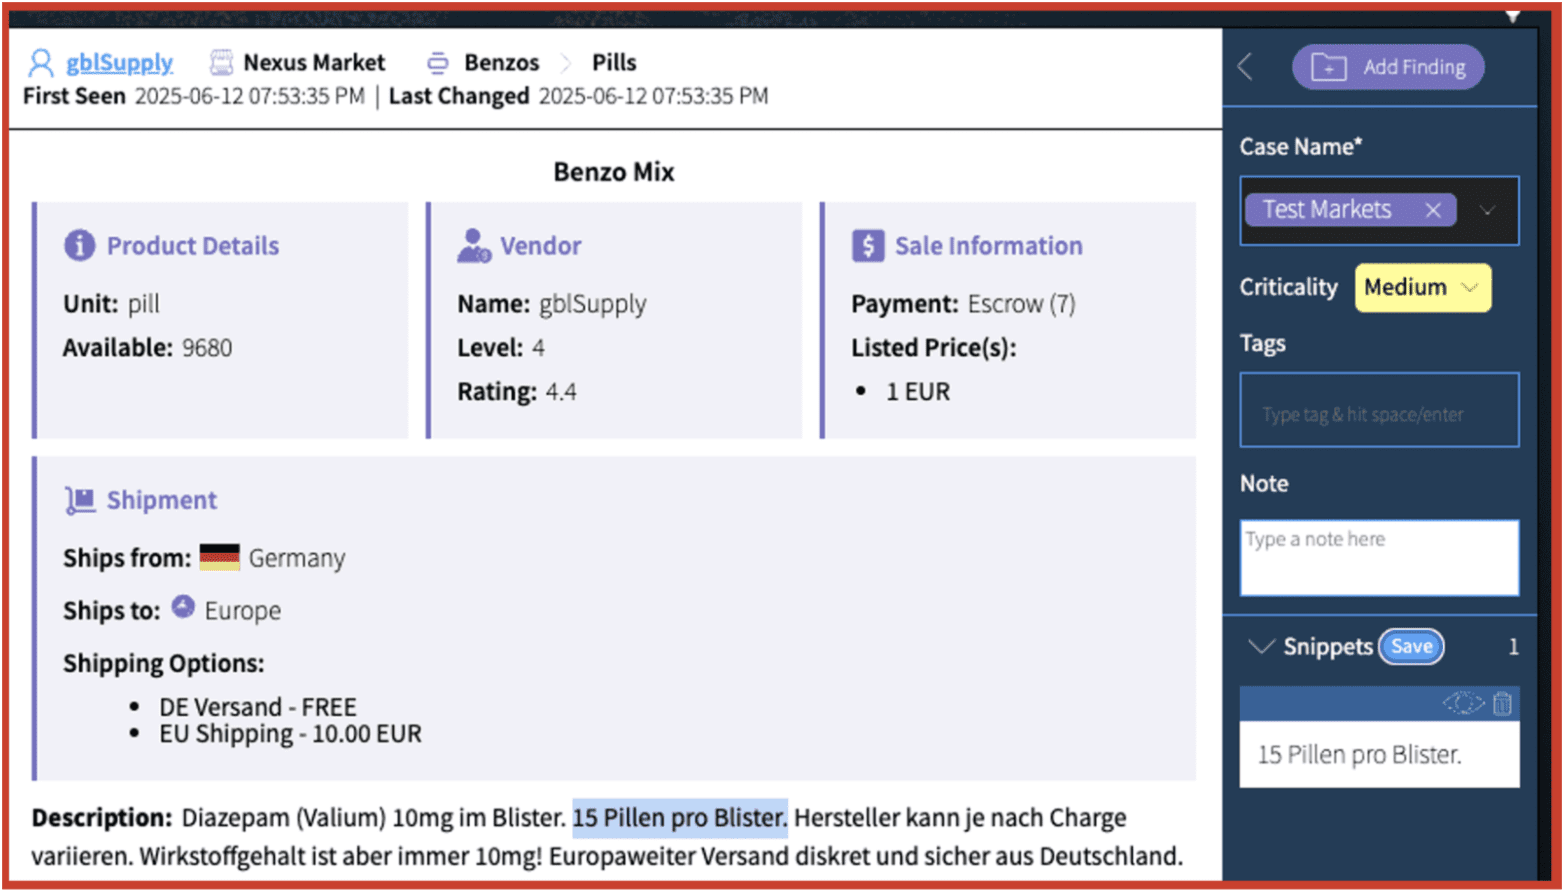
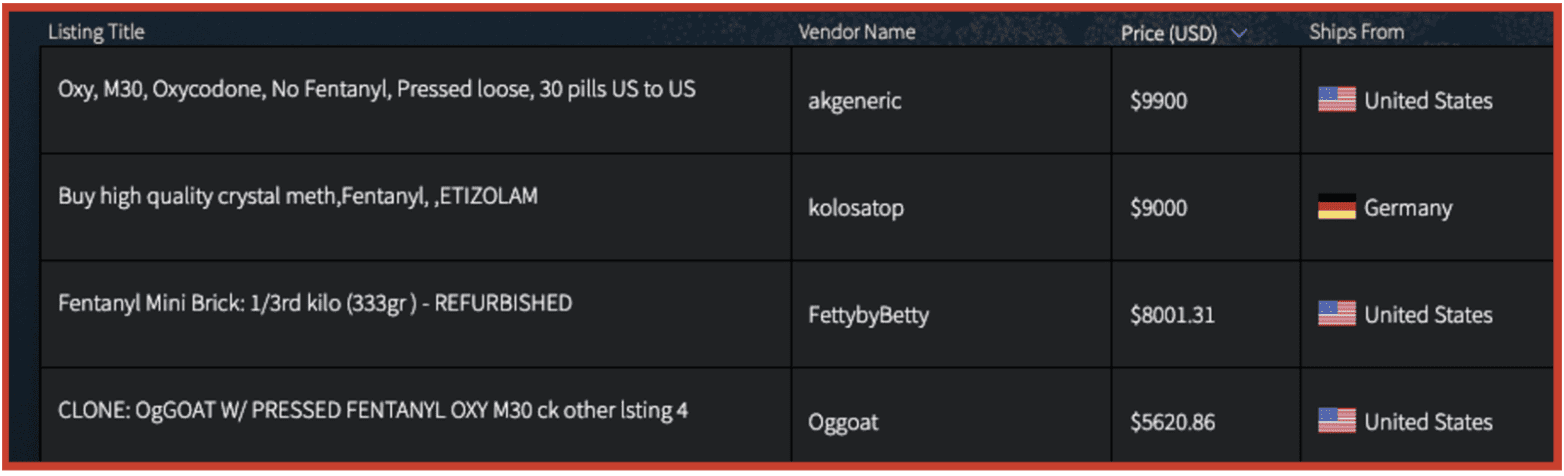
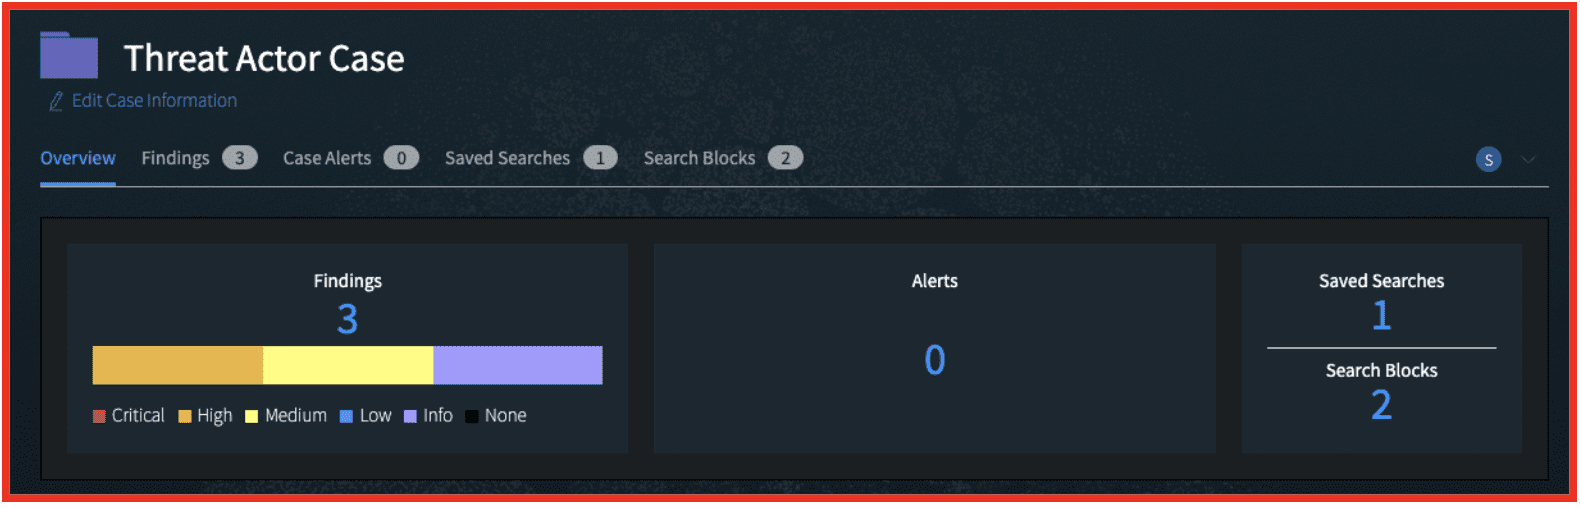
Building on the launch of DarkOwl’s Enhanced Marketplace Research in Q3, the team added several Research features: support for Findings, Search Blocks, and Site Context. Additionally, we have completed currency normalization for prices in market listings, allowing for Sort by Price features. 

Search results from selected paste sources have a new look + improved searchability. Paste results (more than 40 million documents) are now eligible to be returned when you filter by Post Date or Username in both Vision UI or Vision API. If available, Paste Authors are shown on the top of a UI search result and include a pivot link, just like Forum Post Authors or Market Vendors.  

We launched our Findings Export feature for Cases, allowing our users to bulk export important results out of Vision UI into Word, CSV, or JSON. It makes sharing reports and moving data out of Vision UI faster and easier. This was a top feature request from our customers and we are thrilled to have delivered on this ask! 

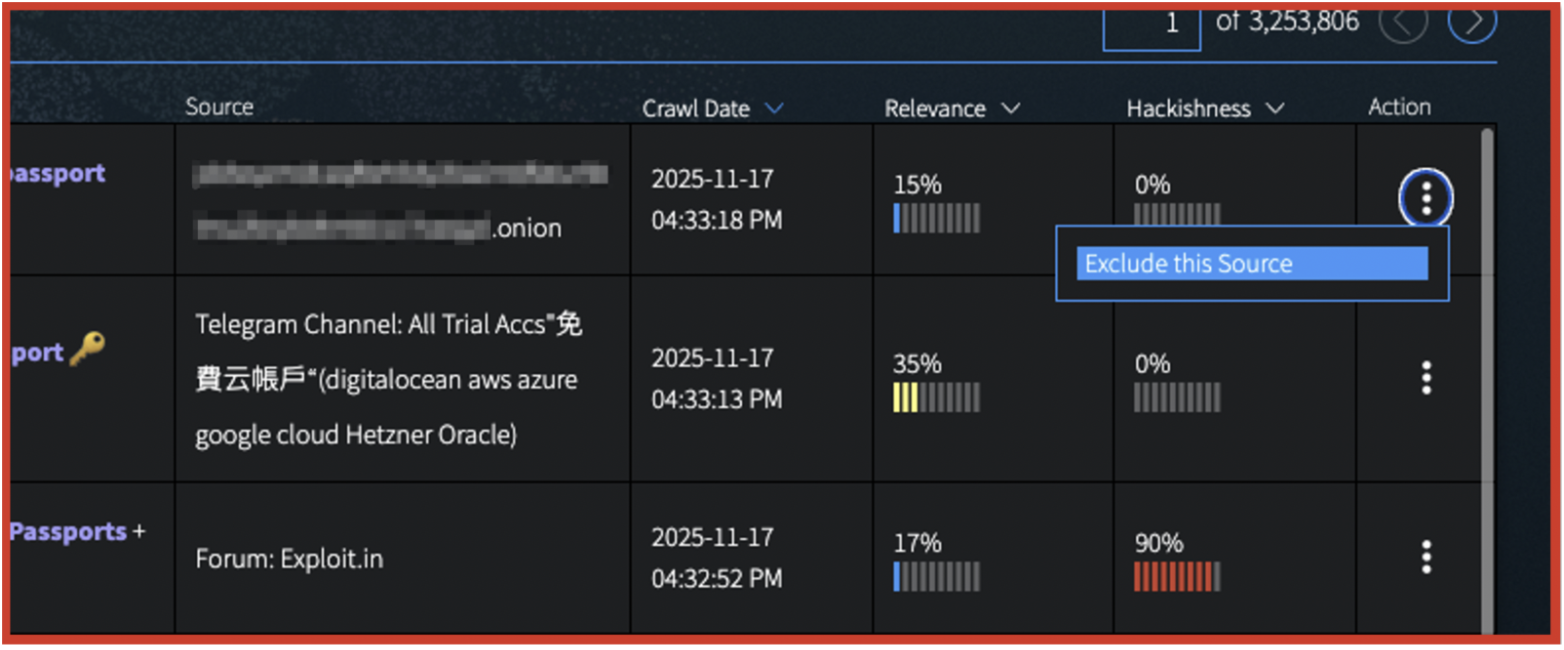
  • To more easily filter our noisy sites, or data leaks you’ve already seen, we’ve added an “Exclude this Source” option on the Vision UI search result table. 
  • We added 9 new actors to our Actor database in Q4. Additionally, Actor Explore and Actor API now include associated Sites in the Darknet Fingerprint tab. 

Highlights 

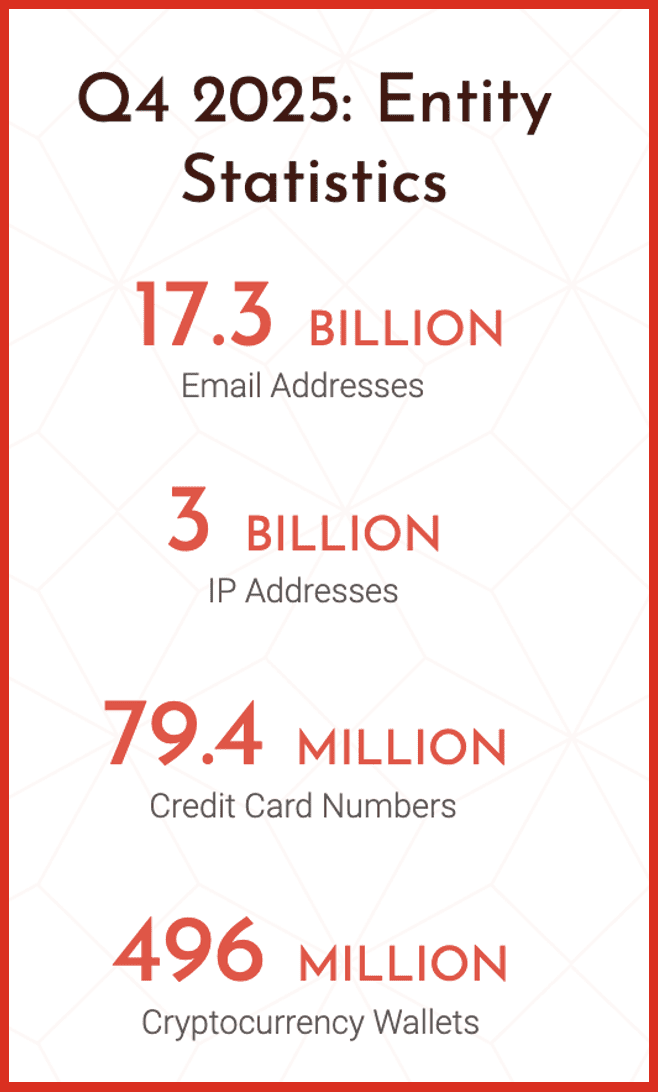
Quarter after quarter, our data collection team continues to astonish us with the quantity of data made available across DarkOwl products. Let’s highlight just some of that growth:

  • 6% increase in credit card numbers
  • 2.5% increase in IPs
  • 5% increase in data leak records

When your search results are from data leaks, users can review additional information curated by DarkOwl analysts, giving you enrichment on the data leak. The descriptions below are all available in our Leak Explore UI feature, or Leak Context API endpoint. 

Ryanair Internal Communications

Data purported to be from RYANAIR was posted on DarkForums, a hacking forum, on November 19, 2025. According to the post, the data breach includes email addresses, ticket bookings, travel details (departures, destinations), flight numbers, and ticket claimants. Data exposed includes names, email addresses, internal documents, company names, and internal emails.

IRAN IP NETWORK INFRASTRUCTURE

A post on DarkForums, a hacking forum, on August 22, 2025 linked to the file: iran-net-100k.json. According to the post, the “Caucasian Brotherhood” leaked a dataset of Iranian network information that included IP addresses, open ports, software versions, and DNS records. Data exposed includes countries, IP addresses, and locations.

Farm Credit Union Of Colorado Bank

Data purported to be from Farm Credit was posted on BreachForums, a hacking forum, on September 8, 2025. Data exposed includes names, customer information, physical addresses, online profiles and user identification number (UID).


Curious how these features and data can make your job easier? Get in touch!

Threat Intelligence RoundUp: January

February 02, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. ‘Bad actor’ hijacks Apex Legends characters in live matches – BleepingComputer

Over the weekend of January 09, players in Apex Legends, a battle royale shooter game, reported game disruptions caused by threat actors hijacking characters, disconnecting users, and changing nicknames. Respawn, the publisher of the game, confirmed the security incident claiming “bad actor is able to control the inputs of another player remotely in Apex Legends”. The company does not believe threat actors were able to exploit or infect malware, nor execute code. Read full article.

2. 27 Malicious npm Packages Used as Phishing Infrastructure to Steal Login Credentials – The Hacker News

On December 23, 2025 the Socket Threat Research Team announced the discovery of a 5 month long spear-phishing operation that turned 27 npm packages “into durable hosting for browser-run lures that mimic document-sharing portals and Microsoft sign-in”. The campaign targeted 25 organizations across the U.S. and Allied nations focusing on manufacturing, industrial automation, plastics, and healthcare. Specializing in focusing on sales and commercial personnel, the operation repurposed npm and package CDN’s “into durable hosting infrastructure, delivering client-side HTML and JavaScript lures that the threat actor embeds directly in phishing pages.” Following initial interaction, the script redirects the browser to threat-actor controlled infrastructure. Article here.

ReliaQuest’s Threat Research team has discovered a new phishing campaign using private messages to deliver malicious payloads with the intent to deploy remote access trojan (RAT). The attack began with a message sent via LinkedIn that contained a “malicious WinRAR self-extracting archive”. Once opened, the archive extracts four components, mainly a PDF disguised with names that align with the victim’s industry. The final payload attempts to communicate with an external server that can grant persistent remote access. Read more here.

Recent activity shows Chinese threat actor, Silver Fox, has begun using income tax themed lures to distribute ValleyRAT. The group has focused on Indian entities, using phishing emails containing decoy PDFs claiming to be from India’s Income Tax Department. Opening the attachment leads victims to download files that injects ValleyRAT into the system and communicates with external servers. Read here.

5. University of Hawaii Cancer Center hit by ransomware attack – BleepingComputer

In August 2025, the University of Hawaii’s (UH) Cancer Center was victim of a ransomware breach that stole participants data, including documents from the 1990’s containing Social Security numbers.  UH reported to the state legislature threat actors broke into Cancer Center services, “encrypted files related to a cancer study and demanded payment for a program to decrypt the files”. The breach targeted a specific research project and had no effect on clinical operations or patient care. Learn more.

6. North Korea-Linked Hackers Target Developers via Malicious VS Code Projects – The Hacker News

The Contagious Interview campaign, which has been linked to North Korean threat actors, has been observed leveraging a version of Microsoft Visual Studio Code (VS Code) to deploy a backdoor on compromised systems. First discovered in December 2025, the attack involves instructing targets to clone a repository “on GitHub, GitLab, or Bitbucket, and launch the project in VS Code as part of a supposed job assessment.” The overall goal is for payload to run every time a file in the folder is opened, which eventually leads to deployment of malwares like, BeaverTail and InvisibleFerret. Read full article.

7. Hackers claim to hack Resecurity, firm says it was a honeypot – BleepingComputer

Scattered Lapsus$ Hunters (SLH) announced via Telegram that they had breached systems belonging to Resecurity and stole internal data. To prove their claims SLH posted screenshots of the data which revealed communications between employees and Pastebin personnel. Resecurity published a report in December 2025 disputing the claims and stated after identifying threat actor probing activity in November 2025, they deployed a “honeypot” account. The account was in an isolated environment that contained fake information and was being monitored. Read full article.

8. China-linked hackers exploited Sitecore zero-day for initial access – BleepingComputer

The China-linked threat actor UAT-8837 has been observed attempting to compromise North American infrastructure by exploiting both known and zero-day vulnerabilities. The attacks begin with leveraging compromised credentials or by exploiting server vulnerabilities. Recent attacks include zero-day flaw in Sitecore products, CVE-2025-53690. Researchers claim UAT-8837 uses “open-source and living-off-the-land utilities, continually cycling variants to evade detection.” Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Tricks, Not Treats: Phishing, Social Engineering & the Dark Web

October 31, 2025

This Halloween, the scariest thing might be what’s tucked inside the candy bar, a lure that looks harmless but hands an attacker the keys to your digital life.  

Phishing and social-engineering attacks are the “tricks” that become catastrophic when the dark web supplies ready-made toolkits and AI-generated messages to amplify them. The result: low-effort, high-impact scams that can ruin reputations and drain bank accounts. 

This Halloween we explore the “scary tricks” cyber criminals are using to successfully trick you into clicking on phishing emails and other attack types, and what you can do to avoid this activity.  

Phishing and the wider family of social-engineering attacks (spear-phishing, smishing, vishing, “quishing” via QR codes, and voicemail impersonation) remain one of the simplest ways to get real access to real systems. For that reason, they remain one of the top cyber-attack vectors in 2025. Phishing and social engineering attacks have been responsible for some of the largest breaches so far this year, such as Salesforce and Allianz.  

Researchers have highlighted that the large majority of successful cyber-attacks usually include a human element and are not purely technological vulnerabilities.

But two trends are supercharging phishing today: 

  • Automation and commoditization — phishing kits and “phishing-as-a-service” lower the technical bar for attackers. These are readily available software people can purchase to conduct attacks meaning they do not need to have the technical skills to conduct the attack. 
  • AI-augmented social engineering — generative models craft extremely convincing lures at scale. That combination turns the old “spray-and-pray” email into a professional, targeted, and scalable crime machine. Not to mention the creation of believable videos, images and voices which can be used to conduct vishing and other attacks.

The dark web and underground communities are where the tools, templates and services live, both marketplaces and forums offer software for sale as well as how to tutorials on how to conduct these attacks. Telegram also shared this information via marketplace channels. Below are some of the things being sold.  

Security researchers have indicated that the availability of ready-to-use phishing kits on the dark web rose by ~50% from 2021 to 2025, highlighting that this is a trend that is only increasing.  

Phishing Kits  

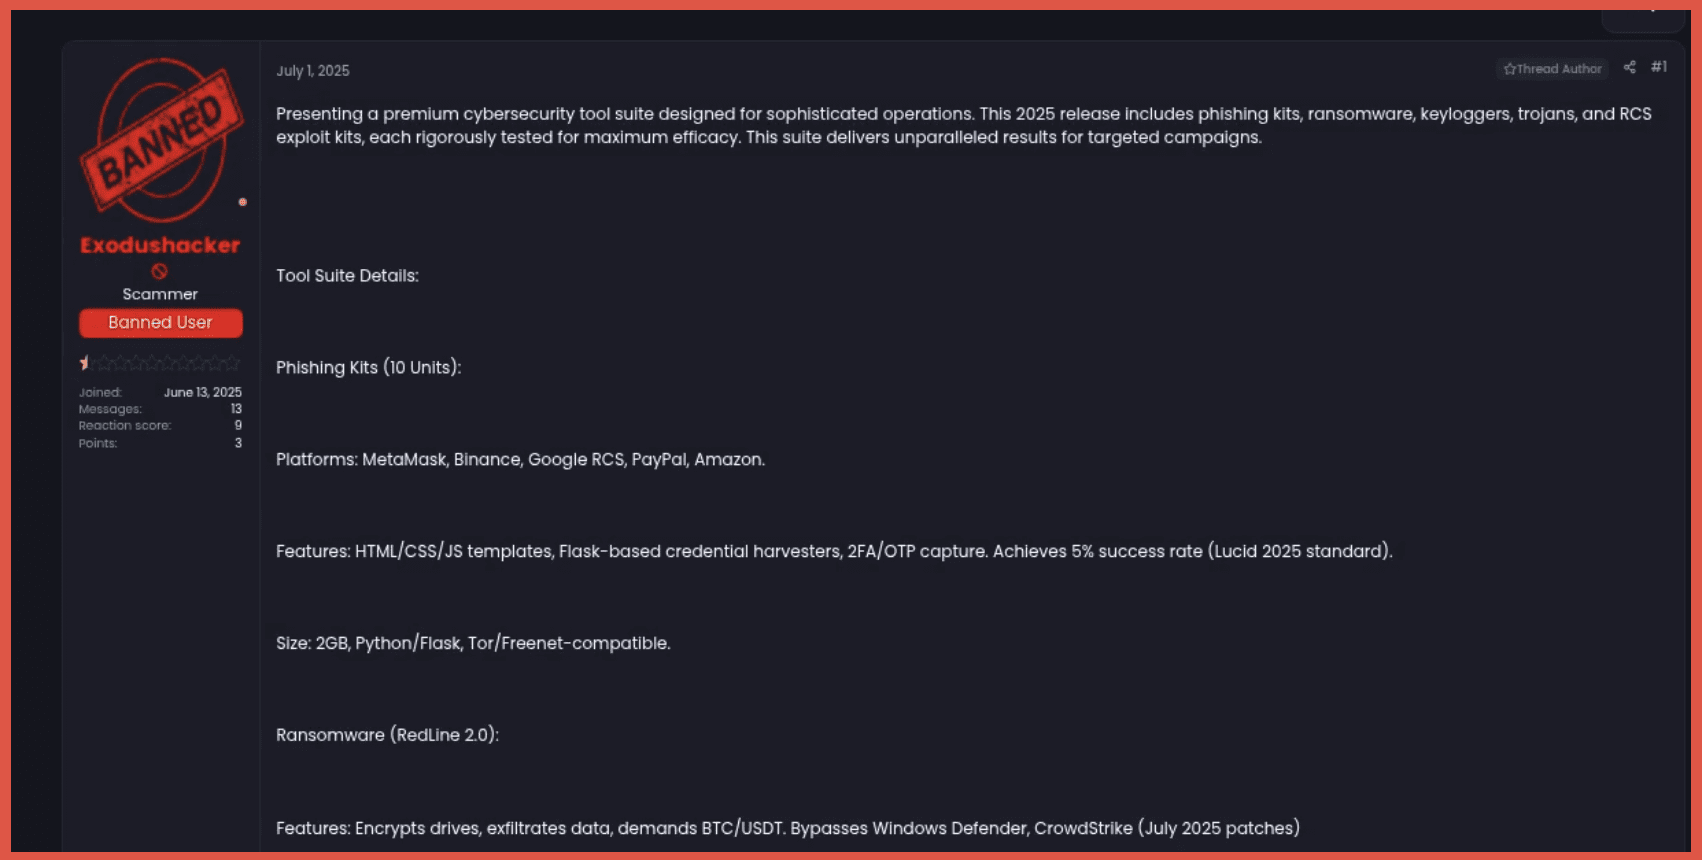
Pre-built fake pages, sending scripts and hosting/configuration guides. Research and reporting show fully fledged kits are routinely sold for pocket change, some reports find kits advertised for as little as ~$25 while others are open source, making it trivial for novices to impersonate banks, delivery services, or SaaS providers. The below image from a dark web forum shows users sharing a list of openly available phishing kits claiming they are the best kits to use in 2025.  

Phishing-as-a-Service & Automation Platforms  

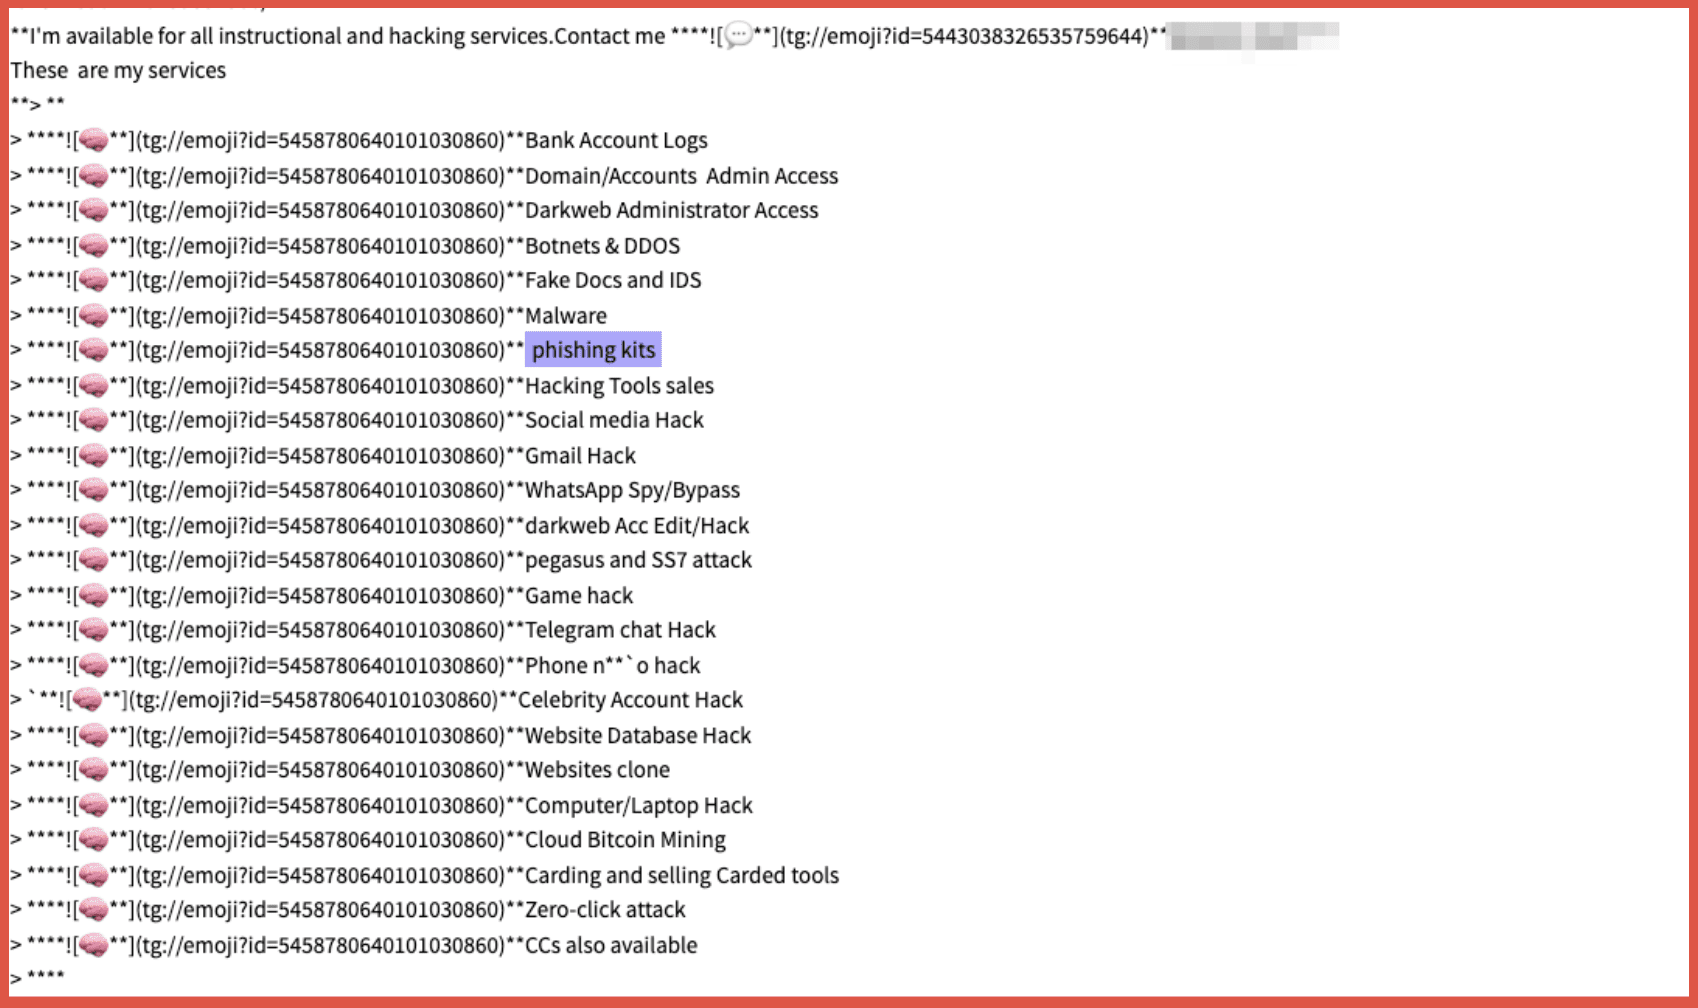
Another offering which is provided on dark web sites, is providing the service on the behalf of an actor. This means the actor doesn’t not need to take any action but can pay someone else to conduct the attack. The below image from Telegram shows a threat actor offering hacking services including phishing kits.  

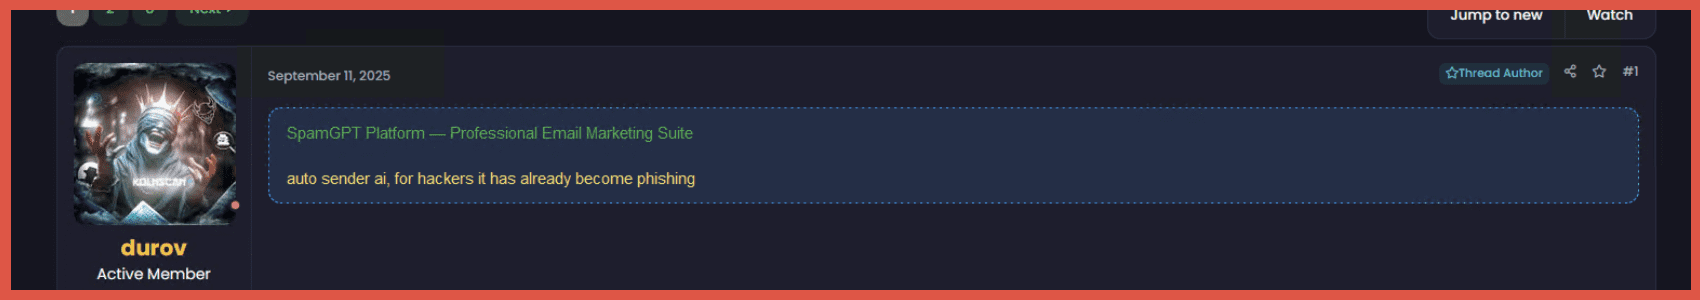
More advanced offerings include campaign dashboards, SMTP pools, deliverability testing and analytics (some newer tools even pair generative AI with mailing infrastructure). The below images show an advertisement for a phishing related AI model as well as the site to purchase the software. The “SpamGPT” toolkit—AI-powered spam-as-a-service sold on underground forums for around US $5,000.

Stolen Contact Lists & Harvested Credentials  

While we have previously shared the sale of human organs, this Halloween the harvesting of credentials can be even more scary with wide ranging ramifications. Harvested credentials and victim lists, often sold in bulk, let attackers skip reconnaissance and target previously compromised users.

These data leaks, with credentials and sometimes a lot more information can be really useful to threat actors when conducting social engineering attacks. This can make phishing attacks seem much more believable as they have accurate and real information in them.  

These tools lower the barrier to entry, enabling less-skilled attackers to launch large campaigns. They are readily available on the dark web and adjacent sites like Telegram. This means that the number of attacks being conducted can and will increase as individuals need less skills to conduct them. But it is likely that AI develops that the attacks themselves will become more sophisticated and complex. A scary thought! 

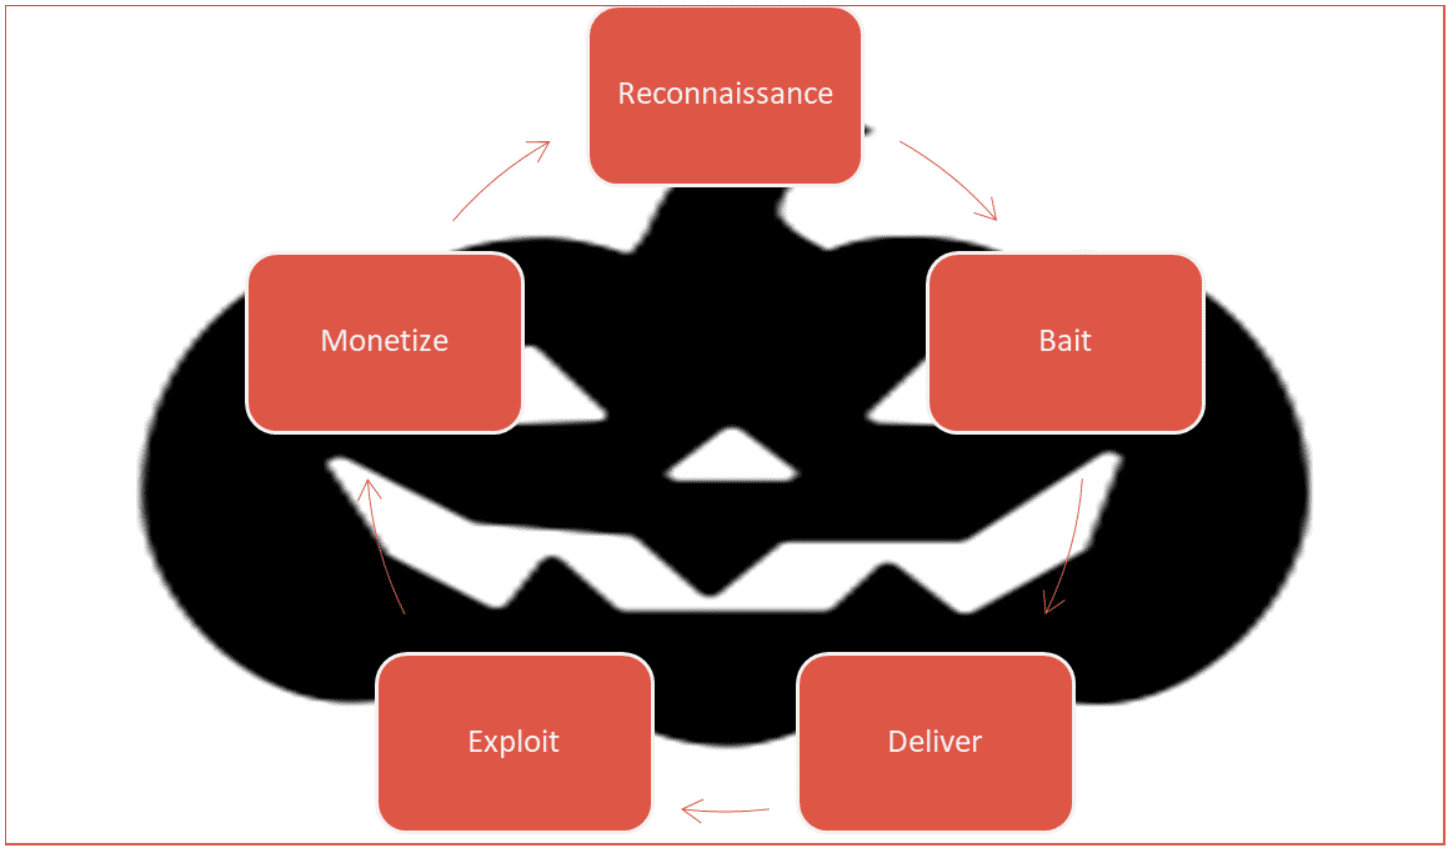
Figure 5: Phishing Campaign Cycle 

Attackers will start with the reconnaissance phase, conducting research usually through open channels or stolen data to find information about the intended targets. Then they create the bait – using a phishing kit or AI they will create a message that they think will hook the target and bypass spam filters. They use the information they found during the reconnaissance phase to make it as believable as possible.  

Next comes the delivery phase. Depending on what they are trying to achieve there are multiple delivery methods that can be used such as email, SMS, QR codes and even phone calls. In some cases, actors will use multiple channels as part of their attacks to increase the success rate.  

The Exploit phase requires input from the victim to be successful. A victim will click on a link or provide credentials to a phishing site or inadvertently install malware on their computer. These credentials are then used by the attackers to conduct further attacks. But the information can be monetized further by selling the stolen information or access to other actors on the dark web – continuing the cycle of phishing attacks.  

Generative AI has already begun to improve the quality, personalization, and scale of phishing. Platforms and toolkits that combine text generation with campaign automation create highly convincing lures that are difficult for users (and sometimes filters) to distinguish from real messages.  

A new class of underground offerings — some reported under names like “SpamGPT” — pair natural language generation with mailing infrastructure and analytics, effectively giving attackers a polished marketing stack for phishing.  

The net effect: phishing no longer requires good writing skills or deep technical know-how. It requires money (often small) and an account on an underground marketplace. That democratization of attack capabilities is why credential theft and phishing success rates have jumped in recent reporting.  

For Organizations  

  • Multi-factor authentication (MFA) everywhere — reduces the value of stolen passwords even if credentials leak. (Use phishing-resistant MFA like hardware keys where possible.)  
  • Email protections + DMARC/DKIM/SPF + advanced detection — deploy and tune anti-phishing gateways, URL detonation, and link rewriting. Train filters to use behavior signals (login geography, device fingerprinting).  
  • Phishing simulations + continuous user training — recurring, contextual training that adapts to current phishing themes reduces click rates. Combine simulated attacks with coaching, not just shame.  
  • Dark-web monitoring & rapid credential-remediation — monitor for leaked credentials or company data; have a playbook to force resets and contain exposed accounts.  
  • Least privilege + segmentation + strong logging — limit how far a single compromised account can go; log and monitor anomalous account activity for fast detection.  

For Individuals (Easy Wins) 

  • Use a password manager and unique passwords for every site. 
  • Turn on MFA (preferably an authenticator app or hardware key). 
  • Hover before you click — inspect links, check sender addresses for subtle typos, and don’t enter credentials after arriving at a link from an email. 
  • Treat SMS and phone callbacks as suspicious for requests about credentials or money; verify independently. 
  • If you click or think you’re compromised — change passwords from a known-good device, enable MFA, run a full malware scan, and notify your employer or bank. 

Phishing and social engineering are the silent spooks in the house: they don’t break doors in—they get invited. And when the dark-web toolkit makes it easy, the threats multiply. This Halloween, treat your security like locking the door and checking the candy. 

Phishing is deceptively simple, but the underground economy and fast-moving AI technology have turned it into an industrialized threat. The good news: many countermeasures are straightforward and inexpensive (MFA, password hygiene, basic email controls). Don’t take a bite of the candy unless you’re sure it’s your friend handing it. Treat yourself to security hygiene; don’t let the attacker trick you with something sweet. 


Keep up with us! Follow us on LinkedIn!

DarkOwl and the MITRE ATT&CK Framework: Strategic Defence Against Cyber Threats 

October 28, 2025

In an increasingly hostile cyber landscape, organizations need visibility into the tactics and techniques used by threat actors. The MITRE ATT&CK Framework has become the gold standard for understanding adversary behavior, providing a structured taxonomy of real-world attack patterns.  

As showcased by Crowdstrike’s Threat Hunting report 2025, attackers are logging in rather than hacking.  

While no single platform can address every category within this comprehensive framework, DarkOwl delivers exceptional coverage of critical, high-impact darknet sources, empowering organizations worldwide to anticipate, prevent, and respond to cyber attacks with greater confidence. 

The MITRE ATT&CK Framework encompasses hundreds of techniques across dozens of categories. The Darknet is establishing itself as a critical early-warning system for reconnaissance, credential compromise, and data exfiltration threats. By providing transparent and flexible navigation of darknet data, DarkOwl maximizes detection capabilities across its core categories, offering organizations unprecedented insight into emerging threats before they impact their systems. 

Gather Victim Host Information 

DarkOwl continuously scans stealerlogs, breaches, and darknet channels and fora to identify corporate IPs, credentials, and sensitive host exposures targeting your organization or those in your supply chain. This reconnaissance capability allows you to understand what information about your infrastructure is circulating in criminal marketplaces. Early visibility into compromised host data enables rapid remediation before attackers launch exploitation attempts. 

Gather Victim Network Information 

Threat actors extensively target networks before striking. DarkOwl monitors high-fidelity darknet sources for corporate network exposures, including IP leaks, asset names, trade secrets, tools, and databases. By surfacing these exposures early, your organization gains the critical advantage of knowing what network vulnerabilities and assets have been discovered by adversaries. 

Gather Victim Identity Information 

Personal and corporate identity information is among the most valuable commodities in underground marketplaces. DarkOwl detects when your employees’ and contractors’ emails, passwords, sessions, and devices appear in stealerlogs and breach databases. Reset credentials and block fraudulent access before it materializes. 

Search Closed Sources 

DarkOwl maintains a proprietary database of historic darknet content spanning years of darknet fourm posts, marketplace listings and ransomware site chatter. This institutional knowledge allows your organization to understand not just current threats, but historical patterns that may indicate ongoing targeting. Access to this closed-source intelligence significantly accelerates threat investigation and attribution. 

Search Open Websites and Domains 

Criminal and terrorist activity thrives across Telegram, Discord, and dark web list sites where threat actors openly advertise services and share stolen data. DarkOwl scans high-fidelity OSINT sources to identify when your organization is being discussed, targeted, or compromised. This open-source monitoring complements traditional security tools by capturing threats in spaces where defenders traditionally have limited visibility. 

Compromise Accounts 

Credential theft is the foundation of modern cyber attacks, and DarkOwl detects compromised social media, email, cloud, and personal accounts from your staff and supply chain partners.  

Compromise Infrastructure 

Infrastructure compromise—including domains, servers, and networks—represents a severe threat to organizational continuity. DarkOwl detects when your infrastructure appears in leaked files and darknet chatter, while also maintaining actor profiles highlighting the hardware, software, and CVEs commonly exploited by specific threat groups. This combination of compromise detection and threat actor intelligence enables targeted defensive hardening. 

Supply Chain Compromise 

Third-party relationships create indirect attack surfaces that many organizations overlook. DarkOwl identifies when contractors, suppliers, and vendors have compromised accounts and infrastructure, providing visibility into supply chain vulnerabilities that could be leveraged to reach your organization. Understanding these indirect exposures allows you to assess risk and implement compensating controls across your extended ecosystem. 

Account Manipulation 

Account takeover (ATO) represents a critical threat vector that DarkOwl actively monitors across all cloud and system accounts, including those from former contractors or suppliers. By collecting stealer logs and highlighting device and OS exposures, DarkOwl alerts your team to anomalous account activity before it escalates into a full-scale compromise. Rapid detection of account manipulation enables swift incident response and evidence preservation. 

Modify Authentication Process 

Multi-factor authentication is a cornerstone of modern security, yet DarkOwl discovers MFA redirect URLs in stealerlogs exposing authentication mechanisms. By publishing comprehensive stealer data organized by device, DarkOwl provides your security team with concrete evidence of authentication modifications and potential bypass techniques used by attackers.  

Persistent Account Manipulation 

Sophisticated attackers maintain long-term persistence through continuous account manipulation, particularly targeting supply chain vendors. DarkOwl monitors stealerlogs to identify ongoing account misuse within your supply chain, alerting to persistent threats that might otherwise remain hidden. Early detection of persistent manipulation prevents attackers from establishing a sustainable foothold within your ecosystem. 

Access Token Manipulation: Token Impersonation and Theft 

Modern applications rely on tokens for authentication, making token theft an attractive target for adversaries. DarkOwl monitors darknet Initial Access Broker advertisements and sales activity to detect when tokens from your organization enter criminal circulation. This intelligence on token compromise allows your team to invalidate affected tokens and audit token-based access before unauthorized actions occur. 

Brute Force: Password Guessing 

While brute force attacks are blunt instruments, they remain effective when attackers possess compromised password lists. DarkOwl detects compromised passwords of staff and supply chain partners circulating on darknet breach sites, indicating that your organization faces elevated risk of password-guessing attacks. Proactive password resets based on DarkOwl’s compromise intelligence significantly reduces the success rate of these attacks. 

Reversible Encryption 

Weak password hashing algorithms create reversible encryption risks, allowing attackers to crack stored passwords at scale. DarkOwl automatically surfaces hashed passwords from corporate domain exposures in historic breach files, highlighting those with weak algorithms subject to reversal by threat actors. This capability allows your team to identify and remediate weak hashing implementations before attackers exploit them. 

Unsecured Credentials 

Credentials often leak beyond your network perimeter, appearing in messenger apps and across distributed networks like TOR, I2P, and Zeronet. DarkOwl collects these widely-scattered credential exposures to demonstrate the full scope of your credential compromise landscape. Understanding where your credentials have been exposed enables comprehensive remediation across all affected platforms and services. 

Internal Spear phishing 

Executive and supplier credentials are prized targets for internal phishing campaigns. DarkOwl continuously monitors darknet sources to detect when your executives’ and partners’ credentials are newly shared by threat actors.  

Browser Session Hijacking 

Stealer logs inherently capture browser sessions, creating direct risks of session hijacking attacks. DarkOwl actively monitors and collects stealer log data containing compromised corporate and personal browser sessions, providing visibility into hijacking risks before attackers exploit them. This intelligence enables your team to invalidate compromised sessions and investigate the scope of browser-based compromise. 

Exfiltration Over Web Service 

Data exfiltration frequently occurs across web services where attackers blend malicious activity with legitimate traffic. DarkOwl detects when your corporate data appears on darknet services including Telegram, TOR sites, ransomware platforms, and underground forums. Rapid detection of exfiltration allows your incident response team to contain the breach, quantify the exposure, and implement targeted notifications. 

External Defacement 

Attackers often publicize breaches through external defacement to maximize damage and reputation impact. DarkOwl monitors for keyword/signpost mentions of your company and alleged stolen data across TOR, I2P, file repositories, and paste sites throughout the darknet. This continuous monitoring ensures your security team detects external defacement threats before they escalate into widespread public disclosure or regulatory complications. 

Financial Theft 

Cryptocurrency plays an increasingly central role in attacks, making financial theft tracking essential for investigation and attribution. DarkOwl allows your organization to validate illicit activity by linking it to specific crypto wallet IDs involved in attacks. This capability supports forensic analysis, law enforcement cooperation, and the tracking and tracing of cryptocurrency flows used to fund future attacks. 

DarkOwl doesn’t attempt to be a universal MITRE ATT&CK solution. Instead, it excels at what matters most: providing transparent, flexible navigation of darknet data to deliver unprecedented visibility into how adversaries gather intelligence, compromise credentials, and exfiltrate data. By mastering these critical categories, DarkOwl gives organizations the early warning and actionable intelligence needed to transform defense from reactive to proactive. 

In today’s threat landscape, organizations need platforms that go deep rather than wide. DarkOwl’s specialized focus on darknet reconnaissance and threat actor activity provides exactly this—strategic depth where it matters most. For security teams committed to staying ahead of emerging threats, DarkOwl represents the specialized intelligence layer that bridges the gap between your internal detection systems and the criminal activity planning your compromise. 

Prepare for attacks before they begin. Detect compromise before it escalates. Respond with confidence backed by darknet intelligence. That’s the DarkOwl advantage in the MITRE ATT&CK era.  


For specific details on how DarkOwl meets MITRE ATT&CK framework, contact us.

Q3 2025: Product Updates and Highlights

October 23, 2025

As we wrap up Q3, we’re excited to share a major expansion to our investigative capabilities within Vision UI—introducing a powerful new module designed specifically for darknet marketplace research. This release reflects our continued commitment to delivering actionable intelligence with precision and depth. 

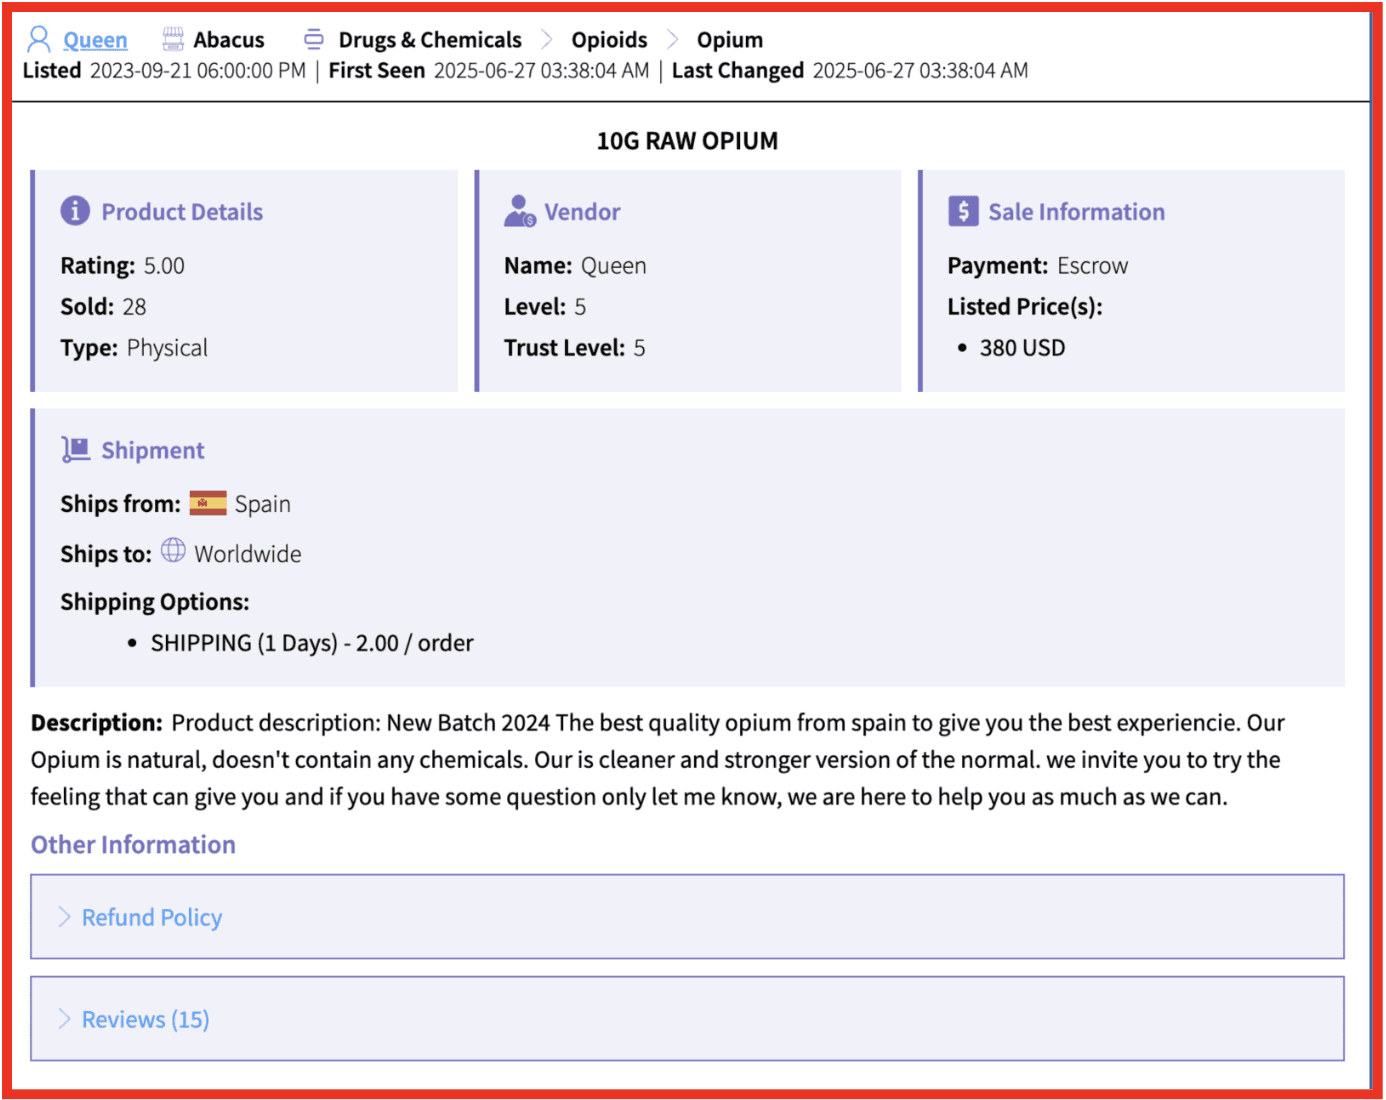
DarkOwl has made substantial updates to the way we capture and store data collected from product listings on darknet marketplaces. Darknet marketplace listings now include up to 26 content fields—including listing titles, categories, vendors, shipping information, prices and payment options, reviews, refund policies, and many more. Access our full listing collection through our new Markets module in Vision UI, or Markets endpoint options in Vision API.  

Figure 1: An example of a market listing collected from Abacus market, prior to its shutdown in July 2025

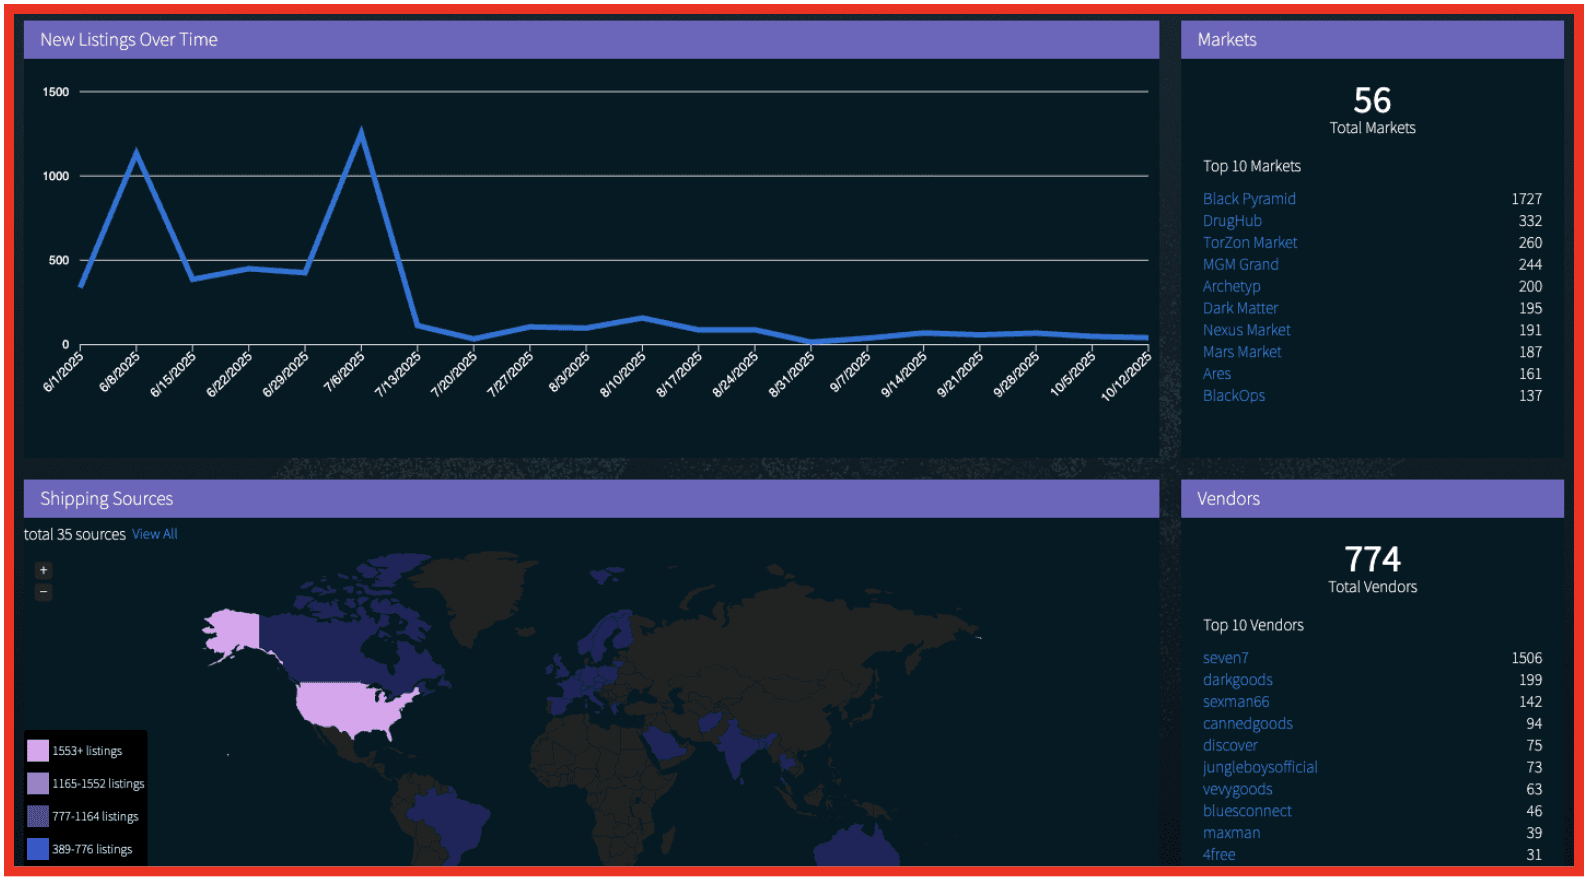
Search by product name, vendor, or even a market name—and see aggregated information and visualizations about your result set. This view provides: 

  • A timeline of new listings 
  • A map of Shipping Sources by volume 
  • Metrics of total and top markets  
  • Metrics of total and top vendors
Figure 2: Aggregated information for a product search ‘Xanax’. 

Additional Features in our Markets module 

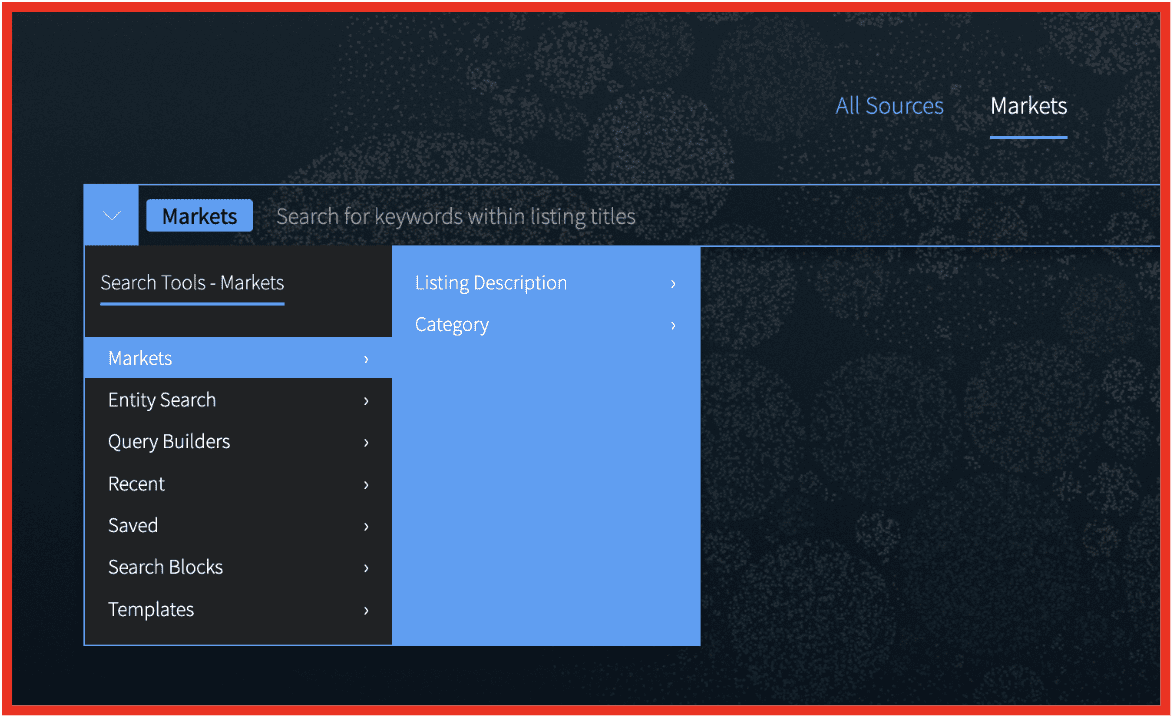
  • Specialized search operators/filters: Search listings by Keyword, Vendor, Market, Category, Price, or other market-specific option. 
  • Additional date options: Search listings or sort results by when the listing was First Seen or Last Changed on the market. 
Figure 3: The Markets module provides customized searching and retrieval for product listings. Listings are also available in the All Sources general search, which provides a uniform experience across all data types within DarkOwl Vision. 
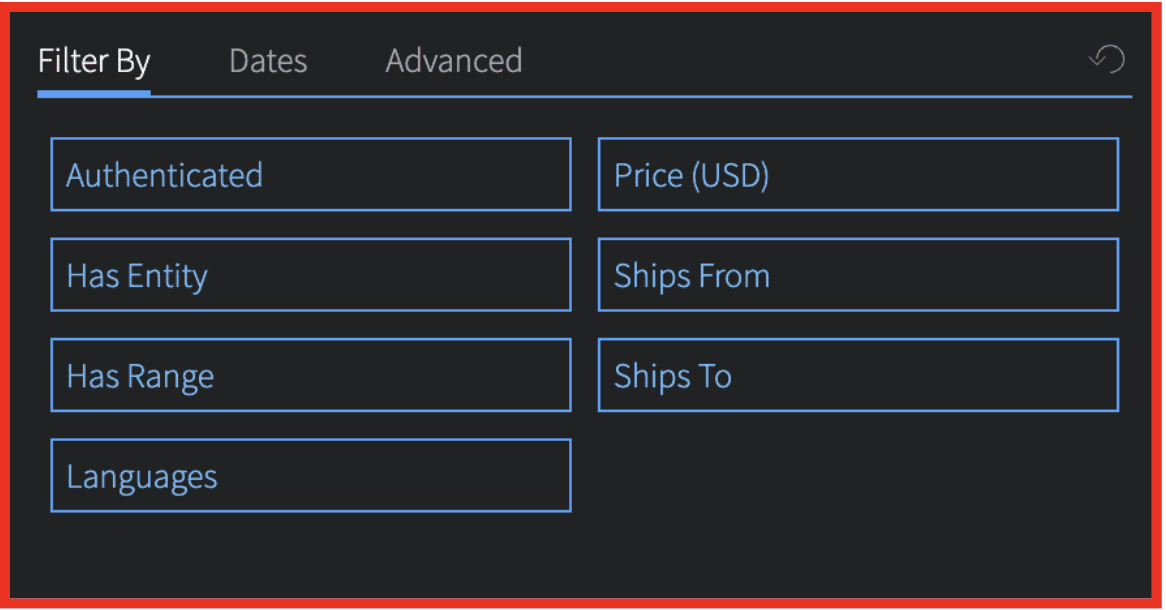
Figure 4: Additional filtering options in this module include Price, Shipping Source, and Shipping Destination.

Marketplace Research in Vision API 

We’ve launched three new endpoints for programmatic access to our enhanced darknet marketplace data. These endpoints provide optimized searching, filtering, and formatting specific to market listing content: 

  • The Markets Search endpoint for an optimized experience and market-specific parameters. 
  • The Markets Summary endpoint provides aggregate information about your search result set. 
  • The Listing Detail endpoint retrieves all information from a single market listing. 

You can continue to find market listing results using our Search API endpoint, which have been enhanced with vendor, price, shipping information, as well as a reference to pull the full listing content from the Listing Detail endpoint if desired. 

We’ve made several search experience upgrades, which streamline and improve search workflows in Vision UI: 

  • Source Domains Filter: The input field has been redesigned for a cleaner, more intuitive experience, making it easier to include or exclude source domains in your searches. 
  • Chat Channel Filters: Our chat filters now support exclusion, allowing you to refine result sets by removing specific channels. 
  • Search Block Expansion: Chat types are now available as search block types—ideal for monitoring high-interest sources. 
Figure 5: The new Source Domains filter provides easier ways to filter to or exclude specific domain sources. 

When your search results are from data leaks, users can review additional information curated by DarkOwl analysts, giving you enrichment on the data leak. The descriptions below are all available in our Leak Explore UI feature, or Leak Context API endpoint. 

USA fullz info cc x200

A post on LeakBase, a hacking forum, on January 28, 2025, linked to the file: ggjtv.txt. According to the post, there are 200 lines of full USA credit cards. Data exposed includes names, email addresses, CVV, physical addresses, expiration dates, dates of birth, Social Security Numbers, phone numbers, passwords, mobile numbers, and credit card numbers.

etsy.com

Data purported to be from Etsy was posted on BreachForums, a hacking forum, on December 5, 2024. According to the post, the leak consists of 3,600 rows of data, containing 3,535 unique Social Security numbers, 1,915 email addresses, and 32 email domains. Data exposed includes customer information, email addresses, physical addresses, genders, dates of birth, SSNs, phone numbers, mobile numbers, user identification number (UID), company names, and product data. The threat actor noted the leak contained additional files of parsed and deduplicated SSN, emails and email domains from the raw leak data, noting the files that contained emails and email domains had free email services removed from them. While the victim data is listed as Etsy, the post indicates the company exploited by the MOVEit vulnerability was Delta Dental.

3.9M Allianz Life 2025.19.08 Sample

Data purported to be from Allianze Life, obtained via Salesforce, was posted on scattered lapsus$ hunters, a Telegram channel, on August 19, 2025. According to the post, the leaked data include Salesforce’s “Accounts” and “Contacts” tables and contains a total of 3.9 million sensitive records, though only 2.8 million were publicly posted. Data exposed includes customer and partner data, names, addresses, dates of birth, and professional information. The Threat Actor indicated that the full leaked database was posted for sale for $10,000 US, with a final sale of $9,000 for the complete database completed on August 21, 2025 by Season via a BitCoin transaction. According to media reports, Allianz Life confirmed a third-party CRM platform was accessed by a threat actor on July 16, 2025. The Threat Actor group is a combination of Scattered Spider, ShinyHunters and Lapsus$. Telegram channels associated to the group are quickly banned, with backup channels being regularly created to repost content associated to their recent activities.

Serasa Experian 2.9 GB

Data purported to be from Serasa Experian was posted on LeakBase, a hacking forum, on September 10, 2022. According to the post, a hacker known as JBR initially posted the file that affected 223 million users. Data exposed includes names, genders, dates of birth, and CPF (Cadastro de Pessoas Físicas) numbers. The dataset includes static identifiers such as CPF numbers and dates of birth. Consequently, the age of the leak does not lessen the potential impact of the exposed data. A February 2023 post on BreachForums from a user named “TheBlob” explained that the original breach was carried out by a Brazilian hacker known as “JustBr” (or “JBR”), who initially advertised the data on the now-defunct forum, RaidForums. The complete database was reportedly sold for $30,000, while portions, which consisted of 40 parts, were available for $755 each.


Curious how these features and data can make your job easier? Get in touch!

Command-and-Control Frameworks: Post Exploitation in Plain Sight

October 21, 2025

Command-and-control (C2) frameworks are used by both red teams and cybercriminals. They provide a wide range of functionality and capabilities that make post-exploitation tactics easier and more effective. In simple terms, a C2 acts as a central server that connects to, communicates with, and manages compromised systems. It establishes persistence and allows the operator to control dozens of infected machines from one central environment. 

There are many reasons why C2 frameworks are popular among attackers and red teams. Most frameworks offer operators powerful capabilities such as privilege escalation, network pivoting, scanning, and data exfiltration. They are so useful, in fact, that cybersecurity companies have developed their own commercial C2 products for ethical red-team engagements. Cobalt Strike is often regarded as the industry leader for production-grade post-exploitation operations due to its broad set of easy-to-use features, making engagements accessible even to less technically skilled operators. Open-source options are also widely available, with frameworks like Covenant, Sliver, Metasploit, and many others freely downloadable from GitHub. 

Regardless of the framework, stealth is the most critical factor for both ethical red teams and cybercriminals. Security Operations Centers (SOCs) constantly monitor traffic and look for suspicious packets moving through the network. No matter how polished a C2 product may appear, it is useless if detected and blocked. In addition to internal monitoring, dedicated threat-hunting teams at Microsoft, Google, Meta, Cisco, CrowdStrike, IBM, and others search for malicious infrastructure outside their own networks as well. 

Offensive security operators understand the importance of obfuscating traffic and minimizing detection. Great effort is made to ensure payloads are covertly delivered, network traffic is routed inconspicuously, and C2 frameworks are hidden behind innocent-looking websites. This constant need for concealment has led to several tactics, techniques, and procedures (TTPs) that blue teams, SOCs, and organizational leaders should be aware of. 

“Small Sieve,” for example, uses the Telegram bot API to communicate over HTTPS and relay commands to and from malicious C2 servers. To defenders, this HTTPS-encrypted traffic moving through the organization’s network may appear normal. Since Telegram is not considered a malicious service, such traffic could easily be overlooked by blue teams and SOC analysts. 

Throughout 2021, a suspected Iranian-backed threat group known as “Oil Rig” conducted an operation called “Outer Space” targeting Israeli organizations. To conceal their malicious traffic, they compromised an Israeli human resources server and repurposed it as a dedicated C2. Subsequent operations appeared to originate from this trusted source. 

This technique is not limited to concealing C2 servers. When a stage-one payload needs to download additional malware, threat actors often host stage-two payloads on trusted platforms that are less likely to raise alarms. Saint Bear, a Russian threat actor active against Ukraine and Georgia as early as 2021, frequently used Discord’s content delivery network for hosting malicious files. To defenders, this traffic appeared to come from Discord, making it harder for intrusion detection systems to flag as suspicious. 

The popularity and awareness of these C2 techniques have expanded beyond nation-state actors and advanced attackers. Using the DarkOwl Vision platform, we can observe multiple discussions emphasizing the importance of stealth in C2 operations. 

Source: DarkOwl Vision

One user highlights the software’s ability to “function covertly, employing stealthy techniques to avoid detection… and [avoid detection from] network security monitoring tools”. 

The following example describes another piece of malware that uses Telegram as its command-and-control platform for communication with infected machines. Again, the author boasts of the software’s “low detection rates due to its advanced obfuscation techniques”. 

Source: DarkOwl Vision

For cyber defenders and blue teams, it is critical to understand these TTPs. In some cases, an SOC analyst may identify something suspicious within an otherwise benign Telegram packet. In others, endpoint detection and response platforms can be tuned to better recognize this malicious traffic. More importantly, the cybersecurity community must accept that these TTPs will continue to evolve into more sophisticated methods. Just as blue teams grow comfortable detecting one technique, red teams adopt the next lesser-known approach that has yet to be widely publicized. 

Resources such as attack.mitre.org are invaluable for fingerprinting and understanding the TTPs that a company, organization, or industry might face during an incident. After an attack, investigators and cyber experts often publish their findings, which can help future targets prepare to identify and thwart similar threats. 

In this blog, we explained how powerful C2 frameworks can be in maintaining stealthy operations for both red teams and cybercriminals. We highlighted examples where advanced persistent threats (APTs) leverage trusted applications and networks to conceal post-exploitation activity. The dark web remains a rich source of intelligence, where forums and discussion boards provide valuable insight into evolving trends and shared techniques. Ultimately, staying ahead in this cyber cat-and-mouse game requires defenders to remain adaptive, vigilant, and continuously informed.


Curious how DarkOwl can help you? Contact us.

Cyber Hygiene at Work & Home 

October 16, 2025

Since the Covid Pandemic in 2020, it’s been proven time and again that the boundary between work and home is thin. Your “office” might be a kitchen table. Your “help desk” might be your teenager asking for the Wi-Fi password. And while we like to think that security is something handled by IT or left to our antivirus, the truth is simpler. It’s your daily habits: at work and at home. They can decide whether attackers get a foothold. 

Below is a field-tested guide to cyber hygiene that treats all aspects of your life with the reality that they are all connected. Use it to harden the places you click, type, scan, and share, no matter where you are. 

  • Turn on MFA for every important account. It adds a second proof (app prompt, code, or security key) so a stolen password alone won’t grant access.
  • Use a password manager to generate and store long, unique passwords for each site. This prevents one breach from unlocking multiple accounts.
  • Keep everything current—laptops, phones, browsers, and even routers/IoT. Updates patch known flaws attackers actively exploit.
  • Slow down on links and attachments. Verify unusual requests on a separate channel and report suspicious emails/messages to IT.

Not all MFA is equal. SMS codes and push prompts can be bypassed (push fatigue, SIM swaps). Where available, use FIDO2/WebAuthn security keys or passkeys for phishing-resistant authentication (CISA). 

Passkeys use public-key cryptography, so there’s nothing reusable for criminals to steal or phish—and they’re now supported across major platforms. If a site offers passkeys, turn them on (FIDO Alliance). 

Step 2: Treat your home like a branch office 

Attackers don’t care if they land on a CFO’s laptop or a teenager’s tablet, both act as launchpads to your data. 

Create separate networks for primary devices, guests, and IoT (cameras, TVs, smart speakers). This limits blast radius if one thing gets infected. At minimum: Primary, Guest, and IoT SSIDs (U.S. Department of War). 

Change default passwords, disable WPS, enable WPA3/WPA2, update firmware, and hide/rename default SSIDs that leak your router model (CISA). 

Firewalls, routers, VPN gateways, and internet-facing boxes need regular patching—treat them like crown jewels, not appliances (CISA). 

Kids and elders are prime targets because they’re helpful and curious. Set up non-admin accounts, turn on automatic updates, and require approval for new installs. Teach a simple rule: no scanning random QR codes. EVER! QR-based phishing (“quishing”) is rising—from stickers on parking meters to QR codes sent in the mail. 

Step 3: Close the “human gaps” at work 

Technology can’t save us from workflows that reward speed over safety. 

Clicking a link, approving an MFA prompt, or running an attachment is a risk decision. If something feels rushed or emotional, pause and verify on a separate channel. 

Never approve a push you didn’t initiate; report repeated prompts to IT. Ask your org to move critical apps to phishing-resistant MFA (CISA). 

People use unsanctioned tools to get work done. Offer safe, approved alternatives—and make them easier than the workaround. 

Use different browser profiles (or separate browsers) for corporate vs. personal accounts to avoid cross-contamination of cookies, extensions, and autofill. 

Step 4: Five Pillars of Cyber Hygiene (with “Work” and “Home” plays) 

Think of these as your daily vitamins—boring, effective, non-negotiable. 

  • Work: Require MFA everywhere; prefer FIDO2 keys or platform passkeys for high-risk roles. Review admin privileges quarterly (CISA). 
  • Home: Use a password manager for everyone in the house. Turn on passkeys where offered. Store account recovery codes securely (not in your email) (CISA). 
  • Work: Enforce OS/browser/driver updates. Block unsigned macros; restrict USB media. 
  • Home: Auto-update everything. On kids’ devices, require approval for new apps and in-app installs. Back up photos/docs to a service or external drive (3-2-1 rule). 
  • Work: Patch edge devices; audit remote access and VPN portals; disable unused services (CISA). 
  • Home: Separate SSIDs: Primary | Guest | IoT. Change router defaults; update firmware; prefer WPA3 (U.S. Department of War). 
  • Work: Maintain an allow-list of approved software and browser extensions. Monitor OAuth app grants to corporate accounts. 
  • Home: Delete apps you don’t use. In browsers, keep extensions minimal and reputable; disable third-party cookies; use separate profiles for kids. 
  • Work: Run short, contextual training (60–90 seconds) tied to real incidents: “Why this phish worked,” “How that MFA prompt slipped through,” etc. 
  • Home: Have a five-minute family drill: “If a pop-up says we’re infected, what do we do?” (Answer: close the browser, don’t call numbers, tell an adult.) 

Step 5: A 15-Minute Monthly Tune-Up 

Set a recurring reminder synced to all your devices will help and knock these out 

  1. Review your password manager for weak/reused passwords; rotate any shared family passwords. (CISA) 
  1. Check bank and email alerts (sign-ins, transfers, forwarding rules). 
  1. Audit browser extensions and remove anything you don’t use. 
  1. Test backups by restoring a file (don’t wait for an emergency). 

Step 6: If you slip (because we all do) 

  • At work: Unplug from the network if malware is suspected; call IT; do not try to “clean it” yourself; preserve evidence (timestamps, screenshots). 
  • At home: Power down the affected device; change important account passwords from a different device; call your bank if credentials were exposed; reset router and update firmware; reinstall OS if necessary. 
  • If you scanned a suspicious QR code or clicked a fake login: reset any password, you entered and revoke OAuth sessions for the affected app. Watch for new MFA prompts you didn’t initiate. 

Cyber hygiene isn’t a fancy toolkit; it’s a set of small, repeatable habits your whole circle can manage. Enable MFA that resists phishing. Use passkeys when available. Update relentlessly. Segment the home network. Slow down on links, attachments, QR codes, and MFA prompts. These are the same moves that security teams recommend, because they meaningfully cut risk at work and at home (IT Services). 

Do this now, and when Clean Out Your Computer Day rolls around next February, you’ll be cruising through a short, satisfying tune-up instead of tackling a backlog. 

Finally, the next time a child asks for your phone at dinner or a relative forwards a “too-good-to-be-true” link, remember: YOU may be the gateway (for better or worse).  

Make the safer choice first. 


Keep up with all tips shared by DarkOwl. Subscribe to email.