Author: DarkOwl Content Team

DarkOwl at IT-SA 2026: Building Momentum Across the DACH Region

November 17, 2026

From October 27–29, DarkOwl joined thousands of cybersecurity professionals at IT-SA 2026 in Nuremberg, Germany. As one of Europe’s leading IT security exhibitions, IT-SA provided an opportunity to connect with existing customers, meet new prospects, and explore how darknet intelligence is becoming an increasingly important component of cybersecurity strategies across the German-speaking market.

Representing DarkOwl were Iyiola Awosika and Magnus Svärd, who spent three days meeting with security professionals, demonstrating DarkOwl Vision, and discussing the evolving role of darknet data in threat intelligence, third-party risk management, and security operations.

IT-SA brought together a predominantly German-speaking audience, with conversations taking place in both German and English, and fosters an environment for meaningful, in-depth conversations with attendees.

Throughout the event, the team connected with cybersecurity practitioners, technology providers, consultants, and organizations interested in expanding their visibility into darknet activity.

A recurring theme across these discussions was the need to move beyond traditional security data sources. Organizations are increasingly recognizing that activity on the darknet can provide valuable context for understanding potential threats, identifying exposed information, and strengthening their approach to risk management.

For DarkOwl, these conversations reinforced the importance of making darknet intelligence accessible, actionable, and easier to incorporate into existing security workflows.

Some of the most valuable conversations at IT-SA came from reconnecting with existing customers and partners. These conversations offered valuable insight into how customers are looking to operationalize darknet intelligence at scale. Whether through more efficient workflows, structured data, or API-driven integrations, the demand for flexible ways to incorporate darknet intelligence continues to grow.

Beyond existing customer relationships, IT-SA introduced DarkOwl to several organizations exploring how darknet data could enhance their security capabilities.

Among the conversations were organizations interested in using darknet intelligence to strengthen third-party risk management, gain greater visibility into potential exposures, and better understand activity targeting their customers and infrastructure. These discussions highlighted demand for deeper darknet visibility beyond what organizations currently receive through their existing security solutions.

These conversations demonstrate the breadth of potential applications for darknet intelligence, extending beyond traditional cybersecurity teams into risk management, critical infrastructure, and broader security consulting.

One of the clearest takeaways from IT-SA was the growing interest in automation and integration.

Several conversations centered on how organizations can incorporate darknet intelligence into their existing technology environments without creating additional manual work. From customers exploring API-only licensing to organizations looking for more structured data and automated monitoring capabilities, there was a consistent emphasis on making intelligence easier to operationalize.

This shift reflects a broader evolution in the cybersecurity landscape. Organizations do not simply need more data; they need relevant intelligence that can be integrated into existing workflows, support faster analysis, and help security teams make more informed decisions.

DarkOwl’s Vision platform and API offerings provide different ways to meet these needs, whether organizations are conducting hands-on darknet investigations or incorporating darknet data into larger security and intelligence platforms.

The conversations at IT-SA reinforced the importance of continuing to evolve alongside customer requirements and ensuring darknet intelligence can support increasingly automated security operations.

The event highlighted an engaged cybersecurity community with growing interest in the value of darknet intelligence. From organizations looking to improve third-party risk management to technology providers exploring API integrations and automation, the conversations reflected a market increasingly interested in understanding what happens beyond the traditional surface web.

For DarkOwl, the value of attending extended well beyond the exhibition floor. The opportunity to meet directly with customers, hear firsthand product feedback, demonstrate new capabilities, and better understand regional requirements makes IT-SA an important event for continued business development in Europe.

A big thank you to everyone who stopped by the DarkOwl booth, shared their perspectives, and took the time to connect with our team. We look forward to continuing these conversations and building on the momentum from Nuremberg.


Interested in learning how darknet intelligence can strengthen your security operations? Explore DarkOwl Vision or request a demo.

Threat Intelligence RoundUp: October

November 03, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. Treasury Dismantles Major Hamas Financing Network – U.S. Department of the Treasury

On October 2, 2026, the U.S. Department of the Treasury announced sanctions against individuals and organizations involved in a Hamas financing network that allegedly moved more than $2 million to the group between 2020 and 2026. According to Treasury, the network operated through France-based organizations that presented themselves as charities raising humanitarian aid for civilians in Gaza, while actually directing donations to a Hamas financial facilitator in Gaza. The network also used cryptocurrency to transfer hundreds of thousands of dollars and promoted fundraising accounts through social media. Treasury stated that $1.5 million of the funds was raised after the October 7, 2023, Hamas attack on Israel. Read full article.

2. Hackers stole Pentagon personnel records of over 3 million people – Bleeping Computer

The Pentagon recently reported a major data breach that exposed personal information belonging to nearly 3 million people in October 2025. Hackers accessed a Defense Manpower Data Center (DMDC) system containing sensitive information, including names, Social Security numbers, dates of birth, and other personal and employment details. The affected individuals include military personnel, civilian employees, contractors, veterans, and others connected to the Department of Defense. Officials say the vulnerability has been fixed and an investigation is ongoing. Read More.

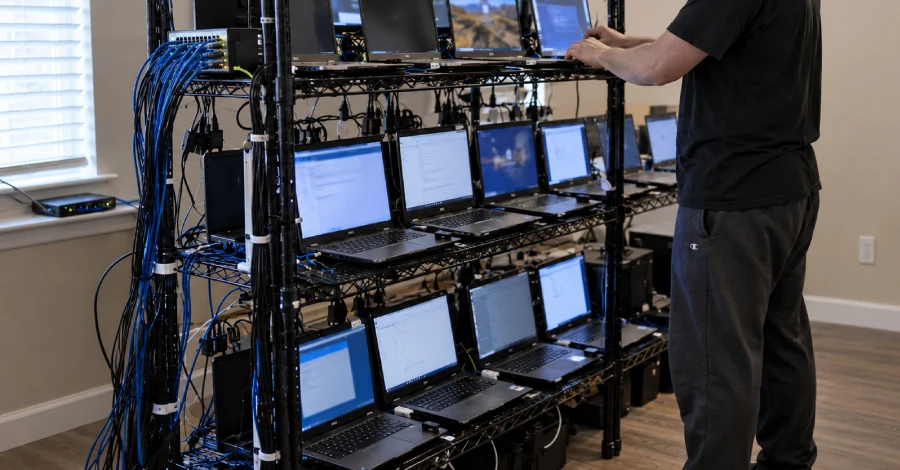
The U.S. Federal Bureau of Investigation (FBI), in coordination with the Department of Justice (DOJ) and cybersecurity firm CrowdStrike, disrupted more than 40 suspected “laptopfarms” across Texas as part of an operation targeting North Korean remote IT worker fraud schemes. These laptop farms were residences used by U.S.-based facilitators to host and operate laptops supplied by American companies, allowing North Korean IT workers to appear as legitimate U.S.-based remote employees while concealing their actual identities and locations. According to U.S. authorities, the workers allegedly used stolen or falsified identities to secure employment with more than 70 U.S. companies across industries including healthcare, communications, retail, manufacturing, and cybersecurity support. The FBI seized approximately 187 laptops and keyboard, video, and mouse (KVM) devices used to facilitate the scheme, which reportedly generated around $3 million in revenue believed to have been transferred to entities controlled by North Korea. Read more here.

The Federal Bureau of Investigation (FBI) and the U.S. Department of Justice (DOJ) seized seven internet domains to disrupt cyber operations associated with Flax Typhoon, a China-linked advanced persistent threat (APT) group connected to Beijing-based Integrity Technology Group. According to U.S. authorities, the group used two primary tools, MicroScan and FishHub, to target critical infrastructure and organizations in the United States and internationally. MicroScan is a Python-based vulnerability scanning tool containing more than 1,300 scripts designed to identify security weaknesses in websites, applications, and network systems. FishHub was used to conduct spear-phishing attacks, gain unauthorized access to victim networks, and potentially steal sensitive information. Investigators also connected the group to a large Internet of Things (IoT) botnet called Raptor Train, which infected hundreds of thousands of devices before a previous FBI disruption operation in September 2024. Read here.

5. Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites – The Hacker News

A researcher at the cybersecurity company NorForge observed a Chinese-speaking hacker breach more than 100 company websites using autonomous AI agents. According to the report, the AI agents attempted to compromise more than 1,200 sites; among the 100 compromised ones were Deere, SharkNinja, and Cummins. Snorre Fagerland, the researcher who observed the incident, discovered it by scanning the web for “inadvertently exposed instances of Cairn,” an AI-powered system often used by hackers. Fagerland observed approximately two dozen instances of Cairn being used in malicious ways—one of which was by the Chinese-speaking hacker. Learn more.

6. Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers – The Hacker News

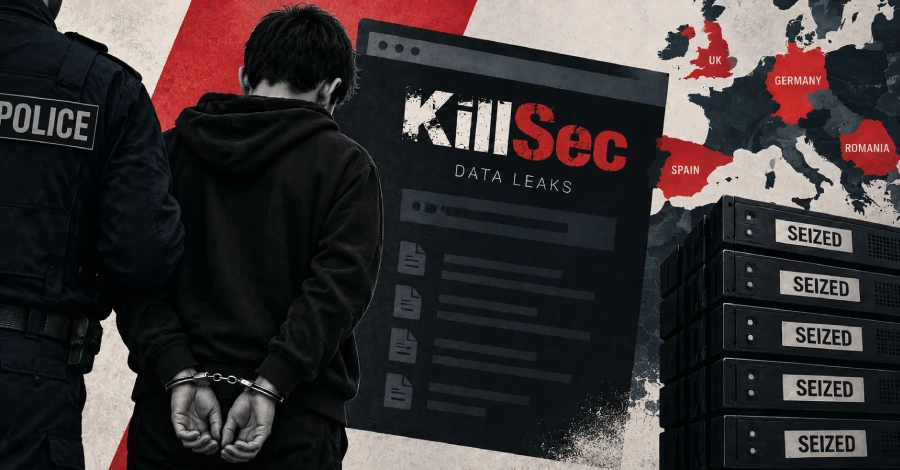
On 30 September 2026, an international law-enforcement operation led by German authorities resulted in three arrests linked to the KillSec ransomware group. The suspected 16-year-old main operator was arrested in Alicante, Spain, where Spanish police also searched a home and a hotel office. A 24-year-old suspect was arrested in Romania, with searches carried out in Bucharest and Vaslui County. The third suspect was arrested in the United Kingdom and is reportedly linked to an extradition request from U.S. authorities. In addition to the arrests, police carried out eight searches across Spain, Greece, Romania and the UK, while seizing five servers and securing at least 110 terabytes of data. Read full article.

7. US soldier gets 70 months in prison for extorting 10 tech, telecom firms – Bleeping Computer

Cameron John Wagenius (known online as ‘kiberphant0m’ and ‘cyb3rph4nt0m’) has been sentenced to 70 months in prison for hacking and extorting 10 technology and telecommunications companies. According to records, the attacks occurred from April 2023 to December 2024 while Wagenius was on active duty with the U.S. Army. Wagenius and his accomplices used stolen credentials to access victim networks, coordinated their activities through Telegram, and later attempted to extort organizations by threatening to publish or sell stolen data on cybercrime forums. The conspirators also sold some of the stolen information and used it to conduct additional fraud, including SIM-swapping, while attempting to extort at least $1 million from data owners. Wagenius was sentenced to 70 months in prison and ordered to pay $294,978 in restitution for his role in the scheme. Read full article.

8. Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks – The Hacker News

Cybersecurity researchers at Dutch mobile security firm ThreatFabric uncovered a new Android banking trojan called Hirudo, which uses modified versions of legitimate banking applications to bypass built-in security protections and facilitate financial fraud. The malware targets users across several countries including Indonesia, China, India, Mexico, Morocco, and Thailand, with eight Indonesian banking apps identified as targets for replacement with malicious versions. Hirudo is distributed through seemingly legitimate shopping, entertainment, and video-streaming applications that prompt users to install the malware through fake in-app updates. Once installed and granted the necessary permissions, it can steal banking credentials, payment PINs, SMS messages, and device information, capture screens and camera activity, and give attackers remote control of infected devices. What makes Hirudo particularly concerning is its ability to replace genuine banking apps with modified copies containing tools designed to deceive security mechanisms, including application-signature verification, accessibility-service checks, screen-capture protections, and Google Play Integrity checks. Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Q3 2026 Product Updates and Highlights 

October 20, 2026

A look at new capabilities, platform improvements, and data updates across July, August, and September. 

This quarter centered on three themes: Cases as the single place for your searches, findings, and alerts; clearer, more targeted search and Explore views; and the first structured Data Leak records, alongside new market analytics and notable leaks collected this quarter. Keep an eye out for more structured data in the coming quarters. 

Investigations produce three kinds of output: searches, the findings those searches turn up, and the alerts that tell you when something changes. Until now, personal tools and Cases held those pieces in different places. This quarter we brought them together. Cases are now the one place where a search is saved, a finding is captured, and an alert is reviewed. With everything in one place, we focused on making Cases faster to work in – starting where the work begins.  

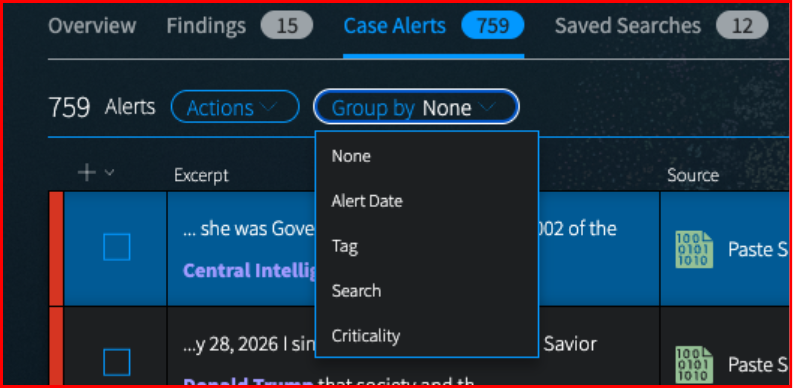
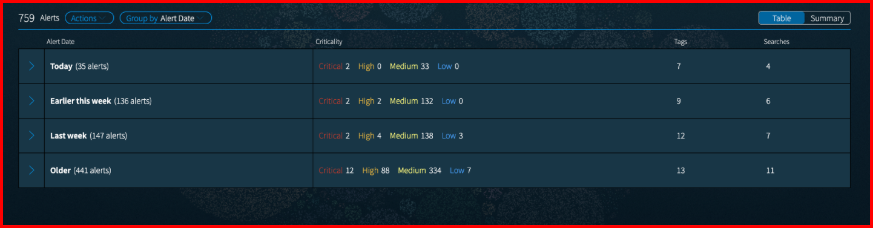
The Search Bar Tools menu now includes Case Tools that puts your searches and blocks one click away. You can Pin a Case as your default, so you don’t interrupt your flow with every Finding. Alerts get the same treatment. A new Case Alert Group feature organizes your alerts by Alert Date, Tag, Search, or Criticality, and each group shows a summary, so you can decide where to start. When an investigation wraps up, Case Archiving separates Active and Archived Cases on the Cases home page, which keeps finished work out of the way. 

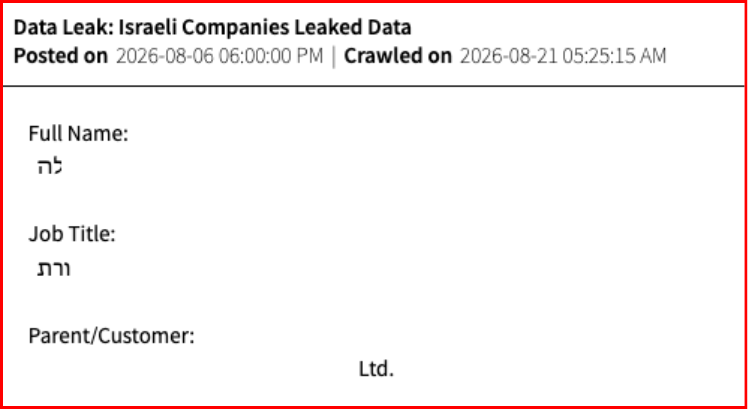
Structured Data Leaks, now live in Vision, turn each leak into records you can query, filter, and read by field. Each record is organized into up to 40 attributes, with classification tags that help surface corporate, financial, identity, and device threats. The original headings from the source are retained and displayed alongside their data values, so context from the source file is not lost. Date options are richer as well, with both collected and posted dates available, and there are many more new features to explore. 

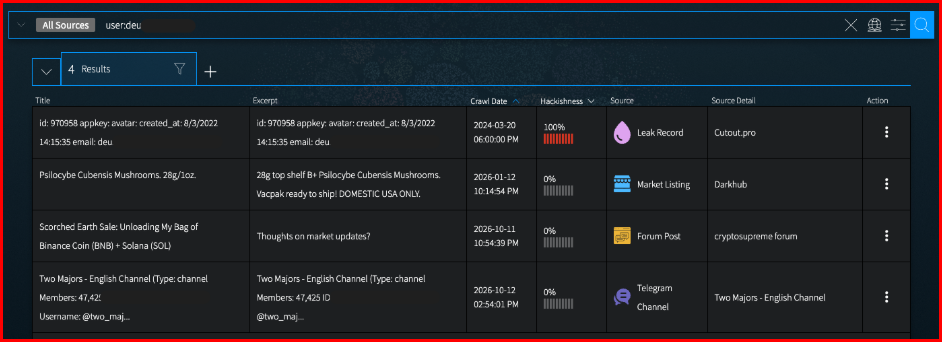
Querying is sharper too. Username and alias searches now reach structured leak records, and they are especially powerful alongside other DarkOwl sources such as Forum Posts and Chat Messages when you are tracking actor activity. A handle that appears in a leak record can be followed to the forums and chats where the same handle is active. 

Structured leak content is supported today in general search and the Search API, and more is coming. Customers can request beta access to our upcoming Leaks API, which will add enhanced query functionality and summarization features. 

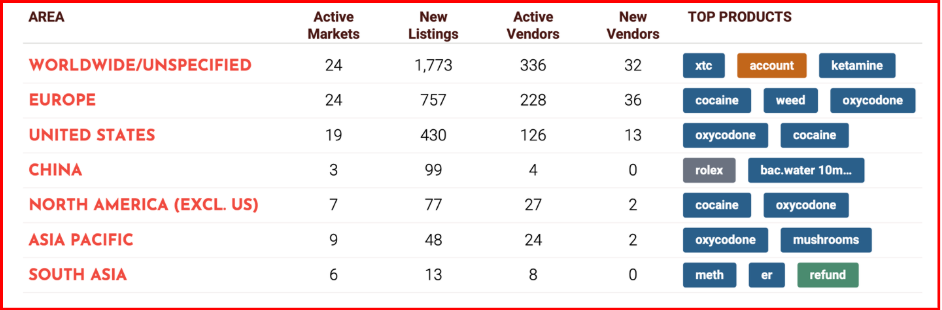
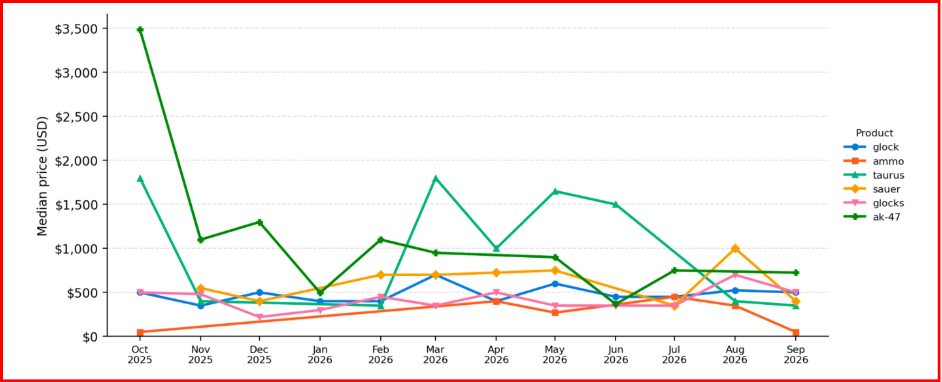
Darknet market data is most useful when it becomes a view you can act on. DarkMart™, DarkOwl’s structured collection of darknet marketplace content, gives us the listings, vendors, prices, and shipping details to build that view. This quarter we added the ability to turn it into intelligence reports. Product Category Reports go deep on a single category found on darknet markets, such as drugs, pharmaceuticals, or weapons. Top products with median prices, leading vendors, biggest movers against the previous period, pricing compared with the 12-month median, active markets, and shipping flows are all included. Activity and Trend Reports show markets that are new or going quiet, popular products moving across markets, pricing trends, emerging products and vendors, and geographic shipping trends. 

Vision UI and the Vision API gained many new features this quarter. The updates below are a sampling: 

  • Data Source Icons: We introduced a new search result layout with Visual Icons, making it easy to scan result types.  
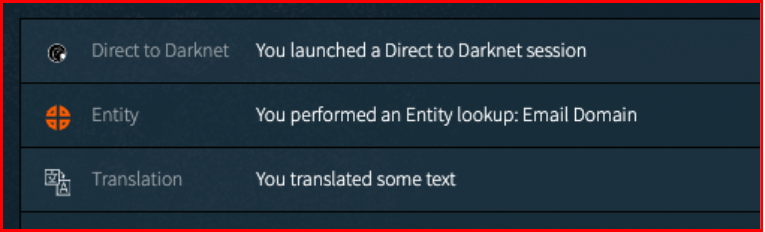
  • Usage and Activity Reporting: Usage metrics for Entity lookups, Translations, and Direct to Darknet launches now appear on the Activity page and in Usage Report downloads, so you can report a fuller picture of how Vision UI is used. For teams that use Vision API, the Usage API now supports filtering by date. 
  • Data Leaks in Entity Explore and Entity API: Cryptocurrency, Card, and BIN entities in Entity Explore now include a Data Leak summary box, and Entity API returns data leak information in the response. 

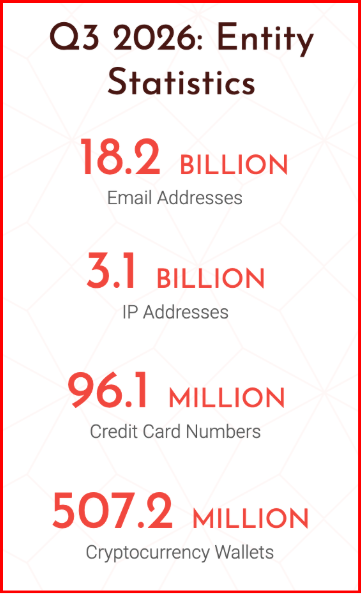
Our data collection team continues to astonish us with the quantity of data made available across all DarkOwl products, including year over year growth for the number of email addresses, domains, credit card numbers, IP addresses, and crypto addresses. 

Notable Content Collected 

DarkOwl indexed a number of leaks attributed to ShinyHunters this quarter, and we are following the group closely. The victims span industries: healthcare and life sciences (Accord Healthcare, Lumenis), travel and retail (Carnival Corporation, Ralph Lauren, [JC Penney]), technology and communications (Fluke Corporation, American Tower Corporation), financial services (Abrigo, BOK Financial), and education and government (Houston City College, Moody Bible Institute, the Council of Europe). For recent activity from the group, read DarkOwl’s September 25, 2026 post, FBI Allegedly Hacked by ShinyHunters.  

BOK Financial 

Data purported to be from BOK Financial was posted on ShinyHunters on August 28, 2026. The post claimed 46 GB or more of data, and DarkOwl collected 48.3 GB. BOK Financial serves consumer, business, and wealth clients across the American Midwest and Southwest. 

DarkOwl’s file tree analysis shows a large and varied collection that includes 848 JSON files, 707 HTML files, 398 SQL files, 76 Excel workbooks, 63 PDFs, 59 email messages, and 22 configuration files. Source code, API keys, and tokens appear among the exposed content, which makes this leak relevant beyond customer data: credentials and code give an adversary a path into systems as well as into records.  

Police National Legal 

Data purported to be from the Police National Legal Database (PNLD) was posted on ExfilSquad on August 3, 2026. According to the post, the leak contains 135,000 law enforcement contact records, including full names, email addresses, and police jurisdictions. DarkOwl indexed 135,065 records, which matches the claim. 

PNLD has provided a legal database to the 43 Home Office police forces in England and Wales and the British Transport Police for over 30 years, and its customers include the Crown Prosecution Service and Trading Standards. In a public statement on August 2, 2026, PNLD acknowledged a July 26 cyber incident that exposed contact information of police staff, partner organizations, and public users. Contact records tied to police jurisdictions can support targeted phishing and social engineering of law enforcement personnel. 

For more on the group that posted this leak, read DarkOwl’s August 6, 2026 analysis, ExfilSquad: A New “Data extortion group” Player Claiming High-Profile Breaches Across the US, UK, and Beyond. It also covers PNLD’s public confirmation of the incident. 

Council of Europe

Data purported to be from the Council of Europe (coe.int) was posted to the ShinyHunters data leak site in June 2026. According to the post, the group claimed to have exfiltrated 297GB of data across 429,000 files, from multiple Council of Europe divisions, including human resources, the Secretariat, the Parliamentary Assembly, and the European Directorate for the Quality of Medicines & HealthCare. Data exposed includes employee names, IDs, addresses, phone numbers, dates of birth, tax and social security information, and medical records, along with payroll and bank account information.

Carnival Corporation and Plc

Data purported to be from Carnival Corporation was posted by ShinyHunters, which listed Carnival Corporation on its “pay or leak” portal on April 18, 2026. According to the post, the leak contained 8.7 million records with 7.5 million unique email addresses and included fields indicating the data related to the Mariner Society loyalty program operated by Holland America Line. Data exposed includes names, dates of birth, email addresses, genders, geographic locations, and loyalty program details.

Data purported to be from the UK’s Police National Legal Database was posted by the extortion group ExfilSquad, which listed PNLD on its leak site on July 26, 2026. According to the post, the group stole about 1.9 GB of data covering roughly 135,000 records, split between 114,000 PNLD subscribers and 21,000 Ask the Police users. Data exposed includes names, organizations, and work email addresses belonging to police officers, police staff, criminal justice professionals, government partners and customers.


Curious how these features and data can make your job easier? Get in touch! 

What is Malware as a Service?

October 08, 2026

Cybersecurity might as well have its own language. There are so many acronyms, terms, and sayings that unless you are deeply knowledgeable, have experience in the security field, or have a keen interest, one may not know what they mean. Understanding these terms is the first step to developing a thorough understanding of cybersecurity and, in turn, better protecting yourself, clients, and employees.

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, push bombing, web application attacks, man-in-the-middle attacks, ransomware leak sites, the CIA Triad, and encryption. In this edition, we dive into malware as a service..

Malware is one of the most persistent threats facing organizations worldwide. From stealing sensitive information to disrupting business operations, malicious software can cause significant financial and reputational damage. Traditionally, developing and deploying sophisticated malware required technical expertise, time, and resources. Today, cybercriminals can bypass much of that work by purchasing access to malware through a model known as Malware as a Service (MaaS).

Malware as a Service is a cybercrime business model in which malware developers sell or lease malicious software, infrastructure, and related services to other threat actors. Rather than building their own tools, buyers can purchase ready-made malware, often through subscription plans or one-time payments. Depending on the offering, these packages may include software updates, technical support, hosting infrastructure, and dashboards for managing campaigns. The result is a more accessible criminal ecosystem. Individuals with limited programming knowledge can use tools developed by more experienced threat actors to launch attacks against organizations and individuals.

MaaS operates similarly to legitimate Software as a Service (SaaS) platforms, where customers pay to access software maintained by a provider. The difference is that MaaS products are designed to facilitate cybercrime. Developers may earn recurring revenue from subscriptions, while customers use the tools to steal credentials, collect sensitive information, establish unauthorized access, or distribute additional malware.

This business model also creates specialization within the cybercrime economy. Developers can focus on building and maintaining malware, while affiliates and customers concentrate on distributing it and exploiting the information or access they obtain. Like Ransomware as a Service (RaaS), MaaS lowers the barrier to entry for cybercriminals and allows malicious campaigns to scale beyond the capabilities of a single operator.

Types of Malware Offered as a Service

Not all malware is designed to accomplish the same objective. MaaS offerings can support a range of malicious activities, depending on the software, infrastructure, and services included in a package. Below are some of the most common.

Information stealers, also known as infostealers, are types of malware designed to collect sensitive information from infected devices. Depending on the malware, this information may include saved browser credentials, authentication tokens, cryptocurrency wallet data, and other sensitive files.

Cybercriminals can use this information to access corporate accounts, impersonate legitimate users, commit financial fraud, or sell the stolen data to other threat actors.

Infostealer operators frequently monetize their activity through subscriptions and the sale of stolen information. Some services also provide access to stealer logs, which are collections of data extracted from infected devices. These logs can become valuable commodities on darknet marketplaces and underground forums, particularly when they contain credentials associated with corporate systems.

Remote Access Trojans (RATs) are malicious programs that allow an attacker to gain unauthorized remote control over an infected device. Depending on their capabilities, RATs may enable an operator to monitor activity, access files, execute commands, or collect sensitive information.

Through MaaS arrangements, threat actors can obtain access to remote-control malware without developing it themselves. Once deployed, these tools may provide a foothold that enables further malicious activity, including surveillance, credential theft, or attempts to move deeper into an organization’s network.

In the Wild

Nimbus Manticore, the Iranian hacking group, has been connected to two (NodeRabbit and PollCat) previously undocumented malwares targeting Linux and Apple macOS systems using cross-platform remote access trojans (RATs) developed using Node.js and JavaScript. Nimbus Manticore, also known as Iranian Dream Job, has been targeting job candidates with fake recruitment coding challenges designed to infect their computers. In one case, attackers distributed a project-management application called Taskflow and asked candidates to find bugs in the frontend within three hours. The challenge appeared legitimate, but malicious code was hidden in the supposedly “bug-free” server.js file. It loaded a trojanized Node.js package that secretly launched NodeRabbit, a backdoor capable of communicating with attacker-controlled servers. Once installed, NodeRabbit can collect system information, run commands, access and modify files, manage directories, and gather network details. It can also execute temporary scripts and delete them afterward to hide evidence of its activity. Read more here.

A botnet is a network of compromised devices that can be controlled by an operator. These devices may include computers, servers, and Internet of Things (IoT) devices.

Some MaaS offerings provide malware that recruits infected devices into a botnet, while other services sell access to existing botnet infrastructure. Threat actors may use these networks to conduct Distributed Denial-of-Service (DDoS) attacks, distribute spam, or support other malicious campaigns.

The scale of a botnet can make it particularly disruptive. By coordinating activity across many compromised devices, attackers can overwhelm online services or use distributed infrastructure to support additional operations.

Ransomware is malware that encrypts files or otherwise prevents victims from accessing their systems or data, typically to extort payment. Some ransomware operations use a service-based model in which developers supply the malware and supporting infrastructure to affiliates.

Although Ransomware as a Service is often treated as its own category, it shares many of the same characteristics as MaaS. Both models allow threat actors to access malicious tools without independently developing the underlying software.

The distinction is that ransomware is specifically designed to support extortion, while MaaS is a broader category that can include many different types of malicious software and objectives.

How Does Malware as a Service Work?

MaaS is not simply a transaction in which someone purchases a malicious program. It is an ecosystem of developers, vendors, infrastructure providers, and customers who work together to distribute malware and monetize its impact.

The process typically involves several stages:

  1. Malware development: Developers create malicious software, maintain its functionality, and may release updates to improve its capabilities or address problems encountered by customers.
  2. Distribution and marketing: Vendors advertise their offerings through underground forums, darknet marketplaces, encrypted messaging channels, or other criminal communities. Listings may describe the software’s capabilities, subscription options, and available support.
  3. Purchase or subscription: Customers pay for access to the malware or related services. Some offerings are sold for a one-time fee, while others require recurring payments. Cryptocurrency may be used to facilitate transactions, although payment methods vary.
  4. Deployment: Customers distribute the malware through methods such as phishing emails, malicious downloads, compromised websites, or other delivery mechanisms. The delivery method depends on the tool and the attacker’s objectives.
  5. Collection and monetization: Once malware has infected a device, attackers may collect credentials, steal files, establish unauthorized access, or carry out other malicious activities. Stolen information can then be used directly or sold to other criminals.
  6. Resale and further exploitation: The information obtained during an attack may be passed through several hands. For example, stolen credentials may be sold to an initial access broker, who then sells access to another threat actor for use in a larger intrusion or ransomware campaign.

This division of labor makes the MaaS ecosystem difficult to disrupt. Developers may never interact directly with victims, and the person deploying the malware may not be the person who ultimately profits from the stolen data.

It also means that a single malware infection can have consequences beyond the original compromise. Information stolen from one device may enable additional attacks against an employer, a business partner, or a customer.

MaaS has changed the economics of cybercrime. Threat actors no longer need to possess advanced programming skills or spend months developing malicious software. Instead, they can purchase tools that have already been developed, tested, and maintained by other criminals.

Several factors contribute to the continued growth of this model.

Low Barrier to Entry

Developing malware from scratch requires technical knowledge, time, and resources. MaaS removes much of that investment by providing ready-made tools that customers can deploy with limited expertise.

Some services even offer user-friendly dashboards, documentation, and technical support. This allows a broader range of threat actors to participate in cybercrime, increasing the number of potential attackers organizations must defend against.

Scalability and Automation

MaaS providers can distribute the same malware to multiple customers, who may use it against different targets simultaneously. Automated features can further increase the speed and scale of malicious campaigns.

For example, a single infostealer sold to multiple subscribers could be used to collect credentials from hundreds or thousands of devices. Those credentials may then be sold, traded, or used to gain unauthorized access to additional systems.

This scalability makes MaaS particularly concerning for organizations that rely on credentials to protect corporate applications, cloud environments, and internal networks.

Professionalized Cybercrime Economy

Cybercriminals increasingly operate through structured marketplaces and service-based business models. MaaS vendors may advertise product features, publish updates, offer customer support, and establish reputations within underground communities.

These practices make malicious services easier to purchase and create recurring revenue streams for developers.

DarkOwl research and analysis provides visibility into these criminal ecosystems by indexing darknet forums, marketplaces, and other underground sources where threat actors advertise malware, discuss attack methods, and exchange compromised information.

Connections to Other Cybercrime Services

MaaS rarely operates in isolation. It can overlap with several other criminal services, creating a chain of activity in which different threat actors specialize in different stages of an attack.

For example, an infostealer may collect corporate credentials from an infected device. Those credentials could be sold through an underground marketplace or passed to an initial access broker (IAB), who specializes in selling unauthorized access to compromised systems. Another threat actor may then use that access to deploy ransomware or steal additional data.

Each participant contributes to the attack without necessarily interacting with the original victim. This interconnected ecosystem makes it more difficult for security teams to understand the full scope of a threat by investigating a single malware sample or security incident.

The darknet plays an important role in the MaaS ecosystem. Underground forums, marketplaces, and encrypted messaging channels give threat actors places to advertise malicious software, recruit customers, exchange information, and sell stolen data.

These environments can also provide valuable intelligence for defenders.

Darknet listings may reveal which malware families are being promoted, what capabilities vendors claim to offer, and which industries or organizations are being discussed by threat actors. Discussions between customers and vendors can provide additional context about the tools being used and the methods associated with particular campaigns.

However, an advertisement does not necessarily mean a product works as claimed or that an attack is imminent. Threat intelligence analysts must evaluate the credibility of the source, corroborate findings, and distinguish between marketing claims, speculation, and evidence of actual malicious activity.

What Darknet Intelligence Can Reveal

Monitoring underground activity can help security teams identify several types of potential risk:

  • Malware advertisements: Listings for infostealers, remote access tools, botnet services, and other malicious software can provide insight into the tools available to threat actors.
  • Credential exposure: Stolen employee credentials, authentication tokens, and stealer logs may indicate that an organization has already experienced a compromise.
  • Emerging attack methods: Discussions about new malware capabilities, security evasion techniques, or vulnerabilities can help analysts understand evolving attacker behavior.
  • Targeted organizations: Mentions of company names, domains, brands, or employees may provide context about potential targeting or previously undiscovered exposure.
  • Criminal relationships: Connections between vendors, malware operators, and other threat actors can help analysts build a more complete picture of the cybercrime ecosystem.

Connecting these findings can help organizations move beyond reacting to individual security alerts and toward a more proactive understanding of their exposure.

There is no single security control that can prevent every malware infection. Because MaaS supports multiple types of attacks, organizations should combine technical safeguards, employee awareness, incident response, and threat intelligence.

Implement Endpoint Detection and Response

Endpoint detection and response (EDR) solutions help security teams monitor endpoint activity, identify suspicious behavior, and investigate potential compromises.

Rather than relying exclusively on known malware signatures, security teams should also look for behaviors associated with malicious activity, such as unauthorized credential access, suspicious process execution, or unexpected connections to external infrastructure.

Strengthen Identity and Access Management

Stolen credentials are a common commodity in the cybercrime economy. Organizations should enforce multifactor authentication (MFA), use phishing-resistant authentication where possible, and apply least-privilege access controls.

Security teams should also monitor for exposed credentials and revoke compromised sessions or tokens when necessary. Resetting a password alone may not be sufficient if an attacker has obtained an active authentication token or maintained another form of access.

Keep Systems Updated

Unpatched software can provide opportunities for attackers to gain access to systems or execute malicious code. Organizations should maintain an inventory of their assets, prioritize security patches based on risk, and address known vulnerabilities promptly.

Regular updates do not eliminate every attack path, but they help reduce the number of weaknesses available for exploitation.

Train Employees to Recognize Phishing

Phishing emails, malicious attachments, and deceptive downloads remain common ways to distribute malware. Employees should understand how to recognize suspicious messages, verify unexpected requests, and report potential security incidents.

Organizations should also use email security controls, web filtering, and application restrictions to reduce the likelihood that a single mistake results in a successful infection.

Maintain Reliable Backups and Incident Response Plans

Organizations should maintain regular, tested backups of critical data and ensure that recovery copies are protected from unauthorized access or modification.

Incident response plans should address how to isolate infected devices, investigate potential credential theft, determine whether sensitive information was exposed, and restore affected systems.

A malware infection may be only the beginning of a larger incident. Understanding what information was accessed and whether attackers retained access is just as important as removing the initial malware.

Monitor the Darknet for Exposed Information

Traditional security tools primarily focus on activity within an organization’s devices, networks, and cloud environments. However, information associated with an organization may appear on underground sources after it has already been stolen.

Darknet monitoring provides another layer of visibility by helping security teams identify exposed credentials, leaked data, malware advertisements, and other indicators of potential risk.

When combined with internal security telemetry, this intelligence can help organizations investigate incidents, identify exposure that might otherwise go unnoticed, and prioritize remediation efforts.


Curious to learn more about dark web monitoring? Contact us.

Threat Intelligence RoundUp: September

October 02, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants – The Hacker News

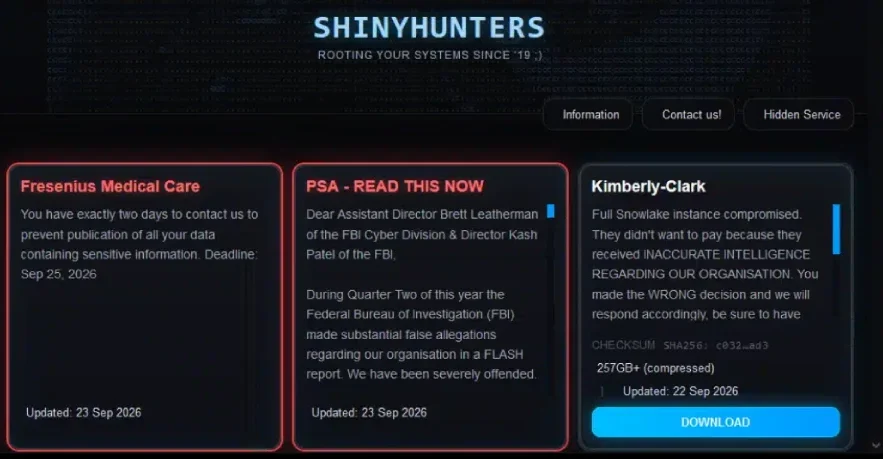
ShinyHunters has announced on their data leak site to have breached the U.S. Federal Bureau of Investigation and stolen data belonging to current and former employees at the agency. The post claims “We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job”. ShinyHunters claimed it targeted the FBI in response to a May 2026 public service announcement warning about the group’s targeting of Canvas, an online learning management system, and urging victims not to pay. The group disputed the FBI’s claims, calling them “substantial false allegations” and denying links to the Com cybercriminal collective, which it described as industry-driven “propaganda.” Read full article.

2. Autonomous AI Agents Compromise Thousands of Credentials in Under Six Hours – The Hacker News

Google Threat Intelligence Group (GTIG) reports that threat actors are increasingly targeting enterprise AI assets for espionage, extortion, and resource theft. Observed activity includes the theft of API credentials and proprietary AI data, including models, prompts, source code, and research, as well as the compromise of cloud environments to run unauthorized AI workloads. Financially motivated threat group, TeamPCP, has targeted software supply chains and AI coding assistants, while China-nexus actors have reportedly deployed local LLM infrastructure and conducted attacks against AI models to evade provider monitoring and extract proprietary capabilities. GTIG has also observed adversaries using agentic AI to accelerate malware and tooling development, underscoring the growing role of AI as both a target and an operational force multiplier for cyber threat actors. Read More.

Nimbus Manticore, the Iranian hacking group, has been connected to two (NodeRabbit and PollCat) previously undocumented malwares targeting Linux and Apple macOS systems using cross-platform remote access trojans (RATs) developed using Node.js and JavaScript. Nimbus Manticore, also known as Iranian Dream Job, has been targeting job candidates with fake recruitment coding challenges designed to infect their computers. In one case, attackers distributed a project-management application called Taskflow and asked candidates to find bugs in the frontend within three hours. The challenge appeared legitimate, but malicious code was hidden in the supposedly “bug-free” server.js file. It loaded a trojanized Node.js package that secretly launched NodeRabbit, a backdoor capable of communicating with attacker-controlled servers. Once installed, NodeRabbit can collect system information, run commands, access and modify files, manage directories, and gather network details. It can also execute temporary scripts and delete them afterward to hide evidence of its activity. Read more here.

According to a joint cyber security advisory, North Korean threat actors (WarPlum) behind the Contagious Interview campaign have compromised at least “30,000 devices located in more than 100 countries and siphoned funds or account credentials from over 7,000 cryptocurrency wallets”. A joint alert from cybersecurity and intelligence agencies in Japan, the U.S., Australia, and Germany warn of a campaign targeting web designers, engineers, and specialists in cryptocurrency, blockchain, and Web3. The threat actors have stolen an estimated $10.71 million or more in cryptocurrency. According to the alert, the group “conducts cyber-attacks by infiltrating unsuspecting job seekers’ computer networks, harvesting sensitive information, and stealing cryptocurrency.”. Following initial access, a variety of malware is deployed in an attempt to ensure access is gained. Read here.

5. Chinese Fire Ant hackers turn Cisco routers into spying platforms – Bleeping Computer

Researchers have uncovered a new tactic used by the threat actor known as Fire Ant, after identifying an active Generic Routing Encapsulation (GRE) tunnel interface on a Cisco IOS XR router that could not be accounted for by the device’s running configuration or commit history.

According to incident response firm Sygnia, Fire Ant activity “strongly overlaps” with the Chinese espionage group, UNC3886. Fire Ant has expanded its targeting beyond VMware hypervisors to include Cisco routers, TACACS authentication servers, and Linux management hosts. Further analysis of the compromised router revealed custom malware designed to maintain persistent access through a fake system service that activated the implant only during alternating hours, helping it evade detection.. Learn more.

6. US takes down NightmareStresser DDoS-for-hire platform – Bleeping Computer

On September 15, the FBI seized the domains of NightmareStresser, one of the longest-running DDoS-for-hire platforms. The service allowed users to rent access to compromised routers and IoT devices to launch large-scale distributed denial-of-service (DDoS) attacks. Before its domains were taken down, NightmareStresser claimed more than 566,000 registered users and the ability to generate attacks of up to 200 Gbps. According to the FBI, the platform was used to launch hundreds of thousands of actual or attempted DDoS attacks against targets worldwide since 2022. Read full article.

7. Spain’s data agency gets first report of AI-powered data breach – Bleeping Computer

The Spanish Data Protection Agency (AEPD) was notified of an alleged cyberattack involving an AI agent powered by a known large language model (LLM). The victim organization reported that the attack autonomously identified vulnerabilities, gained access to systems, modified personal data, and accessed financial documents. While the AEPD has not yet investigated or verified the incident, it said the report highlights how AI could increase the speed, scale, and adaptability of cyberattacks, reducing the time defenders have to respond. The agency recommends that organizations strengthen identity and credential security, improve rapid detection and containment capabilities, and update security and data protection strategies to account for AI-assisted and autonomous attacks. Read full article.

8. ShinyHunters hackers claim breach of Florida “DAVID” DMV database – Bleeping Computer

On September 08, ShinyHunters claimed on its data leak site to have breached DAVID, an online database platform used by the Florida Department of Motor Vehicles and exfiltrated more than 200,000 driver records. According to the threat actors, they gained access to DAVID by exploiting a password-reset vulnerability that enabled them to compromise multiple accounts. ShinyHunters further claimed that, after obtaining access, they enumerated records by ID and downloaded associated HTML pages and driver images. The group alleges that this activity resulted in the theft of more than 200,000 records, with the operation beginning on September 3. Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Cyber Security Awareness Month: Upcoming Content

October 01, 2026

In light of Cybersecurity Awareness month, DarkOwl is committed to sharing research, trends and industry news from our analysts.

Be the first to know as we release new research by entering your email below!

Upcoming Content This Month

BLOG

Threat Intel Round Up: September

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence. Read here.

NPCC Innovation & Digital Summit

DarkOwl’s Regional Director and Co-Founder of the UK OSINT Foundation will be at the NPCC Innovation & Digital Summit in Liverpool, England.  It is the UK’s main policing technology conference and brings together senior digital, data and technology leaders from the police forces of England and Wales, along with government, academia and technology companies.  Use the link below to schedule a time to meet and learn more about DarkOwl. Meet us!

it-sa Expo & Congress

We will be at it-sa 365, Europe’s largest trade fair for IT security and one of the most important dialogue platforms for IT security solutions. The trade fair in Nuremberg, Germany covers the entire range of products and services in the field of cybersecurity: hardware, software, training and consulting services as well as Security as a Service. Stop by and meet with us at Booth 9 – 223. Meet us!

GDPR and Dark Web Investigations: When European Subjects Show Up in Breach Data

An analyst pulls a stealer-log dataset while tracking a threat actor’s infrastructure. Buried in the rows: credentials, device fingerprints, and email addresses belonging to residents of France, Germany, and the UK. The investigation was never framed as a “European” matter — but at this point, GDPR is very likely already in play.

For US-based OSINT and dark web investigation firms, this is a common blind spot. GDPR exposure isn’t about where a firm is incorporated or where its servers sit. It’s about whose data ends up in the workflow, and why. Read here.

Malware as a Service

Cybersecurity might as well have its own language. There are so many acronyms, terms, and sayings that unless you are deeply knowledgeable, have experience in the security field, or have a keen interest, one may not know what they mean. Understanding these terms is the first step to developing a thorough understanding of cybersecurity and, in turn, better protecting yourself, clients, and employees.

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, push bombing, web application attacks, man-in-the-middle attacks, ransomware leak sites, and the CIA Triad. In this edition, we will dive into malware as a service. Read here.

Stay tuned for our quarterly update blog highlighting new product features and collection stats updates. There is always something exciting coming from our Product and Collections teams and the team is excited to share this round of updates! Check it out.

AI Is Rewriting the Ransomware Playbook

Artificial intelligence is reshaping cybersecurity on both sides of the battlefield. While organizations are increasingly adopting AI to strengthen their defenses, cybercriminals are using the same technology to launch faster, more sophisticated ransomware attacks that outpace traditional security measures. According to CrowdStrike’s 2025 State of Ransomware Survey, 76% of organizations say they struggle to keep up with AI-powered threats, and nearly 90% believe AI-driven protection is now essential.  

According to the Global Cybersecurity Outlook 2026 survey, 87% of respondents identified AI-related vulnerabilities as the fastest-growing cyber risk in 2025. Looking ahead, data leaks associated with generative AI (34%) and the advancement of adversarial capabilities (29%) are the leading concerns for 2026. This represents a notable shift from 2025, when adversarial capabilities ranked first at 47%, compared with just 22% for genAI-related data leaks. The change signals a turning point in the AI risk landscape: while the AI arms race between attackers and defenders continues, growing attention is shifting from offensive AI capabilities toward the unintended exposure and misuse of sensitive data through generative and agentic systems. Read here.

Inside the Nexus Leak

In late August 2026, a post appeared on the Russian-language cybercrime forum Exploit offering persistent access to a proprietary database of breached identity documents, reportedly pulled from an identity verification vendor and its client base. Within days, the same dataset was being repackaged and resold across at least three additional forums, a dedicated storefront, and a cluster of Telegram channels — long after the original listing had gone quiet.

DarkOwl analysts tracked the spread of this dataset, known by the name of the tool its original seller built to access it: Nexus. This post walks through what we found, and what it says about how stolen identity data circulates once it hits the dark web. In the interest of protecting the people whose personal documents were exposed, this post omits names, images, and identifying details of any individuals referenced in the underlying leak. Read here.

PHP Vulnerabilities Affect the Darknet Also

On October 21, 2026, PHP’s maintainers released emergency fixes for two critical remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, which were identified through the use of AI. Within hours, government agencies in several countries told operators to consider taking sites offline until they could patch. They also took down their own websites, government websites in Finland and Edinburg council and the BBC all took down webpages as well as countless others.

So did the administrators of popular darknet forums BreachForums, DarkForums, and PwnForums. Read here.

ZeroForums: A New Chinese-Language Dark Web Forum Mimicking Established Cybercriminal Platforms

A newly emerged dark web forum known as “ZeroForums” has been identified, operating with a user interface closely mimicking established cybercriminal platforms including BreachForums and RaidForums. The forum defaults to Simplified Chinese as its primary language, with all threads and posts displayed in Chinese by default, though users retain the ability to switch the interface to English. Check it out.

Halloween: Spooky Finds on the Dark Web

The darknet can be a scary place. 👻 For Halloween, we will highlight some spooky findings from our analyst team that they have come across this past year. In the meantime, check out our previous edition where the team uncovered human organs for sale, human meat for sale, and hitmen for hire! Check out our other holiday editions here and here.


Curious to see how darknet data can improve your cybersecurity situational awareness? Contact us.

What is Encryption?

September 24, 2026

Cybersecurity might as well have its own language. There are so many acronyms, terms, and sayings that unless you are deeply knowledgeable, have experience in the security field, or have a keen interest, one may not know what they mean. Understanding these terms is the first step to developing a thorough understanding of cybersecurity and, in turn, better protecting yourself, clients, and employees.

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, push bombing, web application attacks, man-in-the-middle attacks, ransomware leak sites, and the CIA Triad. In this edition, we dive into encryption.

At its core, encryption is the cryptographic process of encoding plain text or raw data into an unreadable format, known as ciphertext. Only authorized parties who possess the corresponding decryption key can translate that ciphertext back into its original, legible form. Put simply, encryption helps ensure that if unauthorized individuals gain access to data, they cannot simply read it. The National Institute of Standards and Technology (NIST) defines encryption as the process of transforming plaintext into ciphertext using a cryptographic algorithm and key.

Encryption is used throughout modern technology. It can protect files stored on a computer, information saved in a database, messages sent between devices, online transactions, and communications traveling across a network.

Encryption ensures data confidentiality and integrity—two core pillars of the CIA Triad. Without encryption, sensitive corporate communications, credentials, credit card details, and personal health information would travel across local networks and the open web in plain, easily readable text.

How Does Encryption Work?

Encryption relies on two primary components: an algorithm and a key.

An encryption algorithm is the mathematical process used to transform plaintext into ciphertext. The key is a piece of information that controls that transformation. Without the appropriate key, the ciphertext should be extremely difficult to convert back into its original form. The strength of an encryption system depends on several factors, including the algorithm, key management, implementation, and how securely the keys themselves are protected. This last point is particularly important. Even strong encryption can be undermined if an attacker gains access to the keys used to decrypt the information.

Symmetric vs. Asymmetric Encryption

There are two primary types of encryption: symmetric and asymmetric encryption.

  • Symmetric Encryption: Uses a single, shared secret key to both encrypt and decrypt data. Algorithms like AES-256 (Advanced Encryption Standard) are exceptionally fast and computationally efficient. They are routinely used for bulk data protection, such as hard disk encryption and secure database storage.
  • Asymmetric Encryption: Uses a pair of mathematically linked keys—a public key for encryption and a private key for decryption. RSA and ECC (Elliptic Curve Cryptography) are common examples. While computationally heavier than symmetric keys, asymmetric protocols eliminate the risky requirement of sharing a single key across unsecured networks.

Encryption itself is neutral technology—it simply enforces privacy and access control. Because of this, it serves as a critical defense for legitimate enterprises while simultaneously acting as a primary weapon for threat actors operating in darknet ecosystems.

Protective Security Measures

For enterprise organizations, end-to-end encryption (E2EE) and transport layer security (TLS) safeguard sensitive traffic from Man-in-the-Middle (MitM) interception. Furthermore, encrypting data at rest ensures that even if an unauthorized user breaches a corporate database, the stolen files remain unusable without the corresponding keys.

Darknet Privacy & Anonymity

Darknet networks like Tor and I2P rely on multi-layered encryption (often described as “onion routing”) to conceal IP addresses, server locations, and user identities. Security researchers and threat intelligence analysts use tools like Pretty Good Privacy (PGP) and encrypted Linux utilities to communicate safely and store sensitive datasets gathered during darknet investigations.

Malware and Ransomware Weaponization

Threat actors frequently turn encryption against their targets:

  • Ransomware-as-a-Service (RaaS): Cybercriminals deploy malicious payloads to systematically encrypt a victim company’s critical files and network drives, demanding a extortion payment in exchange for the decryption key.
  • Intermittent Encryption: To evade security detection tools, modern ransomware operators often encrypt only select portions of a file rather than the entire disk. This emulates normal administrative system processes and drastically speeds up the encryption process before defenders can respond.
  • Information Stealers: Advanced infostealers incorporate an Encryption Module. Ironical as it is, malicious actors use algorithms like AES to encrypt credentials and system tokens before exfiltrating them back to Command and Control (C2) servers. This hides the stolen data from network monitoring tools and security analysts.

Encryption also plays an important role in the underground ecosystem. Threat actors use encryption and other privacy-enhancing technologies to communicate, exchange stolen information, and conceal aspects of their activities. Encrypted communications can make it more difficult for organizations and investigators to determine what threat actors are discussing or planning.

However, encryption does not necessarily make criminal activity invisible.

Threat actors frequently leave behind other forms of information, including usernames, aliases, email addresses, cryptocurrency addresses, domains, malware advertisements, stolen credentials, and discussions of specific targets. Connecting these seemingly separate pieces of information can help security teams build a more complete picture of a threat actor or campaign.

Ransomware provides a particularly visible example.

During a ransomware attack, threat actors can encrypt files or systems belonging to a victim organization, preventing the organization from accessing its own data. The attacker then demands payment in exchange for a decryption key or other means of restoring access.

Encryption itself is not malicious. The difference lies in how it is used and who controls the keys.

This distinction is important when investigating compromised data. Encrypted information found during an investigation may not be immediately readable, but it can still provide valuable context about an attack, the systems involved, or the threat actors behind it.

Plaintext vs. Encrypted Data: What Appears on the Dark Web?

When darknet market vendors and ransomware groups leak compromised databases on underground forums, the state of the data often dictates its market value:

  • Plaintext Credentials: Cleartext email-and-password combinations are the most easily exploited digital goods. They are immediately usable for credential stuffing, account takeover (ATO), and network intrusion.
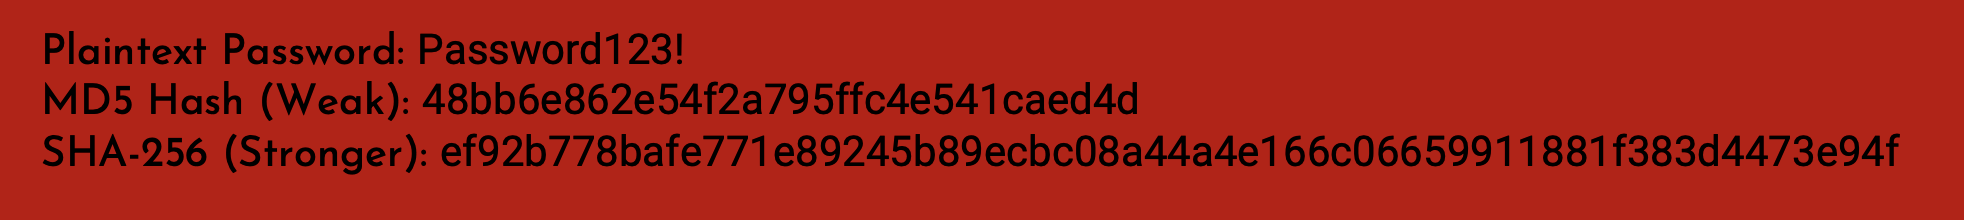
  • Hashed and Salted Passwords: When companies properly implement cryptographic hashing algorithms (such as SHA-256 or bcrypt), leaked database dumps contain cryptographic hashes rather than raw passwords. Threat actors must perform resource-heavy offline cracking routines to revert these hashes back to plain text.

While legacy algorithms like MD5 and SHA-1 remain surprisingly common across darkweb breach dumps, darknet intelligence shows a growing transition toward stronger SHA-256 and SHA-512 hashes as organizations update their authentication standards.

Encryption plays a critical role in protecting sensitive information from unauthorized disclosure.

Without encryption, intercepted or stolen data may be immediately readable.

Consider a laptop containing sensitive customer information. If the device is stolen and its stored data is encrypted, an attacker may have possession of the physical hardware without automatically gaining access to the information stored on it.

The same principle applies to data traveling across networks. Encryption can help prevent unauthorized parties from simply reading intercepted communications.

Encryption is therefore an important component of protecting:

  • Personally identifiable information (PII)
  • Financial information
  • Healthcare information
  • Intellectual property
  • Authentication credentials
  • Corporate communications
  • Customer data
  • Government and critical infrastructure information

However, encryption is not a standalone security solution.

It does not prevent every type of cyberattack. An attacker who compromises an authorized user’s account may be able to access information after it has been legitimately decrypted. Likewise, encryption does not prevent phishing, malware, credential theft, insider threats, or vulnerabilities in applications.

Encryption protects the confidentiality of data, but organizations still need layered security controls to protect the systems, identities, applications, and users that interact with that data.

Implementing robust encryption is essential to maintaining strong data governance and mitigating risk:

  1. Enforce Strong Standard Algorithms: Phase out legacy cryptographic algorithms (such as DES, MD5, or SHA-1) in favor of modern standards like AES-256, SHA-256, and RSA-2048+.
  2. Key Management Discipline: Storing encryption keys on the same server as the encrypted data defeats the purpose of cryptography. Use Hardware Security Modules (HSMs) or centralized, access-controlled key management vaults.
  3. Protect Data in Transit and at Rest: Ensure TLS 1.3 is enforced for all external endpoints and full-disk encryption is mandatory across all enterprise endpoints, remote worker laptops, and cloud storage buckets.
  4. Monitor Darknet Exposure: Even strong internal encryption cannot prevent third-party vendor leaks or endpoint infostealer infections. Utilizing specialized darknet monitoring enables organizations to detect exposed API keys, internal credentials, and database dumps early—before threat actors can exploit them.

Curious to learn more about dark web monitoring? Contact us.

Harakat Ashab al-Yamin al-Islamia: A New Group or Part of a Broader Iranian-Aligned Network?

April 16, 2026

A previously unknown group calling itself Harakat Ashab al-Yamin al-Islamia (Ashab al-Yamin) has recently emerged, claiming responsibility for a series of attacks across Europe and quickly attracting attention from analysts and media outlets. Reporting by CBS News, citing researchers from Tech Against Terrorism and others, has highlighted the group’s sudden appearance and raised questions about whether it represents a genuine operational network or a rapidly assembled media construct linked to broader geopolitical dynamics.

The group’s presence appears largely confined to Telegram, where it publishes a mix of attack claims, propaganda, and geopolitical commentary. Its Telegram footprint is fragmented, with limited persistent content and much of its activity preserved through secondary or supporter accounts.

Rather than evaluating Ashab al-Yamin as a standalone entity, a closer examination of its Telegram activity suggests a different framing. Patterns of shared content, cross-channel distribution, and overlapping narratives indicate that the group operates within a broader, loosely connected ecosystem of Iranian-aligned channels. This ecosystem overlaps with networks commonly associated with the “Islamic Resistance,” where claims, media, and messaging circulate across multiple accounts rather than originating from a single source.

This raises a central question: is Ashab al-Yamin a distinct organization, or a visible node within a broader networked ecosystem? Let’s dive in.

As of early April 2026, the group’s primary Telegram channel, Harakat Ashab al-Yamin al-Islamia, appears to have been removed or banned from the platform. The most recent identifiable content, dated April 4, included a video claiming responsibility for an attack targeting a building associated with Christians for Israel in Nijkerk, Netherlands. No clear successor channel has been identified at the time of writing, further reinforcing the group’s fragmented and unstable presence across Telegram, where continuity appears dependent on redistribution rather than sustained ownership of a single channel.

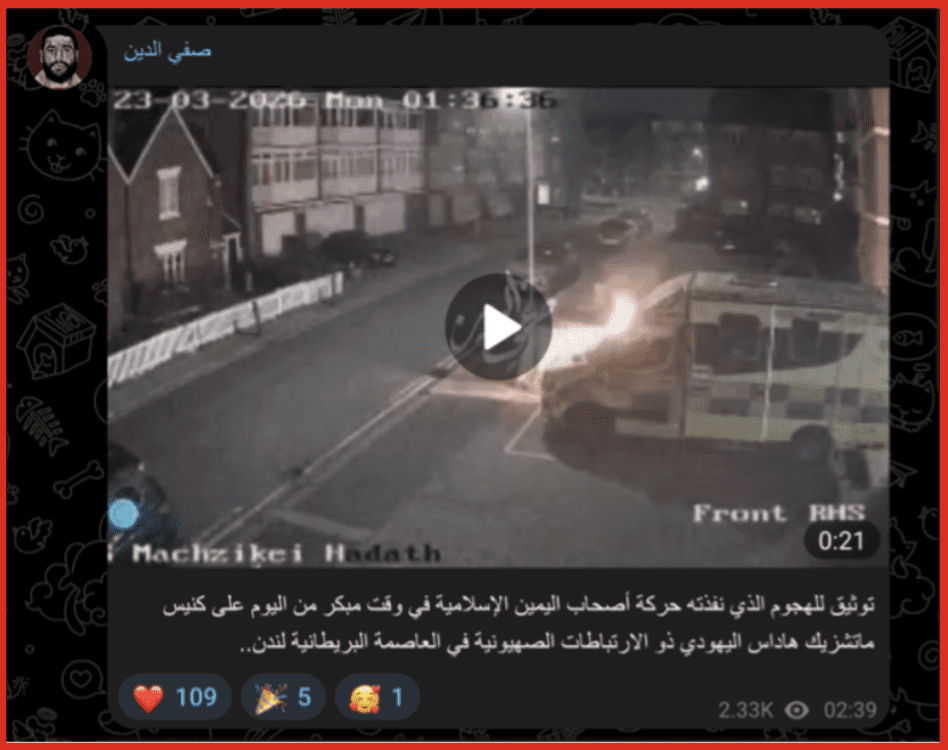
As a result, much of the group’s observable activity is derived from secondary or supporter channels, such as صفي الدين, which continues to circulate attack claims, propaganda, and related content attributed to the group.

Initial review of these channels suggests they do not function solely as claim-of-responsibility outlets. Instead, they operate as hybrid media nodes, combining attack claims, geopolitical commentary, and propagandistic amplification of broader regional narratives.

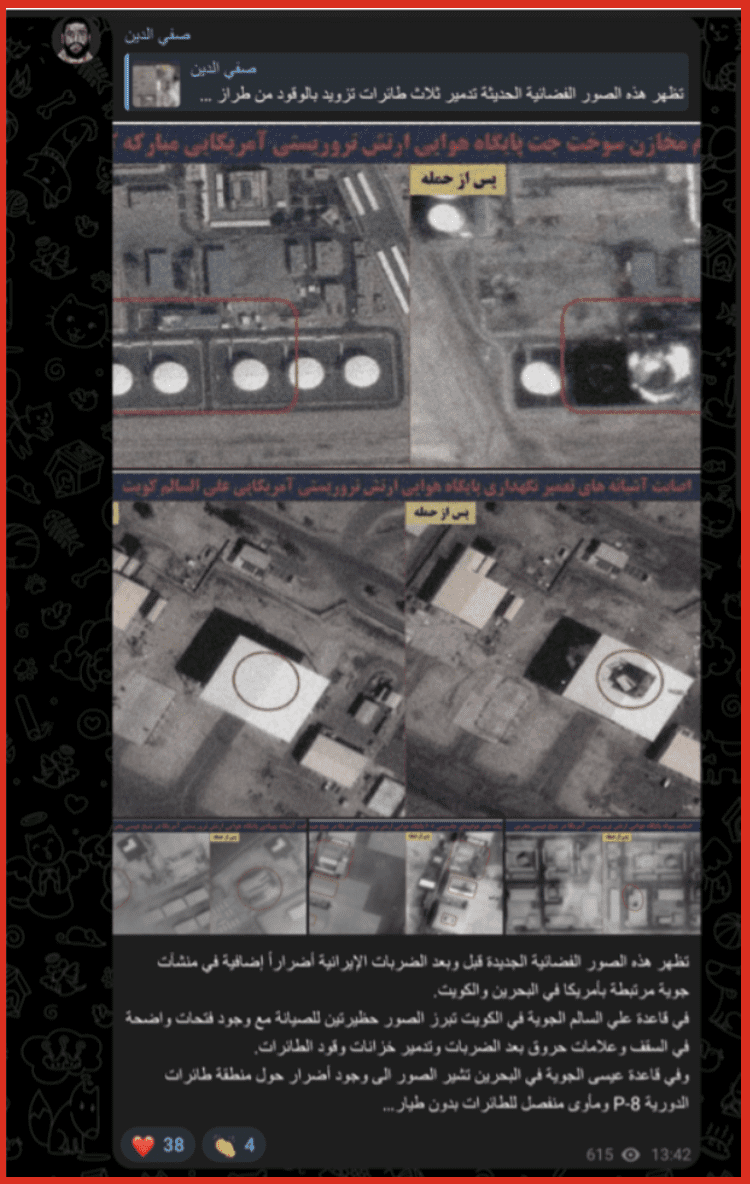
For example, content includes battlefield or intelligence-style analysis, such as satellite imagery purportedly showing damage to U.S.-linked air facilities in Bahrain and Kuwait following Iranian strikes. The accompanying text describes specific targets such as hangars, fuel storage, and drone infrastructure.

Figure 1: Satellite imagery / strike analysis post

This style of posting is consistent with content observed across pro-Iranian Telegram channels, where content blends battlefield updates, geopolitical commentary, and narrative amplification alongside claims of responsibility for attacks in Europe.

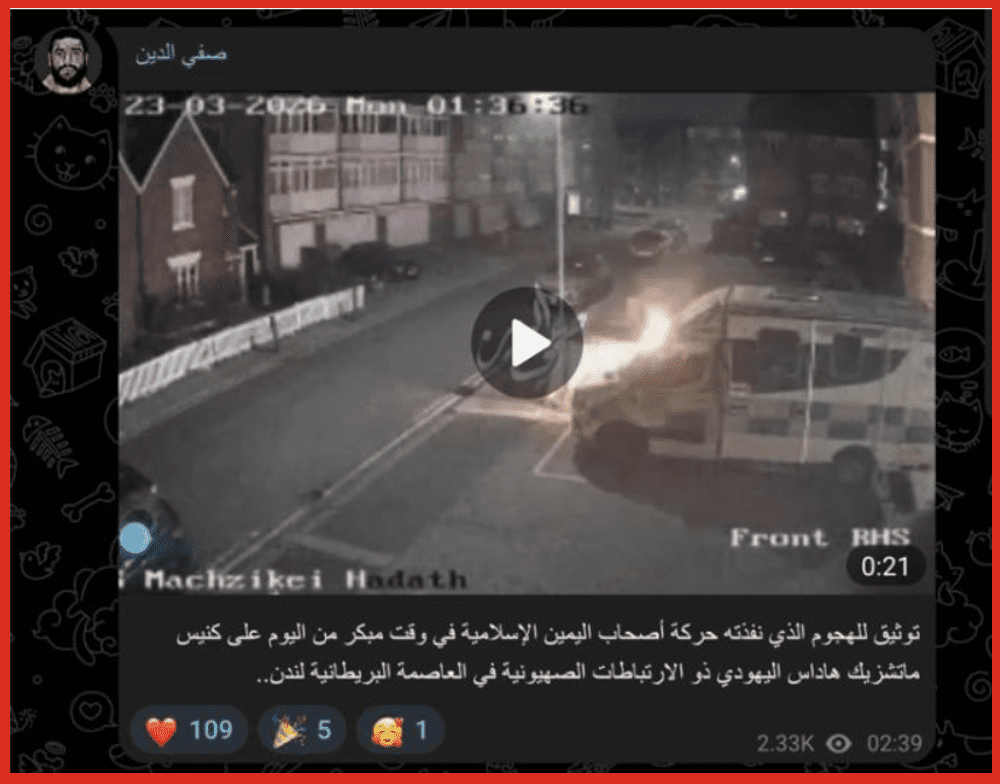
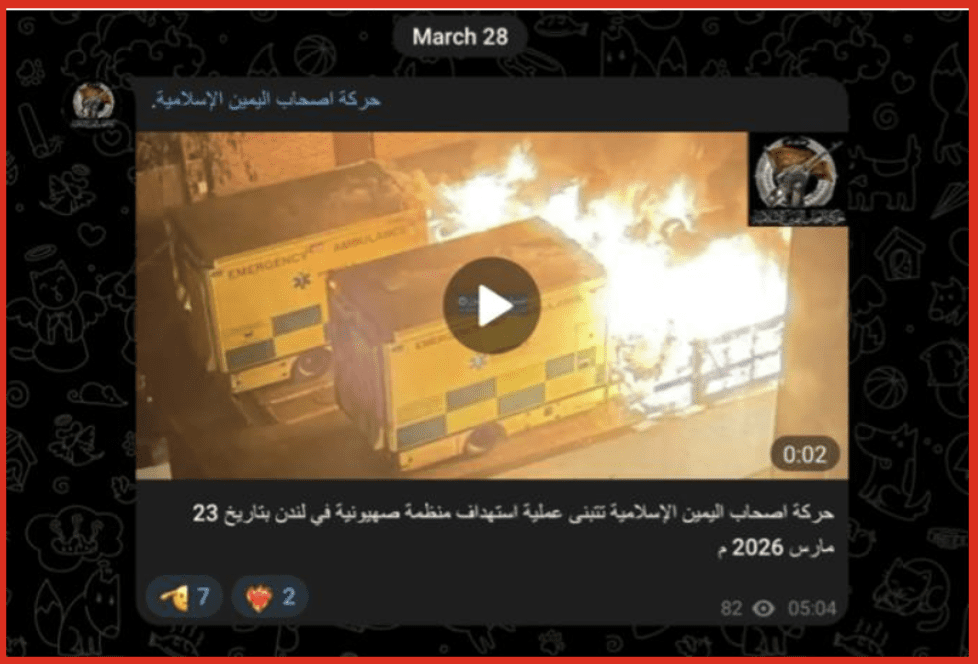
Figure 2: London ambulance attack claim video

One such example includes a video documenting an arson attack in London targeting ambulances associated with a Jewish community organization. The accompanying Arabic-language caption frames the incident as an operation carried out by Ashab al-Yamin, referencing a synagogue in the British capital and linking the action to broader anti-Israel narratives.

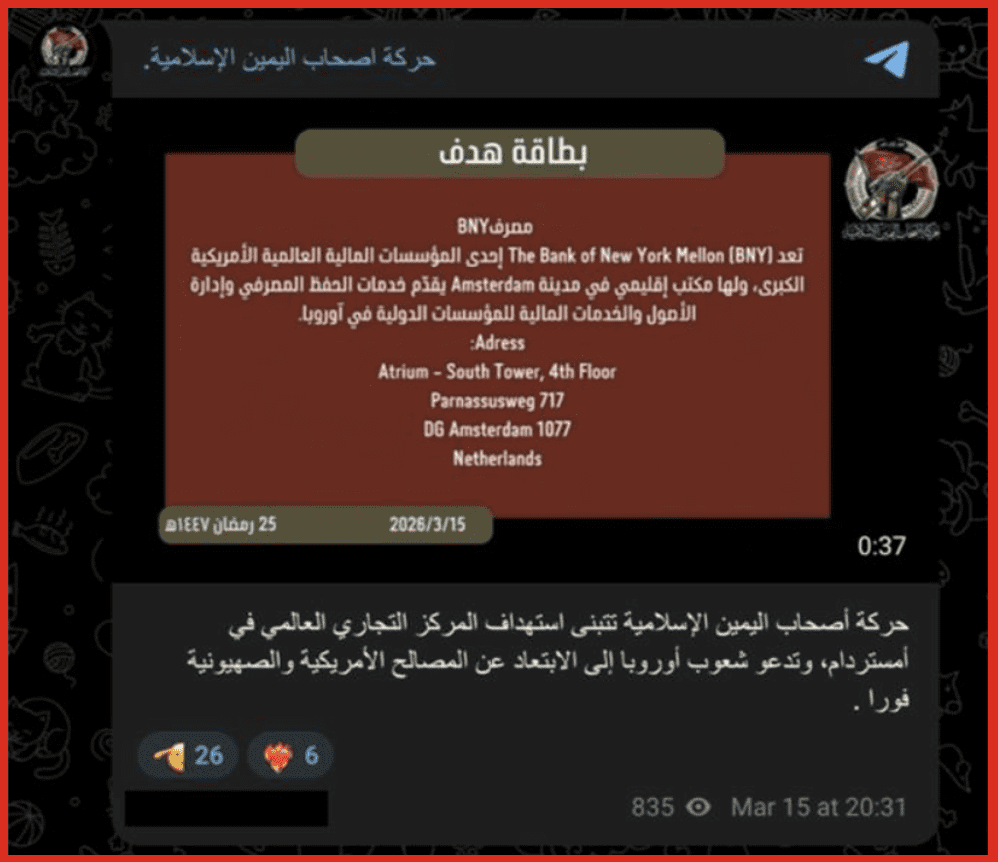
More recent content attributed to the group includes claims related to an attack targeting a commercial center in Amsterdam. One such post states:

Figure 3: Amsterdam attack video from Ashab al-Yamin

حركة أصحاب اليمين الإسلامية تتبنى استهداف المركز التجاري العالمي في أمستردام، وتدعو شعوب أوروبا إلى الابتعاد عن المصالح الأمريكية والصهيونية فوراً.

Translation: “The Islamic Movement of Companions of the Rights claims responsibility for targeting the World Trade Center in Amsterdam and calls on the peoples of Europe to immediately distance themselves from American and Zionist interests.”

The limited availability of such claims on the group’s official channel, combined with their continued circulation across secondary and affiliated channels, complicates efforts to assess a single point of origin. Instead, messaging is distributed across multiple accounts, where content persists through redistribution rather than consistent publication from a single source.

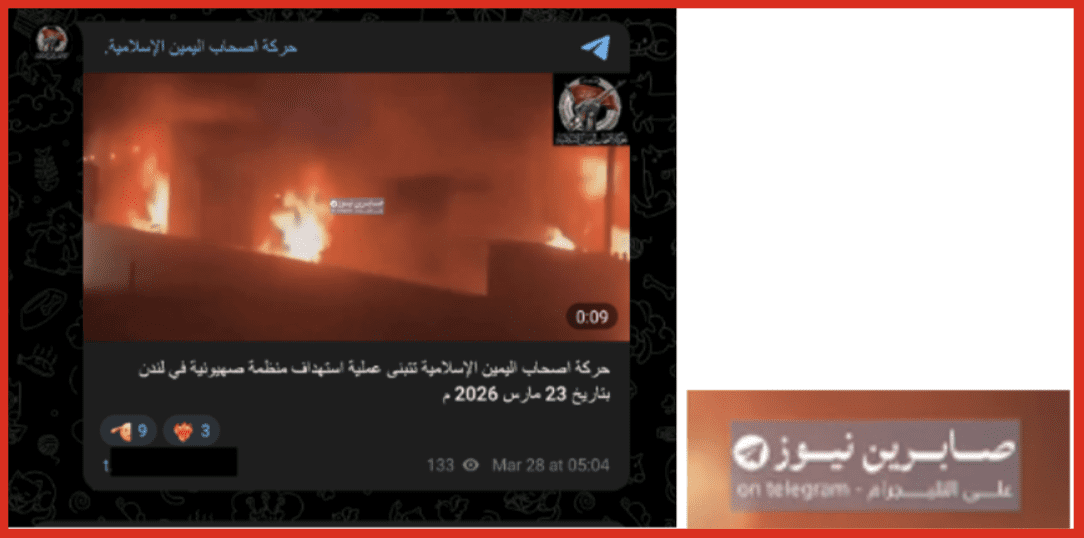
One particularly notable detail is the presence of Sabereen News branding within video content that was previously reposted by Ashab al-Yamin’s official Telegram channel.

Figure 4: Ashab al-Yamin post showing Sabereen News watermark; London attack

Sabereen News is a Telegram-based media outlet widely associated with Iranian-aligned networks, with multiple analyses pointing to links with Iran’s Islamic Revolutionary Guard Corps–Qods Force (IRGC-QF) and Iran-backed militia groups. Research by the Washington Institute for Near East Policy notes “strong indicators” of IRGC-QF connections and highlights that the channel first appeared on Telegram in January 2020. More recent reporting from Iran International similarly reflects its position within IRGC-linked messaging networks.

The visible Sabereen News watermark within the footage of the London ambulance attack suggests that the video was either sourced from, or circulated through, an Iranian-aligned media channel prior to being reposted by Ashab al-Yamin. Rather than serving as definitive proof of origin, this overlap indicates participation in a shared media pipeline where content is reused and redistributed across channels.

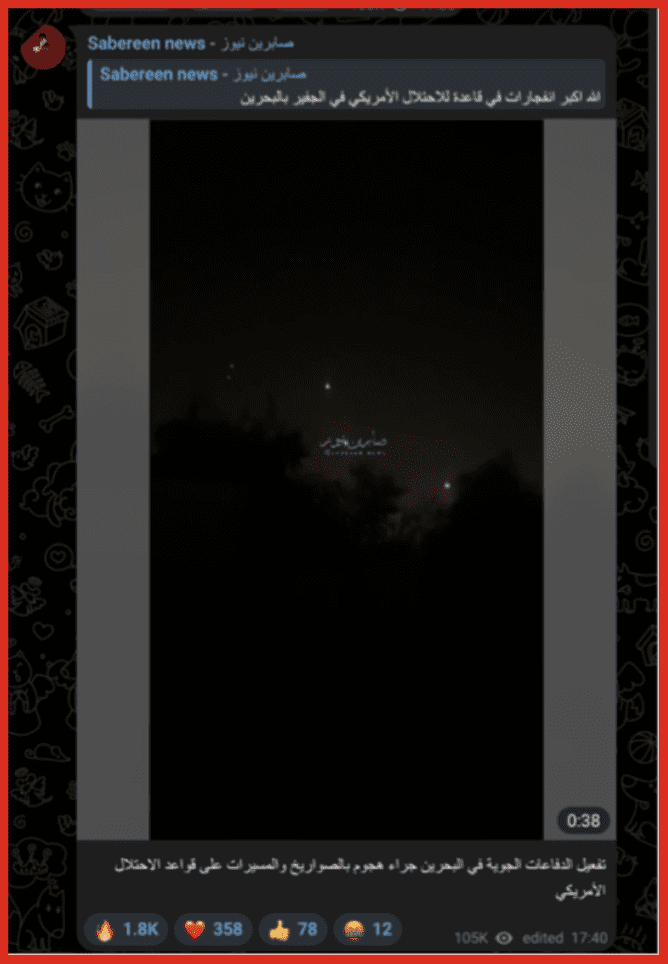
This interpretation is further supported by activity observed on Sabereen News channel, which regularly publishes operational updates, threat messaging, and geopolitical narratives aligned with Iranian interests.

Additional Sabereen content illustrates this narrative.

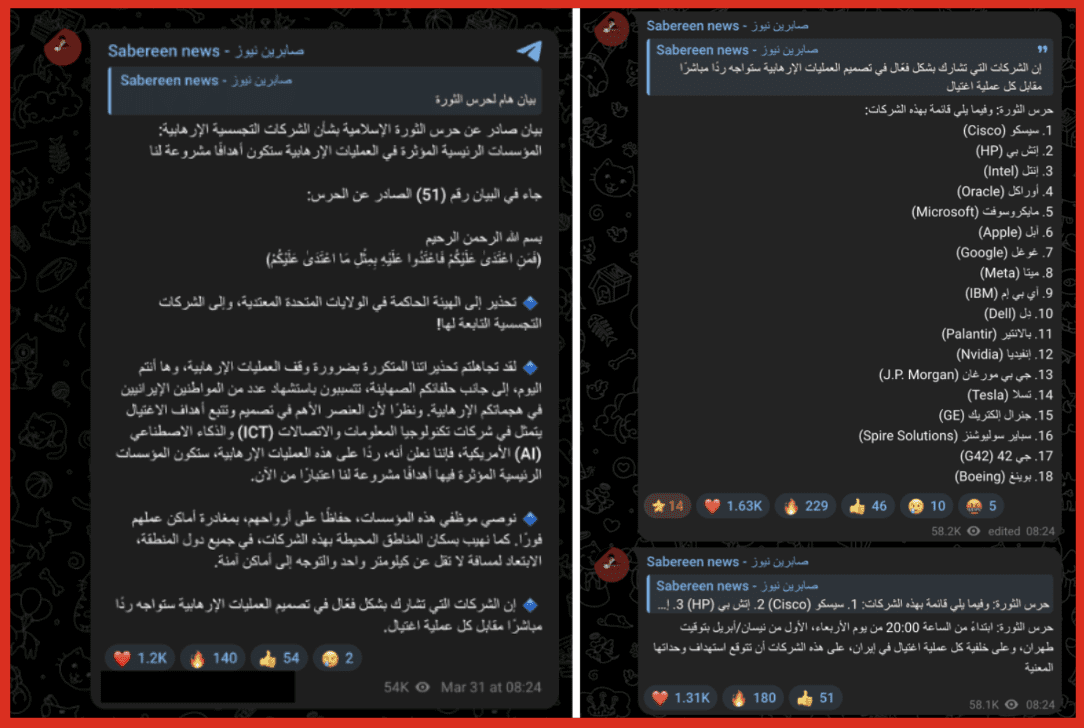
Figures 6 & 7: Sabereen News corporate targeting / company list

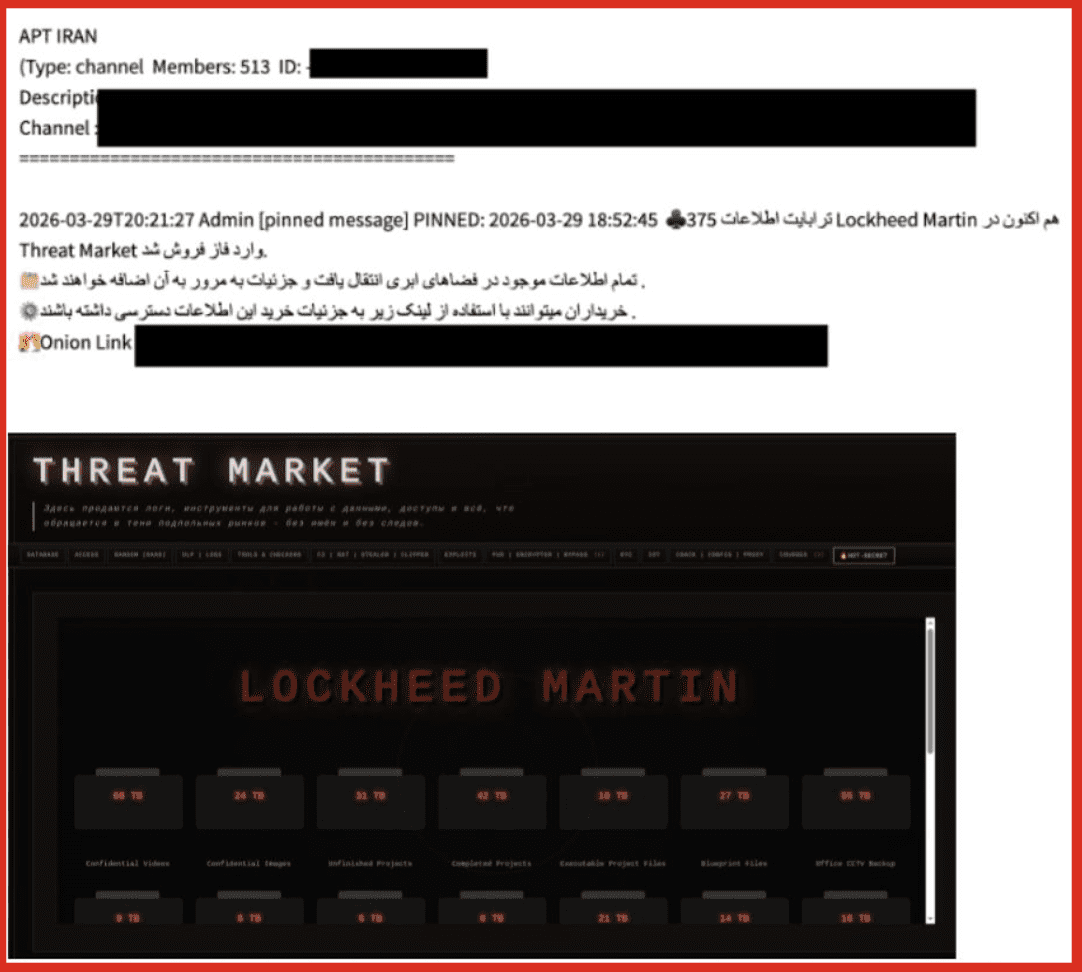
In this example, Sabereen News publishes a list of Western companies, including technology firms, financial institutions, and defense-related entities, framing them as potential targets linked to broader geopolitical events. While this is not a direct claim of responsibility, it reflects a broader pattern of signaling and narrative shaping seen across affiliated channels.

Additional recent content from Sabereen News further illustrates its role as a central distribution node within this ecosystem. In some cases, this aggregation extends beyond Iranian-aligned actors.

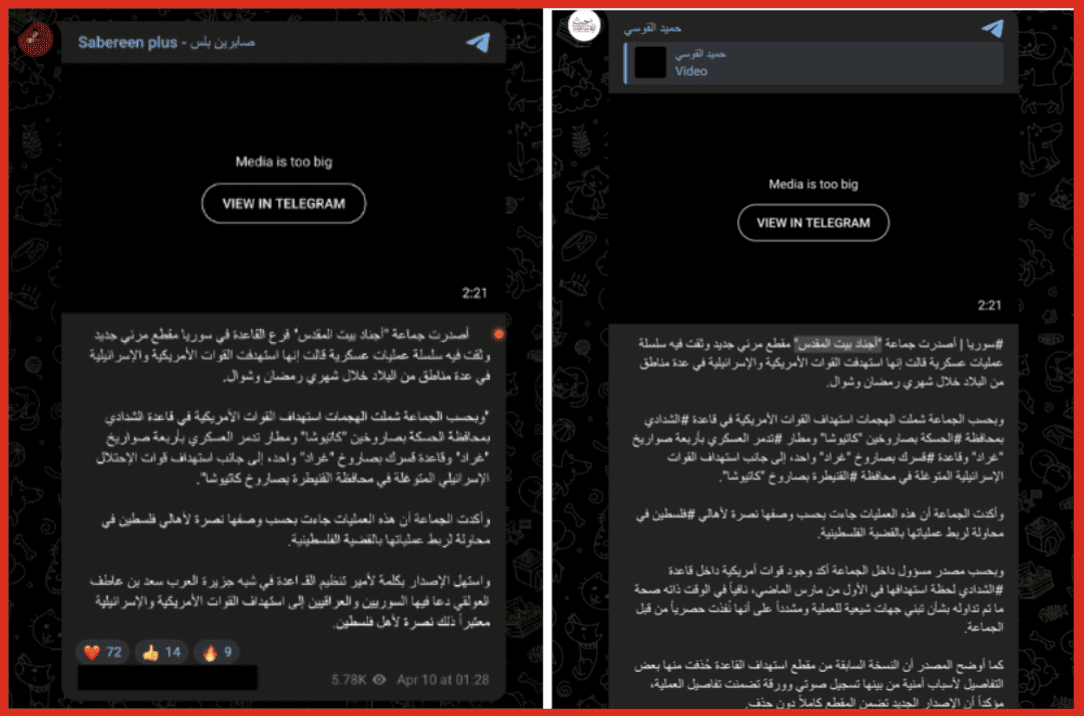
For example, Sabereen News has been observed resharing content attributed to Sunni jihadist groups, including material linked to Ajnad Bayt al-Maqdis. The original post appears to have been published by a Telegram account operating under the name “hamid alqawsi,” before being redistributed through Sabereen. The group’s recent pledge of allegiance to al-Qaeda, dated February 2026, coincides with broader regional escalation reinforcing patterns of opportunistic emergence tied to major geopolitical events. This further illustrates how content moves across distinct networks through centralized amplification channels.

Figures 8 & 9: Original Telegram post from “hamid_alqawsi” account and subsequent repost by Sabereen News

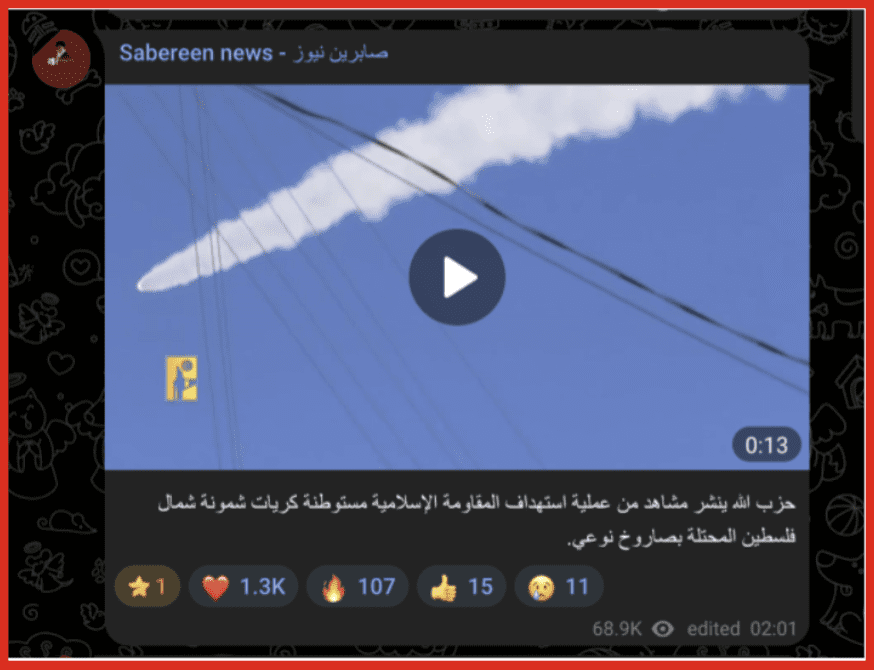
In a separate example, the channel reposts video footage attributed to Hezbollah depicting a missile strike on the Israeli town of Kiryat Shmona. While not directly linked to Ashab al-Yamin, this type of cross-group content aggregation highlights how Sabereen functions as a broader amplification hub, circulating material from multiple actors and reinforcing shared narratives across the network. Channels such as Sabereen News therefore remain key points of observation for tracking how new identities emerge and reappear within this network.

Figure 10: Sabereen News Telegram post reposting Hezbollah-attributed missile strike footage targeting Israel

An earlier Telegram channel, Haraka Ashab Al Yamin, identified as one of the first to publish content associated with the Amsterdam attack, appears to have been removed or banned from the platform, further complicating efforts to trace content back to a single point of origin.

Across posts, several additional patterns emerge that reinforce this ambiguity. The language is primarily Arabic, with no observable use of Farsi despite speculation of Iranian association, and messaging consistently incorporates anti-Israel and anti-Western themes aligned with broader regional narratives. Taken together, these characteristics further complicate attribution and raise questions about the group’s structure, consistency, and underlying coordination, which become more apparent when examining its claims and media output more closely.

The available Telegram content presents a mixed picture of Ashab al-Yamin’s credibility as an operational group. While the channel attempts to project visibility through attack claims and messaging, it lacks several features typically associated with more established militant organizations.

Unlike known Iranian-aligned and PMF-affiliated groups, Ashab al-Yamin does not consistently produce formalized statements, leadership messaging, or a clearly defined media structure. Its presence appears limited in scale, with no clear evidence of sustained or centralized coordination.

At the same time, the quality and style of its media output vary noticeably, with some videos appearing more refined and others more rudimentary. This inconsistency likely reflects contributions from multiple actors rather than a single coordinated media wing. This aligns with assessments from analysts cited in CBS News, who note that such output may be designed to generate psychological impact rather than demonstrate operational sophistication.

The group’s messaging also closely tracks ongoing geopolitical developments, suggesting a degree of responsiveness and an understanding of how to maximize visibility within a rapidly evolving information environment. Taken together, these patterns support the interpretation put forward by the Foundation for Defense of Democracies: that Ashab al-Yamin may function less as a centralized organization and more as a front identity used to claim attacks carried out by loosely connected or externally recruited individuals. This ambiguity becomes more meaningful when placed alongside the wider ecosystem in which the group operates.

More broadly, this model reflects a pattern observed across comparable ecosystems, where decentralization, narrative amplification, and perceived reach are often prioritized over formal organizational structure. In such contexts, visibility and attribution can be strategically leveraged to amplify perceived impact without requiring sustained operational capability.

Rather than viewing Ashab al-Yamin in isolation, its activity is more clearly understood when placed alongside a broader cluster of Telegram channels linked to the “Islamic Resistance” ecosystem.

This ecosystem includes a mix of militia-linked channels, media outlets, and amplifier accounts. Channels such as:

· شباب الإسلام

· أصحاب الكهف

· جيش الغضب

· صفي الدين

· التعبئة الشعبية للمقاومة الإسلامية في العراق ( بسيج العراق)

· القدرات العسكرية الإيرانية

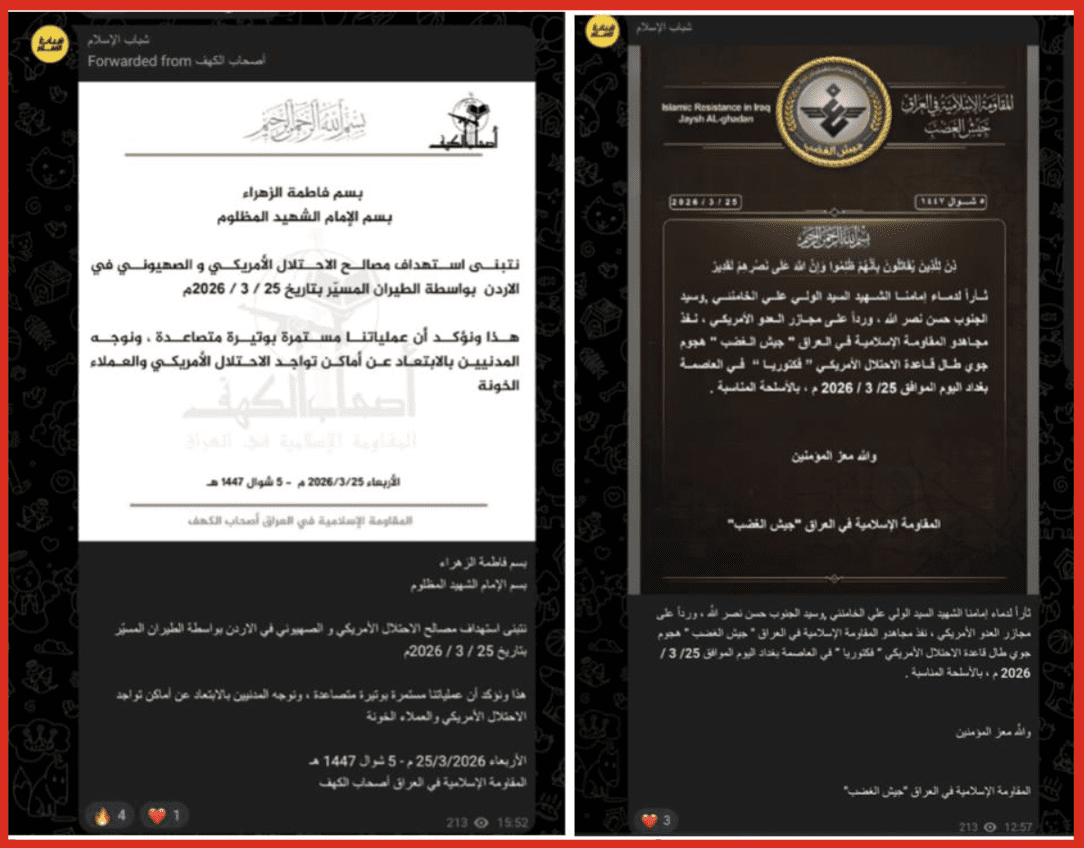
These channels regularly publish claims, updates, and propaganda tied to attacks against U.S. and allied targets, while also forwarding and resharing content from one another. These channels function as an interconnected network, regularly cross-posting and reinforcing shared narratives.

Figure 11: Safee al-Deen / ecosystem connections post

Posts such as the above highlight explicit relationships between multiple groups operating under the umbrella of the “Islamic Resistance,” including Ashab al-Kahf and Jaysh al-Ghadab.

Ashab al-Kahf is an Iraqi militia group aligned with the Islamic Resistance in Iraq, known for claiming attacks against U.S. military and allied targets in the region. Its Telegram presence reflects a structured communication style, including consistent branding, formalized statements, and clearly framed claims of responsibility.

Figure 12: Ashab al-Kahf Telegram profile / branding insignia

Jaysh al-Ghadab similarly operates within this ecosystem, publishing claims and messaging tied to attacks and broader resistance narratives. Like Ashab al-Kahf, its content reflects a more established and consistent media presence, with recognizable visual identity and integration into a wider network of affiliated channels.

Figure 13: Jaysh al-Ghadab Telegram profile / branding insignia

While these groups exhibit more structured branding and communication styles, they operate within the same broader environment as Ashab al-Yamin. Figures 14 and 15 illustrate formalized statements published by Ashab al-Kahf and Jaysh al-Ghadab, both of which were subsequently forwarded by the Shabab al-Islam channel. This pattern highlights how official statements originating from more established actors are redistributed across affiliated channels, reinforcing shared narratives, and expanding reach.

Figures 14 & 15: PMF formal statement example

Both statements follow a consistent format typical of PMF-aligned media output, including religious framing, attribution of attacks against U.S. and Israeli interests, and references to specific operations. For example, one statement claims responsibility for a drone attack targeting Israeli-affiliated infrastructure in Jordan, while emphasizing civilian evacuation warnings and framing the operation within a broader resistance narrative. The second statement similarly adopts formalized language, invoking religious justification, and positioning the attack within the context of ongoing regional conflict. This contrast becomes more apparent when comparing how similar attack-related content appears across different channels within the network.

Figure 16: London ambulance attack claim Ashab al-Yamin TG channel
Figure 17: London ambulance attack claim: Safee al-Deen TG channel

Figures 16 and 17 show the same London ambulance attack being circulated through Ashab al-Yamin and Safee al-Deen channels, illustrating how identical content is redistributed across different nodes within the network, often with variations in framing and presentation.

These examples illustrate how similar content is circulated, reframed, and redistributed across different channels, reinforcing visibility and narrative consistency.

The emergence of Ashab al-Yamin aligns with a broader pattern seen across similar ecosystems: the rapid creation of new identities designed to claim responsibility, amplify narratives, and generate strategic effects. Recent analysis by Militant Wire similarly suggests that the group may function less as a traditional organization and more as an “astroturfed” identity embedded within existing Iranian-aligned networks, leveraging low-cost, high-visibility activity to maximize perceived impact.

Rather than representing the development of a traditional, hierarchical organization, this model prioritizes speed, flexibility, and visibility. New entities can quickly establish a presence, insert themselves into ongoing events, and reinforce narratives already circulating across interconnected channels. As noted in reporting by CBS News, even relatively unsophisticated or ambiguous content can achieve outsized strategic effects. This aligns with analysis from the Foundation for Defense of Democracies, which notes that such models can rely on low-cost, deniable actors and coordinated messaging without requiring a formal organizational structure. Recent research by the Global Network on Extremism and Technology similarly highlights how digital actors across different ideological and operational backgrounds can converge within shared wartime ecosystems, forming loose networks that amplify common narratives and targets.

These dynamics are not limited to militant media channels. Similar patterns can be observed among pro-Iranian hacktivist groups, which use Telegram to promote alleged data breaches and advertise them on darknet marketplaces. For example, “APT Iran” has claimed to possess stolen data from Lockheed Martin, promoting it through Telegram and advertising it on a Russian-language darknet marketplace known as “Threat Market.”

The listing advertises an estimated value of approximately $374 million, with an exclusive buyout price nearing $600 million, alongside tiered pricing for partial data access. While these figures remain unverified, their scale reflects a broader pattern of inflated valuation and narrative amplification, where the perceived significance of a breach is emphasized as much as the underlying data itself.

Figures 18 & 19: APT Iran Telegram post referencing Lockheed; Lockheed leak posted on Threat Market

More recent activity suggests increasing instability and responsiveness to external pressure. Following attention surrounding the alleged Lockheed Martin leak, the actor associated with “APT Iran” appears to have changed its Telegram identity to “Brona

Blanco had begun posting images of purported source code tied to the breach. Concurrent messaging in Farsi references potential law enforcement scrutiny, including warnings about FBI targeting of infrastructure linked to Threat Market and the implementation of contingency measures such as a “dead man’s switch.”

Figure 20: APT Iran Telegram post referencing the FBI targeting Threat Market
Figure 21: APT Iran/Brona Blanco Telegram post referencing Lockheed Martin Source Code

While these claims remain unverified, this shift in tone and behavior reinforces a consistent pattern observed across these actors: rapid escalation in claims, reactive messaging driven by perceived pressure, and an emphasis on perceived impact over independently verifiable outcomes.

This same dynamic is evident in recent claims by a group calling itself “Ababil of Minab,” which has claimed responsibility for a cyber incident targeting Los Angeles Metro infrastructure. As reported by Dark Web Informer, the group used Telegram to publicize the claim, asserting large-scale data exfiltration and system disruption while providing limited verifiable evidence. While attribution remains unclear, the group’s messaging style and distribution patterns reflect characteristics observed across other Iranian-aligned or Iran-affiliated cyber personas.

Figure 22: “Ababil of Minab” Telegram posts claiming responsibility for a cyber intrusion targeting LA Metro

As with other actors in this ecosystem, the framing of the operation emphasizes scale and impact, including claims of hundreds of terabytes of data being wiped and additional sensitive data extracted. This reflects a recurring dynamic in which perceived significance is amplified through messaging rather than confirmed technical outcomes. This interpretation is consistent with emerging reporting on Iran-linked hybrid activity, where analysts have noted coordination across pro-Iranian online ecosystems and raised questions about the authenticity of some groups operating within them.

Harakat Ashab al-Yamin al-Islamia has emerged rapidly, but its fragmented Telegram presence, recycled media, and overlap with Iranian-aligned channels complicate its assessment as a standalone organization.

Instead, it is best understood as part of a broader ecosystem in which content is circulated, repurposed, and reinforced across multiple actors. In this environment, attribution becomes less about identifying a single origin point and more about understanding how narratives move across channels.

This model allows new entities to project visibility and claim relevance without demonstrating sustained operational capability, blurring the line between coordinated activity and opportunistic amplification.

As this ecosystem evolves, tracking how new entities emerge, gain visibility, and integrate into existing networks will remain critical to assessing how influence and perceived operational reach are constructed within these networks.

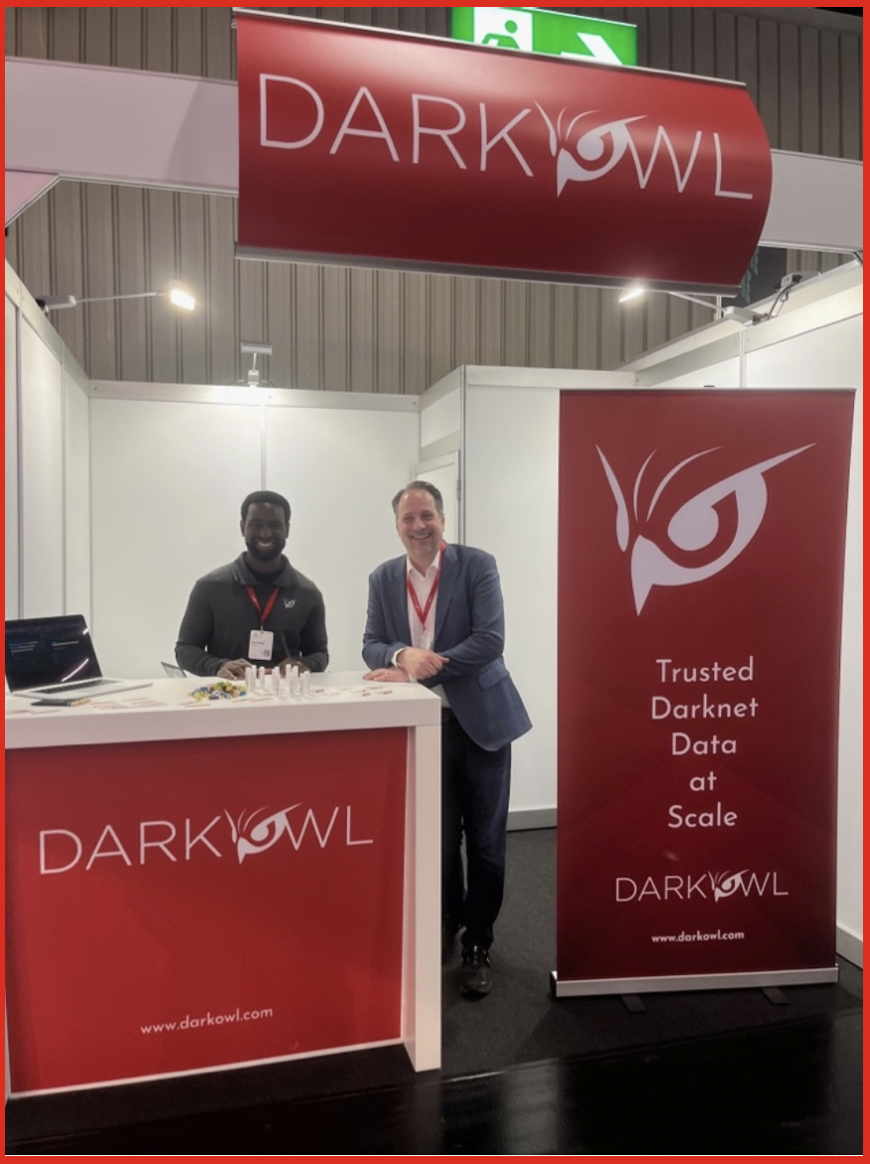
Keep up with the latest. Follow us on LinkedIn.

Threat Intelligence RoundUp: March

April 02, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. Fake Google Security site uses PWA app to steal credentials, MFA codes – Bleeping Computer

Using a fake Google Account security page, a recent phishing campaign was discovered delivering a web-based app designed to steal “one-time passcodes, harvesting cryptocurrency wallet addresses, and proxying attacker traffic through victims’ browsers”. The campaign uses social engineering and Progressive Web App (PWA) features to convince users that they are interacting with a legitimate Google webpage. The threat actors use the domain (google-prism[.]com) and have users follow a four-step process that gives permissions and allows the installation of malware. Once installed the malware can exfiltrate contacts, real time GPS data, and clipboard contents. Read full article.

2. UAC-0050 Targets European Financial Institution With Spoofed Domain and RMS Malware – The Hacker News

Recent social engineering attacks targeting European financial institutions has been attributed to the Russian linked threat actor, UAC-0050 (DaVinci Group). According to researchers, the attack mimicked a Ukrainian judicial domain “to deliver an email containing a link to a remote access payload.” The attack begins with a spear-phishing email designed to look urgent and legitimate. It uses legal-themed language to pressure the recipient into acting. The email includes a link that directs the target to download a compressed file hosted on PixelDrain, a file-sharing service. If the victim opens the fake “PDF,” the malicious file runs and installs an MSI package for Remote Manipulator System (RMS). Article here.

Surveillance firm, Intellexa, utilizes a single hook function (‘HiddenDot::setupHook()’) inside Springboard that prevents sensor activity updates in IOS products. This activity had been acknowledged previously, but the way the firm carried it out was not well understood. Recent research by Jamf analyzed Predator samples and was able to document the hiding process. The malware does not exploit IOS vulnerabilities but instead leverages “previously obtained kernel-level access to hijack system indicators that would otherwise expose its surveillance operation”. This information has helped address previously existing gaps in understanding the exploitation techniques used by commercial spyware. Read more here.

Since 2024, Chinese aligned threat group (Silver Dragon) has been observed operating within the umbrella of APT41 and targeting organizations throughout Europe and Southeast Asia. Silver Dragon gains its initial access by exploiting public-facing internet servers and delivering phishing emails that contain malicious attachments. To maintain persistence, the group hijacks legitimate Windows services, which allows the malware processes to blend into normal system activity. The group’s operations appear to specifically target government organizations. On compromised systems, they deploy Cobalt Strike beacons to maintain persistence, along with GearDoor, a backdoor that uses Google Drive as its command-and-control (C2) channel. Read here.

5. Medtech giant Stryker offline after Iran-linked wiper malware attack – Bleeping Computer

Iranian linked and pro-Palestinian hacktivist group, Handala, has claimed to have wiped tens of thousands of systems and servers belonging to medical technology company, Stryker. In a statement Handala stated “over 200,000 systems, servers, and mobile devices have been wiped and 50 terabytes of critical data have been extracted,”. The attack allegedly forced offices in 79 countries to shut down. The group does not give details on logistics but declared to target the company in “retaliation for the brutal attack on the Minab school” as well as the companies alleged “Zionist” ties. Learn more.

6. SLH Offers $500–$1,000 Per Call to Recruit Women for IT Help Desk Vishing Attacks – The Hacker News

On February 22, 2026, Scattered Lapsus$ Hunters (SLH) posted on their Telegram Channel stating, “if you are female and want to make some money via calling for us hit up”. The group is offering women $500-$1000 per call to help desks, with a provided written script. The recruitment seems to be an effort by the group to sidestep the “traditional” attacker profiles that IT help desk staff are trained to recognize, thereby making their impersonation attempts more convincing and effective. SLH’s primary objective is to target help desks and call centers as entry points into organizations, further highlighting the intent behind their new recruitment strategy. Read full article.

7. Poland’s nuclear research centre targeted by cyberattack – Bleeping Computer

On March 12, Poland’s National Centre for Nuclear Research (NCBJ) claimed hackers had targeted their IT infrastructure but were blocked before accessing information. The organization stated that its early-detection security systems and internal procedures prevented a breach and allowed IT staff to rapidly secure the targeted systems. The attack has not been formally attributed to any group. While Polish authorities say early indicators suggest a possible connection to Iran, they warn that the evidence could represent a false-flag attempt meant to take advantage of ongoing global tensions. Read full article.

8. SloppyLemming Targets Pakistan and Bangladesh Governments Using Dual Malware Chains – The Hacker News

SloppyLemming, a threat activity cluster, has been linked to two separate attack chains that delivered malware to government agencies and critical infrastructure operators in Pakistan and Bangladesh between January 2025 and January 2026. The first attack delivered PDF lure documents to victims that once open installed his application installed a package that included a legitimate Microsoft .NET file (NGenTask.exe) and a malicious file (mscorsvc.dll). The malicious file used a technique called DLL sideloading to run. It then decrypted and launched a custom 64-bit shellcode implant. The second attack deployed Excel documents that contained malicious macros that deliver “keylogger malware”. Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

The New Face of Deception

April 01, 2026

While you’re hopefully busy avoiding all the harmless classic April Fool’s jokes, the threat actors lurking in the corners of the darknet are busy perfecting much more convincing—and dangerous—”pranks”.

Over the last few years, we’ve tracked how phishing evolved from misspelled emails to AI-generated perfection. But this year, the joke is getting even more personal.

In our previous April Fools’ specials, we’ve explored everything from the absurdity of 24 hours on the dark web to the rise of AI-powered smishing. This year, threat actors aren’t just writing better emails—they’re stealing faces and voices. Threat actors have evolved. They’re no longer just blasting generic emails into the void—they’re refining tactics using real data, automation, and even AI-generated content to increase success rates.

The AI Factor

More and more phishing messages aren’t feeling like scams: no spelling errors, no awkward phrasing, no obvious red flags. That’s because they probably weren’t written by humans. AI is now being used to generate phishing emails, fake profiles, and even voice messages that mimic real people—making scams faster, cheaper, and more believable than ever. The old advice of “look for bad grammar” is quickly becoming outdated.

Here are the new ways threat actors are trying to “fool” you this year:

Using just a few minutes of public video from LinkedIn or a recorded webinar, threat actors can now overlay a “digital mask” in real-time; this is a deepfake. Don’t be fooled into your “boss” asking for an urgent wire transfer on what seems to be a standard zoom call. Watch for unnatural blinking, “glitching” around the neck area, or a slight delay between their mouth moving and the audio.

We’ve warned about vishing (voice phishing) before, but it has leveled up. Threat actors no longer need to “act” like your IT person. With as little as 30 seconds of audio, they can clone a specific person’s voice to leave a voicemail that is indistinguishable from the real thing. Our analysts have seen a 40% uptick in “Urgent Voicemail” scams where the actor impersonates a C-suite executive requesting a password reset “while they’re boarding a flight.”

Forget the broad survey scams and junk car emails from the past. Today’s threat actor uses AI to scrape your entire digital footprint—your recent vacation photos, your “workversary” post, and even your favorite coffee shop—to build a persona that feels like a long-lost friend. We always suggest exercising caution when sharing online. Imagine this: you return home from attending a work conference and get a message on LinkedIn: “Hey [Your Name], saw you were at the Cybersecurity Summit last week! I’m the guy who sat next to you during the AI keynote. Here’s that whitepaper we discussed.” One click, and you’ve installed a specialized infostealer.

Spotting a digital deception requires a keen eye and a bit of healthy skepticism.

  • Implement a “Safe Word”: For high-stakes financial transactions, establish an offline “challenge-response” phrase that only your team knows.
  • Trust, But Verify: If your “boss” makes an unusual request via video or voice, hang up and call them back on a known, trusted number.
  • Assume Nothing is Private: If it’s on the internet, a threat actor can use it to build a profile of you. Tighten those privacy settings!

Cyber threats continue to evolve—but the fundamentals still matter: enable multi-factor authentication, use strong, unique passwords, verify before you click, and stay informed.

Technology moves fast, but the goal of the threat actor remains the same: to exploit human trust. This April Fools’ Day, let’s keep the surprises limited to harmless office pranks. Stay vigilant, stay skeptical, and remember: if a request feels “off,” it probably is.
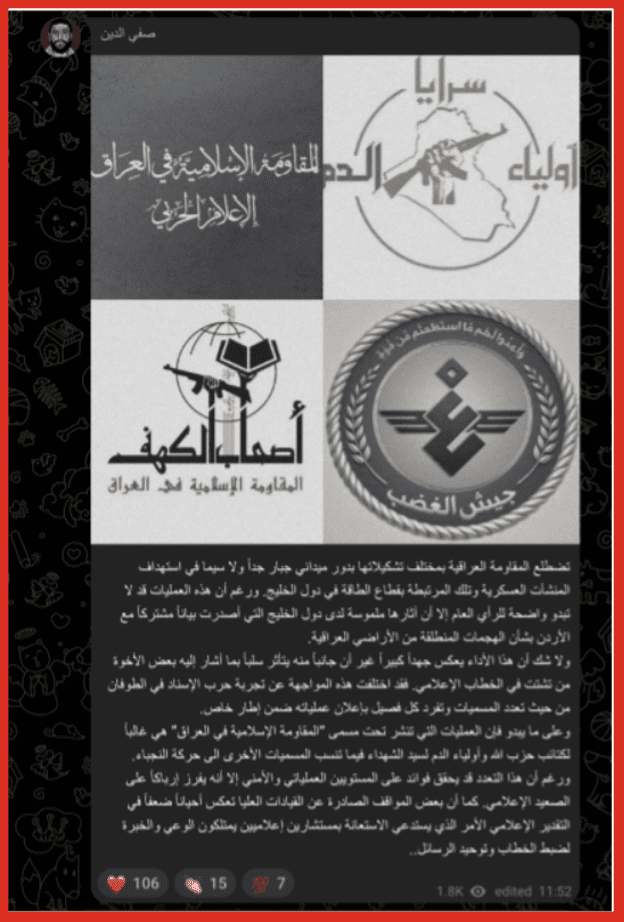

Follow us on LinkedIn.