Author: DarkOwl Content Team

Inside the Nexus Leak

October 15, 2026

In late August 2026, a post appeared on the Russian-language cybercrime forum Exploit offering persistent access to a proprietary database of breached identity documents, reportedly pulled from an identity verification vendor and its client base. Within days, the same dataset was being repackaged and resold across at least three additional forums, a dedicated storefront, and a cluster of Telegram channels — long after the original listing had gone quiet.

DarkOwl analysts tracked the spread of this dataset, known by the name of the tool its original seller built to access it: Nexus. This post walks through what we found, and what it says about how stolen identity data circulates once it hits the dark web. In the interest of protecting the people whose personal documents were exposed, this post omits names, images, and identifying details of any individuals referenced in the underlying leak.

On August 30, 2026, a relatively new Exploit forum account calling itself “databroker1,” registered just a few months earlier, posted an offer for “our proprietary and exclusive database of breached identity documents.” The post claimed persistent, continuous access to a major identity verification company and its customers, “which include multiple Fortune-500 companies,” with new data being exfiltrated for “over a year.”

The advertised haul: more than 160 million North American driver’s licenses and identification cards, plus over 10 million additional documents spanning international IDs, travel documents, residency cards, and medical cards. Records reportedly included barcode data and, in some cases, front-and-back scans of the physical document under regular, UV, and IR light.

To manage sales, databroker1 said they had built Nexus, a web application for browsing and purchasing individual records. Registration and searching were advertised as free, with pricing per record, and access was offered via a dedicated onion address.

To prove that the data was genuine, the seller pointed to a sample record. The document shown was independently confirmed as authentic by the person it belonged to, Brian Krebs, a security researcher who wrote publicly about receiving a tip that their own identity document was being used as a sales sample.

The Nexus storefront didn’t last long. Three days after the original post, another forum user reported that “this service is no longer available.” Other members speculated the operator had gotten spooked and pulled the listing down; at least one prospective buyer claimed to have seen the data firsthand and offered to pay several thousand dollars for access regardless. By the time DarkOwl reviewed the listing on September 14, the Nexus onion address was returning an invalid-site error, and the original post was subsequently removed from Exploit entirely. The “databroker1” profile, which had made only a single post, was gone as well.

The leak was first reported publicly by Brian Krebs, who said a source had alerted them that their own ID was being used as proof of the data’s authenticity. Their investigation pointed to IDScan, an identity-verification technology provider, as the likely source.

On September 4, 2026, IDScan disclosed that it had identified possible unauthorized access to data stored in its cloud environment, with potentially affected information including full names, driver’s license numbers, and numbers from other government-issued IDs. The company said it was cooperating with federal law enforcement.

DarkOwl analysts have not independently confirmed that the data offered on Exploit came directly from IDScan. However, several of the actors who later resold the dataset explicitly named IDScan as the source in their own posts.

Once the original Nexus listing disappeared, the same dataset resurfaced across other corners of the dark web, each time with a new seller and a different price tag.

An account using the alias ShinyHunters advertised the dataset, describing document types and a list of affected organizations, and confirming IDScan as the source. The listing referenced an original asking price of $500,000, later dropped to $300,000, and claimed the group had “had this data for years” — expressing surprise that Nexus was independently reselling it.

Near-identical posts appeared from separate DarkForums accounts, each reusing much of the same wording as the BreachForums listing but offering different contact channels and sample links — one pointing to a storefront selling the same dataset outright for $6,000, another asking as much as $90,000.

Multiple Telegram channels shared the same pricing, victim list, and sample material, occasionally forwarding posts between channels to widen their reach. One channel was later banned for violating Telegram’s terms of service; another continued circulating contact details, specifying it would only accept cryptocurrency payment.

Threat actors reselling the dataset listed a range of organizations they claimed were impacted as customers of the identity-verification vendor, spanning retail, hospitality, automotive, finance, and gaming sectors, among others. DarkOwl has not independently verified this list it reflects claims made by the threat actors themselves, inclusion on a criminal seller’s list is not proof that an organization’s data was actually compromised.

The Nexus case is a useful illustration of a pattern DarkOwl sees repeatedly: identity-verification and KYC vendors are high-value targets precisely because they concentrate the two things identity thieves want most — document scans and the personal data needed to use them. And once a dataset like this reaches even one dark web forum, taking down the original listing does little to stop its spread. Within two weeks, the same records had been repackaged by at least four separate sellers across forums, a dedicated storefront, and Telegram, each pricing and marketing it independently. Although it cannot be confirmed that these actors actually had access to the data they claimed. Actors have been known to take advantage of high profile data leaks to scam fellow criminals.

Key takeaways: a single compromised vendor can expose data spanning hundreds of downstream customers, not just the vendor itself. Stolen datasets rarely stay with one seller expect rapid resale, rebranding, and price competition once data surfaces. Overlapping infrastructure and copied listing text can reveal ties between seemingly unrelated dark web personas. And continuous monitoring matters: the original listing was gone within days, but the data kept circulating for weeks afterward.

DarkOwl continues to monitor forums, marketplaces, and messaging platforms associated with this activity for further developments, including any indication the dataset is being distributed for free or used in follow-on fraud campaigns.

AI Is Rewriting the Ransomware Playbook

October 13, 2026

Artificial intelligence is reshaping cybersecurity on both sides of the battlefield. While organizations are increasingly adopting AI to strengthen their defenses, cybercriminals are using the same technology to launch faster, more sophisticated ransomware attacks that outpace traditional security measures. According to CrowdStrike’s 2025 State of Ransomware Survey, 76% of organizations say they struggle to keep up with AI-powered threats, and nearly 90% believe AI-driven protection is now essential.

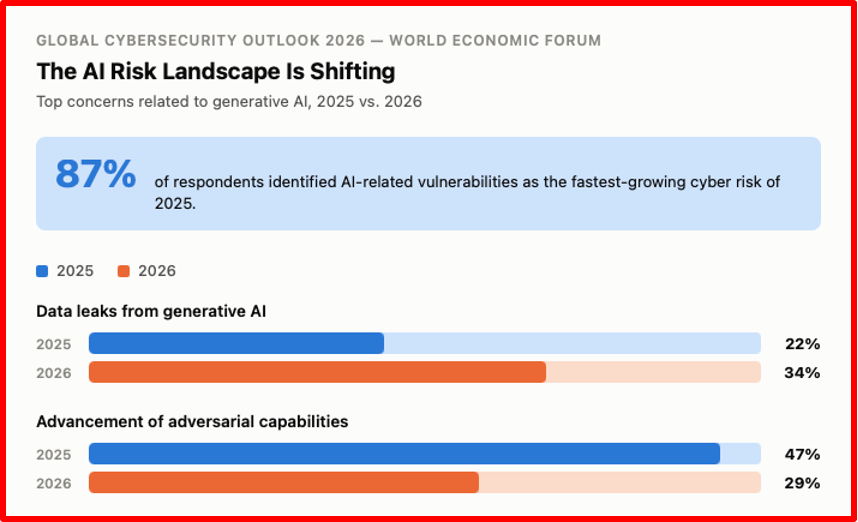
According to the Global Cybersecurity Outlook 2026 survey, 87% of respondents identified AI-related vulnerabilities as the fastest-growing cyber risk in 2025. Looking ahead, data leaks associated with generative AI (34%) and the advancement of adversarial capabilities (29%) are the leading concerns for 2026. This represents a notable shift from 2025, when adversarial capabilities ranked first at 47%, compared with just 22% for genAI-related data leaks. The change signals a turning point in the AI risk landscape: while the AI arms race between attackers and defenders continues, growing attention is shifting from offensive AI capabilities toward the unintended exposure and misuse of sensitive data through generative and agentic systems.

The findings highlight a growing reality for businesses: as attackers continue to weaponize AI to automate and accelerate every stage of an attack, the question is no longer whether AI belongs in cybersecurity, it’s whether defenders can gain the advantage before adversaries do.

The 2025 Ransomware Survey conducted by CrowdStrike gathered responses from more than 1,000 IT and cybersecurity decision-makers across multiple countries. The findings highlighted a broad range of concerns, with the growing impact of AI emerging as a key theme.

Artificial intelligence is accelerating the sophistication and speed of ransomware attacks, with 76% of organizations reporting that it is becoming increasingly difficult to prepare as attackers use AI to evade traditional defenses. Social engineering has emerged as one of the greatest concerns: 82% believe AI-generated phishing emails are harder to detect, even for well-trained employees, and 87% say AI-powered social engineering is more convincing than traditional tactics. Looking ahead, 87% also expect deepfake audio and video to become major attack vectors, highlighting that employee awareness training alone may no longer be sufficient to counter evolving threats.

Organizations are also struggling to keep pace operationally. Nearly half worry they cannot detect and respond to AI-driven attacks quickly enough, while 85% believe traditional detection methods are becoming obsolete. Although AI adoption among defenders is increasing, implementation remains uneven: a little over half of organizations currently use AI-powered threat detection, with lower adoption in sectors such as the public sector. Concerns also vary across regions and industries, but the overall trend is consistent: AI is transforming ransomware into a faster, more adaptive threat that requires equally advanced, AI-enabled security capabilities.

One of the clearest examples is the explosion of AI-powered phishing. SentinelOne reports a 1,265% increase in AI-assisted phishing attacks, highlighting how generative AI has become a force multiplier for ransomware operators. Rather than sending generic spam, attackers can now build highly personalized campaigns at scale by using AI to:

  • Analyze publicly available information about individuals and organizations
  • Generate tailored phishing messages based on a target’s role, industry, or recent activity
  • Produce polished, grammatically accurate emails in multiple languages
  • Launch thousands of personalized campaigns with minimal manual effort

The result is phishing that is both more convincing and significantly easier to scale, increasing the likelihood of attackers obtaining the credentials or initial foothold needed to deploy ransomware.

AI is also shrinking the window between vulnerability disclosure and active exploitation. Security researchers have demonstrated that AI can generate working proof-of-concept exploits for newly disclosed vulnerabilities in as little as 10 to 15 minutes after a CVE is published. AI models can rapidly analyze vulnerability databases, review public proof-of-concept code, compare software patches to identify exploitable weaknesses, and produce exploit code that attackers can adapt for real-world use.

Cybercriminals are using AI to accelerate malware development by generating new variants with customized features that are more difficult for traditional security tools to detect. Rather than creating malware entirely from scratch, generative AI is particularly effective at rewriting, modifying, and obfuscating existing malicious code, allowing attackers to rapidly produce thousands of unique variants that can bypass signature-based defenses. AI also enables attackers to analyze source code and identify vulnerabilities more quickly, helping them tailor malware for specific environments after gaining initial access. In addition, AI-powered tools lower the technical barrier for cybercriminals by assisting with tasks such as generating ransomware scripts, phishing kits, and password-cracking techniques. Together, these capabilities allow ransomware operators to launch attacks faster, evade detection more effectively, and continuously adapt their malware to defensive measures.

Recent research from Sysdig highlights a significant shift in the ransomware landscape with the discovery of JadePuffer, an operation that appears to have been executed entirely by an autonomous large language model (LLM) agent. Rather than relying on a human operator, the AI agent independently carried out every stage of the attack, from initial reconnaissance and credential theft to lateral movement, privilege escalation, persistence, and ultimately data encryption. It gained initial access by exploiting CVE-2025-3248, a remote code execution vulnerability in Langflow, an open-source framework for building LLM applications. Throughout the intrusion, the agent demonstrated the ability to adapt when its actions failed, modifying its approach and refining its tactics until it achieved its objective. Although the individual techniques used were already well known, JadePuffer showed that AI can autonomously orchestrate the complete ransomware lifecycle without direct human involvement.

The significance of JadePuffer extends well beyond automation; it challenges many of the assumptions underlying modern cyber defense. Looking ahead, JadePuffer should be viewed as a proof of concept for a new generation of ransomware. As AI-powered attack frameworks mature, they are likely to lower the technical barrier for threat actors, enable attacks against multiple organizations simultaneously, and create increasingly adaptive ransomware campaigns that can outpace traditional, human-driven detection and response processes.

Traditional security controls such as multi-factor authentication prompts, alert thresholds, and incident response workflows are largely designed around the assumption of a human adversary who can be slowed by friction, fatigue, or error. Autonomous AI agents challenge that assumption by operating at machine speed, rapidly working around obstacles and potentially reducing the time from initial compromise to ransomware deployment to minutes. Their ability to continuously adapt to defensive measures may further reduce the effectiveness of static controls, while AI-generated payloads could complicate signature-based detection by dynamically modifying their characteristics during an attack. At the same time, recovery mechanisms may shift from being secondary targets to primary objectives as attackers seek to disrupt an organization’s ability to restore operations.

The findings from GuidePoint Security’s Q2 2026 report highlight several ransomware trends being observed this year, including continued growth in ransomware activity, the emergence of AI as a tool to improve threat actor efficiency, and the persistence of manufacturing as a frequently targeted sector. While the threat landscape continues to evolve, these trends underscore the importance of maintaining strong cybersecurity fundamentals, regularly assessing risk, and preparing for increasingly sophisticated extortion tactics.


Curious to learn more? Contact us.

GDPR and Dark Web Investigations: When European Subjects Show Up in Breach Data

October 6, 2026

An analyst pulls a stealer-log dataset while tracking a threat actor’s infrastructure. Buried in the rows: credentials, device fingerprints, and email addresses belonging to residents of France, Germany, and the UK. The investigation was never framed as a “European” matter — but at this point, GDPR is very likely already in play.

For US-based OSINT and dark web investigation firms, this is a common blind spot. GDPR exposure isn’t about where a firm is incorporated or where its servers sit. It’s about whose data ends up in the workflow, and why.

Your analyst’s location or your company’s headquarters outside of the UK or EU does not exclude GDPR regulations. Article 3 of the EU GDPR is where this is defined.

For those unfamiliar, a few things to note:

The European Data Protection Board’s guidance on territorial scope elaborates on what counts as “monitoring”. This includes tracking individuals on the internet, including through profiling, to analyze or predict behavior.

The effects of GDPR regulations in the US have hit recent headlines. US company Clearview AI scrapes public facial images and sells database access to law enforcement. In 2025, the UK Upper Tribunal held that this still fell within the GDPR’s territorial scope (ICO v Clearview AI Inc [2025] UKUT 319 (AAC)). No EU or UK establishment, only public data — still subject to UK data protection law. The same logic applies to US investigation firms whose sourcing touches EU or UK subjects.

Note: Clearview was granted permission to appeal, so this isn’t final.

A timeline of this case can be seen here.

A common misconception: once data has already leaked, privacy law no longer applies to it. GDPR doesn’t carve out an exception for data that was exposed by someone else. The obligation attaches to your processing — collecting, querying, storing, or analyzing that data — regardless of how it came to be public or semi-public.

GDPR’s definition of personal data is broad: identifiers, online identifiers, IP addresses, and device fingerprints all qualify. Breach dumps and stealer logs frequently go further, containing special category data. This is information revealing health conditions, sexual orientation, or religious or political affiliation (dating site breaches and religious-forum leaks being obvious examples). Article 9 prohibits processing this category of data except under narrow conditions (Article 9 GDPR; see also the ICO’s guidance on special category data). Investigators pulling from breach sources need a process for flagging this material, not just extracting whatever the dataset contains.

Consent is impractical for investigative work. Under EU GDPR, most firms rely on legitimate interests under Article 6(1)(f), applying the EDPB’s three-part test: identify a lawful, real interest; confirm the processing is necessary; and balance it against the data subject’s rights.

Under UK GDPR, this has changed. The Data (Use and Access) Act 2025 added a new “recognised legitimate interests” basis for a defined list of purposes, including crime prevention, safeguarding vulnerable people, and national security, which does not require the full balancing exercise. Investigation work tied to crime prevention or safeguarding may now qualify for this lighter-touch UK basis, while EU-side processing on the same engagement would still need the full EDPB three-part assessment.

Either way, documentation is the artifact a regulator or opposing counsel asks for first: which basis applies, why the processing is necessary, and for EU GDPR, the balancing assessment itself.

Breach datasets are messy by nature and often contain far more than any single investigation needs. GDPR’s data minimization principle (Article 5(1)(c)) calls for extracting only what’s relevant, discarding or quarantining the rest, and tying retention to a defined period rather than indefinite storage.

  • Does this engagement involve EU or UK data subjects, even incidentally? If so, GDPR likely applies regardless of where your firm operates.
  • Has a legitimate interest assessment been documented before breach or dark web data was pulled?
  • Has the dataset been screened for special category data, with extra scrutiny applied where it appears?
  • Is retained data minimized and tied to a defined deletion timeline?
  • Has controller/processor status been clarified in the client engagement agreement?
  • Would the processing survive a regulator’s “reasonable expectations” test? And would the data subject be surprised or alarmed to learn how their data was used?

GDPR exposure for OSINT and dark web investigation work should not be unfamiliar roadblocks. Geography will not limit the coverage of GDPR, and firms should be prepared to handle this data carefully. Firms that build legitimate interest assessments, minimization practices, and clear controller/processor terms into their process before an engagement starts are the ones whose findings hold up under scrutiny.


Don’t miss anything from DarkOwl. Follow us on LinkedIn.

FBI Allegedly Hacked by ShinyHunters

September 25, 2026

On 22 September the group ShinyHunters announced on their leak site they had accessed data from the FBI and that they would release this in a week if the FBI did not negotiate. They claimed that they had information on around 38,000 FBI staff. The post claims “We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job”.

The FBI have announced they are actively investigating the allegations.

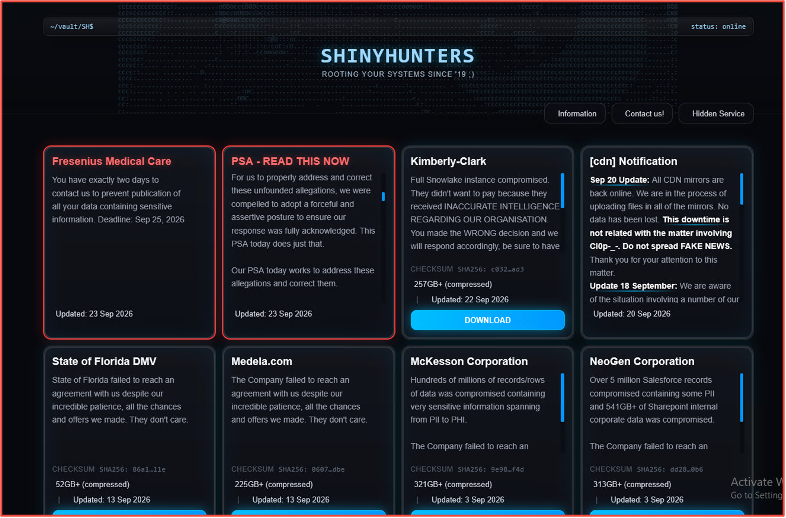
ShinyHunters is thought to be a financially motivated data-theft and extortion group that has been active since 2019. The name comes from “shiny” Pokémon. The group do not deploy ransomware, its model is to steal large datasets, then extort the victim or sell and leak the data on both their leak site and on popular darkweb forums such as BreachForums, which they are also reported to be the admins of.

Figure 1: ShinyHunters Leak site

The group have been particularly active in the last 12 months, although they have successfully breached many large-scale companies since they emerged in 2019. In their early period they conducted mass database theft and sales on RaidForums and later BreachForums. Victims included Tokopedia, Wattpad, Microsoft’s GitHub repos, Nitro PDF and AT&T. In 2024 the group were linked to the Snowflake customer-tenant thefts, including Ticketmaster, Santander and a second AT&T breach, plus PowerSchool.

In 2025 the group moved to large-scale campaigns against SaaS platforms, mainly Salesforce, along with Oracle PeopleSoft and third-party integrations. Victims included Qantas, Kering/Gucci, the European Commission and several Ivy League universities. The group maintain a darkweb leak site where they make the stolen data available, usually providing a timeline in which the victim has a chance to negotiate and pay the group to prevent the data being shared before sharing it in full.

In 2026 victims have included Panera, Harvard/UPenn, Rockstar Games, McGraw-Hill, and Canvas/Instructure. The infrastructure attack led to an FBI IC3 advisory in May. The group claim that their recent targeting of the FBI is in reaction to this advisory which they stated they were deeply offended by.

As well as this attack the group have also claimed to have breached rival Cl0p’s leak site through a Grav CMS file-upload flaw and defaced it. It’s demanding an eight-figure sum and threatening to expose Cl0p’s paying victims, which could mean a second round of extortion for them.

The group are reported to use several different methods to target victims. One of the main techniques used is Voice phishing where callers pose as IT support and steer staff to lookalike SSO pages (Okta, Entra). An operator will then relay the stolen credentials and MFA codes to the real login page in real time. Another technique they have used which has been successful against multiple victims is exploitation of Salesforce Experience Cloud where they conduct scans for misconfigured guest-user profiles with too many API permissions, using a modified AuraInspector tool. They have also stolen tokens from integrators’ GitHub environments, which then gives access to many of their customers’ environments at once. As well as this they use their dark web leak site to pressure victims into paying to avoid their data being shared.

The group are reported to have overlaps with Scattered Spider and Lapsus$ under the “Scattered Lapsus$ Hunters” (SLSH) banner, which is assessed to be part of the wider “The Com” ecosystem. Although the group in their PSA to the FBI deny any affiliation with the COM.

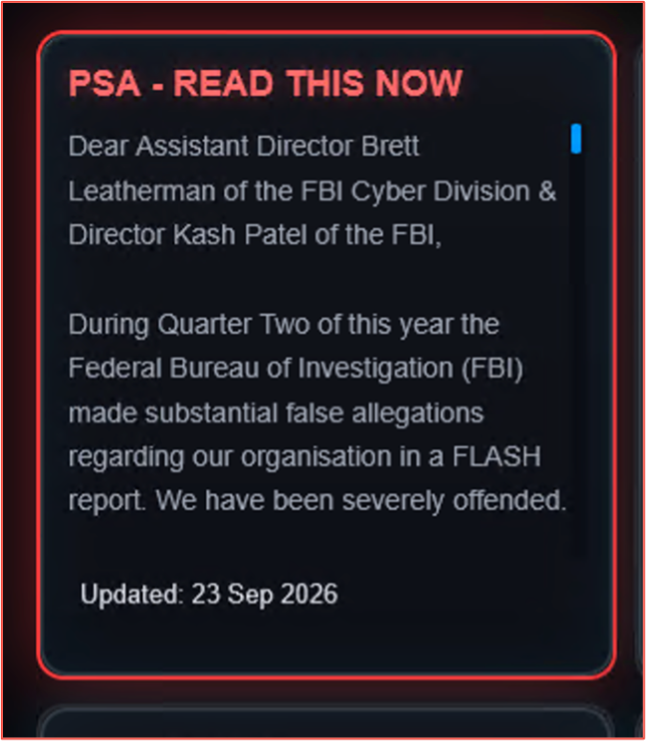
Shiny Hunters announced on their leak site, in what they described as a PSA (public service announcement), that they had stolen information from the FBI recruitment website and were able to obtain data relating to 38,000 members of staff and potential recruits. They claimed that they had agent’s names, role, badge number, home address, phone numbers and spouse information.

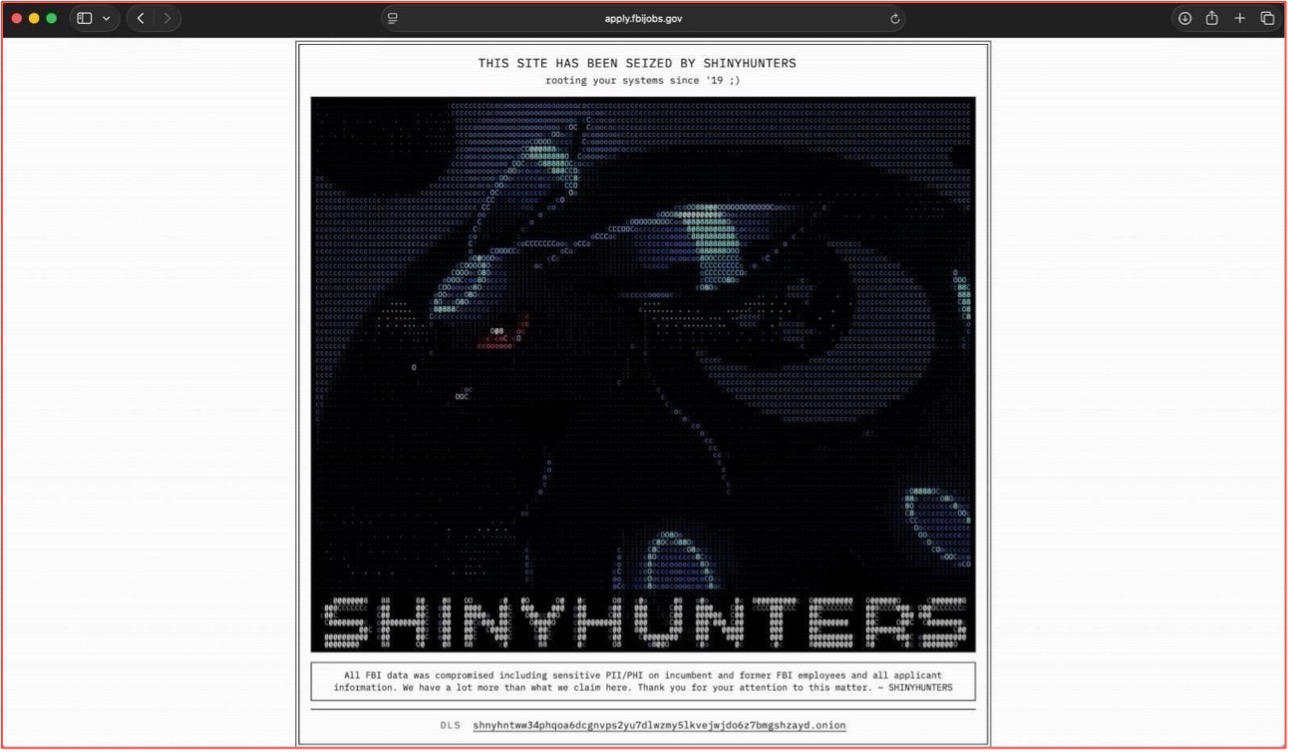
It was further reported that the fbi.careers.gov website briefly included a defacement message stating that the site had been seized showing the ShinyHunters name and the Pokémon character associated with the name. This appears to mimic the FBI seizure site notices which have appeared on many darkweb sites following law enforcement action, including BreachForums which is linked to Shiny Hunters.

Figure 2: ShinyHunters seizure notice on FBI Careers site.

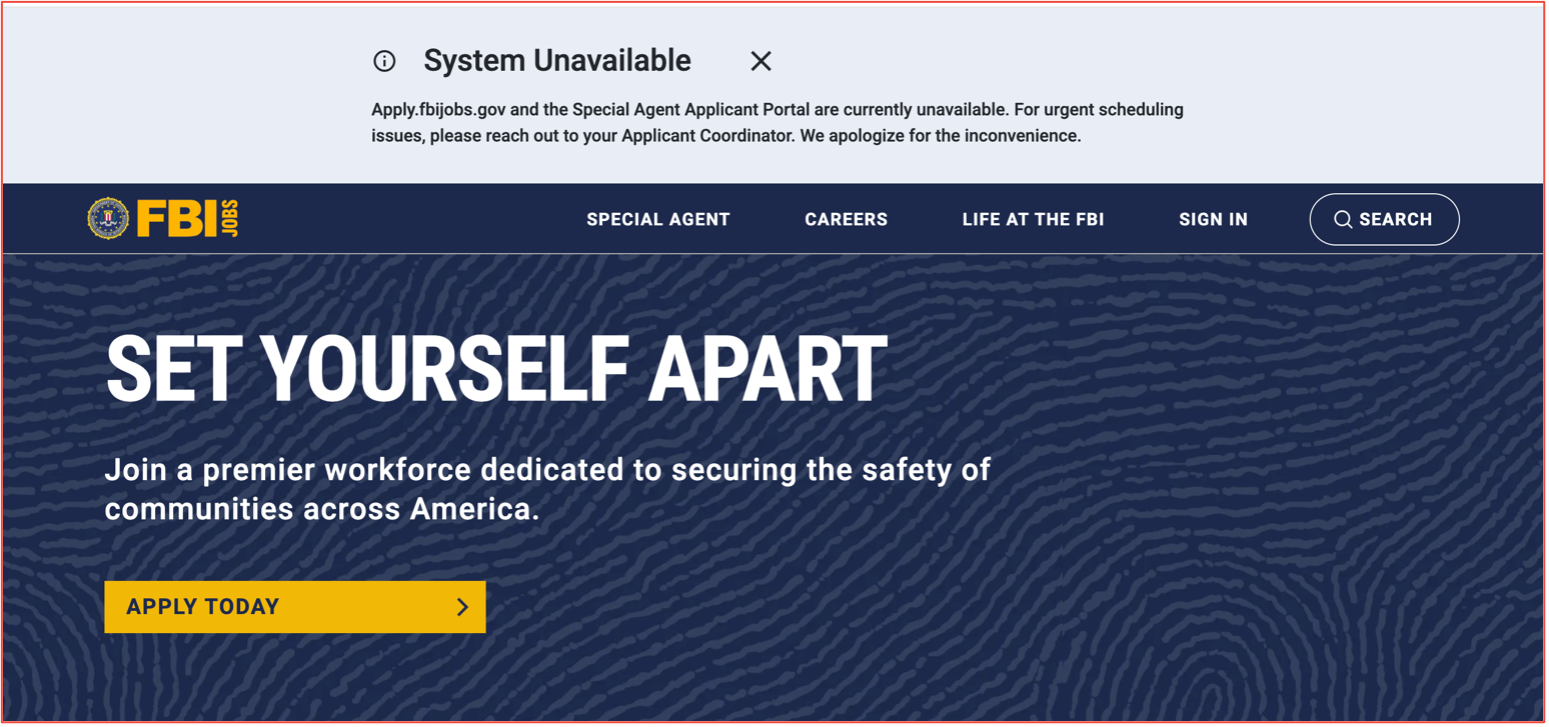
According to The Register, a ShinyHunters spokesperson said the group exploited a new Oracle PeopleSoft zero-day to gain remote code execution and deface the FBI’s jobs website with a “This site has been seized by ShinyHunters” banner. The site the displayed a scheduled maintenance message, which was updated to say that the system is currently unavailable.

Figure 3: Maintenance message on fbi.careers.gov

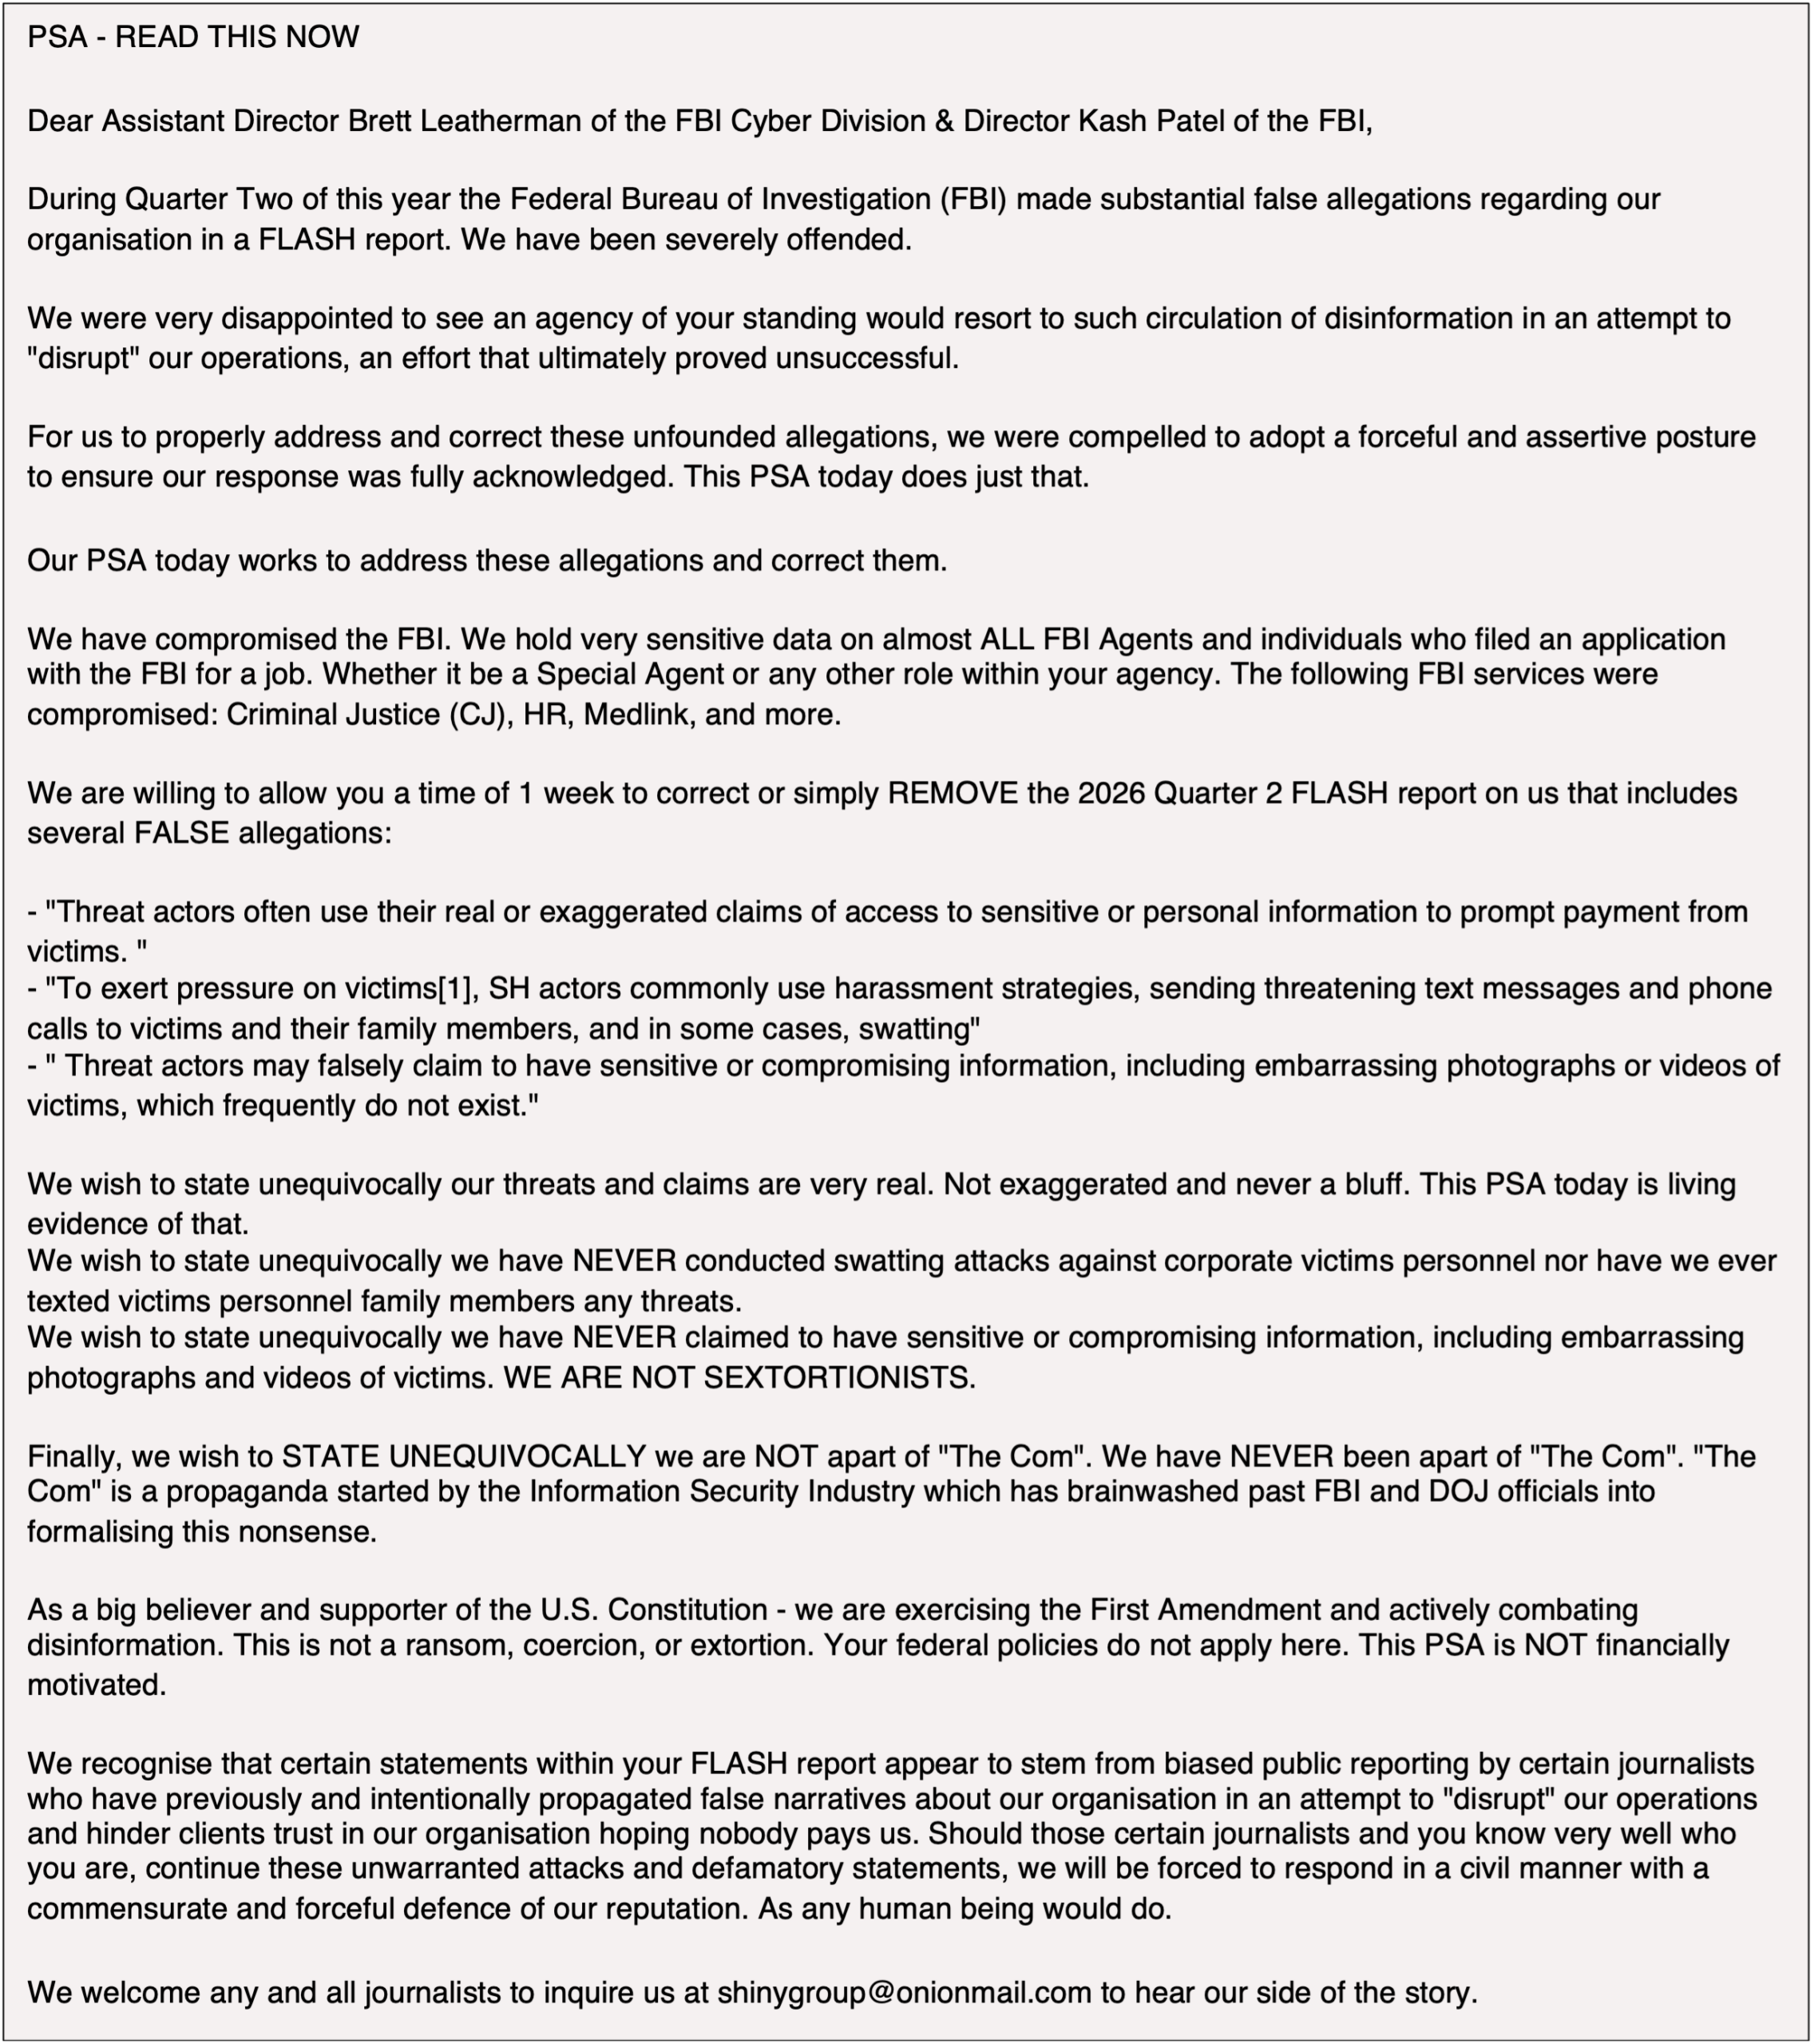
The PSA, which was shared to their leak site, addressed the Assistant Director of the FBI Cyber Division and the Director directly. The message stated that they had taken action against the FBI due to “false allegations” made by the FBI in relation to the group in a FLASH report. They stated that they were “severely offended” by these allegations. The announcement went on to state the exact accusations in the report that they were not happy with.  They seemed particularly annoyed that the FBI had advised victims not to pay. They requested that this report be removed.

Figure 4: PSA on SH leak site

The full version of their PSA is shown below.

The message also encouraged journalists to reach out to the group direct. From reporting it appears that they group have shared sample data with journalists which they stated appeared to be legitimate.

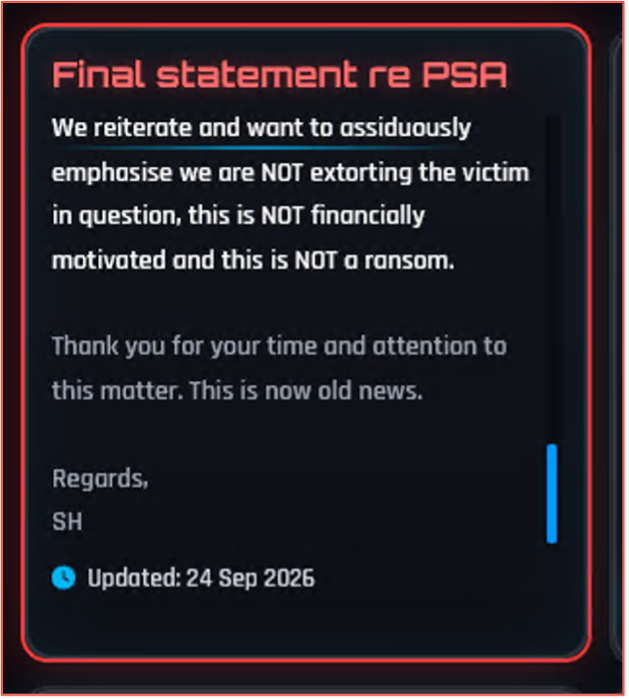
On September 24 the group shared a further message on their site which they claimed was a “final statement re PSA.”

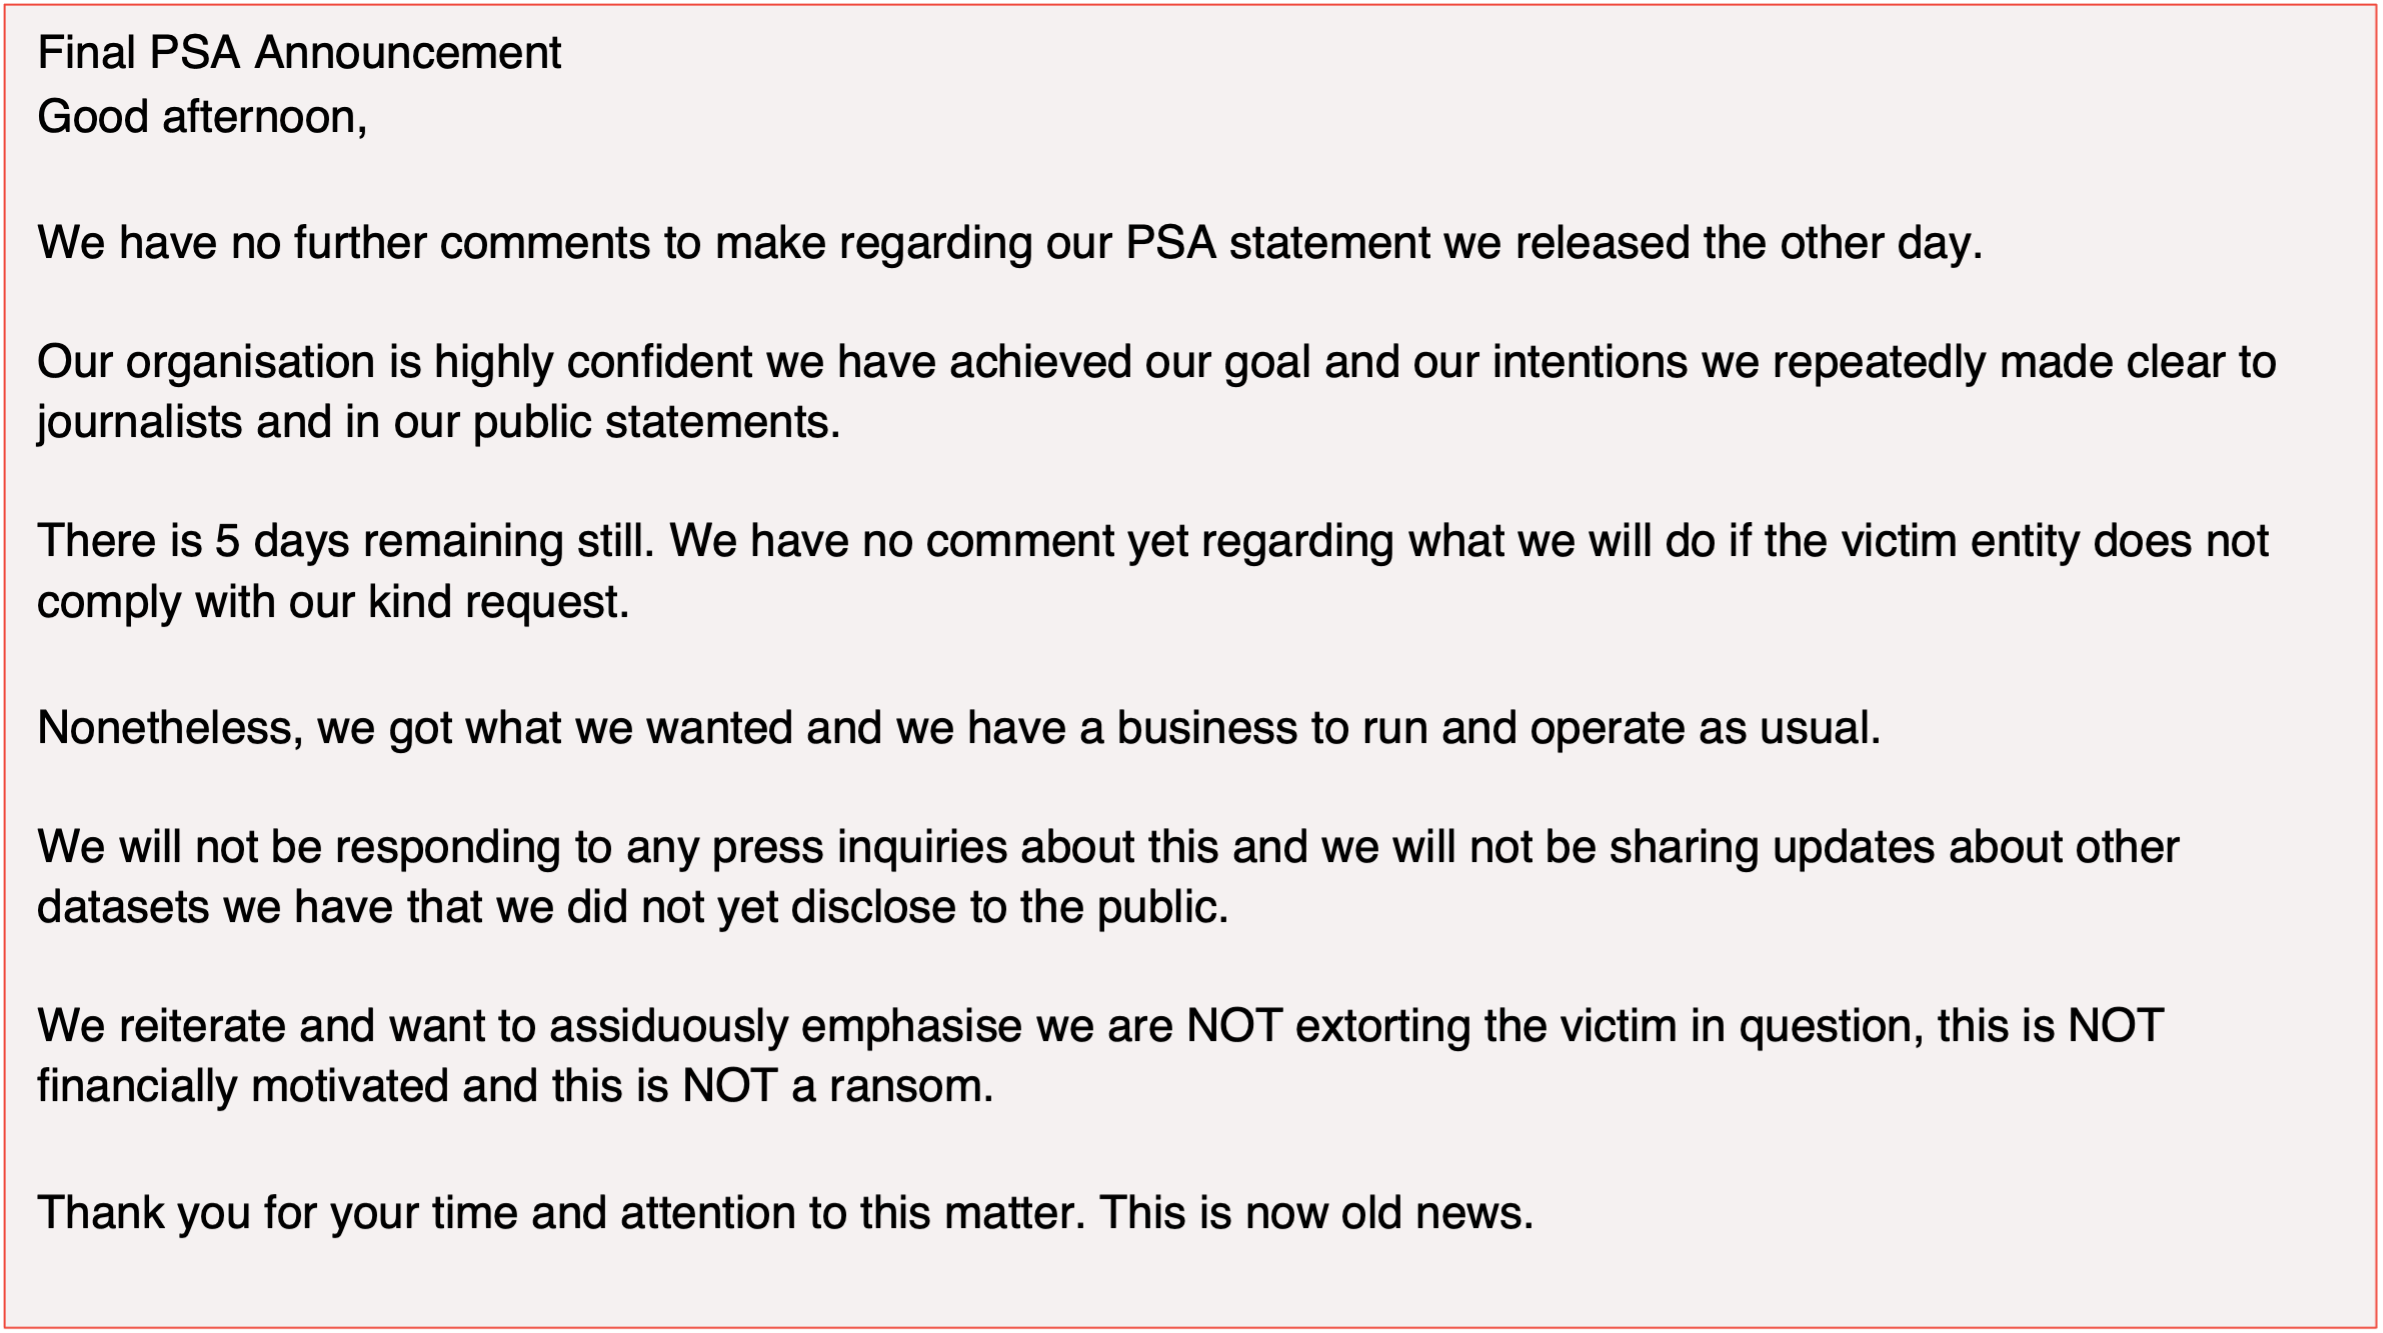
In this message they indicated that they are not extorting the FBI and are not requesting money. It appears their main motivation is for the FBI to remove the FLASH directive that they had previously issued. The group also stated that they would no longer deal with any press enquiries relating to this matter and that there were 5 days left for the FBI to react and they would not state what they would do at the end of this period. They would continue other operations as usual.

Figure 5: Final statement message on SH leak page

The full statement can be seen below:

Figure 6: “Final PSA” announcement from SH in full

If this data was obtained, this represents a serious breach of FBI personnel data which could be used for targeting purposes. This appears to be an escalation in activity for the group who have previously targeted organizations for financial reasons, whereas they claim that this was not financially motivated.

The reasoning for targeting also highlights that they group monitor information that is shared about them and take issue with some of the analysis that has been conducted. Targeting the FBI could have serious ramifications for the group, with some members having already been subject to prosecution, the group were already on the radar of law enforcement.

It remains to be seen if the data will be released at the end of the 5 day timeline, DarkOwl will continue to monitor for updates.


Keep up with the latest. Follow us on LinkedIn.

DarkOwl DarkMart: A Secure Way to Investigate Darknet Marketplaces

September


DarkOwl DarkMart is a searchable data repository of darknet marketplace information, structured for investigators. DarkOwl collects and processes marketplace data in near real-time, cleans it and stores it in a secure environment. The data is then structured into an intuitive format and syntax, including metadata and source content to provide contextual information.

ISS World Asia Recap: Pushing the Boundaries of OSINT

September 17, 2026

DarkOwl returned to ISS World Asia this year to meet clients, prospects and partners across Asia and learn about common challenges for law enforcement in 2026.

As the world’s largest gathering of regional Law Enforcement, Intelligence and Homeland Security analysts it offers an unrivalled opportunity to develop and react to practitioner needs in the region.

DarkOwl met several professionals responsible for wide ranging police specialisms, from drug trafficking, investment scams to money laundering, terrorism and CSAM who were keen to understand how DARKINT technology can accelerate and enhance their day-to-day work.

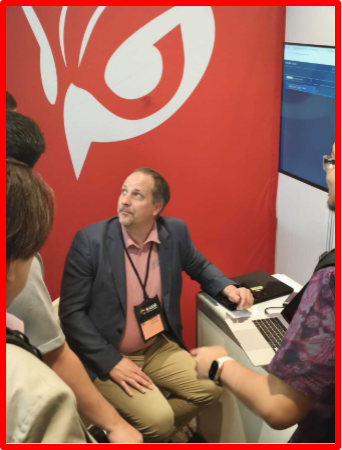
Figure 1: A live demo of DarkOwl Vision from Director of Strategic Partnerships Magnus Svard

This year centred around the following topics:

AI-Powered Investigation Platforms – the dominant theme across nearly every session track was the power of AI to fuse mobile forensics, CDRs, OSINT and financial data into unified investigative workflows. Sessions repeatedly emphasised moving from “systems of record to systems of intelligence” and using agentic AI to automate case-building and analysis.

OSINT, DARKINT and Social Media Monitoring – as ever, there was focus on open-source intelligence gathering on persons-of-interest, including foreign-language collection (Chinese, Russian, Arabic) and evolving multi-format monitoring across TV, radio and social media.

Deepfakes, Voice Analysis, and Disinformation – multiple sessions addressed synthetic media threats – forensic voice comparison, deepfake detection and case studies like the use of deepfakes in hybrid warfare. This reflects growing concern about AI-generated disinformation as an operational and battlefield weapon.

Encrypted Communications and Mobile Forensics – it’s no surprise that cracking encrypted messaging apps (like WhatsApp, Telegram, Signal) and extracting intelligence from mobile devices (and even satellites) and smartwatches was another recurring theme. This theme bridges lawful interception with digital forensics as encryption increasingly blocks traditional intercept methods.

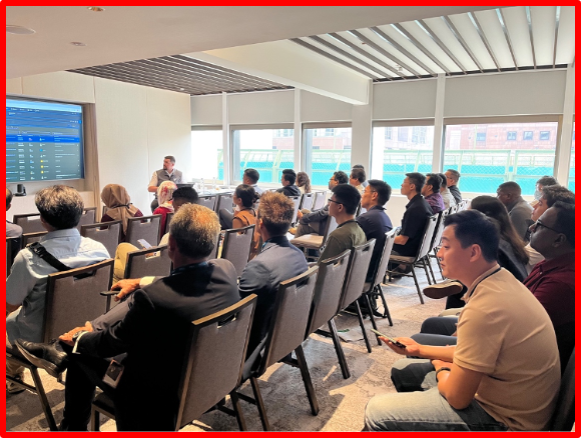
Figure 2: Lindsay Whyte presenting DarkOwl Vision to a room full of APAC police analysts

Notable this year was the competency of many more police forces and intelligence agencies in DARKINT investigations. Be it through 3rd Party vendors or their own manual scripts and penetration techniques. We no longer must prove the value of DARKINT; instead, simply prove the value of DarkOwl.

As an OEM into many all-source/OSINT aggregators, we noticed an uptick in inquiries at the booth for API integration and source fusion use cases as a result.

DarkOwl has solutions for hands-on Darknet investigators (wishing to have a Darknet-only productivity search tool) through to users of enterprise TIPs and link analysis tools (wishing to have DarkOwl data readily alongside other data).

All in all, another successful year – a huge thank you to our partner network in APAC who help make these trips so productive.


New to DarkOwl? Find as an upcoming event.

DarkOwl and Aftra Announce Strategic Partnership to Unite Darknet Intelligence with Attack Surface Management

September 16, 2026

Integration pairs DarkOwl’s DARKINT™, darknet intelligence dataset, with Aftra’s external attack surface management solution, giving security teams a single, actionable view of their organization’s risk and executives a simplified view of security risk and compliance.

DarkOwl, the industry leader in darknet intelligence, and Aftra’s attack surface management solution today announced a strategic partnership. With the partnership, DarkOwl’s darknet intelligence will be integrated directly into the Aftra solution, giving Aftra customers continuous visibility into darknet exposure alongside their external attack surface and employee exposure findings.

Aftra provides organizations the ability to see their company the way a hacker does, with continuous discovery of exposed assets, shadow IT, and employee risk across the internet and converting the findings into prioritized actions for security, IT, and leadership teams.

With DarkOwl’s DARKINT™ dataset now integrated as part of Afrtra’s attack surface and employee exposure management solution, clients can see where their exposure extends onto darknet marketplaces, criminal forums, and darknet-adjacent channels such as Telegram.

“Integrating DarkOwl directly into Aftra expands visibility for our customers where traditional defenses end. Pairing dark web intelligence with our attack surface management and employee exposure gives organizations a single, actionable view of their entire risk profile.” – shared Sindri Guðmundsson, CTO, Aftra

“Attack surface management tells an organization what’s exposed at the perimeter. Darknet intelligence tells them what’s already been compromised beyond it. By integrating DarkOwl’s data directly into Aftra, we’re closing that gap — giving security teams one place to see both where they’re vulnerable and where they’ve already been exposed.” —  Commented Mark Turnage, Co-founder and CEO, DarkOwl

The partnership reflects a broader shift in how security teams are asked to work: rather than triaging alerts from disconnected tools, organizations increasingly need a consolidated view that connects what is exposed with what has already been compromised.

About DarkOwl
DarkOwl is the industry’s leading provider of darknet data. We offer the world’s largest commercially available database of information collected from the darknet. Using machine learning and AI, as well as human analysts, we automatically, continuously, and anonymously collect and index darknet, deep web, and high-risk surface net data. Our platform collects and stores data in near real-time, allowing darknet sites that frequently change location and availability to be searched and monitored in a safe and secure manner without having to access the darknet itself. Customers are able to turn this data into a powerful tool to identify organizational risk and criminal and adversarial behavior. For more information, contact us.

About Aftra
Aftra is the only cybersecurity solution built to bridge the gap between executive strategy and technical execution. While providing the C-suite with high-level visibility and decision-ready insights, Aftra delivers a robust, automated platform that allows IT and Security teams to manage their daily workflows and remediate risks in real-time. We turn complex cyber data into a strategic asset, ensuring the entire organization stays secure, compliant, and aligned.
Learn more at aftra.io

Revolut Compromised

September 15, 2026

On Monday, 14 September 2026, the UK based financial institution Revolut confirmed they had disclosed sensitive customer information to an unauthorized third party. Quickly information and samples of this data began to circulate on the darkweb. In this blog we explore what happened.

Revolut is a British financial technology company and digital banking platform headquartered in London, England.

The company was founded in July 2015 by Nikolay (Nik) Storonsky and Vlad Yatsenko. They offer digital banking services, international money transfers, multi-currency accounts, budgeting tools, stock trading, and cryptocurrency exchange through a mobile app.

In the UK they operate as a fully licensed bank, authorized by the Prudential Regulation Authority and the Financial Conduct Authority, as well as across the European Economic Area, alongside partner-backed financial services globally.

Revolut has experienced exponential growth since its inception in 2015, transforming from a simple digital travel-card app into Europe’s largest digital bank.

Revolut confirmed it disclosed sensitive customer information to an unauthorized third party after receiving fraudulent requests sent from a legitimate government agency email domain.

The data exposed reportedly contained customer identity information, contact details, DOB (date of birth), addresses, email addresses and phone numbers. As well as images that are routinely used by organizations to prove KYC (Know Your Customer), which often include a selfie, identity documents and proof of date, as well as identity documents such as passports and driver’s licenses.

A Revolut spokesperson confirmed a “limited” number of customers were impacted and they had been contacted directly. Further reporting suggests approximately 700 customers were affected, with the highest profiles and affluent being targeted.

According to reporting from TechCrunch, who spoke with a Revolut representative, “Revolut recently identified a sophisticated external impersonation scam where an unauthorised third party utilised a legitimate government agency domain email to submit fraudulent requests for information.”

A cyber security researcher stated that they had been in touch with the Revolut hacker and they claimed they had also compromised multiple Italian law enforcement departments and that access is what they used to send data requests to Revolut.

Once the intrusion was announced, the Darkweb, and particularly Telegram, chatter began about who was responsible for this. Actors claiming responsibility began to emerge.

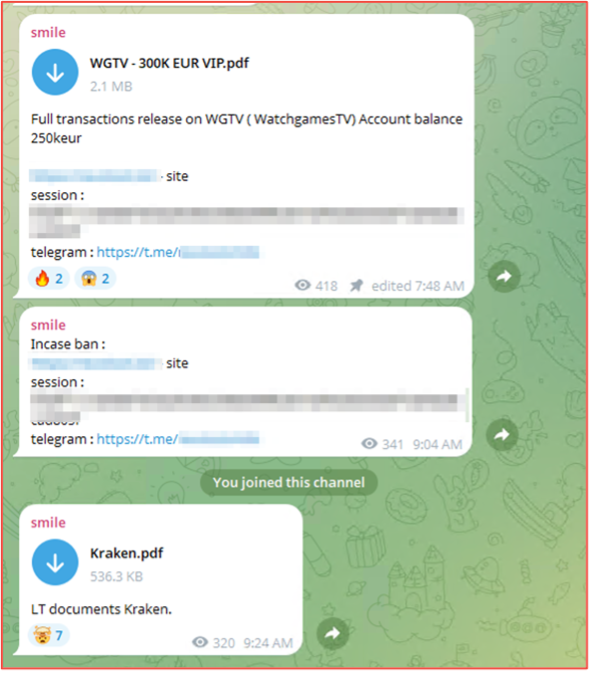
On 13 September a Telegram channel was created which claimed to share images and data linked to the breach of Revolut. The channel claimed to have data from Kraken and Poloniex as well as naming specific individuals and their personal information.

The channel went on to share downloads linked to the companies mentioned.

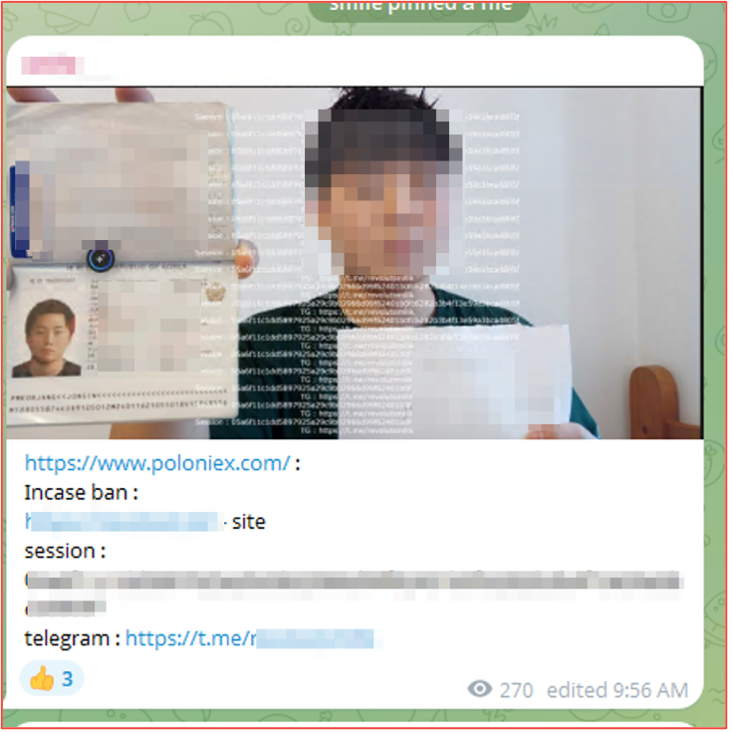
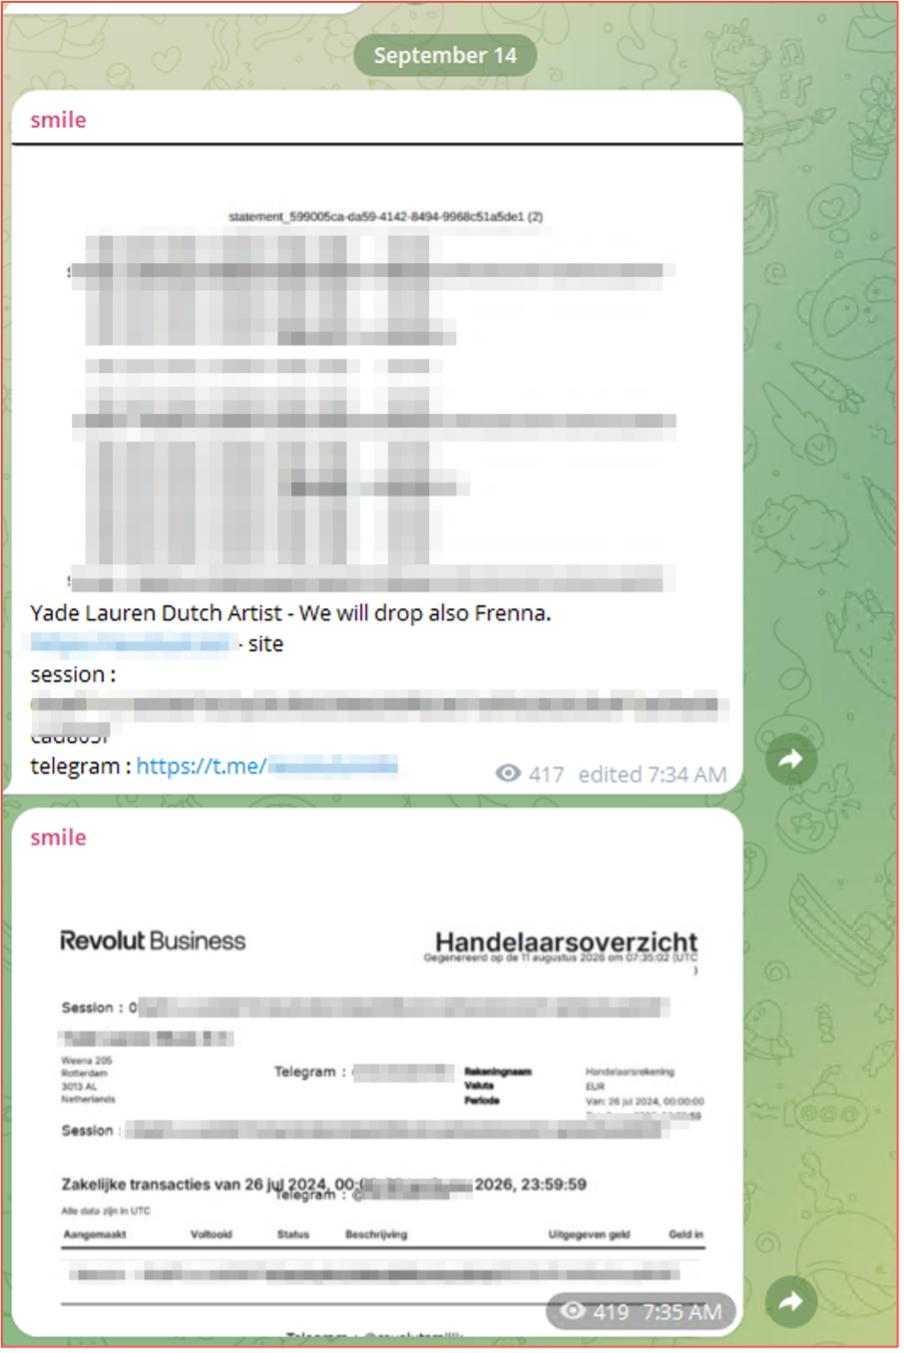
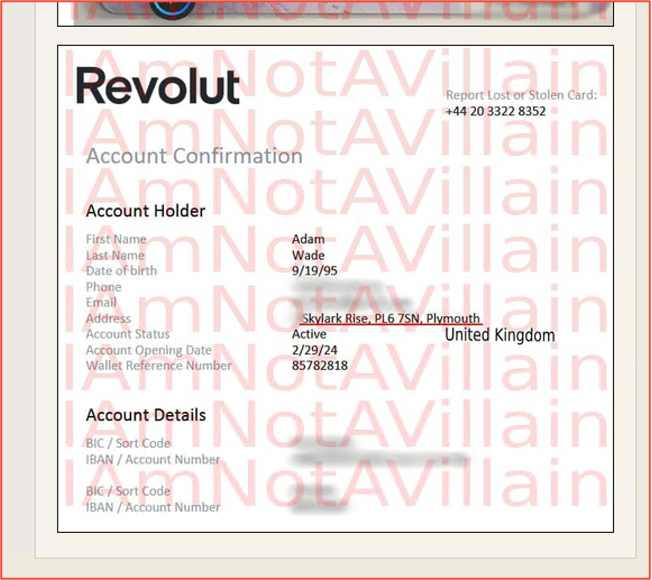
The channel also shared documents directly which appeared to be invoices or internal documents from Revolut. The actor watermarked the documents with their Session ID and Telegram account.

The account also shared further information in case the channel was banned by Telegram, this included details of their Session ID and their personal Telegram handle.

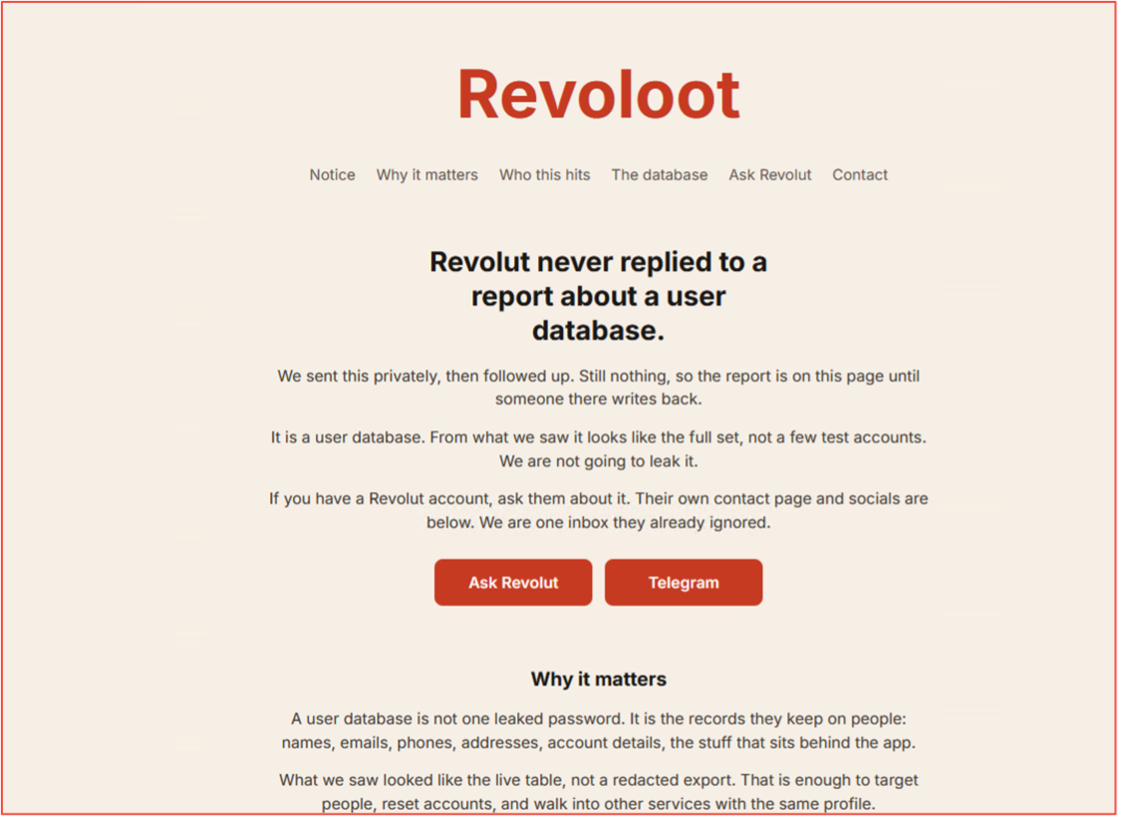
The website provided information about the hack and the reasons for leaking the information which was cited as the company closing accounts for no reason and freezing funds. The website was hosted on the clear web. By 15 September, it appeared to have been taken down. A message posted on the Telegram channel indicated that the threat actor may have deleted the page.

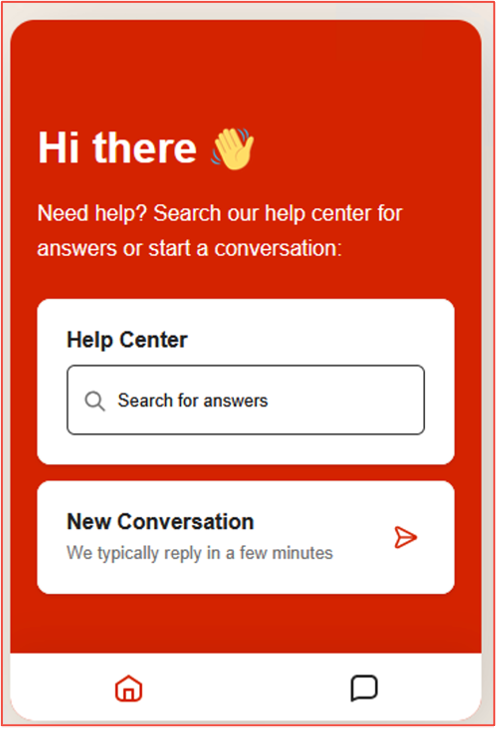
The site also included an AI chatbot which you could use to message the threat actor directly regarding the leak.

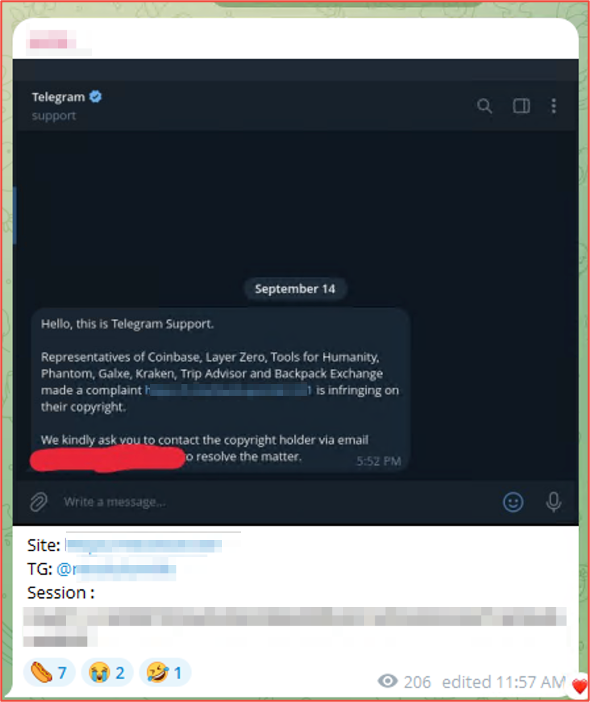
On September 14, the Telegram channel shared an image of a message from Telegram relating to one of the backup channels that has been created stating that several companies had made a complaint against the channel as it infringed on their copyright. The message stated the owner of the channel should contact the copyright holder direct to resolve the issue. The validity of this message has not been confirmed.

The actor posted on their Telegram channel that they were open to being interviewed by journalists free of charge.

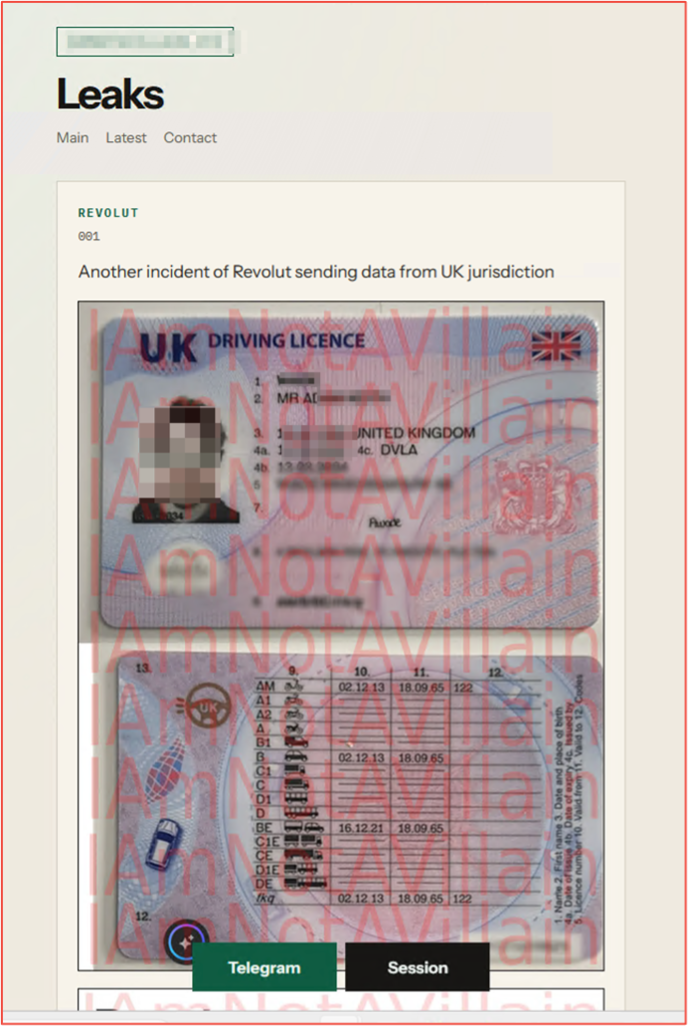
It was then identified that a second website had been created, as well as a new Telegram channel also claiming to be the threat actor behind the attack. This threat actor had been in contact with journalists. The handle used by this threat actor is IAmNotAVillain.

The website created used different colors to the previous website and a different name, however, does have similar sections explaining the leak. The session ID provided and the Telegram channel are also different from the first actor. This site claims an individual who was working with them, took a small sample of the data and is using that to claim they are behind the attack. They warn this is a scam.

On the site the actors began to release images to prove they had access to the data, showing KYC selfies and identity documents as well as account information including financial data.

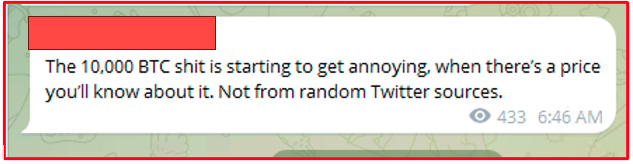
On the Telegram channel the group state that they have not yet announced a price they want for the data:

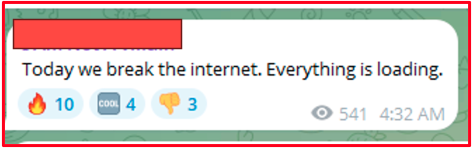
They also state more data is coming:

As well as sharing more samples through file sharing sites.

This is a developing incident. DarkOwl Analysts will continue to monitor.


Keep up with the latest. Follow us on LinkedIn.

The Warning Was Already Online: Iran-Linked Attacks on UK Power and US Water

September 9, 2026

A UK power plant offline for four days. Wastewater systems disrupted across a dozen US states. In back-to-back incidents this summer, Iran-linked hackers showed the world how quickly online rhetoric turns into physical disruption, and how thin the line has become between the operational technology that keeps the lights on and the industrial control systems that keep the water running. This wasn’t espionage. It was a demonstration.

In back-to-back incidents this summer (2026), Iran-linked hackers took down a small-scale power plant in the United Kingdom and disrupted wastewater treatment facilities across a dozen US states. The UK plant went offline for four days in July 2026 before staff were able to restore control; the facility’s identity has not been disclosed for security reasons, and the wider UK power supply was not affected. US officials say the attackers gained access to programmable logic controllers (PLCs) using simple techniques, not sophisticated tradecraft: scanning the internet for exposed devices and exploiting default credentials that were never changed.

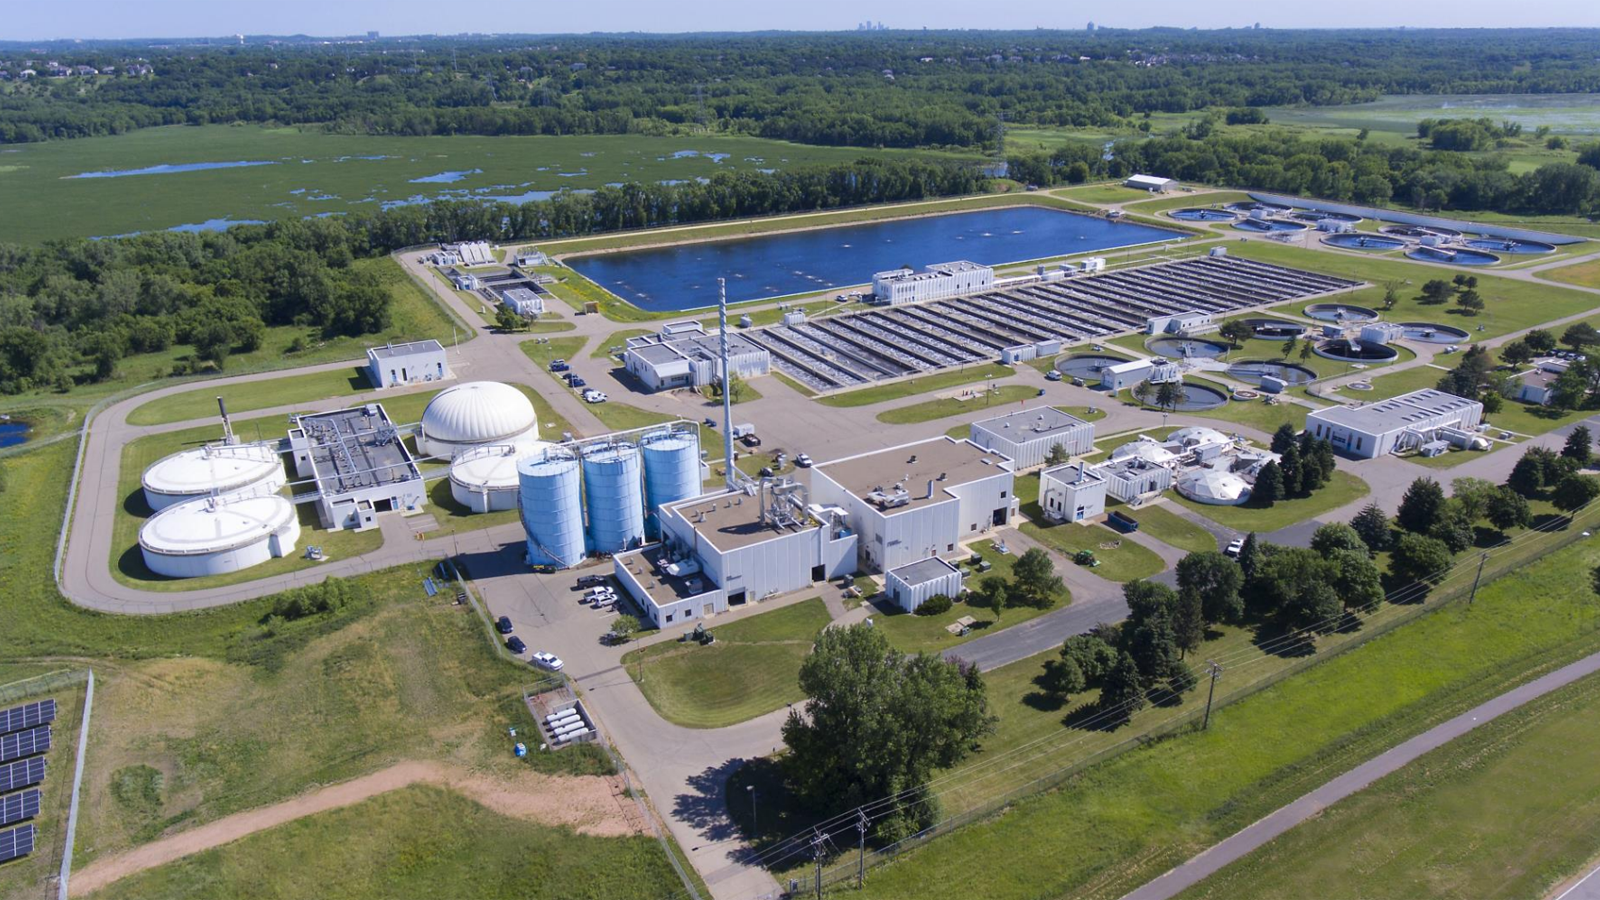
The same month, dozens of wastewater treatment plants across twelve US states, including New Jersey, Minnesota, Georgia, and South Dakota, were hit in a related wave of intrusions. The result was tangible and physical, loss of water pressure and flooding at multiple sites, not stolen files or encrypted servers. The FBI attributed the activity to malicious cyber actors, with US government sources pointing to Iran as the likely origin.

No group has formally claimed responsibility for either incident, but the pattern points to Iran-linked actors reported to be affiliated with CyberAv3ngers and the IRGC, a group with a documented history of targeting operational technology at Western utilities. The UK incident was reported to the National Cyber Security Centre (NCSC), which has neither confirmed nor denied it publicly. Security experts note that the low sophistication of the intrusion, default credentials and exposed devices rather than custom exploits, suggests these may be proof-of-concept attempts, cheap tests of what’s reachable before an actor commits to something more disruptive against higher-value targets.

Full attribution across both incidents took weeks. That lag matters. It is the gap between when an attack happens and when defenders can confidently say who did it and why, and it is exactly the window this piece is about.

This didn’t appear to be data theft or long-term espionage; it was a demonstration of capability against physical infrastructure, and it landed in two different countries within days of each other. Confirmed nation-state intrusions into Western OT (operational technology) and ICS (industrial control systems) environments, systems that control power generation and water treatment rather than the IT networks around them, remain rare. When they happen close together like this, they read less like coincidence and more like a signal being sent deliberately, to adversaries and to watching researchers alike.

That signal fits a broader pattern. Iran has increased cyberattacks against Western countries since February 2026, with operations reported across several European nations. Lowering the technical bar for this kind of attack, through more accessible tooling and, increasingly, AI-assisted reconnaissance, means capability demonstrations like this one are likely to keep showing up, and to keep showing up in places, power, water, and other critical infrastructure, that were largely theoretical targets until recently.

For critical infrastructure operators, the practical lesson isn’t really about PLC (programmological logic controller) hardening, though that matters too. It’s about timing. Dark web chatter, hacktivist forum activity, and posts on IRGC-linked channels are, more often than not, the earliest available signal that an operational hit is coming. In this case, formal attribution took weeks to occur. Organizations that were actively monitoring the actors’ own channels, forums, and known infrastructure had a real chance to see the groundwork being laid well before the FBI and NCSC put a name to it publicly.

That’s the gap dark web intelligence is built to close: not replacing incident response, but shrinking the distance between first chatter and first alert, so operators are acting on signal instead of waiting on confirmation.

Iranian linked groups continue to post threats. The below screenshot from 30 August 2026 shows a group named APT Iran threatening the US via it’s Telegram channel.

8/30/2026 1:09 PM] APT IRAN: 🔴 “Soon, the United States will witness unexpected and critical incidents in the energy, water, and telecommunications industries.”

[8/30/2026 1:17 PM] APT IRAN: 🔴 “We have previously warned that anyone who lays hands on this land and threatens our beloved Iran will pay for this mistake with their life. You did not heed our warnings, and we warned you again in Minnesota. You ignored us again — but this time, we will silence the American people.”

Treat proof-of-concept-style intrusions, ones that look unsophisticated or opportunistic, as leading indicators rather than curiosities; the actors testing default credentials today may be the ones causing real disruption tomorrow.

Audit internet-facing PLCs and ICS components for default or reused credentials and unnecessary exposure, since that was the entire entry point in the UK case.

Ensure you have continuous monitoring of darknet forums, hacktivist channels, and known IRGC-affiliated group activity, so that the weeks-long attribution lag seen in this case becomes a smaller window the next time around.

A UK power plant offline for four days. Wastewater systems disrupted across 12 US states. Iran-linked actors just showed how fast rhetoric turns into real-world disruption, and how much of that path is visible in advance to anyone watching the right corners of the dark web.


Make sure to read our latest report: Iran, Israel, and US Data Advertised Across Dark Web Forum

Threat Intelligence RoundUp: August

September 01, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. CISA: Medusa ransomware hit over 500 critical infrastructure orgs – Bleeping Computer

The Cybersecurity and Infrastructure Security Agency (CISA), in coordination with the Department of Health and Human Services (HHS) and the Federal Bureau of Investigation (FBI), announced Tuesday that the Medusa ransomware group has breached more than 500 critical infrastructure organizations in the United States since June 2021. As of April 2026, the victims span multiple sectors, including Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology, and Financial Services. Other affected organizations include those in the medical, education, legal, insurance, technology, and manufacturing industries. The updated figures represent an increase from a March 2025 joint advisory, which estimated that Medusa had impacted more than 300 critical infrastructure organizations.

The Medusa ransomware operation first emerged in January 2021, but its activity increased significantly in 2023 after the group launched the Medusa Blog leak site. The group began using stolen data as an additional form of leverage, threatening to publish sensitive information to pressure victims into paying ransoms. Medusa initially operated as a closed ransomware group but later evolved into a ransomware-as-a-service (RaaS) operation. Under this model, the group adopted an affiliate-based approach, allowing outside cybercriminals to carry out attacks using Medusa’s ransomware infrastructure. Read full article.

2. Sandworm hackers target IT pros with trojanized WireGuard VPN client – Bleeping Computer

Hackers linked to the Russian threat group Sandworm have been targeting IT professionals with fake job offers, according to the Ukrainian Computer Emergency Response Team (CERT-UA). The UAC-1045 campaign impersonated IT companies and recruiters, moving conversations to Telegram before sending victims fake technical assignments requiring access to a supposed corporate VPN. Attackers provided WireGuard configurations that triggered a fake error, then directed victims to download a modified client called “SopraVPN” from SourceForge. On Windows, the malware creates a scheduled task and downloads another payload; on Linux, it uses cURL to retrieve an executable from attacker-controlled infrastructure. Read More.

The North Carolina Ports Authority has confirmed that cyberattacks on three of its facilities disrupted IT systems and slowed operations. The attack was detected on August 4 and resulted in a system-wide outage, forcing gates at all three facilities to open at 8 a.m. on August 5 and causing delays for port operations and truckers. The affected facilities are the Port of Wilmington, Port of Morehead City, and Charlotte Inland Port, which together comprise the North Carolina Ports system’s two principal commercial deepwater seaports and an inland hub. The authority has not attributed the attack to a known threat actor and has not disclosed whether any sensitive data was compromised. Read more here.

Four cybercriminals have been arrested in Brazil, while three others have been charged in Europe over allegations that they exploited a vulnerability at a service provider to withdraw funds from Commerzbank customers’ accounts. The theft, investigated jointly by Brazilian and German federal police, took place over four days in November 2023 and resulted in losses of approximately €30 million. Commerzbank, one of Europe’s major financial institutions, generates more than €11.1 billion annual revenue. German authorities claim the hackers exploited a software vulnerability caused by a faulty update to the payment and transaction-processing system of a financial institution. The attackers used the vulnerability to initiate numerous unauthorized withdrawals from German online banking accounts. The stolen funds were then transferred to Brazil through an extensive network of accounts and transactions intended to obscure their origin. Authorities stated most of the money was withdrawn in Brazil, while smaller amounts were cashed out in four European countries. Read here.

5. ExfilSquad hackers leak info of over 100,000 UK police officers, staff – Bleeping Computer

On July 26, the U.K.’s Police National Legal Database (PNLD) was compromised, exposing the contact information of more than 100,000 police officers and criminal justice professionals. The data extortion group ExfilSquad claimed responsibility for the breach, having previously taken credit for the attack on Analog Devices. The incident is under investigation with support from cybersecurity experts and the National Crime Agency (NCA). At this time, investigators have found no evidence that passwords or other security credentials were compromised. Learn more.

6. Homeland Security Task Force (HSTF) investigation leads to dismantling of dark web drug trafficking organization – DOJ

A multinational law enforcement investigation has dismantled the “Undertaker45” dark web drug trafficking organization, which operated from 2017 to 2023. The group used several dark web marketplaces and encrypted messaging platforms to sell counterfeit OxyContin pills containing fentanyl and counterfeit Adderall pills containing methamphetamine. Led from Medellín, Colombia, the organization relied on U.S.-based members in Florida and North Carolina to receive and distribute the drugs across the country. The organization sold approximately 40 kilograms of methamphetamine and fentanyl pills and laundered about $2.5 million in proceeds, primarily through cryptocurrency. Read full article.

7. Hackers disrupt over 30 Minnesota water utilities in coordinated OT attack – Bleeping Computer

Minnesota IT Services (MNIT) activated its cybersecurity incident response capabilities following a targeted cyberattack affecting 30 community water service systems. The attack disrupted operational technology (OT), with multiple water treatment plants experiencing system outages for initially unknown reasons. Authorities later confirmed that “crews identified that the water plant outage was the result of a malicious cyberattack targeting computerized operating systems by unknown actors.”. In guidance published yesterday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) advised critical infrastructure organizations to isolate key OT systems where possible to help ensure the continuity of essential services in the event of a cyberattack. Read full article.

8. New AmnesiaStealer macOS malware hijacks browser sessions via remote control – Bleeping Computer

A new information-stealing malware, AmnesiaStealer, is targeting macOS users through ClickFix campaigns. The malware can copy Chromium browser profiles, including active authentication sessions, and load them into a hidden browser, potentially allowing attackers to access victims’ accounts without needing their passwords or MFA codes. It can also steal passwords, cryptocurrency wallets, Apple Notes and documents, Keychain data, and other sensitive information from 16 Chromium-based browsers. Current campaigns use fake GitHub download pages to trick victims into downloading a password-protected ZIP archive. AmnesiaStealer’s stream_module can clone profiles from seven Chromium-based browsers, including Chrome, Edge, Vivaldi, Arc, Opera, Brave, and Chromium. It launches the legitimate browser in hidden, headless mode with weakened security settings, then copies the victim’s profile and stores the stolen data. Learn more.

Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Copyright © 2026 DarkOwl, LLC All rights reserved.
Privacy Policy
DarkOwl is a Denver-based company that provides the world’s largest index of darknet content and the tools to efficiently find leaked or otherwise compromised sensitive data. We shorten the timeframe to detection of compromised data on the darknet, empowering organizations to swiftly detect security gaps and mitigate damage prior to misuse of their data.