The darknet has long been a place for criminal actors to operate with the hope of anonymity – they utilize forums to discuss nefarious and extremist activities, use marketplaces to buy and sell illicit goods, and more. In efforts to stop security researchers and law enforcement from accessing and scraping information from these sites threat actors are using increasingly sophisticated methods. In this blog, we explore some of the more complex CAPTCHAs we have seen threat actors using on darknet sites. Could you solve them?
What is a CAPTCHA?
A CAPTCHA is a type of challenge-response test used in computing to determine whether the user is human. This is done in order to deter Bots and Spam from accessing certain portions of online content. The acronym loosely comes from the phrase; “Completely Automated Public Turing test to tell Computers and Humans Apart.”
The tool was developed by two groups working in tandem in the late 90s and was put to the task of protecting sites soon after. The first form required a user to enter a sequence of letters and numbers in a distorted image. Since then, comparable tools like Cloudflare and others have been employed for similar reasons, and CAPTCHAs have continued to develop and become more complex. Google’s reCAPTCHA and the independent hCaptcha have emerged as the most commonly used tools to ensure that the person on the other end of the browser is human.
CAPTCHAs on the Darknet
The black markets and community platforms on the darknet have developed a lot of different versions of these CAPTCHAs, which are also sometimes known as “Turing Tests” and have become pretty ingenious with their various methods of preventing automated traffic on their sites.
Some of the puzzles are colorful, funny or intentionally misleading, and have definitively become a way that the various Markets and darknet operators express themselves; but not all are created equally. Some require logic, needing a human to parse out directions in the text, while others are simple. Typically, the more advanced the CAPTCHA, the more involved the other protocols of a darknet market or forum will be. Often times, they are also multi-layered, using the usual method of geometric or graphical interfaces to confuse a would-be bot attacker alongside text and other information that explains what to do. Over time, when the CAPTCHA fails to do its job, it is improved, upgraded and deployed to prevent their sites from getting crawled.
Of course, not all sites on the darknet are in English. There are many sites which represent countries across the globe, and many of the CAPTCHAS function in the native languages of the market. An emerging trend around the darknet are CAPTCHAS intentionally implemented in different languages so that the user must manually adjust to be able to access what’s on the other side.
Examples
In the following section, we explore some of the more interesting CAPTCHAs frequently found on the darknet.
The below image from the Russian market, OMG!OMG!, requires the user to input the characters shown in the box, in the traditional way that CAPTCHAs have operated. However, this site is Russian and it therefore requires you to input your response in the Cyrillic language. If the user is not a Russian native or resident, this will require them to change their keyboard settings or copy their input from a Cyrillic character tool.
The following CAPTCHA asks the “human” to pick the odd one out. It shows various images on a confusing background. In this case, the plant would be the odd one out as all the others are animals. This appeared on the site RuTOR.
The marketplace Kerberos requires you to complete two puzzles, one asks you to identify what is in the image from a selection of answers in a drop-down menu, to make this more difficult the pixels in the image constantly change. The other asks you to select the correct characters from a phrase, again using a drop-down menu. You have to complete this in a given amount of time otherwise the CAPTCHA will expire, and you will have to start over again.
The below CAPTCHA from the seized and now-defunct Kingdom Marketplace asks you to fill in the characters in the image, but it also highlights the characters that should appear in the URL to ensure that you are not on a scam site and that you are not being phished.
Another methodology that has been adopted by darknet operators is asking you to fill in the characters, but it will highlight which character to enter based on the box that you are filling in – meaning that the characters are not sequential as shown in the image below.
Another example is shown below where the circle will move to different characters as you enter in more. In some cases, you are able to correct your work, other times you have to reload the CAPTCHA, but these more interactive versions are fairly commonplace among the various dark web sites, many of which are tailored versions of each other.
The below image shows an example of a CAPTCHA that requires you to solve a math problem in order to be admitted into the site. More and more sites are using sometimes quite complex math problems to make it more difficult for bots to enter the site.
Others focus more on images. Asking you to identify which image is missing. In the below image, in order to enter the site you have to figure out which hieroglyph is missing.
Another, from AlphaBay, will test how good you are at telling the time, but complicates the task by adding shapes to the clock face that make it very difficult to see the accurate time. You are also only given 1 minute to complete the test before it will reset.
Conclusion
In this blog, we have shown you the wide range of CAPTCHAs that are used across darknet sites to protect them. CAPTCHAs are used to ensure that bots are not entering a site, usually for the purposes of crawling the site or to flood the site for malicious purposes or to ensure access, such as with ticket purchasing bots. They are widely utilized on the dark web to not only protect the sites from DDOS attacks (distributed denial-of-service attack) but also to protect the users and the information on those sites from security researchers and law enforcement. This can make it particularly difficult for some users to access the darknet.
The team at DarkOwl routinely deals with these CAPTCHAs and are able to access the dark web in order to assist those who seek to protect their information and bring an end to online criminal activity.
Learn more how DarkOwl’s expertise in the darknet can help your organization. Contact Us.
Now in its 16th year, FIC proudly asserts itself as the preeminent gathering in the realm of digital security and trust. Positioned as a cornerstone event in the European cybersecurity landscape, FIC distinguishes itself by fostering an inclusive environment that unites every facet of the cybersecurity ecosystem. From end consumers to service providers, law enforcement agencies to academic institutions and consultants, FIC’s scope encompasses them all.
With a dual mission, FIC addresses the operational hurdles of cybersecurity while also championing the development of a digital future aligned with European values and interests. This holistic approach ensures that attendees and sponsors gain comprehensive insights into the state of cybersecurity in Europe and have the opportunity to glean knowledge from industry luminaries.
At FIC, the over 20,000 attendees have unparalleled access to both end-users and providers of solutions and services, facilitating discussions on both tactical challenges and strategic imperatives in cybersecurity.
“Ready for AI?”
The theme of FIC 2023, was “Ready for AI?”. According to a recent report by Forbes, the artificial intelligence (AI) market is projected to reach $407 billion by 2027 and 64% of businesses expect AI to increase overall productivity.
To build relationships and trust, and share the value and essential need of darknet data for any cybersecurity posture, David Alley, CEO of DarkOwl FZE based in Dubai and Magnus Svärd, Director of Strategic Partnerships, based out of DarkOwl’s headquarters in Denver, CO, represented DarkOwl at FIC.
In addition to networking and conversations at the booth, top minds of the space have the platform to share thought leadership, innovations and the latest in the cyber security space. Speakers were present from all across Europe and the world: France, Switzerland, Luxembourg, Belgium, the United States, Netherlands, Germany, Spain, Canada, Singapore, Poland, Norway, Romania, Mexico, South Africa, China, Thailand, and more. Topics ranged from industrial infrastructure cybersecurity, quantum-resistant cryptography, identity security, international cybersecurity law, AI and counterterrorism, digital crime, social engineering, cybercrime trends, trust and safety in the cloud, and many more. Many of the presentations throughout the three days were not just thought leadership, but also practical presentations – showing the “how to.”
David and Magnus both expressed that they experienced “non-stop traffic” and kept busy on the show floor throughout the event meeting new prospects and showcasing our industry leading darknet platform, Vision UI, and meeting with several current clients and partners. With many current clients present, the DarkOwl team was able to spend time understanding how we can best optimize and elevate our current partnerships and how we can continue to provide the most value as their darknet data provider, focusing on continuing to build up our customer relationships and building trust. The DarkOwl team is confident there will be many follow ups and successful connections coming from our participation at FIC and looks forward attending The International Cybersecurity Forum in 2025.
As the tax deadline fast approaches, it is important for us all to be aware of the risks that are posed to us by cyber criminals at this time of year. Whether it be identity theft from tax forms, targeting of tax filing providers, or fraudulent returns, there are a number of ways that the tax system can be exploited for criminal financial gain.
As we do each year, DarkOwl analysts have reviewed the activity of cyber criminals on the dark web and dark web adjacent sites and messaging platforms to highlight some of the activities cyber criminals are participating in.
Selling Tax Refund Methodologies
Fraudsters on the dark web will sell step by step guides on how to conduct specific types of identity fraud. The below advertisement from Telegram is soliciting users to contact an individual to buy a tax refund methodology that allegedly bypasses the ID.ME facial recognition verification method that has recently been implemented by the IRS as a fraud prevention method.
DarkOwl analysts have also noted several instances where the technology vendor, ID.ME, has been targeted on stealer log marketplace websites like 2Easy or Russian Market, which may allow threat actors to access accounts of users for fraudulent purposes, as stealer logs usually contain usernames, passwords and session cookies.
Another Telegram post claims to provide buyers with a guide to obtain a Federal Tax refund claiming to offer advice on what bank account you should cash out to and what method to use. They claim that a refund will be guaranteed.
Phishing Templates
ID.ME is commonly targeted across the darknet. DarkOwl analysts have observed fraudsters selling phishing admin panels for sites like ID.ME, PayPal, and USPS on Telegram as well, meaning that they are able to collect the data of unsuspecting victims who believe they are adding their credentials to a legitimate site. Access to these accounts could mean that a threat actor is able to steal someone’s identity whether that be for tax fraud or other types of financial fraud.
Selling Tax Forms
DarkOwl analysts identified threat actors on the popular carding forum 2crd and found an actor advertising counterfeit identification documents, and also included tax return information and common tax forms which could be used to impersonate an individual. It is unclear if these documents are fraudulent in nature or had been stolen from a legitimate owner.
Similar postings were found on another site, ProCRD, offering W2 forms with a 1040 and full info. These documents are being sold for as little as $10. These appear to be sold as part of Fullz, which is a term used by dark web actors to indicate they have the full information for an individual – this usually includes financial information and identity details to be used to conduct identity fraud or financial crime.
A post on a Telegram channel claimed to have W2 forms, tax returns, and pay stubs for sale as well as credit card numbers, Social Security numbers and other sensitive personal information used to conduct fraud. DarkOwl analysts note this advertisement relates to an automated Telegram bot where one can purchase these illicit items. Telegram bots are an effective way to sell illicit items on Telegram because it maintains a certain level of anonymity between the seller and end user.
Another Telegram advertisement was identified which sells similar products, but notes all of the sensitive documents being sold are from other countries like the UAE and European countries. This highlights that it is not just the US that is subject to this type of fraud.
A third similar example from Telegram is shown below. It is important to note, as shown in all of these examples that tax forms are typically sold with other identity fraud products like fullz, credit card numbers, etc. This allows the fraudsters to be more convincing in their fraudulent activities as they have more information which makes them appear legitimate.
The tax fraud community is considerable on Telegram, a search across DarkOwl’s dark web collection for the mention of “tax refund” on Telegram resulted in nearly 100,000 hits. However, Telegram fraudsters will typically also advertise across the darknet and deep web from sites like Royal or Russian Market to ProCRD or WWH Club – often moving to private messaging on Telegram for security.
Telegram is a major medium/vehicle for all types of identity fraud in 2024 because the platform allows for increased security, anonymity (between sellers and end users), as well as more efficient transactions through automated chat bots, rather than processing transactions directly on a .onion site. DarkOwl analysts therefore identify a large amount of this activity on Telegram but cross over from other dark web sites highlighting that similar communities are active on both.
Tax Filing Providers
Many individuals will use services in order to file their taxes, as it often removes some of the stress associated with tax season, and hopefully ensures that you maximize your return. However, these organizations are also targeted at this time of year.
A review of Stealer Logs collected by DarkOwl highlighted several instances in the last several months where credentials for these organizations were stolen. Allowing actors to access sensitive information and conduct fraudulent filings.
There are also Telegram channels which offer buyers the chance to obtain tax refunds through TurboTax.
Ransomware
Ransomware attacks continue to be prevalent in 2024, with many companies subject to attack, one group PLAY, like many other groups, post their victims details on their leak site as well as details about what information they have relating to them.
In almost all of the posts relating to their victims the group claim to have information relating to taxes, likely both the company taxes as well as employees’ details. Some of them also claim to have evidence of tax evasion.
If/when these details are released by the ransomware group that information can be used by other threat actors to conduct other types of fraud.
Conclusion
Tax season is just another thing that can be used by threat actors to commit fraud against individuals and companies. However, financial fraud can be committed at any time of the year and it is important to protect your personal information by practicing good cyber hygiene, do not reuse passwords, and be vigilant to phishing and malvertising campaigns.
Read on for highlights from DarkOwl’s Product Team for Q1, including new exciting product features. The team is starting the new year off strong and looks forward to an exciting 2024!
Enhanced Forum Structuring
The team made upgrades to forum structuring within the platform, empowering users with unparalleled insights into darknet forums. This latest development enables users to navigate darknet conversations in a structured manner, presenting discussions in chronological order for accurate and effortless reconstruction. The upgraded search capabilities further empower users to pinpoint relevant information swiftly, facilitating comprehensive analysis.
Access to forum data in a structured format is particularly crucial for organizations seeking to bolster their cybersecurity defenses and proactively address emerging threats.
Figures 1 and 2 (left to right): Previous view of a thread versus new enhanced view
Last month, the DarkOwl Marketing team sat down with DarkOwl’s Director of Client Engagement, Caryn Farino and Product Manager, Josh Berman to learn more. You can read that interview here.
Access the Darknet Safely and Securely Directly from DarkOwl Vision
This quarter the team released “Direct to Darknet” within Vision UI in partnership with Authentic8, a leading provider of cloud-based secure browsing solutions. This feature allows users to further investigate Vision UI search results on forums, marketplaces, and other Onion sites. This can be helpful for an investigation to view the original website, view images or advertisements that may be on the sites, take a screenshot for reporting, and more. By combining DarkOwl’s comprehensive darknet database and monitoring capabilities with Authentic8’s Silo cloud browser, which is known for its secure browsing environment, organizations will gain unprecedented visibility and protection against cyber threats surfacing on the darknet.
Figures 3 and 4 (left to right): Vision UI result and associated darknet result for guns in Miami
Context and Enrichments
The team has significantly increased context information for leaks, actors, ransomware, and has added features to make doing research easier than ever.
On the new Leak Explorepage, customers can see information about our leak dataset and get information about an individual leak. Customers can look for a leak that we have in our system, see if it’s relevant to them, pivot to the filetree or original posting, and look at the underlying data. We highlight some of leaks we collected this quarter in the next section – all of the information highlighted below is taken directly from this feature.
Tox ID search and Compare features (Tools/CVEs) have been added to Actor Explore profiles. The compare feature on the Tools and CVEs page allows users to see commonalities between actor groups, including timelines and any commonalities between actor groups.
Site Context on Ransomware search results provide site names, relevant dates, cipher information, and pivoting options to Actor Explore or further research, all provided by the DarkOwl analyst team.
The DarkOwl analyst team has added several new Search Blocktranslations in Arabic, Russian, and Chinese languages.
More Vision UI Updates
Multi-Factor Authentication login option for customers
Alert section enhancements to delete single alerts and display Category in the main table. This makes alerts easier to use and more functional. “Category” has been added as a new column on the Alerts page to more effectively use these tags to organize alerts. One way to use these tags is to classify alerts by organization or category such as “Credentials,” to view related alerts from multiple monitors together.
Collection Stats
This quarter showed tremendous growth in data collection. The team had 5% growth quarter over quarter in added Tor documents, 27% growth in I2P documents, 31% growth in ZeroNet documents, 15% growth in records from Telegram, to highlight a few.
Highlights
Chat platform collection continues to grow as darknet threat actors migrate to darknet adjacent sites. Currently, the platform has coverage of more than 22,000 channels across multiple chat platforms.
The team added 117 data leaks this quarter alone, many of which were requests from customers, which the team always prioritizes. A select few of those are highlighted in the next section – all gathered from the DarkOwl analyst team.
Actor Explore continues to grow – with a total of 307 actor profiles able to searched, compared, and researched within the platform.
Leaks of Interest Collected
As mentioned, the descriptions below are all available in our Leak Context product feature.
Naz.api
The naz.api leak was made available on BreachForums, on January 15, 2024. According to the post, it is a 35 GB collection of public URLs, usernames and passwords. The post also notes that it was originally on xkey.info but was taken down for allegedly not being the real naz.api leak. naz.api is one of the largest credential stuffing lists originally posted in September 9, 2023 by 0x64. According to that post, the database was created by extracting data from stealer logs, and contains over 1 billion unique records of saved logins and passwords in users’ browsers. The post also notes that the original naz.api dataset was donated to 0t.rocks. Infostealer logs are files produced when a trojan is installed on a system that collects information from the infected system. Depending on the infostealer malware, the extracted data can include system information and browser session data (including autofills, credentials, financial information, cookies, browser history, etc.). Some malware will also capture stored local files and install keylogging on the system to exfiltrate data outside of the browser sessions.
USA 500K SSN
Data purported to be of US Social Security numbers was posted on LeakBase, a hacking forum, on September 11, 2023. Data exposed includes full names, dates of birth, social security numbers, and physical addresses. Analyst Note: Three leaks with “500K SSN” included in the leak name were identified during a recent review, with each leak containing the same data format. These leaks may have been parsed from a larger historical leak and reposted in several parts. For this data leak, DarkOwl noted references to the same sample data dating back to December 2021, supporting this leak contains older content. Notwithstanding, given the presence of social security numbers, the recirculation of this data is of concern.
DC Health Link
Data purported to be from DC Health Link was posted on BreachForums, a hacking forum, on July 22, 2023. According to the post, this breach occurred in March 2023. Data exposed includes member names and IDs, policy information, social security numbers, full names, dates of birth, e-mail addresses, phone numbers, physical addresses, employment information, genders, medical records, and other personal identifiers such as ethnicity and citizenship status. Analyst Note: Review of the original post on Breach Forums on March 9, 2023, indicates the original leaker was thekilob. This is further supported by commentary in the Telegram Channel, BreachForums Chat, where they indicate thekilob was removed as a reference from the original post. Analyst Note 2: DC Health Link made a public statement about the breach on their website on March 14, 2023, detailing information about the breach.
AT&T
Data purported to be from AT&T was posted on BreachForums, a hacking forum, on March 17, 2024. According to the post, AT&T’s database was hacked by ShinyHunters in 2021 and contains 70 million lines. Data exposed includes names, e-mail addresses, phone numbers, physical addresses, social security numbers, and dates of birth. Analyst Note: According to the information provided in the post, in order to link the SSN and DOB for each record, one will need to grep and replace the encrypted values for these fields in the master file with unencrypted value of these fields provided in a separate file. Analyst Note 2: DarkOwl notes to replicate this connection in the raw indexed files, a search will need to be run using the encrypted value in quotes as the keyword to locate both documents in the leak (i.e. “1lpxFgIp7MlY” would result in both the document that contains the full record with the SSN encrypted value and the file which contains the decrypted SSN value). Analyst Note 3: A high level review of the data indicates the data is from customers in the United States. Analyst Note 4: Research in DarkOwl Vision indicates the data was initially posted for auction on August 22, 2021, for $80,000.
Curious how these features can make your job easier? Get in touch!
A new Middle East conflict emerged on October 7, 2023, when Hamas launched an attack on Israel. It rages on to the present day, resulting in physical, digital, and hybrid events that threaten both Israel and Palestine and their borders with multiple surrounding countries. Regional stability is extremely low as actors supporting all sides of the conflict take stances and attack their self-defined opponents on the ground, at sea, and with cyber capabilities. Most recently, Hamas rejected an Israeli offer for a ceasefire on 25 March 2024, ensuring that this conflict continues for an undetermined amount of time.
In the past six months, some of the trending issues the world has witnessed include drastic upticks in maritime and ground-centered activity against Iranian-supported actors, such as the Houthis and Hezbollah. Air attacks and maritime incidents against the Houthis continue all over the Middle East region, impacting civilian vessels in various bodies of water and civilian shipping routes. Telegram remains a vital part of the conflict, with propaganda emerging from Iranian, Arabic, and Israeli Telegram channels, as well as sympathizers and opponents from all sides of the conflict taking a public stance and offering to attack on behalf of their beliefs. A sampling of these activities over the past six months since the start of the conflict is covered in this blog.
Telegram and Choosing Sides
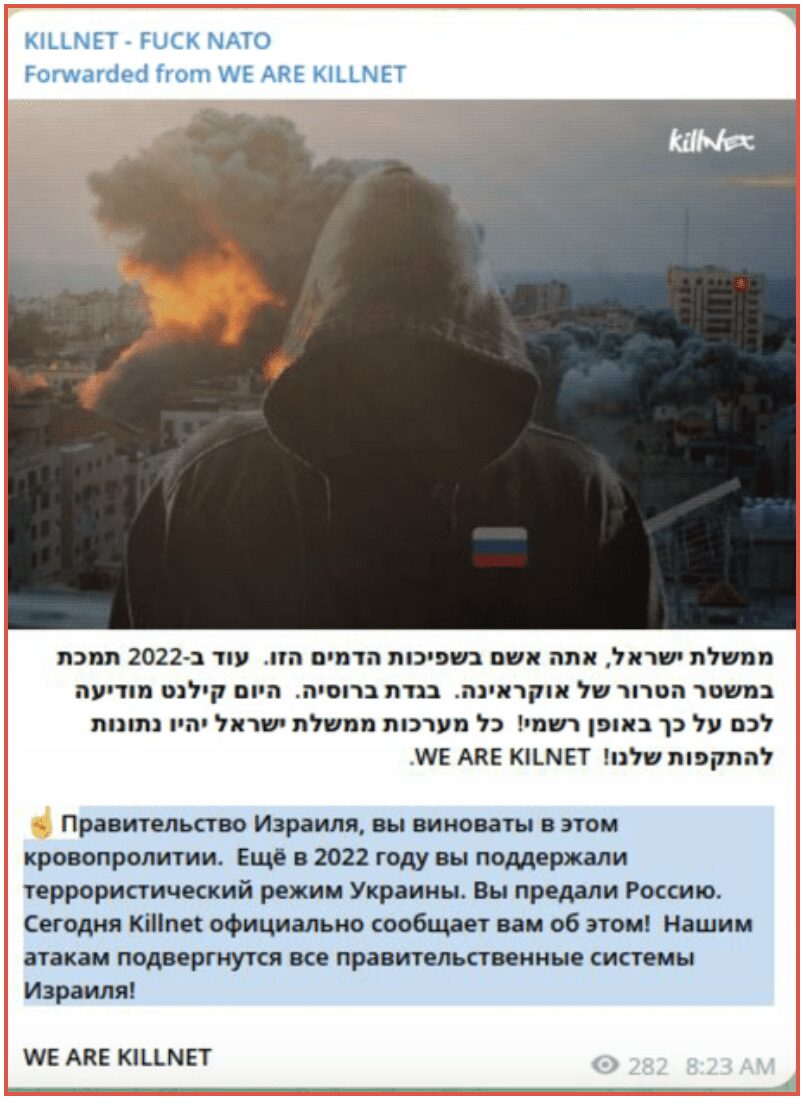
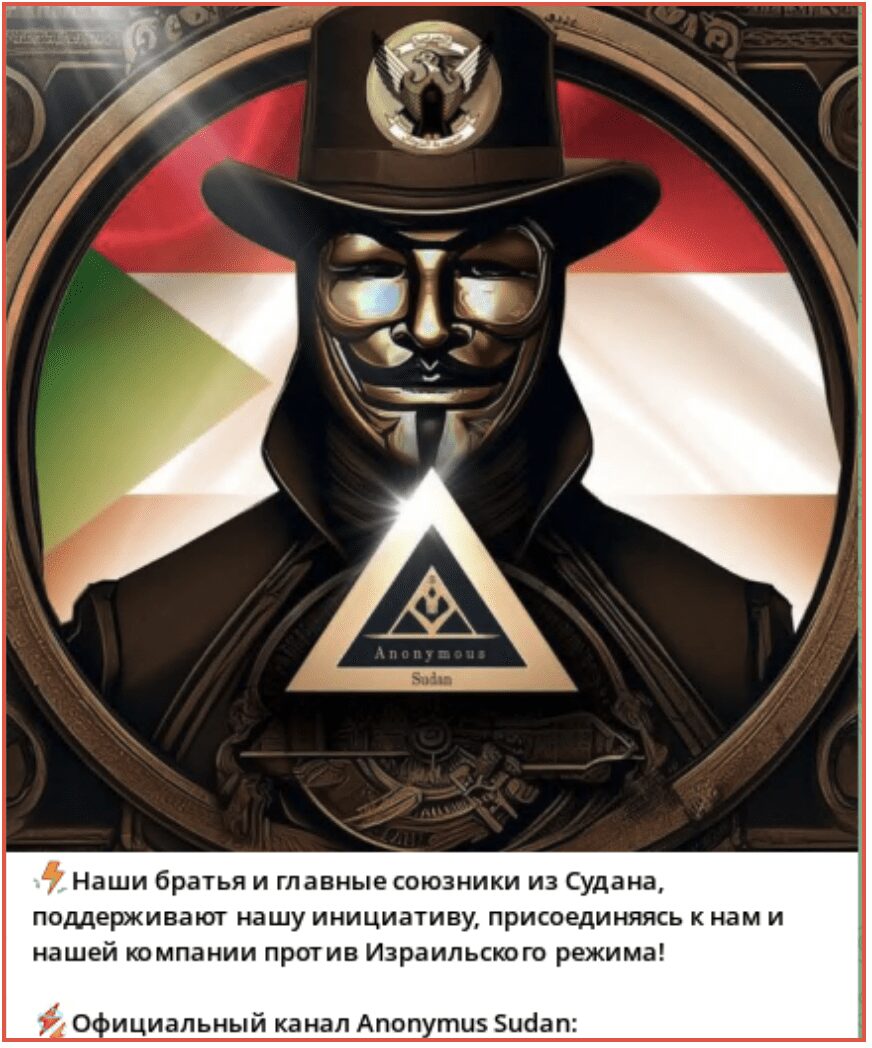
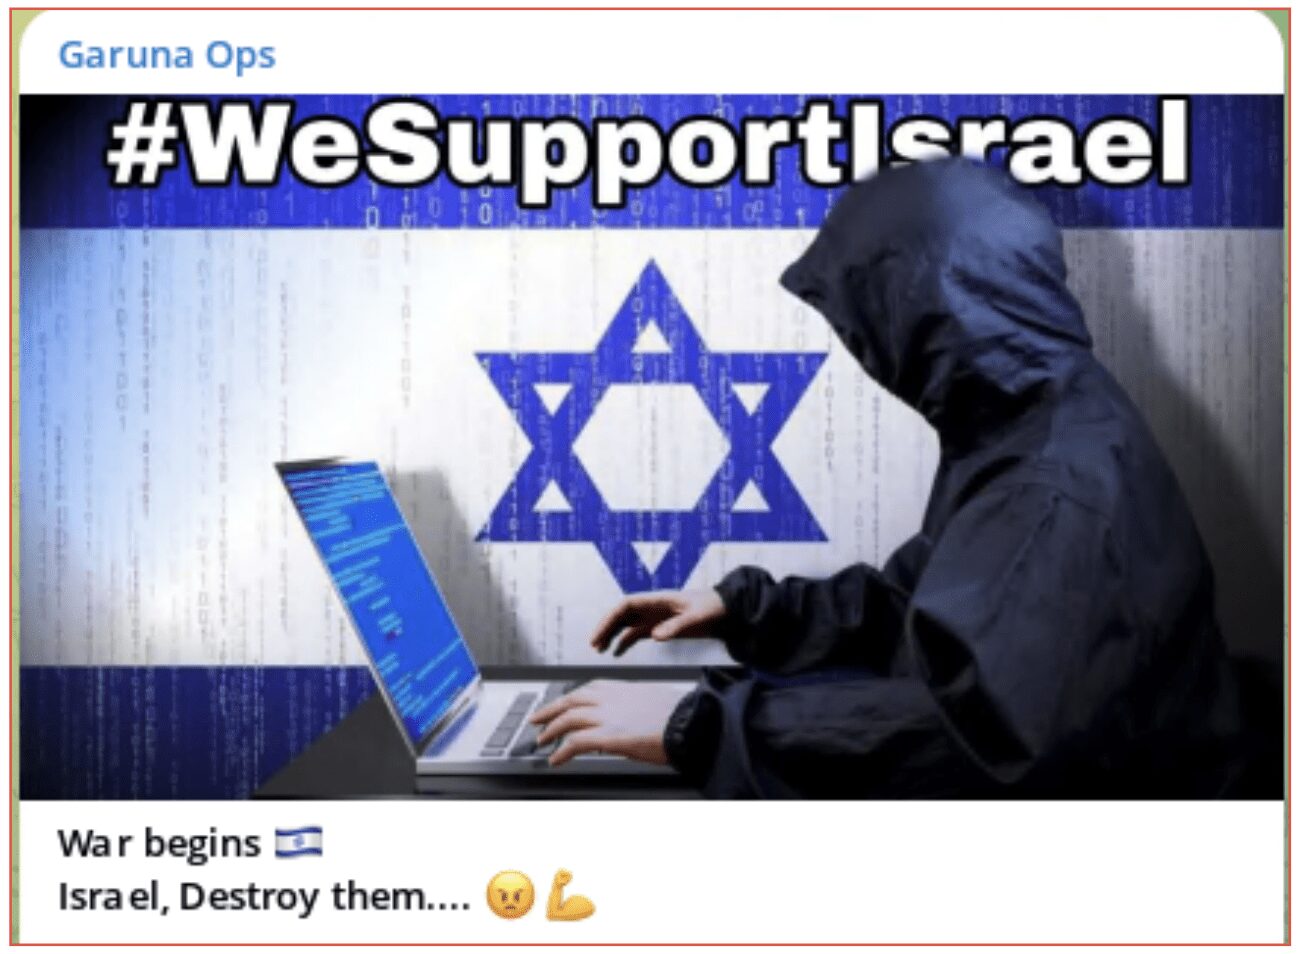
As was previously mentioned and covered extensively in a previous blog, a trend that emerged almost immediately and continues six months later to today, was actors choosing sides in the conflict. No matter what side is supported, whether an entity is pro-Israel or pro-Hamas, supporters publicly emerge and then are targeted by opponents.
Figure 1: Killnet posting their intention to target the Israeli government on Telegram
Figure 2: Anonymous Sudan posting their intention to target the Israeli government on Telegram
Figure 3: The group Garuna Ops made a number of posts on Telegram in support of Israel and stated as well as attacking Palestine they would attack any other countries that supported them
The end of 2023 witnessed a few key events, ensuring the conflict would continue into the new year of 2024. The list below is not exhaustive, and is only meant to provide high-level examples:
Navitas Petroleum, based in Israel, was purportedly hit by BlackBasta ransomware (December, 2023)
However, as of the time of this writing, Navitas had no entry on the BlackBasta ransomware victim blog. It is possible this event was fabricated, or that the impacted entity struck a deal of some kind with the BlackBasta actors to have their data removed from the ransomware website. Either way, the threat of malicious actors coming after an organization because of their country or other allegiance is a continuing trend.
Predatory Sparrow hacking group attacked 70% of Iranian gas stations (December, 2023):
Figure 4: Predatory Sparrow group publicizes their attack of Iranian fuel stations in December, 2023; Source: DarkOwl Vision
Iran issued a statement that the October 07 attack against Israel was in retaliation for the January 2020 assassination of IRGC commander Qassem Soleimani (December, 2023)
Hamas leaders publicly rejected this claim.
In 2024, some incidents included (the list below is not exhaustive, and is only meant to provide high-level examples):
Anonymous Sudan claims to have hit Israel’s telecom company Pelephone (January, 2024):
Figure 5: Anonymous Sudan uses their Telegram channel to advertise the January 2024 attack against Israeli Telecom Pelephone; Source: DarkOwl Vision
Lulzsec group targeted Israeli red-rocket alert system:
Figure 6: Lulzsec hacking group advertises their mid-January 2024 efforts against the Israeli rocket alert system on Telegram
Anonymous Sudan claims to have hit Israel’s Bazan group:
Figure 7: Hacking collective Anonymous Sudan uses their Telegram channel to publicize an attack on Israeli Bazan Group in January, 2024; Source: DarkOwl Vision
Anonymous Sudan also claimed it conducted a cyberattack targeting “critical parts” of healthcare infrastructure in Israel, and adds “more than a thousand devices are completely disconnected.”
Terminator Security hacking group claims to have taken down Israeli Air Force servers.
As of mid-March 2024, Raytheon was again targeted, this time by the Anonymous group due to their supplying weapons to Israel. However, Raytheon and other US defense contractors are frequently targeted by Russian groups, such as this Snatch Ransomware group observation which also came in March 2024:
Figure 8: Snatch ransomware group details attacks against US government contractor Raytheon, which is frequently targeted due to its weapons supplied to Ukraine; Source: DarkOwl Vision
Maritime Activity
Underwater mining conducted by the Houthis and other attacks against maritime vessels continued as recently as mid-March, with this physical element of conflict having cyber implications:
Underwater sea telecom cables that transit approximately 17% of international data were damaged as maritime conflict continued in the Red Sea. Some media outlets blamed Houthi militants, while other experts state the cables were damaged by ships sinking and hitting them, as they are in shallow waters.
Maritime activity in the Red Sea also involved the United States conducting a cyberattack on an Iranian ship that had been gathering intelligence on cargo vessels in the region. This was intended to prevent the ship from sharing intelligence with Houthi members in Yemen, who have been frequently targeting civilian vessels. DarkOwl analysts have observed multiple platforms, including Discord, onion websites, and 8kun, sharing information regarding the hostile situation in the Red Sea:
Figure 9: Users discuss and share videos of Iranian activity in the Red Sea between January to March 2024; Source: DarkOwl Vision
Figure 10: Users discuss and share videos of Iranian activity in the Red Sea between January to March 2024; Source: DarkOwl Vision
Figure 11: Users discuss and share videos of Iranian activity in the Red Sea between January to March 2024; Source: DarkOwl Vision
Hybrid Incidents
Hybrid events, comprised of both digital and physical efforts to have a real-world impact, have also grown. In mid-February 2024, international media reported on an attempt to reroute an Israeli El Al airliner. The original flight path was from Bangkok, Thailand, and Tel Aviv, Israel. However, during the flight, the crew were provided with instructions that derailed them from their set route. These instructions were discarded, and the crew remained on their original flight path, once they contacted other air traffic controllers and compared flight data, and realized actors were trying to intentionally mislead them.
The incident occurred over Somali airspace, and Israeli sources revealed a certain frequency that was consistently trying to change flight paths, indicating a constant attempt to disrupt air activity. Using technology to attempt to derail a plane or any other means of transportation that carries humans who could be used as leverage in a geopolitical situation, or harmed, brings a new level of urgency towards vetting online information tied to any world event, especially a conflict.
Conclusion
As is confirmed by the events above, conflict these days has a new paradigm using technology to influence and increase physical air, ground, and maritime events, such as using a certain frequency to communicate with planes while trying to pull them from a planned, safe route. Global infrastructure such as underwater cables are either accidentally damaged by water mining or intentionally cut, in some cases, to interfere with regional internet access and connectivity. These physical threats to infrastructure and personnel are separate to the propaganda that is quickly spun and shared among all sides via messaging platforms and social media.
Malicious actors use technology to go after petroleum and water supplies, or even put services for human life, such as healthcare, at risk during geopolitical incidents. Even weapons supplies are in danger, as actors try to prevent weapons delivery or jeopardize the providers of the weapons. The technological component to conflict is here to stay, and actors will undoubtedly use any platform they feel is safe – Telegram, social media, or private messaging, or an online collection of supporters who can contribute to research, and disseminating propaganda to try and influence the public to see issues from a certain perspective.
Authentic8, a leading provider of cloud-based secure browsing solutions, and DarkOwl, the leader in darknet data, are proud to announce an innovative partnership that revolutionizes cybersecurity capabilities for organizations globally. This partnership showcases the power of product integration, leveraging DarkOwl’s unparalleled darknet intelligence alongside Authentic8’s secure browsing technology, Silo, to set new standards in threat detection and mitigation.
This partnership brings together the advanced technologies and expertise of both Authentic8 and DarkOwl to address the escalating challenges posed by cyber threats. By combining DarkOwl’s comprehensive darknet database and monitoring capabilities with Authentic8’s Silo cloud browser, which is known for its secure browsing environment, organizations will gain unprecedented visibility and protection against cyber threats surfacing on the darknet.
With this partnership, DarkOwl’s platform serves as the launch point for identifying darknet content and initiating investigations. Once identified, Silo enables full-page analysis for deeper research, providing full isolation from darknet cyber threats and anonymity from malicious actors. This capability enables organizations and government agencies to leverage DarkOwl’s data and Authentic8’s platform to uncover and investigate various threats, including cybercrime, ransomware, malware and other threats arising from the darknet.
“We are excited to partner with Authentic8 to empower organizations to stay ahead of evolving cyber threats,” said Mark Turnage, CEO of DarkOwl. “By combining our unmatched darknet intelligence capabilities with Authentic8’s secure browsing technology, we are enabling organizations to strengthen their defenses and safeguard their digital assets against sophisticated cyber adversaries.”
Ramesh Rajagopal, CEO of Authentic8 adds, “Investigative work in the Silo browser complements DarkOwl’s innovative intelligence solutions, enabling investigators to secure and streamline their dark web intelligence activities across both solutions.”
Together, Authentic8 and DarkOwl demonstrate their shared commitment to driving innovation and excellence in cybersecurity with this partnership. With this, they lead the industry in delivering cutting-edge solutions that address the evolving challenges in the cybersecurity space.
About Authentic8 Authentic8 are the creators of Silo for Research, a purpose-built solution for safely conducting open-source research on the surface, deep or dark web. The cloud-based, isolated browsing environment offers one-click access to Tor and in-region points of presence around the world. To learn more, visit www.authentic8.com.
About DarkOwl DarkOwl uses machine learning and human analysts to collect automatically, continuously, and anonymously, index and rank darknet, deep web, and high-risk surface net data that allows for simplicity in searching. DarkOwl is unique not only in the depth and breadth of its darknet data, but also in the relevance and searchability of its data, its investigation tools, and its passionate customer service. DarkOwl data is ethically and safely collected from the darknet, allowing users secure and anonymous access to information and threats relevant to their mission. For more information, visit www.darkowl.com.
DarkOwl LLC announced today that it has purchased certain assets of Skurio Ltd from the Administrators Keenan CF Ltd, effective March 22, 2024. These assets include certain customer information, source code, and other commercial material.
Mark Turnage, DarkOwl CEO commented that “the purchase of these Skurio assets will enhance DarkOwl’s market presence in the UK and Europe, and add optional new features to the DarkOwl product platform. Supplementing DarkOwl’s unique darknet capabilities with these Skurio improvements will enhance the depth and breadth of our market positioning.”
About DarkOwl DarkOwl uses machine learning and human analysts to collect automatically, continuously, and anonymously index and rank darknet, deep web, and high-risk surface net data. This allows for comprehensive searching, monitoring and alerting of these sites, as well as layering analytical tools on the data for pattern mapping. DarkOwl is unique not only in the depth and breadth of its darknet data, but also in the relevance and searchability of its data, its investigation tools, and its passionate customer service. DarkOwl data is ethically and safely collected from the darknet, allowing users secure and anonymous access to information and threats relevant to their mission. For more information, visit www.darkowl.com.
Disclaimer: This blog seeks to illuminate the practices used by threat actors that involve the nefarious application of artificial intelligence (AI) technologies. While the instances discussed herein do not imply that chatbots and similar tools are intrinsically hazardous, they serve to demonstrate the potential for their misuse by cybercriminals. None of the examples generated should be used.
Introduction
Cyberattacks are becoming more and more commonplace, with no one immune from attacks, whether it be corporations suffering from ransomware attacks or individuals falling victim to romance scams. But as people become more educated about the risks of cyberattacks and scams, cyber attackers must change their methods to ensure success.
Last April Fool’s Day, we looked how cyber actors trick us with phishing emails. This April Fool’s Day, we explore some of the ways that cyber actors could use new technology such as AI to fool their victims into allowing them access to their systems or finances.
Phishing
A phishing email is a deceptive email designed to trick the recipient into believing it’s from a trustworthy source, with the aim of stealing sensitive information, such as login credentials, financial details, or personal data. These emails often mimic the appearance and tone of official communications from well-known companies, banks, or government agencies. The emails will often request personal information, include suspicious links or attachments and generic information.
Most people these days are aware that they should not click on links in emails from people they don’t recognize and emails that appear to have spelling or grammar mistakes in them. But phishing emails are becoming more sophisticated, and AI can be used to generate emails that are more believable.
We asked an AI platform to write us an email:
This is the response we got:
This took seconds to generate and could be used to fool people.
Smishing
Smishing is a type of phishing scam conducted through SMS (Short Message Service) text messages. It involves sending deceptive text messages that aim to trick recipients into revealing personal information, clicking on malicious links, or performing actions that compromise their security. These messages often impersonate legitimate companies, organizations, or even acquaintances, creating a sense of urgency or fear to prompt immediate action from the victim.
Smishing campaigns are often used by threat actors to entice people as part of a romance scam or pretending to be customer support asking a user to share a password or click on a push notification. They can take many forms pretending to reward you with a prize or tell you that you missed a package delivery. They are becoming increasingly sophisticated and take many forms. Below we show a sample of these.
Social Engineering
Social engineering is a manipulation technique that exploits people to gain unauthorized access to information, systems, or buildings. Unlike traditional hacking, which often relies on technical vulnerabilities, social engineering targets the human element of security systems. The goal is to trick or deceive people into doing what the attacker wants them to do, whether that be access to systems or obtaining financial reward.
Social engineering can take many forms, from generating a phishing email based on specific information found on social media to make it more targeted to the victim to creating fake social media profiles to target individuals whether on a dating app or networking app to entice people to communicate with them.
We had an AI tool generate us a dating profile:
But we also need a picture to go with the profile to make it more believable, so we asked AI to generate us one of those as well.
These prompts could be tailored in order to create a profile that is more likely to appeal to the desired victim. Research can be conducted, and all of that information can be inputted into an AI generator to create the perfect profile for the job.
Vishing
Vishing, short for “voice phishing,” is a form of social engineering attack where fraudsters use telephone services to scam individuals into disclosing sensitive personal information, such as bank account numbers, credit card details, personal identification numbers (PINs), and passwords. Unlike traditional phishing attacks, which typically occur through email or malicious websites, vishing specifically involves voice or telephone communication.
While threat actors previously had to conduct these calls themselves it is now possible to generate voices using AI. While it is difficult to use this for an actual conversation it can be used to create prompts of voicemails. Using AI, it is also possible to emulate someone’s voice meaning that you could receive a voicemail from someone who sounds just like your boss asking you to send funds or resent a password that sounds really believable. There have also been reported instances of people appearing on video conferencing calls where their image and voice have been manipulated to provide the message the threat actor wants to give.
Using AI, we are able create a voice message. You can select the type of voice you want to hear, the tone of the message, how to pronounce certain words and where to pause in the conversation. Leading to a believable message.
Conclusions
It is worth noting that most AI providers have tried to implement security features and guardrails to prevent threat actors from utilizing their platforms for nefarious purposes. However, systems can be jailbroken and threat actors are also able to use the technology to create their own LLM (large language model) to generate the kinds of responses that they want. There are already dark web AI tools that have been developed such as WormGPT and FraudGPT. AI does not create new scams or ways of working. As it does with all of us, it simply speeds up and improves the activities the prompter is seeking to conduct. In fact, some of the descriptions in this blog were generated using AI highlighting legitimate uses.
There are lots of ways that cyber criminals can trick us into providing information we don’t want to, falling for scams, providing funds or access to profiles. However, this is nothing new and we should continue to be vigilant in the same way we always have been, while understanding that as technology develops, cyber actors are also developing the tools and techniques they use to try and fool us.
Curious how DarkOwl can help with your use case? Contact Us!
Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.
1. LockBit ransomware re-emerges after law enforcement takedown – The Hacker News
Proving resilient, LockBit ransomware came back into operation using new infrastructure just days after a global law enforcement operation took them offline. The actors debuted a new onion address and already had 12 new victims in their post-takedown operations. Additionally, the actors themselves authored a long note explaining what happened from their perspective. Read full article.
2. ALPHV/BlackCat ransomware group exit scams – The Hacker News
One of the most active ransomware groups of the past few years, ALPHV/BlackCat, shut down their onion site after their latest big victim, UnitedHealth’s Change Healthcare unit, purportedly paid their $22 million ransom. Actors believed to be a part of the gang engaged in conversation on Russian forum RAMP. Read article.
3. US government agencies are impersonated in business email compromise attacks – SC Media
US government agencies have been impersonated in business email compromise (BEC) attacks. The Department of Transportation, Department of Agriculture, and the Small Business Administration have all faced QR codes circulating in PDF documents. The QR codes send victims to phishing sites mimicking portals for the aforementioned agencies. All PDF’s had the same metadata, which indicated creation in Nigeria. Article here.
4. Iranian actors observed targeting aerospace and aviation industries in the Middle East – The Hacker News
Malicious Iranian cyber activity was observed targeting various industries using cloud infrastructure for their command and control (C2) along with social engineering tactics to deliver two backdoors named Minibike and Minibus. Targeting these industries allows for strategic information to be procured and sent back to the Iranian government. Article here.
5. Darknet marketplace Nemesis Market seized by German police – Bleeping Computer
German authorities, using intelligence from Lithuanian and American agencies and partners, captured infrastructure in both Germany and Lithuania, resulting in the take down of popular dark web Nemesis Market. Authorities seized $100,000 in cash as well as digital infrastructure that supported the illicit goods market. No information was provided regarding the status of the platform’s operators being arrested or contacted as of the time of this writing; DarkOwl will continue to monitor for updates. Read article.
6. Cybercrime gangs join forces to launch double extortion ransomware attacks – The Hacker News
GhostSec and Stormous ransomware groups have combined their operations to conduct ransomware attacks against technology, education, government, and many more verticals. Both groups are part of “The Five Families.” In August of 2023, cybercrime conglomerate SiegedSec announced the formation of “The Five Families” to attempt to offer structure to the digital criminal underground on August 28. They named ThreatSec, GhostSec, Stormous, Blackforums, and themselves as the five participants. Read full article.
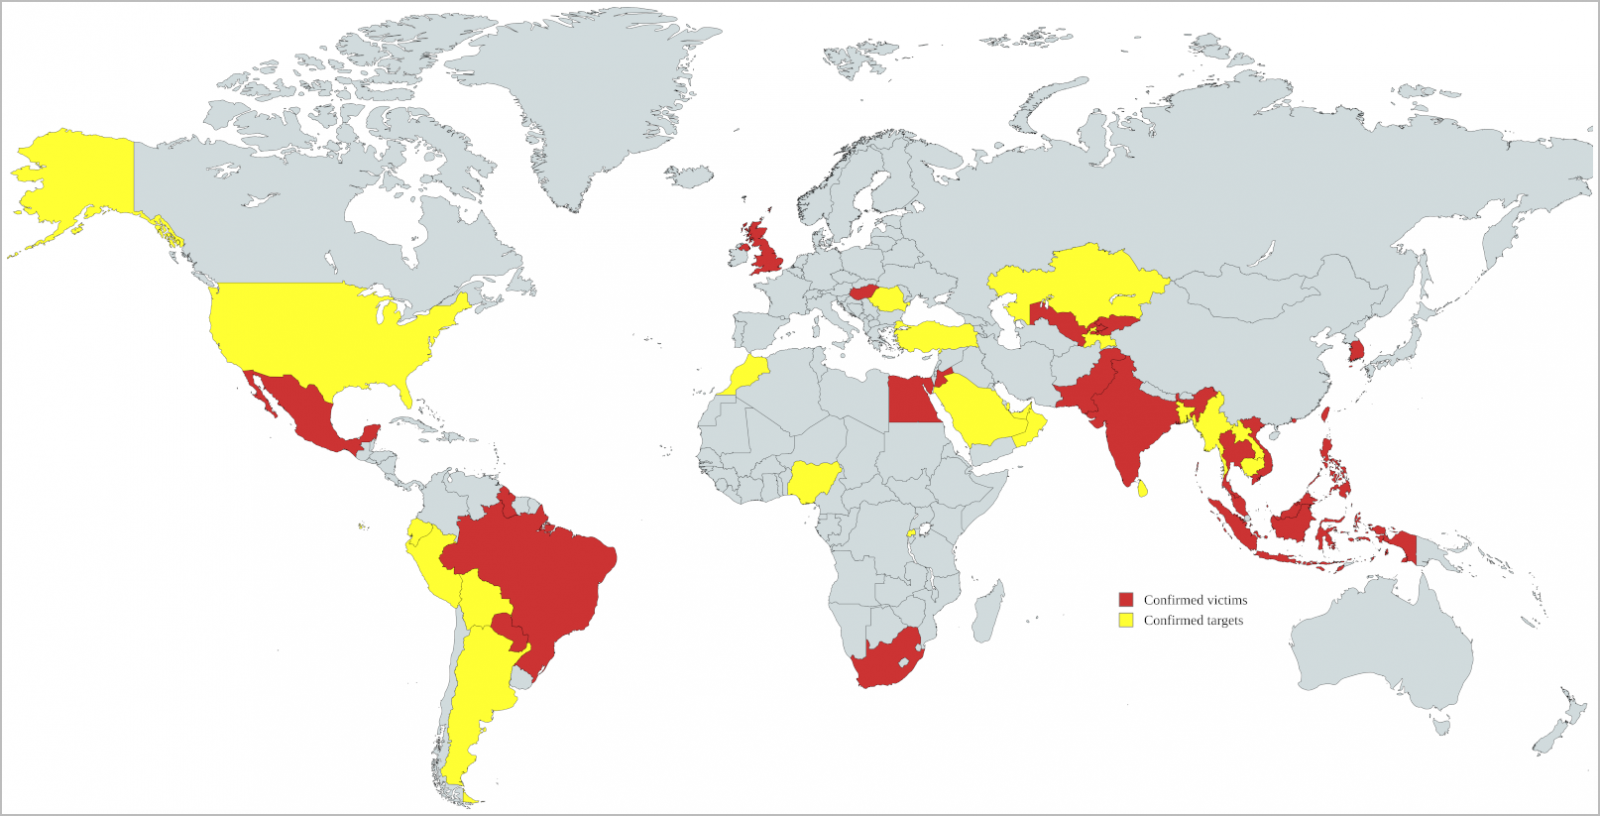
7. China’s “Earth Krahang” infiltrates organizations throughout 45 countries – Bleeping Computer
Government organizations worldwide were the target of a two-year, Chinese state-sponsored campaign. Spear-phishing is employed to deploy backdoors while exposed internet-facing servers are also attacked, leading to a multi-pronged attack. The group uses open-sourced tools to build VPN servers and then brute-forces email accounts to procure passwords, focusing on compromised Outlook accounts. Article here.
8. Microsoft source code accessed by Russian actors Cozy Bear – CyberScoop
As of January 2024, Russian state-sponsored actors Cozy Bear (who are believed to be part of Russia’s SVR intelligence branch) accessed Microsoft source code and company systems. The actors were able to read the emails of senior Microsoft executives. While the exact nature of this infiltration is still under investigation, Microsoft offered that they do not believe customer-facing systems were accessed/impacted. Read full article here.
Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.
The government, along with Law Enforcement, is heavily impacted by ever-evolving technology and there is a multitude of malicious actors conducting espionage, stealing data, attempting to infiltrate, and shut down systems critical to everyday life.
These malicious actors with a proven state-sponsored tie are often called Advanced Persistent Threats (APTs). The digital realm is heavily involved in geopolitical conflict, and its role and that of adversarial actors must be explored.
In this session, we will dive into the big 4 cyber adversaries:
Explain how cyber experts are trained
Explore the use of front companies and technology to online activities
Examine ties to their governments
Cover common offensive and defensive capabilities
Glimpse into the possible future with AI used in operations
For those that would rather read the presentation, we have transcribed it below.
NOTE: Some content has been edited for length and clarity.
Mark: My name is Mark Turnage, I’m the CEO and Co-Founder of DarkOwl and with me, I have Erin Brown, who’s our Director of Intelligence. We’re pleased that you joined us here this morning. I’m just going to make some introductory remarks, and we’re going to conduct this webinar as a sort of fireside chat between me and Erin and talk about four cyber countries – powerful cyber countries: Iran, North Korea, China, and Russia.
Just a couple of introductory remarks from me, we live in very interesting times. It’s a very famous Chinese curse and I think it’s fair to say that over the last several years, the world has become considerably more uncertain and more unstable. We have wars being waged in Ukraine, in the Middle East, we have a considerable amount of tension in East Asia, between China and Taiwan, and against that backdrop, there are a number of elections taking place this year around the world, including here in the United States, our presidential election. All that means that the cyber sphere has become even more important and more deserving of our attention as we think about that instability and how to better manage that instability. And against that background, four countries are continually mentioned: Iran, Russia, China, North Korea. Interestingly enough, two of those, China and Russia, are quite large countries and powerful in their own right. Two of them, North Korea and Iran, are cyber superpowers, in spite of being relatively small and in the case certainly of North Korea, having quite a small economy. So, we thought it would be useful to talk, to have a conversation about those four countries and talk about their cyber capabilities and how they use the cyber sphere, both for their own purposes and to sow instability and discord. So, with that, I’m going to just start asking Erin some questions.
What are the main cyber threats posed by these four countries?
Erin: There are a lot of different threats that they’re posing, and it really depends on what they’re trying to achieve. We see them conducting cyber espionage, we see intellectual property theft, attacks on infrastructure. It really depends on what their motivations are and they have many groups within their countries that are conducting these types of attacks – but most of them, all four of them, I would say, have a joint desire to advance their global influence. They all want to be the superpower of the world and they want to do that in both the digital and the physical world. We’re seeing that overlap, as you just mentioned in your introduction, as there’s more and more real-world conflicts happening. We’re seeing a huge cyber element to that. But then they do have their own distinct motivations as well in terms of what operations they’re conducting. North Korea, for example, we’ve seen them conducting a lot of attacks that lead to financial gain because they’re using those funds to finance other operations that they’re doing and things that they’re doing within the country. So, they all pose a huge amount of risk to both countries and organizations in terms of what they’re trying to achieve to advance their global power, basically.
And is it fair to say that of those four, North Korea is the most quote unquote, financially oriented in terms of their cyber activities? Or is the same true, say, of Russia?
I would say so. I think we know North Korea from a government perspective, is doing that financial motivation and gain. I think with Russia, especially and Iran, to a certain extent as well, we see that overlap and bleeding between who is the state-sanctioned, state-sponsored groups, and those actors that maybe the state is allowing them to operate. So obviously, you know, the ransomware gangs in Russia are making a huge amount of money off of corporations worldwide and there are suggestions that they’re at least allowed to conduct their activities by the Russian government. One could infer from that that the Russian government may be getting kickbacks from them and from that type of activity, but we don’t see necessarily the state-sponsored groups that are the military groups necessarily having that financial motivation and other countries. But Iran and Russia certainly have that criminal overlap.
Which brings us to the question of how these countries actually organize their cyber operations. You mentioned that some of them may or may not incorporate private actors in those operations, and others are more official. So, how do they organize their operations?
It’s quite a complex makeup across all the different countries and they all do it slightly differently. You do get those differences between what is state-sponsored, what is state-sanctioned, what is state-allowed. So, there are all of these distinctions within how you group them, but primarily, we see that the countries have military and civilian intelligence services. So, they’ll have military operators that are part of their armed forces that are going out and conducting these cyberattacks, and then you’ll also have intelligence agencies. So similar to how we have the CIA in the US, they have their equivalents that will also be conducting cyber operations on their behalf as well and depending on who’s conducting the attack, you’ll see different types of attacks and different victims as well in terms of what they’re trying to achieve.
But then we do also see civilians that are somewhat separated from the government being utilized. So, we do see a lot of front companies being used by these countries. This will be a seemingly legitimate company that is set up in country that has government backing behind it. That’s not necessarily obvious, so that they can have that air of conducting activity and not being linked to the government, even though they are. Then also we do see, as we just mentioned, with the financial motivation, we do see in especially North Korea, around countries that don’t have as much stability and financial security. We’ll see these actors that are doing a day job with the government and then in the evening, they’ll be using those skills that they’ve learned with the government to conduct cyber activities and criminal activities. So, it’s a murky infrastructure in terms of how these are set up but I would say is all of these countries do have set up groups and organizations that are there to conduct cyber espionage and cyberattacks on other countries.
Mark: This odd mixture of official and unofficial criminal gangs must make attribution really difficult when you’re looking at an activity, trying to attribute who the actor is who is behind the actual action.
Erin: Yeah, it’s incredibly difficult. And I would say it’s probably more difficult for people like ourselves that are outside of the government remit to identify that information because it’s very noisy in terms of what’s being conducted, who’s doing what attacks, and then things like the malware that they use. A lot of countries will use off the shelf malware, but lots of other groups use that as well. So, just because a malware is being used doesn’t mean that it’s attributed to one particular group. Even if that group invented it. For instance, Stuxnet is a good example of that – it was developed by the US and the Israelis, but it has been utilized far and wide by other nation-states, and by criminal actors since then. So, it’s really difficult to know who is conducting these activities and mistakes are made in terms of these attributions as well between different groups. Whenever we’re looking at this attribution, whenever we’re looking at this activity, the attacks that are happening, we’ll make assumptions about what we think that’s connected to you don’t really know unless you’re in those groups and being able to see that. So attribution is incredibly difficult and when we’re talking about APTs and we’re talking about nation-states, we’re talking about probably the most sophisticated cyber actors that are out there, that most of the time are trying very hard to obfuscate their activities and obfuscate who they are and who is conducting them. It’s a very tricky thing to be able to attribute that activity. So, one of the things I would say about it is it’s more about knowing what the techniques are than knowing who is doing it so that you can protect yourself from those techniques and those vulnerabilities within your organization. I guess some might say it doesn’t really matter who’s doing it when it comes down to attribution, it just matters that you stop it. So, it’s an interesting balance.
Mark: Yeah. Although, if you’re a foreign leader, say, the president of the United States, the Prime Minister of Great Britain, the President of France, and your country is in some fashion attacked by a cyber operator, attribution becomes important in terms of how you respond. So that’s a challenge I’m sure that many leaders face.
Let me switch gears a little bit and talk specifically about China. The Great Firewall of China – what’s the impact of that on both their capabilities and on the ability of outsiders to see what’s happening in China?
Erin: For those who don’t know, I’m sure most people do, but the Great Firewall is what we refer to as the operations that China put in place to silo their internet from the rest of the world. So, it means that most of their citizens aren’t able to access the internet in the same way that we do and they’re not allowed to access certain things. So, it means that the government can really lock down the messaging and the news that citizens are being able to access. And as part of that, they do also have their own apps and search engines and things like that. A lot of social media like Facebook and Instagram and WhatsApp can’t be accessed in China. Instead, they have WeChat and WeChen and Weibo and other ways that they’re, doing that. It always from the outside is seen as a way of controlling the citizens and the messaging that they’re getting and what they’re able to do, but it does also highlight the sophistication that the Chinese government have in terms of cyber activities, in terms of how they’re able to monitor their own citizens and lock down that information and how sophisticated their surveillance and censorship is. So, it really highlights some of the skills that they have. It’s the same cyber operators influencing the Great Firewall as conducting some of these attacks that are happening, and it shows how they want to have their world order and what some of their motivations are in terms of the cyber operations that they’re targeting.
It’s worth mentioning that they aren’t the only country that’s doing that. Russia has Runet – they are expanding and trying to lock down what their citizens are able to see. And Iran and North Korea have very similar methodologies in place. I would say with North Korea, we know even less about that, just because of the isolationist way that North Korea operates. It’s very hard to know how that functions but I think it just demonstrates the sophistication that they have and the abilities that they have of surveillance and censorship that they utilize outside of the firewall as well as inside it.
Mark: So, from an adversarial perspective, we’re in an environment where these four countries have unencumbered access to the world’s internet. It’s open. We’ve made it open deliberately, but we have very limited access, on a variable basis to their internal country networks and I would put, you would put China at the top of that at the top of that list.
Erin: Yeah, definitely. So, it’s very hard as analysts. Going back to that attribution point as well, to know what’s going on inside of that firewall because they’re locking down that information. What messages are they sharing? What is it that they’re putting out about adversaries when there is a campaign that is publicly reported or Chinese actors are indicted, which has happened several times? What is the messaging that they’re putting inside internally? And I think, with Russia, we’ve seen this with the Ukraine war and the messaging that they’ve put forward about Ukraine to their citizens in terms of “they’re saving the country, it’s not a war, it’s a defensive position,” like very different to what we’re seeing outside of, of that realm. So, it definitely impacts on that attribution and what we’re able to understand about what they’re doing. One thing I would mention, just as well, because we’re a dark web company, but this is one of the ways that Tor can be used in a very legitimate way. I think we tend to focus on the dark web being a bad thing for criminal activities, but it’s a way that a lot of citizens are in these countries that have lockdown internet, are able to access Western and outside media and this is the reason that a lot of social media companies will have mirrors on the dark web. X, formerly Twitter, has it, Facebook has it, some governments have websites on the dark web. So, people are able to access that information. It’s a useful way for people to be able to get that outside information as well.
Can you talk about some of the notable cyber campaigns that have been conducted by these four countries?
Sure. There are a lot, and as we’ve already covered attribution is tricky in terms of how we associate particular campaigns that we’re seeing to particular countries and the groups within them. China has had some very significant operations in recent years targeting a lot of countries in their region. We’ve seen them spying on Cambodia, the Philippines, South Korea, and they do this using phishing techniques to gain access. So, you know, they are using some of the same techniques that we’re seeing criminals using that we’re all warned about at our companies in terms of “don’t click on a link.” Those sophisticated users are using those methodologies as well and we have seen things like when they recently targeted Japan’s space agency and one of the things that China is well known for is targeting companies in stealing intellectual property, and then taking that information back and using it to develop their own technologies and issue patents on their technologies. So, that is a thing that they continue to do in terms of expanding their power and what they have access to. That’s something that we’ve seen China doing a lot of recently.
With Russia, probably the most significant one that is fairly recent was that they targeted Microsoft’s corporate systems. They targeted the executives and I believe the legal team and were able to access some emails and documents, and they did this again with fairly simple methodology. It was a password spray attack. So basically, they just took lots of different ways that people might use a password and put it across all of their systems. This really highlights why you need to have good password hygiene across your corporation, and governments everywhere because that is a way, not just with nation-states, but across the whole adversarial cyber field that we’re seeing people get access is through credentials. So, it’s a really important thing to identify. And then I think you can’t talk about Russia’s activities without mentioning the war in Ukraine, because there definitely is a cyber war going on as well as the on the ground war. One of the things we’ve seen fairly recently was they hacked into webcams in Kiev, so that they could look at what air defenses were being used in the city and they did that ahead of a missile attack. They wanted to see where their missiles would be defended and where they wouldn’t. That is a real-world example of how the cyber and the real world are linked together and they’re utilizing cyber tools to help them with military campaigns.
In terms of Iran, there is a group known as, Mint Sandstorm. So again, using phishing techniques, but social engineering as well. This is something we see a lot with Iranian actors – utilizing social media and fake social media accounts to lure people into giving them what they want. We saw them on a large recruitment and job networking sites that were creating these accounts, creating several levels of personas that knew each other to make them look as, as real as possible and then we’re using that to identify people that they wanted to target as part of the Israel-Gaza conflict. They were using this as an espionage dash intelligence gathering campaign. With these campaigns, it’s not just about disruptive action or getting access, sometimes it’s just understanding things that are going on to help them with other areas.
Then North Korea, again, is a trickier one just because of their isolationism and the groups that we see. Probably the most prominent group that’s been mentioned in recent years, and they have been around for a long time now is Lazarus. They have been involved in significant financial thefts as well as espionage. So, a lot of cryptocurrency, ransomware attacks, etc. They were responsible for the Sony hack way back when, I believe it was 2016, but as recently as this year, they’re still operating. They were seen conducting cyber espionage campaigns, targeting defense technologies, again creating fake social media profiles, and then deploying malware once they’ve got access to individuals. So, you know, there’s a range of activities that are going on and that very much is a high-level overview of some of the activities. There’s probably a lot more going on that we don’t know about, and a lot more going on that we do know about, but it hopefully gives you a sense of the types of campaigns that they’re conducting and also the variety of people that they’re targeting. I think you said earlier about governments obviously care about attribution, and they should, and their governments hopefully are better at attribution, but I think there’s an old world view that nation-states and spying and espionage is a thing between governments and these days with cyber, it just isn’t like everyone is vulnerable to attacks. Everyone has information worth stealing, so everyone has to be vigilant.
Mark: It’s notable that in your answer, in talking about the various cyber campaigns conducted by these countries that many, if not most of them, are using basic password access, phishing, social engineering, as opposed to, Zero-day exploits that they have access to on an exclusive basis. That’s quite notable.
Erin: Zero-day exploits are really hard to develop and they’re really expensive to develop. If you don’t need them, because you can get in by a weak link of a person clicking on a link or believing a phishing email, then then why waste your time and infrastructure? I would say they still definitely do utilize those Zero-day attacks and that is something that’s developed, especially Russia and China, but those are the ones that it’s harder to hear about, right? Those are the ones that they don’t want people to know what that capability is and who they’re targeting. And they would save that for their most important victims.
Mark: We, in the cyber security industry, live in evolving times. There’s a lot of changes in technologies and I would include in that, by the way, artificial intelligence, the rise of artificial intelligence. How does that affect how these four countries are both organizing themselves and conducting their cyber operations?
Erin: I think in the same way that the rest of us are, right, they’re still learning. They’re still coming to grips with these new technologies and how they can utilize them and how they’re going to work, but they definitely are. I think they definitely want to utilize them and there is a growing sophistication. We have seen particular countries trying to target AI companies. I think there was an article, a month or two ago about OpenAI reporting, I think it was 4 or 5 specific APT actors that they had kicked off of their site and they were using AI to do the things that a lot of other people are doing, like help them with their work, but also create phishing emails and ask it questions to do research for them about the capabilities that other countries and their victims have. So, we know that they’re using AI, we know that that’s happening.
There are also, I believe it was China, I’m trying to remember – it was either China or North Korea, but they’re actually investing in companies that are developing AI in certain areas of the world so that they can own that technology for themselves as well. What I would say with AI and those technologies is the US and Europe and the likes of OpenAI, oh, I can’t their name is escaping me. But, you know, the prominent AI providers at the moment, they are far and above, ahead of Russia, and China at the moment. But I was actually at a talk with someone from those companies a couple of weeks ago, and they were saying, we’re only a couple of months ahead and they are going to catch up, like it is going to happen. So, it’s something that everyone needs to be aware of and needs to be vigilant about. I think the takeaway point from that is that they are using it. They are keeping an eye on emerging technologies. They themselves as well have to constantly evolve to remain relevant and successful because people’s defense gets better all the time. So, you need to constantly evolve to get around those defenses and those ways of operating. It’s definitely something that they focus on.
Mark: You mentioned earlier, by the way we’re a darknet company and we cover the darknets, and we cover darknet adjacent sites. You mentioned earlier in one of your answers the use of the darknet by citizens in countries which are behind firewalls or where they have limited access to the outside internet. But how do the countries themselves use darknet and these other online platforms in their own operations?
Erin: Yeah, that’s a difficult one and it’s a bit murky. Again, going back to that attribution problem and especially on the dark web where everyone is trying to stay as anonymous as possible to know who is doing what. We know that they definitely do utilize it. We know that there are probably actors on there that are sowing disinformation and details on the dark web and sharing them. But, you know, one of the things that we’ve seen more in recent years and is a bit more obvious is hacktivist groups and criminal groups that are associated or in somewhat sanctioned by governments. So, we’ve seen this with Killnet in Russia and a handful of other groups that came out in support of Russia when the invasion of Ukraine happened, and they are very active on things like Telegram. They will say who they’re targeting. They will say why they’re targeting them. They’re often going after NATO participants. They will show evidence of defacements or DDoS attacks. So, they’re very vocal and they want people to know what they’re doing, and they do have those links or at least a nationalist fervor that is very clear. And we see that other groups linked to North Korea and Iran also have telegram channels and other channels that are very vocal. One of the interesting things that we’ve seen, though, that is less how they’re operating but gives us more insight into how they’re operating, is we have seen a lot of data leaks relating to some of these countries and their governments. Everyone’s falling victim to data leaks in recent years. It’s big business on the dark web – selling that data, but there’s been a huge increase in the last probably 6 to 9 months, especially for China in terms of government data being leaked. There was a huge leak of the Shanghai police late last year that was assessed to be one of the biggest breaches ever, data breaches ever, and it had a huge amount of information about their law enforcement, but also their tools that they were using to target their citizens. So, it gave security analysts insight into what they’re doing that the governments wouldn’t necessarily want them to have and there was another recent one as well on a GitHub repository. So slightly not the dark web, but where it was one of the front companies that was conducting cyberattacks on behalf of China. All of their information was released, and we’ve seen large scale releases of Russian data, Israeli data as well, talking about those conflicts. There is information like that and while we’re all looking at that dark web data and saying, oh, this is giving us insights into these countries that we don’t know as much about. You can believe that they are also doing the same. So, when there are leaks of US, UK, European data, those countries are definitely going to have individuals that are on those dark websites collecting that data and reviewing it as well.
What do we do about this? It’s not like these four countries are going to wake up tomorrow and become parliamentary democracies and decide to conform to rules of international law. So, what do we do? What do we do about this?
Erin: I think it’s points we’ve already mentioned. You just have to be vigilant, and you have to have as much security as possible. I think there’s education that needs to happen to people about how you should operate, as you said, like these phishing techniques, password spray attacks, things like that. They’re fairly simple and they’re things that we can educate people about and I think we’ve been too focused in recent years on; okay, people know that if you get a bad email that you shouldn’t click on it, hopefully most of the time, but we’re seeing more and more smishing attacks, so text messaging and with the advent of AI, you can develop someone’s voice and get them to say anything you want them to say. So, you can get like a voicemail from your boss telling you to send you money or to click on a link. Things are becoming way more sophisticated in terms of how attacks can be conducted and therefore, our education to people about how to combat those attacks needs to be more sophisticated and I think it’s just staying up to date with what these threat actors are doing and this isn’t just the nation-states, it’s across the board, like what tools and techniques are being utilized, and are your systems set up to protect against those vulnerabilities? So I think it’s trying to be as proactive as possible and not just reacting when attacks happen.