Marketplace Spotlight: DarkBay

June 18, 2026

Darknet marketplaces (DNMs) have become one of the defining features of the dark web, enabling anonymous users to buy and sell illicit goods and services beyond the reach of traditional online platforms. Early marketplaces like The Farmer’s Market laid the groundwork, but it was Silk Road that brought global attention to the underground economy operating through anonymized networks such as Tor. Since Silk Road’s takedown by law enforcement in 2013, the DNM ecosystem has remained in constant flux, with competing platforms emerging, collapsing, or disappearing altogether as vendors and buyers migrate in search of stability and security.

In recent years, law enforcement agencies have significantly improved their ability to disrupt and seize DNMs, forcing marketplaces to adapt, else vanish. At the same time, users face growing risks from “exit scams,” where marketplace administrators abruptly shut down operations and abscond with funds held in escrow. This instability has accelerated the rise of more security-conscious platforms that prioritize operational resilience and tighter user vetting.

Modern DNMs typically operate on Tor or similar anonymity-focused networks, using layered trust and security mechanisms to protect both buyers and sellers. Features such as encrypted communications using PGP (Pretty Good Privacy), escrow payment systems, user verification, and rotating mirror domains are designed to reduce exposure and maintain continuity during takedowns. Some platforms have gone further by adopting invite-only models, restricting access to vetted users in an effort to strengthen operational security and avoid infiltration.

Darkbay is a darknet marketplace accessible through the Tor network, with a name seemingly designed to mirror the familiarity of the legitimate platform eBay. Like many dark web marketplaces, it connects buyers and vendors involved in the trade of illicit goods and services, including narcotics, stolen financial data, counterfeit documents, malware, and hacking tools. Transactions are typically conducted using cryptocurrencies, while features such as vendor ratings and escrow services help build trust in an otherwise high-risk environment. As with other DNMs, users face significant risks ranging from scams and financial loss to potential law enforcement action. According to DarkOwl’s Vision, we have over 12,534 results pertaining to DarkBay Market. Open-source information reveals versions of the DNM have existed since 2020. Since first collection, activity has remained steady averaging around 500 listings per month, excluding a drastic increase of listings in January 2026. Analysis of the increase in January reveal over 2K listings made by the vendor amazonianstore selling primarily prescription drugs. According to DarkOwl Vision, amazonianstore, is the most active vendor on the site posting over 7K listings.
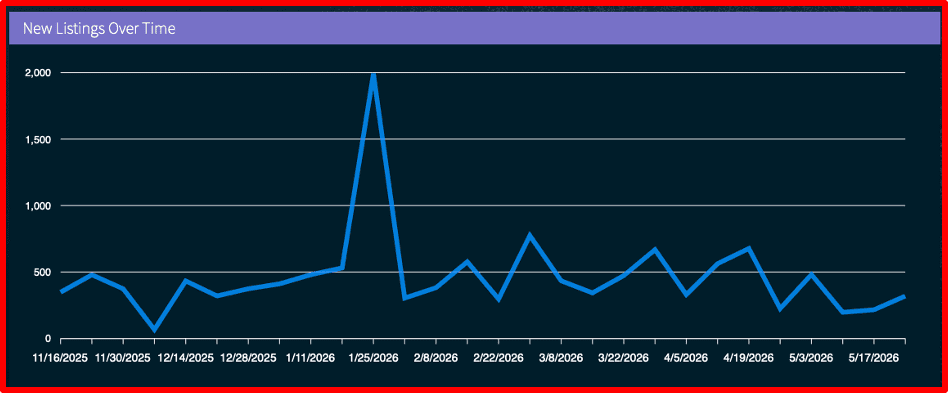
Figure 1: DarkOwl Vision Graph of DarkBay Market Activity
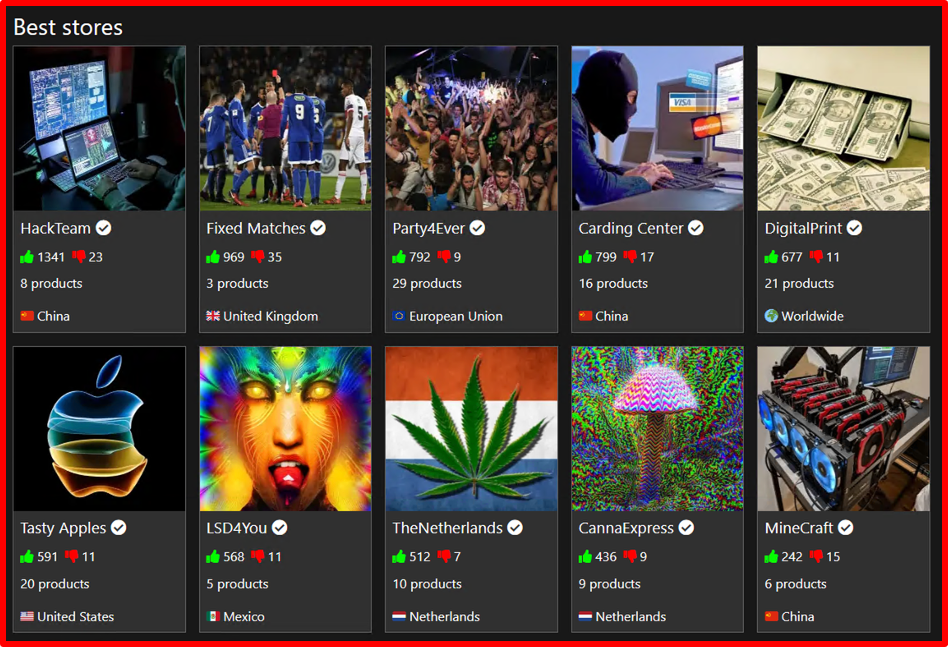
Figure 2: DarkOwl Vision Top 10 Vendor List for DarkBay Marketplace
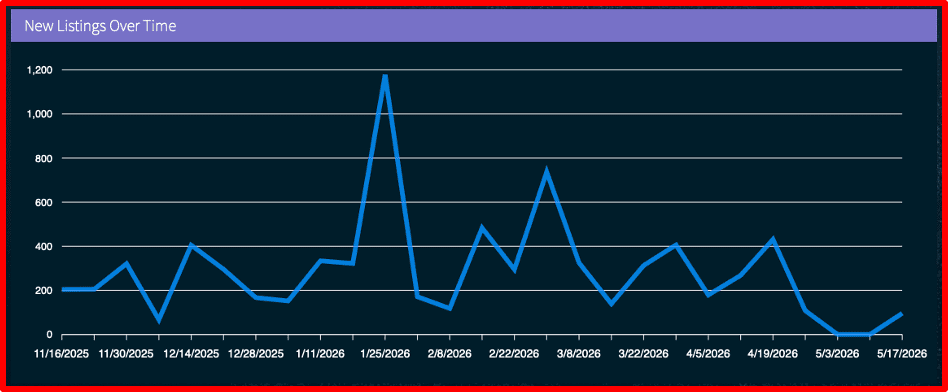
Figure 3: DarkOwl Vision Graph Activity for Vendor Amazonianstore

Open-source reporting on the marketplace remains limited. However, a Reddit discussion from January 2020 included multiple users questioning the site’s legitimacy. More recent analysis suggests that vendors primarily operate through associated Telegram channels, which buyers can contact directly. The overall credibility of sellers on the platform remains difficult to verify, and the extent of fraudulent activity is unclear.

The below screenshot shows DarkBay’s homepage. Unlike other DNM’s the site does not require you to log in to view “merchandise”. DarkBay’s page layout advertises popular sales, such as drugs and weapons, database leaks, and even a Goldendoodle puppy.
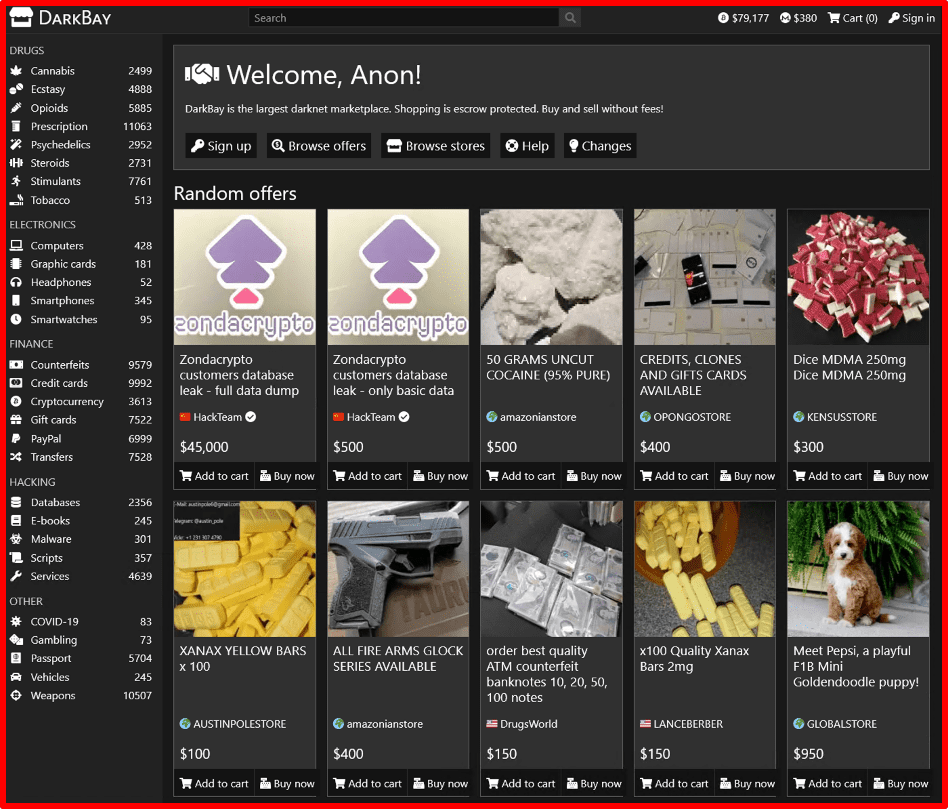
On the left-hand side, the page provides links to specific sales categorizing them as:

  • Drugs (38,292 Listings)
  • Electronics (1,101 Listings)
  • Finance (45,233 Listings)
  • Hacking (7,898 Listings)
  • Other (16,612 Listings)

Currently (as of early June, 2026) there is a total of 109,136 product listings. The drugs section currently contains the most product listings, while Miscellaneous contains the fewest listings. The products with the most listings are currently prescriptions (11,063 listings), weapons (10,507 listings), and credit cards (9,992 listings).

Additionally, DarkBay features dedicated “store” pages that highlight individual sellers and present them as verified vendors. These pages allow buyers to browse all products offered by a seller and indicate their experience through a simple thumbs-up or thumbs-down rating system.
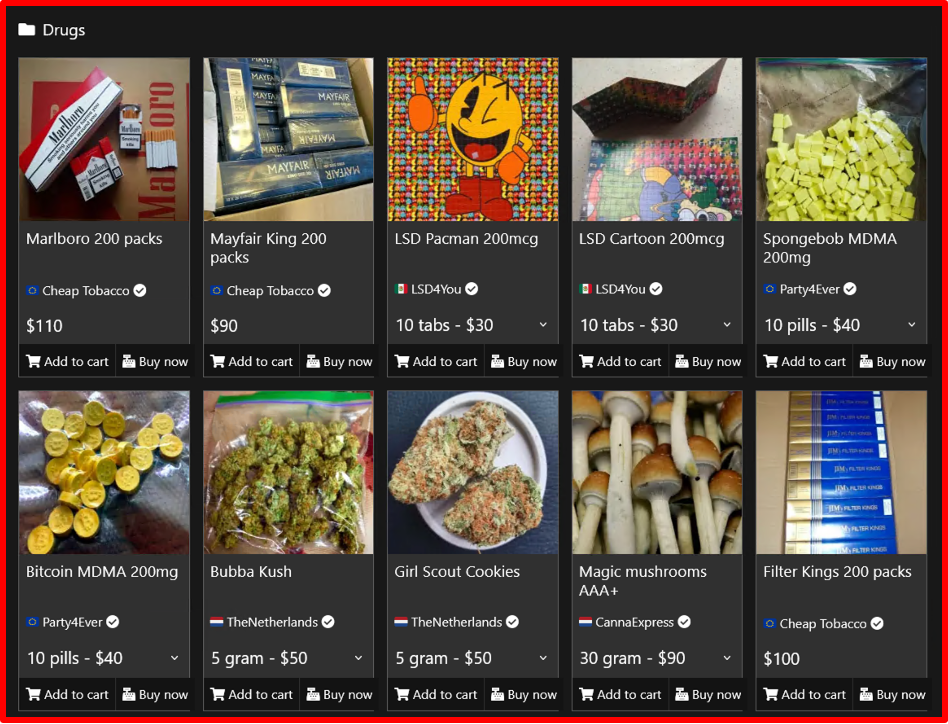
The drugs section on DarkBay offers a variety of illicit narcotics and prescription drugs (including tobacco products) such as marijuana, MDMA, LSD, and more. Currently (as of early June, 2026) there are a total of 38,292 drug listings on this market. The below displays a preview of these listings: 

  • LSD Pacman 22mcg, $30 USD 
  • MDMA, 10 pills/$40.00 USD 
  • Magic Mushrooms, 30 grams/$90 USD 

DarkOwl analysts selected one product (see below screenshots) to further examine. The below product is allegedly “Pure Uncut Heroin 90%” shipped from Germany. According to the description the product is “Pure uncut Afghan heroin” and can ship worldwide. The site does not provide an area for reviews or comments. Since November 2025, DarkOwl Vision shows over 300 listings for “Heroin” from 7 vendors.
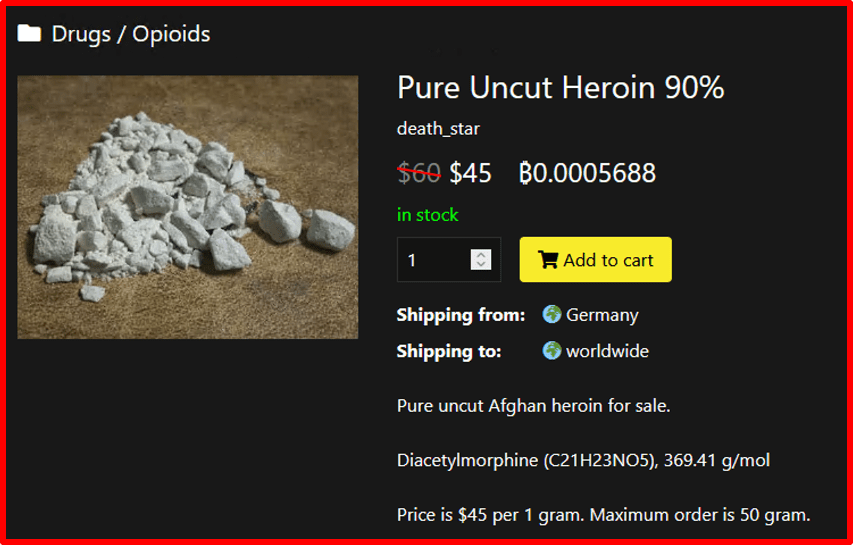
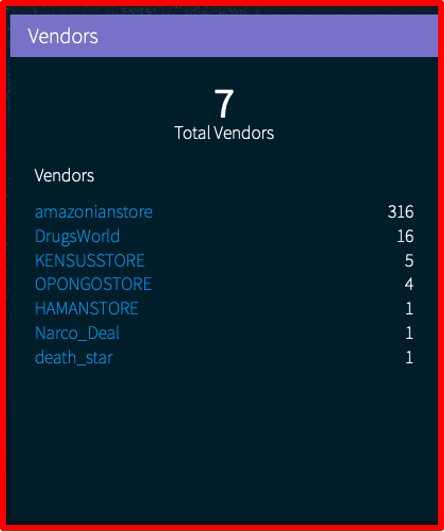
Figure 9: DarkOwl Vision Vendor List

The Electronics section on DarkBay features a wide range of illicitly sold devices, including smartphones, computers, smartwatches, and other consumer electronics. Among the available categories, the computers section contains the highest number of listings, totaling approximately 428 active posts. In addition to hardware sales, vendors also advertise cyber-related services such as social media account hacking, as well as fraudulent documents including fake driver’s licenses and passports.

A significant portion of the smartphones listed for sale — including both Apple and Android devices — are offered by vendors identified as “verified sellers” on the platform, suggesting an established reputation within the marketplace. The prevalence of verified accounts may contribute to increased buyer trust and the continued growth of illegal electronic commerce on the site.

The Finance section offers “Counterfeits, Credit Cards, Cryptocurrency, Gift Cards, PayPal, and Transfers” with counterfeits and credit cards containing the highest number of results. The section’s homepage prominently showcases counterfeit currency and fraudulent credit card offerings, indicating that these products constitute a significant portion of the marketplace’s financial activity.
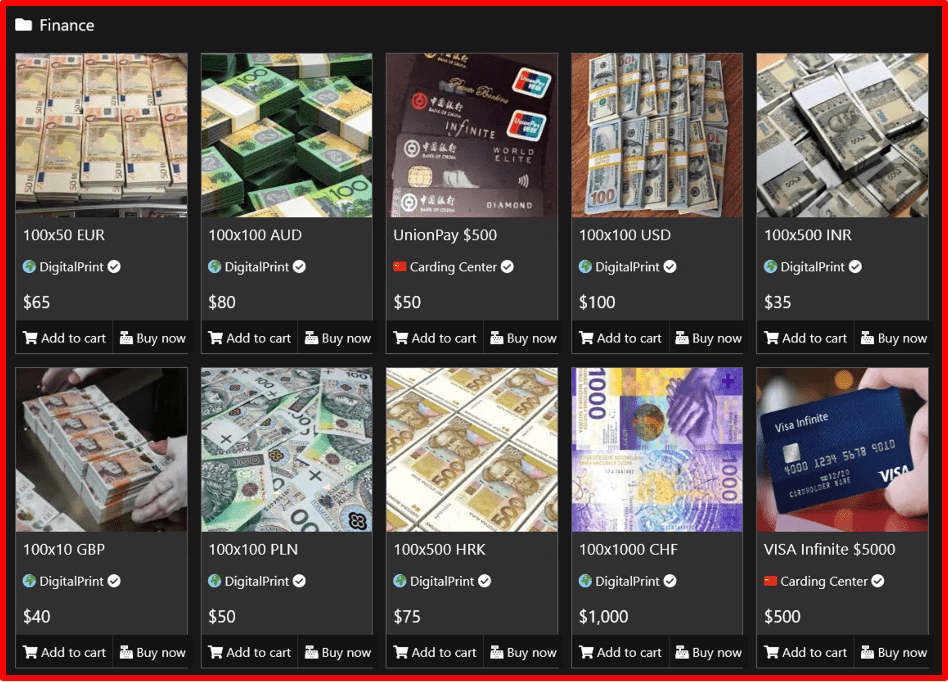
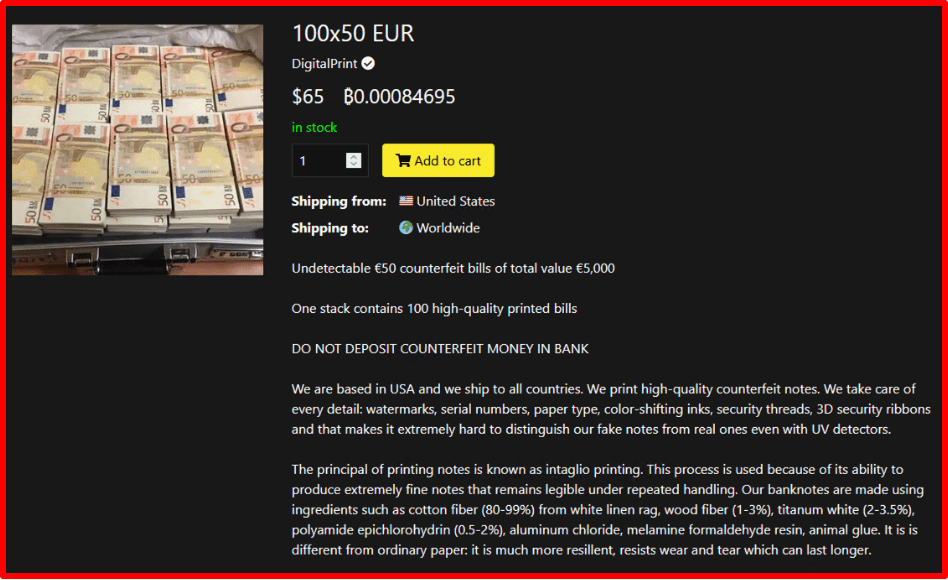
After reviewing the counterfeit cash offerings, analysts identified a significant volume of sales linked to the verified seller, DigitalPrint. The vendor advertises counterfeit currency from multiple countries and claims to operate out of the United States. In promotional posts, the seller states they “take care of every detail: watermarks, serial numbers, paper type, color-shifting inks, security threads, 3D security ribbons and that makes it extremely hard to distinguish our fake notes from real ones even with UV detectors.” They also caution buyers against depositing the counterfeit currency into banks.
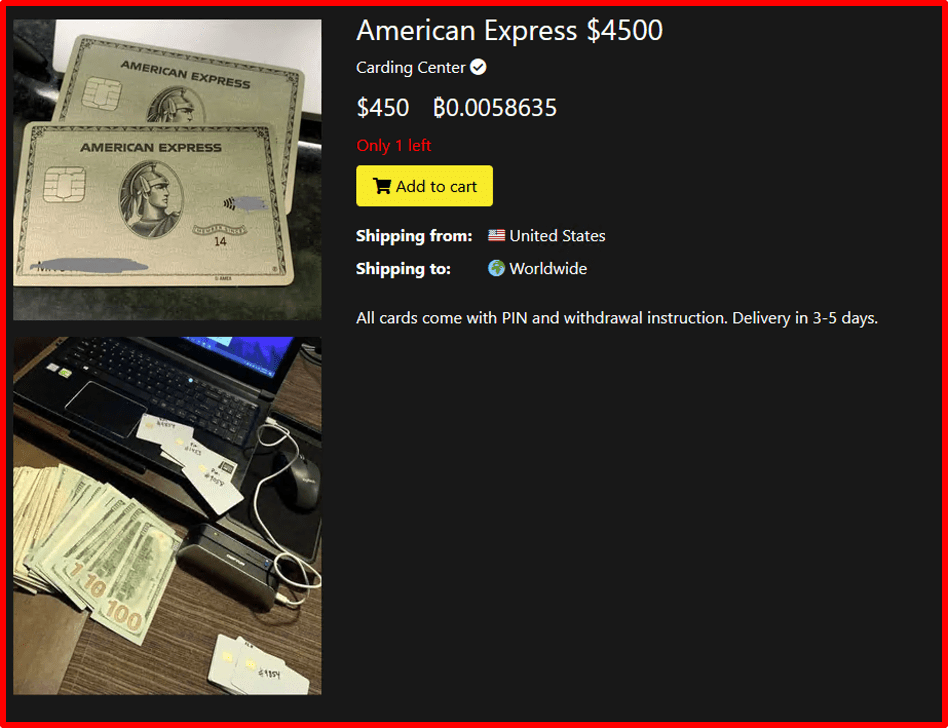
A review of the credit cards for sale indicates that many of the listings claim to include preloaded spending limits. This section appears to contain a higher number of random, unverified sellers compared to the counterfeit documents section. In the example below, a seller advertises an American Express card with a purported $4,500 limit for $450 USD. The listing also states that the card includes a PIN and cash withdrawal instructions.
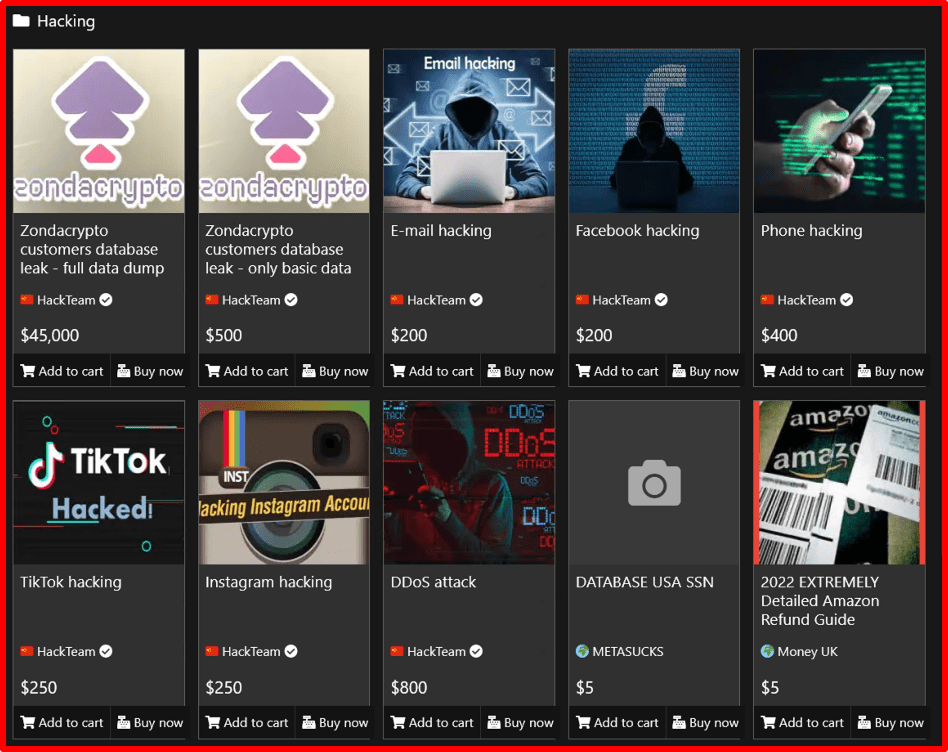
The Hacking section offers a range of illicit “products,” including database leaks and services claiming to provide unauthorized access to email and social media accounts. This includes alleged “pre-built” malware that buyers can purchase and use to infect machines of their choosing.

Due to the absence of review or feedback mechanisms on the site, the credibility and effectiveness of these sellers’ claimed hacking capabilities cannot be verified. Although sellers rarely disclose how the information was obtained, it is likely that at least some of the account data originates from prior database breaches or leaked credential collections.
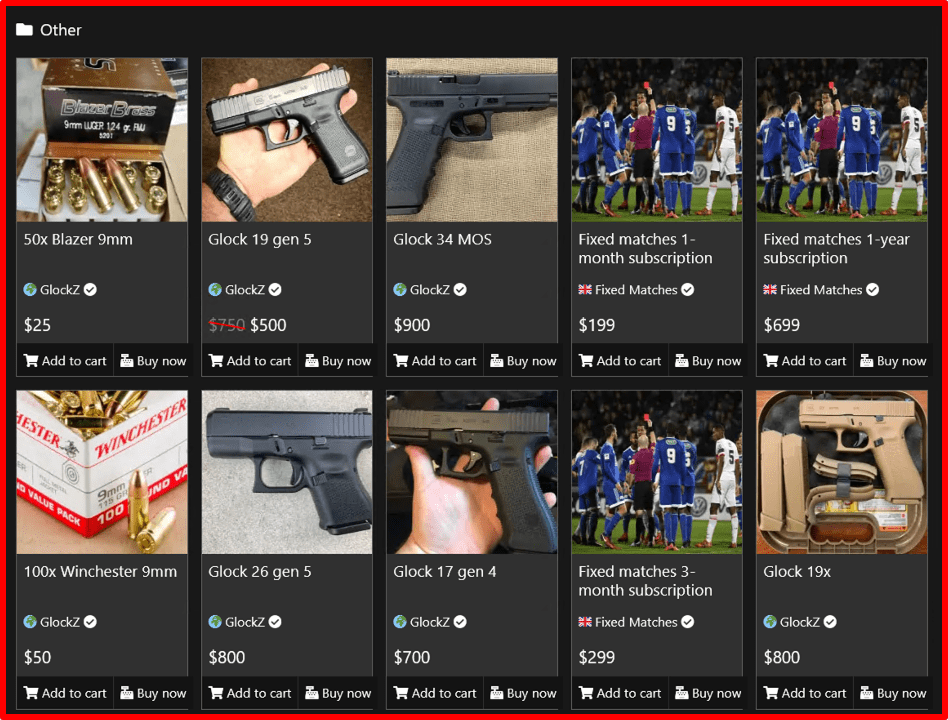
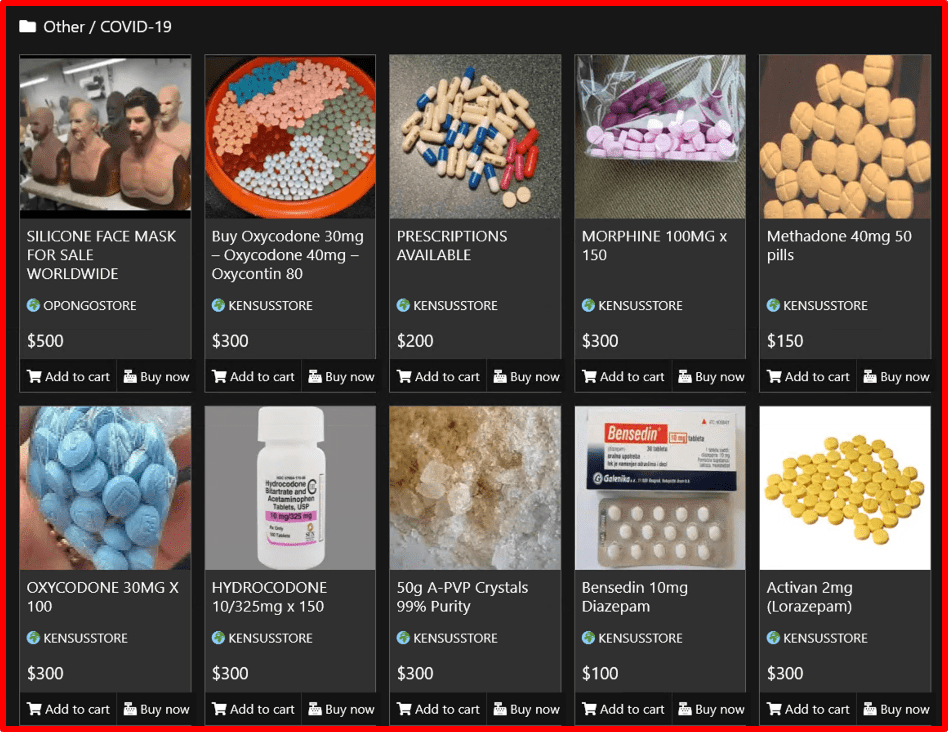
The “Other” category includes a variety of miscellaneous sale sections, such as COVID-19 items, gambling services, passports, vehicles, and weapons. Among these, weapons account for the largest volume of listings, with a total of 10,507 sales. Another notably active section is passports, where buyers can obtain counterfeit identification documents, including Social Security numbers.
Open-source information revealed a 2021 publication from the National Library of Medicine (NLM) that referenced the sale of COVID-19-related materials on DNMs prior to the availability of legitimate vaccines. The publication specifically identified DarkBay marketplace as hosting the majority of COVID-19-related listings, with personal protective equipment (PPE) being the most frequently advertised product category. The chart below presents NLM’s findings on COVID-19–related listings across DarkBay compared with other analyzed marketplaces, showing a significantly higher number of such listings on DarkBay.
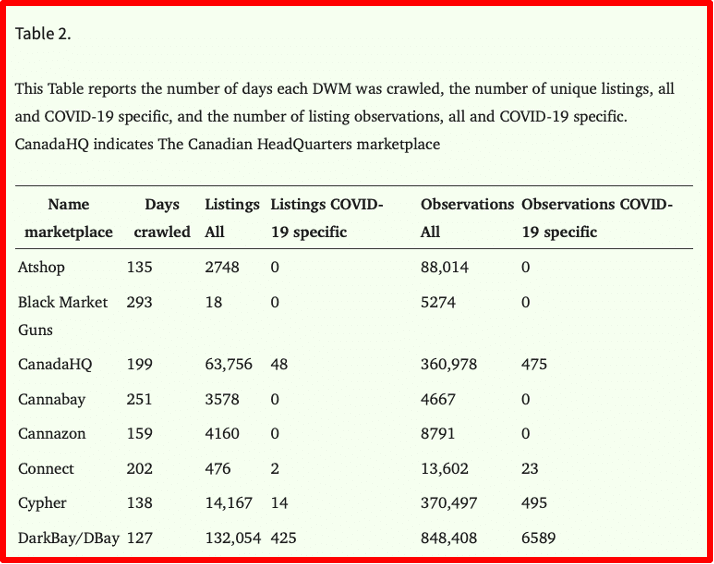
Figure 16: https://pmc.ncbi.nlm.nih.gov/articles/PMC7819623/

Analyst review of the current COVID-19 section found that most listings now appear to involve illegal prescription drug sales, representing a shift from the activity observed in 2021. The reason these prescription drug listings remain categorized under the COVID-19 section is unclear.
While DarkBay appears to lack the legitimacy and reputation of more established DNMs, many buyers are still drawn to them because they offer products at lower prices. Its rise in prominence reflects the disruption caused by the shutdown of major marketplaces such as Silk Road seizure and AlphaBay shutdown. Although the legitimacy of vendors and listings on these platforms is often uncertain, the products advertised are typically in high demand among individuals seeking illicit goods. As a result, transactions continue to occur on these sites regardless of concerns about their credibility or authenticity.


Curious to learn more about darknet monitoring? Contact us.

What are Man-in-the-Middle Attacks?

June 18, 2026

Cybersecurity might as well have its own language. There are so many acronyms, terms, sayings that cybersecurity professionals and threat actors both use that unless you are deeply knowledgeable, have experience in the security field or have a keen interest, one may not know. Understanding what these acronyms and terms mean is the first step to developing a thorough understanding of cybersecurity and in turn better protecting yourself, clients, and employees. 

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, push bombing, web application attacks. In this edition, we dive into man-in-the-middle attacks.

While the concept itself is straightforward, the digital execution can be incredibly sophisticated. Let’s explore what a man-in-the-middle attack is, how threat actors pull it off, and how you can protect your data from being intercepted.

Man-in-the-middle attacks may not generate the same headlines as ransomware or major data breaches, but they remain a significant threat across the cybercrime ecosystem. These statistics highlight a simple reality: while many organizations focus on attacks against endpoints and applications, data in transit remains a highly valuable target for cybercriminals.

  • Industry reports suggest nearly 58% of all posts on criminal forums and marketplaces contain banking data of others collected by MITM or other attack types.
  • Estimates show that 35% of exploitation activity involves man-in-the-middle attacks.
  • MITM attacks continue to evolve alongside cloud adoption, mobile devices, and remote work environments, creating new opportunities for attackers to intercept sensitive communications.

A Man-in-the-Middle Attack (MitM) is an attack that compromises the communication between the two parties who believe that they are communicating directly with each other. Instead of data moving directly from a user to a website, application, or service, the attacker inserts themselves into the connection to observe, steal, or manipulate information being transmitted, placing themselves “in the middle.”

The goal of an MitM attack is to compromise the CIA Triad, specifically violating confidentiality (by reading private data) and integrity (by altering the data in transit). Threat actors use these attacks to steal credentials, account details, credit card numbers, to inject malware into a victim’s system, or to create a smokescreen for an advanced attack. Depending on the technique used, victims may never realize their traffic was compromised.

  • Confidentiality: is your sensitive information only accessible to those authorized to see it?
    • Common Threats: phishing, ma-in-the-middle attacks, human error
  • Integrity: is your data authentic, accurate, and reliable?
    • Common Threats: man-in-the-middle attacks, human error, malware, hardware/software glitches

When you type a web address into your browser, your device trusts the local network to direct it to the correct destination. Threat actors exploit this trust using a couple of distinct phases: Interception and Decryption.

First, the attacker must get between the victim and their network destination. This can happen through compromised Wi-Fi networks, malicious routers, spoofed websites, DNS manipulation, or malware infections. Public Wi-Fi networks are a common target because users often connect without verifying the legitimacy or security of the network. Once traffic passes through the attacker-controlled system, the threat actor can monitor the communication in real time. After gaining access to credentials, cookies, or authentication tokens, attackers may impersonate the victim and gain unauthorized access to accounts or systems.

Common Types of Man-in-the-Middle Attacks

ARP Spoofing: Address Resolution Protocol (ARP) links IP addresses to physical MAC addresses on a local network. An attacker sends fake ARP messages to link their own MAC address with a legitimate server’s IP address. Suddenly, all data meant for the server goes to the attacker first.

Wi-Fi Eavesdropping / Rogue Access Points: An attacker sets up a malicious, free public Wi-Fi network with a common name (like “Free Airport Wi-Fi”). When a user connects, the attacker can view all unencrypted traffic flowing through the router.

DNS Spoofing (DNS Cache Poisoning): Attackers alter a DNS server or a device’s local cache to route a user to a fraudulent website that looks identical to a legitimate one (like a banking portal), allowing them to steal credentials.

Session Hijacking: Attackers steal session cookies or authentication tokens to impersonate legitimate users without needing their password.

SSL Stripping: SSL stripping downgrades secure HTTPS connections to unencrypted HTTP communications. This enables attackers to intercept information that users assume is encrypted.

Public Wi-Fi Credential Theft

While individual incidents often go unreported, cybersecurity firms routinely observe threat actors creating fake Wi-Fi networks that mimic legitimate hotel, airport, and conference, coffee shop wireless networks. Unsuspecting users connect to these networks and unknowingly expose login credentials, emails, and sensitive corporate traffic. These attacks remain one of the most common real-world examples of man-in-the-middle activity because they require relatively little sophistication and can affect large numbers of victims.

MyEtherWallet BGP Hijacking (2018)

In 2018, attackers hijacked internet routing to redirect users attempting to access MyEtherWallet. Victims were presented with a fraudulent SSL certificate and redirected to attacker-controlled infrastructure, allowing credentials and wallet information to be captured. The incident resulted in the theft of cryptocurrency and demonstrated how internet infrastructure attacks can facilitate man-in-the-middle operations.

Iranian Cyber-Espionage Campaign Using Fraudulent SSL Certificates (2011)

In 2011, attackers compromised Dutch certificate authority DigiNotar and generated fraudulent SSL certificates for domains including Google. Security researchers and Google reported that the certificates were used in man-in-the-middle attacks targeting users in Iran, allowing attackers to intercept supposedly secure communications such as Gmail traffic. Investigators later estimated that as many as 300,000 Iranian users may have been affected, making it one of the most significant documented MitM attacks ever discovered.

The common thread across MitM is trust: attackers succeed when they can convince victims—or their devices—that malicious communications are legitimate. Organizations and individuals can significantly reduce risk by following security best practices:

  • Use HTTPS: Always verify websites use HTTPS encryption. Modern browsers warn users about insecure connections, but users should still validate certificates and domains before entering credentials.
  • Avoid Untrusted Public Wi-Fi: Public wireless networks increase exposure to interception attacks. If you must use public Wi-Fi, always use a reputable Virtual Private Network (VPN) to securely tunnel and encrypt your traffic.
  • Implement Strong Wi-Fi Security: Ensure your home and office networks use strong encryption protocols (like WPA3) and change default router admin credentials immediately.
  • Enable Multi-Factor Authentication (MFA): Even if an attacker steals login credentials via an MitM attack, MFA acts as an extra layer of defense, making it much harder for them to gain access.
  • Keep Systems Updated: Security patches help close vulnerabilities attackers may exploit to conduct interception or session hijacking attacks.
  • Use VPNs: Virtual Private Networks encrypt internet traffic and reduce the risk of traffic interception on untrusted networks.
  • Monitor for Suspicious Network Activity: Organizations should implement network monitoring and anomaly detection to identify unauthorized devices, DNS changes, or unusual traffic patterns.
  • Implement Endpoint Protection: Ensure your corporate devices utilize robust endpoint detection software capable of identifying network anomalies, rogue certificates, and localized ARP spoofing attempts.
  • Train Employees on Phishing and Network Security: Many MitM attacks begin with social engineering or fake infrastructure designed to appear trustworthy. Security awareness training helps reduce successful compromises.

Security is a holistic culture, not just a software update. By understanding how threat actors operate and protecting both the physical and digital layers of your defense, you can ensure your data remains confidential, secure, and out of the middle.


Curious to learn more about dark web monitoring? Contact us.

What Darknet Markets Actually Look Like From the Inside 

June 11, 2026

Across 53 darknet marketplaces actively observed between January and April 2026, DarkOwl collected new listings spanning more than 3,200 unique category labels. That fragmentation is not an accident — markets and vendors invent categories independently, which means a listing for methamphetamine might be filed under “Stimulants,” “RC Chems,” “Speed,” “Uppers,” or something else entirely depending on where it’s posted. 

Making sense of that data requires moving past the labels. Rather than treating market-defined categories as meaningful, DarkOwl normalizes every listing into a consistent framework, then aggregates those normalized categories to produce a fingerprint: a profile of what a market actually hosts, expressed as a distribution across standardized categories. 

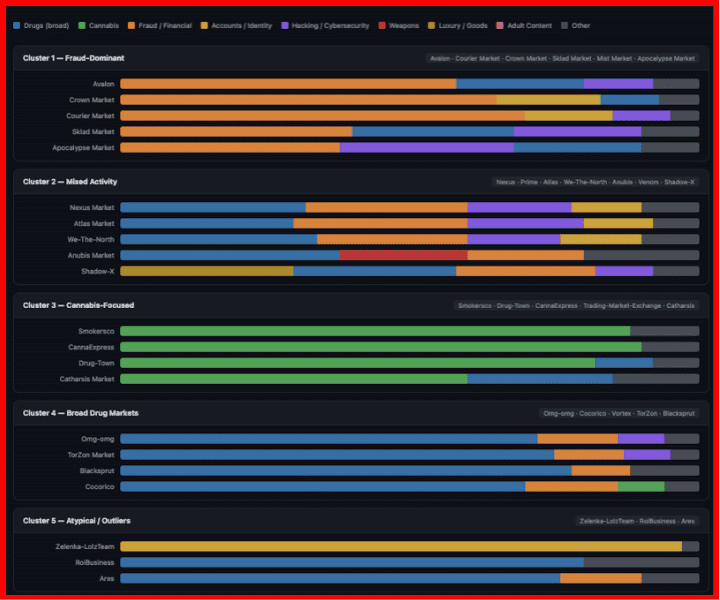
When you compare those fingerprints across the 53 markets active in Q1 2026, five structural groupings emerge. Below, we take a look at these findings. 

First Cluster: Fraud-Dominant Markets 

Avalon, Crown Market, and Courier Market group together because financial fraud, identity documents, and stolen credentials dominate their listing mix — not drugs. Sklad Market, Mist Market, and Apocalypse Market form a related sub-cluster, where fraud remains primary but is accompanied by a substantial hacking and cybersecurity presence. None of these markets are necessarily known by reputation as fraud platforms, but their listing distributions are unambiguous. 

Second Cluster: Mixed-Activity Markets 

Nexus Market, Atlas Market, Prime, and We-The-North maintain roughly balanced distributions across drugs, fraud, hacking tools, and compromised accounts. No single category dominates. Shadow-X occupies this cluster but stands out within it — it carries a notable share of luxury goods that distinguishes its profile from its peers. Anubis Market and Venom are grouped nearby, differentiated by a higher concentration of weapons listings alongside drugs. 

Third Cluster: Cannabis-Focused Markets 

Smokersco, CannaExpress, Drug-Town, and Trading-Market-Exchange group together not because they’re small or inactive but because their category distributions are so concentrated. These platforms sell almost exclusively cannabis — sometimes 85–90% of all listings fall into a single subcategory. Fingerprinting separates them from the broader drug markets precisely because their specialization is so pronounced. A platform that’s 90% cannabis looks nothing like a platform that’s 70% drugs across stimulants, opioids, psychedelics, and other classes. 

Fourth Cluster: Broad Drug Markets 

Omg-omg, TorZon, Blacksprut, Cocorico, and Vortex Market group here — drug listings dominate at 70–80%, with fraud and hacking as secondary categories. These are the markets the ecosystem knows by reputation, and their fingerprints confirm it. 

Fifth Cluster: Atypical Outliers 

Zelenka-LolzTeam hosts almost nothing but gaming accounts and social media profiles — its fingerprint bears no resemblance to any other market in the dataset. RoiBusiness and Ares are drug-focused but have low enough listing volumes that they remain separate from the main drug cluster, making cross-market comparison unreliable without accounting for scale. 

Markets Don’t Stay Still 

The cluster analysis reflects a four-month average, which obscures something important: several markets changed their category composition significantly over the period. Some changes are consistent with normal variation — different vendors posting different volumes in different months. Others are not. 

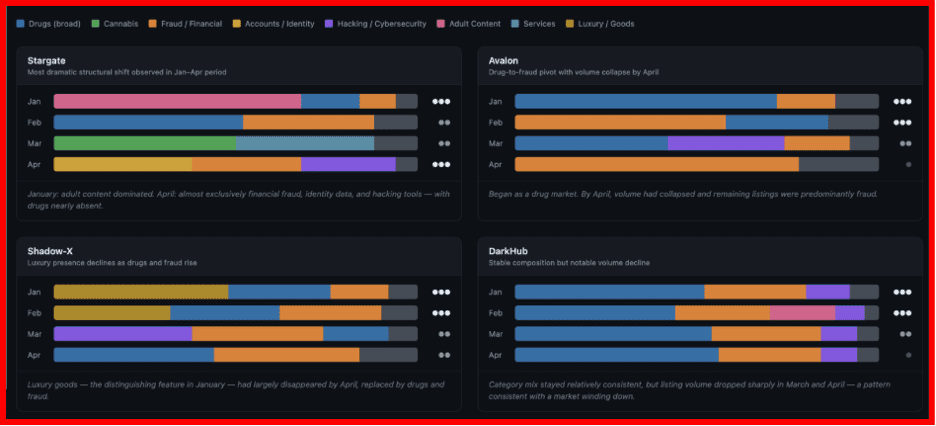
Stargate Market is the clearest example. January listings are dominated by adult content — the platform looks, at first glance, like a niche adult market. By February the adult content has largely disappeared, replaced by drugs and fraud. March shifts again to cannabis and services. By April, financial accounts, identity fraud, and hacking tools dominate, and drug listings have almost vanished. Over four months, Stargate cycled through four structurally different profiles. 

Avalon shows a different trajectory. January is drug-dominant. February brings a sharp increase in fraud. March sees reduced volume with a higher proportion of hacking and cybersecurity. By April, volume is significantly lower, and remaining listings are primarily fraud. The arc is consistent with a platform losing its drug vendor base — through enforcement action, vendor migration, or market reputation decline — with fraud listings filling the remaining activity. 

Shadow-X begins the period with a distinctive luxury goods presence that places it as an outlier within the mixed cluster. That distinguishing feature disappears by April, replaced by the drugs-and-fraud profile that characterizes most of its neighbors. Whatever made Shadow-X distinctive in January was gone by Q2. 

DarkHub shows the opposite pattern: category composition stays relatively consistent across all four months, but listing volume drops sharply in March and April. The mix doesn’t change — drugs and fraud, roughly stable proportions — but the platform is generating far fewer new listings. That’s a different kind of signal: not a change in what’s being sold, but a contraction in who’s selling it. 

Market reputation — what a platform is known for in forums, reviews, or community discussion — is a lagging and often inaccurate indicator of what’s actually being sold. Avalon does not carry a reputation as a fraud market. Its January data wouldn’t suggest one. Its April data is almost entirely fraud. An investigator relying on reputation-based targeting would have the wrong picture of Avalon for much of the year. 

The cluster analysis and temporal tracking together point toward a more reliable approach: compare what a market is really hosting, using normalized categories, against the broader ecosystem. Markets that appear structurally similar to known fraud-dominant platforms are worth treating as fraud-dominant platforms, regardless of what they’re called or how they’re marketed. Markets whose category composition is shifting toward fraud or hacking-focused activity are worth monitoring more closely, because that shift is often a precursor to vendor migration, enforcement attention, or platform collapse. 

When a market does collapse — as happens regularly in darknet ecosystems — its vendor population redistributes. Fingerprinting the collapsed market makes it possible to track that redistribution: look for increases in specific category clusters on other active platforms in the weeks following shutdown. The category signal persists after the market name disappears. 

Analysis based on DarkOwl’s DarkMart dataset, covering 53 active markets and new listings observed from January through April 2026. Category distributions are derived from DarkOwl’s normalized category framework, applied uniformly across all markets including listings without market-defined categories. 


Curious how DarkOwl can do deeper analysis for your company? Contact us.

The Attack Was the Message: The DOJ Indictment and the Operational Model Behind HAYI

June 9, 2026

On May 28, 2026, the U.S. Department of Justice unsealed an eight-count indictment against Mohammad Baqer Saad Dawood Al-Saadi, a dual Iranian-Iraqi national charged with terrorism-related offenses for his alleged role as a senior operative of Kata’ib Hezbollah and Iran’s Islamic Revolutionary Guard Corps (IRGC). The indictment covers nearly 20 attacks and attempted attacks across Europe and the United States, all carried out in the name of Harakat Ashab al-Yamin al-Islamia (HAYI), a group that first emerged publicly in March 2026.

Figure 1: HAYI logo and branding; Source: Foundation for Defense or Democracies

The legal case matters on its own terms. But the more analytically interesting question is what the indictment reveals about how HAYI functioned: not as a standalone terrorist organization, but as a coordinated media-and-operations network allegedly directed by Iranian-aligned actors. DarkOwl began monitoring HAYI’s Telegram footprint in April 2026. Mapping that monitoring against the indictment’s allegations puts several patterns that were already observable at the time into a different light.

Analysis for this blog was conducted using DarkOwl Vision, through targeted tracking of Telegram channels associated with HAYI and the broader Iranian-aligned amplification network.

Al-Saadi, 32, is a dual Iranian-Iraqi national with a career spanning more than a decade inside IRGC-aligned militia networks. According to the DOJ and a detailed CTC Sentinel profile published in May 2026 by Crispin Smith and Michael Knights of the Militia Spotlight platform, he reportedly fought in Syria around 2016 in support of Assad’s forces and returned to Iraq to participate in operations against the Islamic State. Open-source imagery from as early as 2015 shows him operating alongside Iraqi Shia Popular Mobilization Forces and, unusually for someone his age, photographed repeatedly with senior IRGC-Quds Force and militia leadership including Qassem Soleimani.

After his arrest, Al-Saadi waived his Miranda rights and spoke voluntarily to U.S. law enforcement. He described himself as a leader within “the resistance,” a term he used to refer to the IRGC, Kata’ib Hezbollah, Hezbollah, and the Houthis. He said he had been like a son to Soleimani and traveled with him constantly before Soleimani was killed in a U.S. airstrike in January 2020. He also stated he met with Iran’s then-Supreme Leader Khamenei approximately three days before the conflict with Iran began in February 2026.

The CTC authors describe his career as reflecting “rarified trust and access” within Iranian-aligned militant structures. That background matters for understanding how someone allegedly coordinated a multi-country attack-and-media campaign while based in Iraq.

The DOJ alleges Al-Saadi played a significant role in planning, coordinating, and amplifying approximately 18 attacks across Europe conducted in HAYI’s name, including arson attacks, rudimentary bombings, stabbings, and a claimed drone operation targeting the Israeli Embassy in London. Two additional attacks in Canada are also alleged. Prosecutors describe HAYI as “actually a front of Kata’ib Hizballah and other U.S. designated foreign terrorist organizations.”

This is not a standard material support case. The allegations describe a level of operational integration between the attacks themselves and the surrounding media operations that goes well beyond financing or inspiration from a distance. According to prosecutors, Al-Saadi participated in live FaceTime calls with attackers while operations were underway, recorded those attacks, helped produce propaganda videos, and coordinated dissemination in parallel with the attacks themselves.

A video from April 18, 2026, the day of an attack against a synagogue in London, shows Al-Saadi on a FaceTime call projected onto a large screen against the HAYI logo, recording the attack as it happened. A voice on the call directs the attacker to “take a lighter,” “light it,” and “throw the fourth one.”

After his arrest, Al-Saadi told U.S. law enforcement he was “in charge of media and psychological warfare, including against the United States, as well as strategy and military intelligence.” He said HAYI’s propaganda videos were part of the “psychological warfare” the resistance was waging against the United States, designed to “instill fear and terror in civilians.”

His instructions to a Kata’ib Hezbollah contact about distributing attack footage reflect the same logic. In one exchange cited in the indictment, Al-Saadi told the contact that “[t]he most important thing is that within the psychological warfare, they [HAYI’s messages] are useful,” and that “anything that distracts the enemy is useful.”

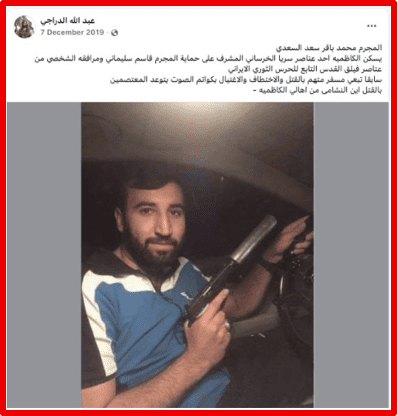
Figure 2: Arrested senior officer of Kata’ib Hezbollah (December 2019 Facebook post accusing al-Saadi of assassination against protesters, reposting an image shared by al-Saadi himself in May 2018); Source: CTC West Point

Most public attention has focused on the European attack campaign, but the indictment also documents Al-Saadi’s alleged efforts to bring the campaign to the United States.

Prosecutors allege that in March and April 2026, Al-Saadi worked to arrange attacks in the United States, including against a synagogue in New York City. On April 30, 2026, the day before his detention while traveling in Turkey, he called an individual in the United States and asked whether that person knew “someone who could ‘attack’ in the United States, including by ‘burning, . . . or whatever he can,’ including ‘killing.’” He was detained the next day.

That attempted expansion fits with what Al-Saadi told investigators about his broader objectives. He described “the resistance” as waging psychological warfare specifically against the United States, and the geographic scope of HAYI’s claimed attacks had been moving steadily from Europe toward North America over the course of the operation.

DarkOwl began monitoring HAYI-linked activity in April 2026 as attack claims circulated across Telegram. Our April 16 analysis raised the question of whether HAYI was a distinct organization or a node within a broader network. Several findings from that monitoring connect directly to what the indictment now alleges.

  • Al Faqaar as a structured amplification node. DarkOwl identified the Al Faqaar Telegram channel as consistently publishing HAYI-attributed content before or alongside the group’s own channels. At the time, we noted it functioned “similarly to established IRGC-aligned media outlets such as Sabereen News, acting as an early dissemination node.” The indictment now alleges that Al-Saadi instructed his Kata’ib Hezbollah (KH) contact to post attack footage “in the news, important” and coordinated directly on which channels to use and when. The distribution pattern DarkOwl tracked was not organic reposting. It fits the picture of structured, upstream direction.
  • The Sabereen News watermark. Our April 16 analysis also found Sabereen News branding within video content reposted by HAYI-affiliated channels, pointing to “participation in a shared media pipeline where content is reused and redistributed across channels.” The indictment’s allegations about Al-Saadi coordinating directly with KH propagandists on media timing and channel selection offer a plausible account of how that pipeline worked.
  • April 29, London. In our April 29 post, DarkOwl documented Al Faqaar’s near-real-time coverage of the London stabbing of two Jewish men, including a dual U.S.-British citizen. Al Faqaar published a text-only alert at 0500 MST, followed by attack footage, arrest footage, and a final branded video by 0830 MST. We noted at the time that the speed and structure of the media response suggested the incident was “either anticipated or quickly incorporated into a broader narrative framework.” The indictment shows what was allegedly happening on the other end: that same day, Al-Saadi told his KH contact to post the attack footage (“post it in the news, important”) and sent a message about a planned restaurant shooting for that evening. He was detained the following morning. DarkOwl was tracking the media operation in near-real time while Al-Saadi was allegedly running it.
  • A note on Russian-linked amplification. DarkOwl’s monitoring of the Axis of Resistance channel network identified that two of the four primary Telegram channels distributing HAYI content appear to have ties to sanctioned Russian networks. Whether this reflects deliberate coordination between Iranian and Russian information operations infrastructure, or parallel amplification by actors pursuing compatible objectives, remains an open question. It is a thread that warrants continued monitoring given the broader context of Iranian-Russian strategic convergence since February 2022.
  • The “lone wolves” framing reconsidered. The April 29 analysis noted that the final video from the London stabbing framed the attackers as “lone wolves” and observed that this language “may reflect a deliberate strategy that allows groups to claim or amplify attacks while maintaining plausible deniability.” The indictment supports that reading. According to prosecutors, the deniability language in HAYI’s public messaging ran alongside direct tactical coordination, including real-time FaceTime calls during attacks. The two were not in tension. They were apparently by design.

The analysis in CTC Sentinel characterizes HAYI as bearing “all the hallmarks of a muqawama ‘façade group’ operation, in which an online brand is used to partially conceal the real-world identity of an Iranian-aligned attacker.” The authors document that Al-Saadi sent HAYI’s launch statement and associated iconography via his Snapchat account more than four hours before it circulated publicly, indicating, as they put it, “his advanced and insider knowledge of HAYI’s operations.”

That finding tracks with what DarkOwl observed. In our April 16 analysis, we described HAYI as “best understood as part of a broader ecosystem in which content is circulated, repurposed, and reinforced across multiple actors” and noted that “attribution becomes less about identifying a single origin point and more about understanding how narratives move across channels.” HAYI’s primary Telegram channel was removed or banned by early April, but content continued moving through Al Faqaar, Safee al-Deen, and affiliated channels. The indictment suggests that continuity was structural from the beginning, with centralized direction continuing regardless of which channel was carrying the content at any given time.

HAYI was not, according to prosecutors, a spontaneous movement that KH later amplified. The branding, messaging, and distribution were managed upstream from the start.

In Al-Saadi’s own account, as alleged by prosecutors, propaganda was not something that happened after an attack. It was part of the attack. “Psychological warfare” was described as a strategic objective, sitting alongside kinetic operations. Attack footage was reviewed, curated, timed, and sent to specific channels. The same person allegedly directing FaceTime calls during attacks was also coordinating which Telegram accounts received the footage and when.

The Institute for Strategic Dialogue (ISD) has characterized this type of approach as consistent with a potential “violence as a service” model, where individuals may be recruited, inspired, or financially incentivized to conduct attacks that are then amplified through a broader media network. The DOJ allegations add specificity to that framework: recruitment of local criminals (frequently minors, according to court documents, with at least one recruit offered €600 via Snapchat), real-time tactical coordination via video call, payments made via cryptocurrency and ZainCash, and propaganda production and distribution run through the same command structure as the attacks themselves.

This creates real problems for attribution and disruption. A decentralized channel network built around a disposable front brand lets organizing actors benefit from the psychological effects of violence while keeping distance from the individuals carrying out attacks. The deniability framing visible in HAYI’s public messaging was not a gap in the model. According to the indictment’s allegations, it was part of the design.

  • Tracking the amplification network matters as much as tracking the primary brand. HAYI’s own channel was banned in early April. Its operational footprint stayed visible through Al Faqaar, Safee al-Deen, Sabereen News, and affiliated channels. In this model, monitoring the distribution layer is as important as monitoring the group itself.
  • Rapid media response can be a signal, not just noise. HAYI’s near-real-time output after attacks could be read as unsophisticated or opportunistic. The indictment points in the other direction: that speed reflected upstream coordination.
  • The “Lone wolf” framing should be treated as a narrative choice, not an analytical conclusion. The deniability language in HAYI’s messaging was visible before the indictment. Prosecutors now allege it ran alongside direct tactical direction of attacks in real time.
  • Propaganda channels and attack planning may share a command structure. Al-Saadi is alleged to have managed both simultaneously. Monitoring media production and distribution may provide as much operationally relevant signal as monitoring attack planning activity directly.
  • The model is transferable. Front branding, recruited or inspired attackers, real-time coordination, and rapid media amplification require fewer resources and expose fewer operatives than traditional terrorist infrastructure, while potentially generating outsized psychological impact. If it continues to prove effective, other actors are likely to adopt it.

The indictment offers a rare look inside a structure where violence and media amplification were apparently run as a single operation. The question it raises is not just who carried out a given attack, but how the surrounding channel network was built to turn that violence into narrative impact.

Much of what the indictment now alleges as fact was already partially visible in HAYI’s Telegram footprint: in Al Faqaar’s distribution patterns, in the Sabereen News watermarks embedded in attack footage, in the speed and coherence of the media response to the London stabbing on April 29. The indictment adds prosecutorial detail to patterns that DarkOwl’s monitoring had already flagged.

Recent academic research on HAYI, including work cited by the Combating Terrorism Center at West Point, has drawn on DarkOwl’s prior analysis of the group’s Telegram footprint and its relationship to the broader Iranian-aligned network. The Al-Saadi case makes clear why that kind of monitoring matters, and why the channel networks surrounding these operations deserve as much analytical attention as the operations themselves.

DarkOwl continues to monitor how this model evolves and whether it inspires adoption by other state-aligned actors or extremist networks. The case against Al-Saadi is one data point in what may be a longer trend toward operational structures that treat media amplification and physical violence as inseparable. How other groups respond to that example, and whether the model proves durable after a high-profile arrest, will be worth watching closely.

U.S. Department of Justice, SDNY. Dual Iranian-Iraqi National Indicted For Providing Material Support To Terrorist Organizations. May 28, 2026. 

Smith, Crispin and Michael Knights. Mohammad Baqer al-Saadi: Profiling an IRGC and Iraqi Militia Operative. CTC Sentinel, May 2026. 

Fiennes, Guy. Islamic Movement of the Companions of the Right: The ‘Gig-Economy’ Proxy Group Attacking Europe. ISD Digital Dispatch, April 30, 2026 (updated May 15, 2026).


Check out our other recent blogs on Harakat Ashab al-Yamin al-Islamia and Handala.

Darknet Market Vendor Analysis 

Of the 7,314 vendors active on darknet markets between January and April 2026, more than 2,000 posted exactly one listing. Another 1,000+ posted only two. The distribution has a long tail: the vast majority of accounts are transient, low-volume, and individually uninformative. They appear and disappear without accumulating enough activity to characterize. 

This is the baseline condition of darknet vendor data. Most of it is noise. What’s operationally useful is concentrated in a smaller population of high-activity sellers whose behavior is sustained enough to analyze — and whose patterns persist across migrations, rebranding, and platform shifts. 

Among the 285 vendors who posted more than 50 new listings during the period, two findings stand out. 

The first finding is about specialization. Drug vendors, in aggregate, are more narrowly focused than any other vendor category. Cannabis sellers are the extreme case: most concentrate 90% or more of their activity in cannabis listings, with almost nothing else. Stimulant specialists and opioid specialists are nearly as concentrated — a vendor who sells stimulants rarely sells psychedelics or opioids at meaningful volume, even within the broader drug category. 

This pattern is analytically useful. A cannabis vendor with 200 listings is maximally exposed in a single product category. Their profile is easy to recognize, easy to track across platforms, and easy to distinguish from vendors who happen to have a few cannabis listings alongside other inventory. 

Broad-spectrum drug vendors — those distributing activity across stimulants, opioids, psychedelics, and other subcategories — exist but are less common. When they appear, the diversity itself is a signal. Vendors who source across multiple drug classes typically operate at larger scale or have more diversified supply chains than single-substance specialists. 

Fraud vendors look structurally different. The typical high-activity fraud vendor spreads across financial instruments, identity documents, compromised accounts, and sometimes hacking tools within the same portfolio. This breadth is consistent with organized operations that source across multiple pipelines — not a single individual with a specific product, but a coordinated set of supply relationships. An investigator treating a fraud vendor the same way as a drug vendor — looking for a narrow category concentration — will misread the profile. 

The second finding concerns identity. Darknet vendors routinely reuse usernames across platforms, and other vendors independently register identical names on markets where those names aren’t taken. The result is that a username, on its own, is an ambiguous identifier. 

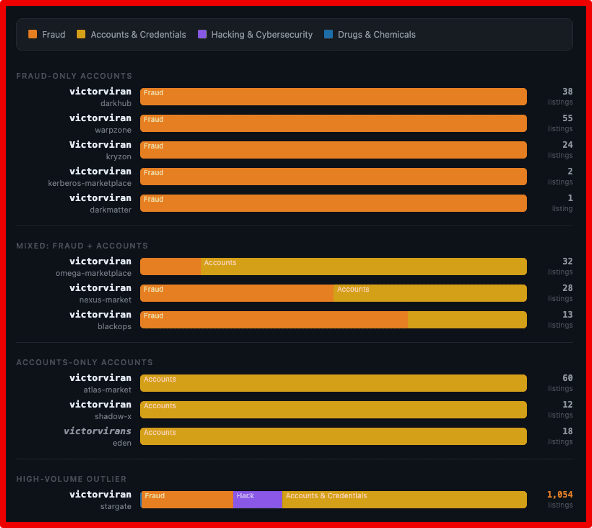
The username victorviran appears on eleven markets during the January–April period. It’s an instructive example because the behavioral divergence across those eleven accounts is stark. 

Three of the accounts — on WarpZone, Atlas Market, and Nexus Market — show nearly identical fingerprints: almost entirely accounts and credentials, with minimal activity in other categories. The structural similarity across platforms is too close to be coincidental. These accounts are plausibly the same operator maintaining parallel presence on multiple markets. The Stargate account bearing the same name has expanded its profile to include hacking tools alongside credentials — either an evolution of the same operation or a closely related actor. 

Then there are accounts with the same name selling primarily financial fraud, with no meaningful overlap with the credentials-focused accounts. And at least one victorviran account whose listings are drugs. The profile bears no resemblance to the others. 

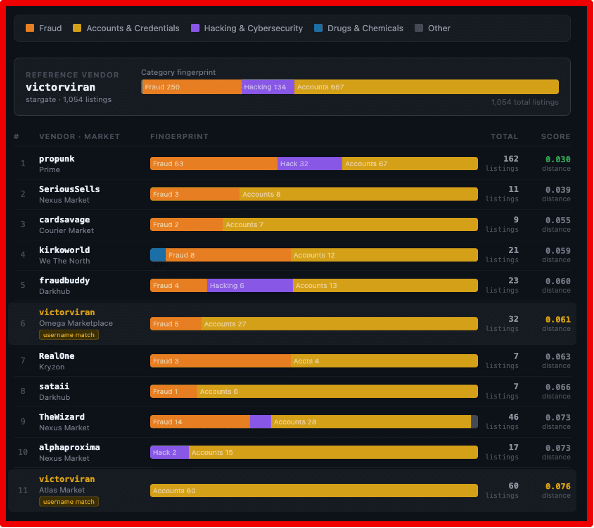
The inverse of this problem is equally significant, and in some ways more useful to investigators. Different vendors operating under different names can produce nearly identical fingerprints — the same category distribution, the same subcategory emphasis, similar listing volumes. When a vendor migrates from a collapsed market to a new platform under a new username, the fingerprint often follows. 

This is where similarity search across markets becomes operationally relevant. Starting from a known vendor profile — say, a confirmed drug distributor on a market that has since shut down — you can compute fingerprint similarity across all vendors on currently active markets and surface accounts whose behavioral profiles closely match. The name is different. The behavior is not. 

In the victorviran similarity network, the most closely matching profiles include accounts that share the username. But they also include accounts that don’t. The fingerprint search finds both, and the username search alone would miss the latter entirely. 

The operational framing matters here. Fingerprints are a similarity signal, not an attribution mechanism. Two vendors with identical category distributions are not necessarily the same person. But vendors with highly similar fingerprints, appearing on different platforms in overlapping time windows, are worth treating as related until evidence suggests otherwise. The alternative — treating every new username as a new actor — understates continuity in an ecosystem where continuity is deliberately obscured. 

The specialization patterns matter too. A vendor who is 95% cannabis is not a general drug distributor who happens to sell cannabis. They’re a cannabis-specific operator, and their investigative profile should reflect that. A fraud vendor who combines identity documents, financial instruments, and hacking tools in a single portfolio is not an opportunistic individual seller — the breadth implies supply chain access that a single person doesn’t typically have. 

Seven thousand vendors is too many to work through manually. Fingerprint-based clustering reduces that population to meaningful groups: the cannabis specialists who cluster together by behavior, the credentials vendors who look similar across platforms, the broad-spectrum fraud operations that stand apart from everything else. The 285 high-activity vendors are not representative of the 7,314 — they’re a different kind of actor and analyzing them as a separate population surfaces patterns that the full dataset obscures. 

Analysis based on DarkOwl’s DarkMart dataset, covering 7,314 active vendors across 53 markets from January through April 2026. Vendor fingerprints are derived from normalized category distributions across all listings associated with each vendor during the period. High-activity vendors are defined as those with 50 or more new listings during the observation window. 


Curious to learn more about dark web monitoring? Contact us.

Threat Intelligence RoundUp: May

June 01, 2026

Our analyst team shares a few articles each week in our email newsletter which goes every Thursday. Make sure to register! This blog highlights those articles in order of what was the most popular in our newsletter – what our readers found the most intriguing. Stay tuned for a recap every month. We hope sharing these resources and news articles emphasizes the importance of cybersecurity and sheds light on the latest in threat intelligence.

1. Instructure hacker claims data theft from 8,800 schools, universities – Bleeping Computer

New posts on ShinyHunters data leak site reveal the threat group allegedly has breached the education technology company Instructure. The group has claimed to have stolen 280 million records connected to students and staff from over 8K colleges, school districts, and online education platforms. Using Canvas data export feature ShinyHunters was able to harvest “hundreds of gigabytes of user records, messages, and enrollment data”. According to the data leak site, ShinyHunters extended their deadline until May 12, claiming some of the affected institutions were engaging with the group. Read full article.

2. 15-year-old detained over French govt agency data breach – Bleeping Computer

French authorities have detained a 15-year-old suspect in connection to the cyberattack on France Titres (ANTS). Using the alias “breach3d”, the suspect was selling between 12 to 18 million records stolen from the ANTS data breach. The minor faces charges for “unauthorized access, persistence, and data exfiltration from a state-run automated personal data processing system, as well as for possession of software that enables the offenses.” These charges carry a maximum sentence of 7 years in prison and a fine of 300K euros. Article here.

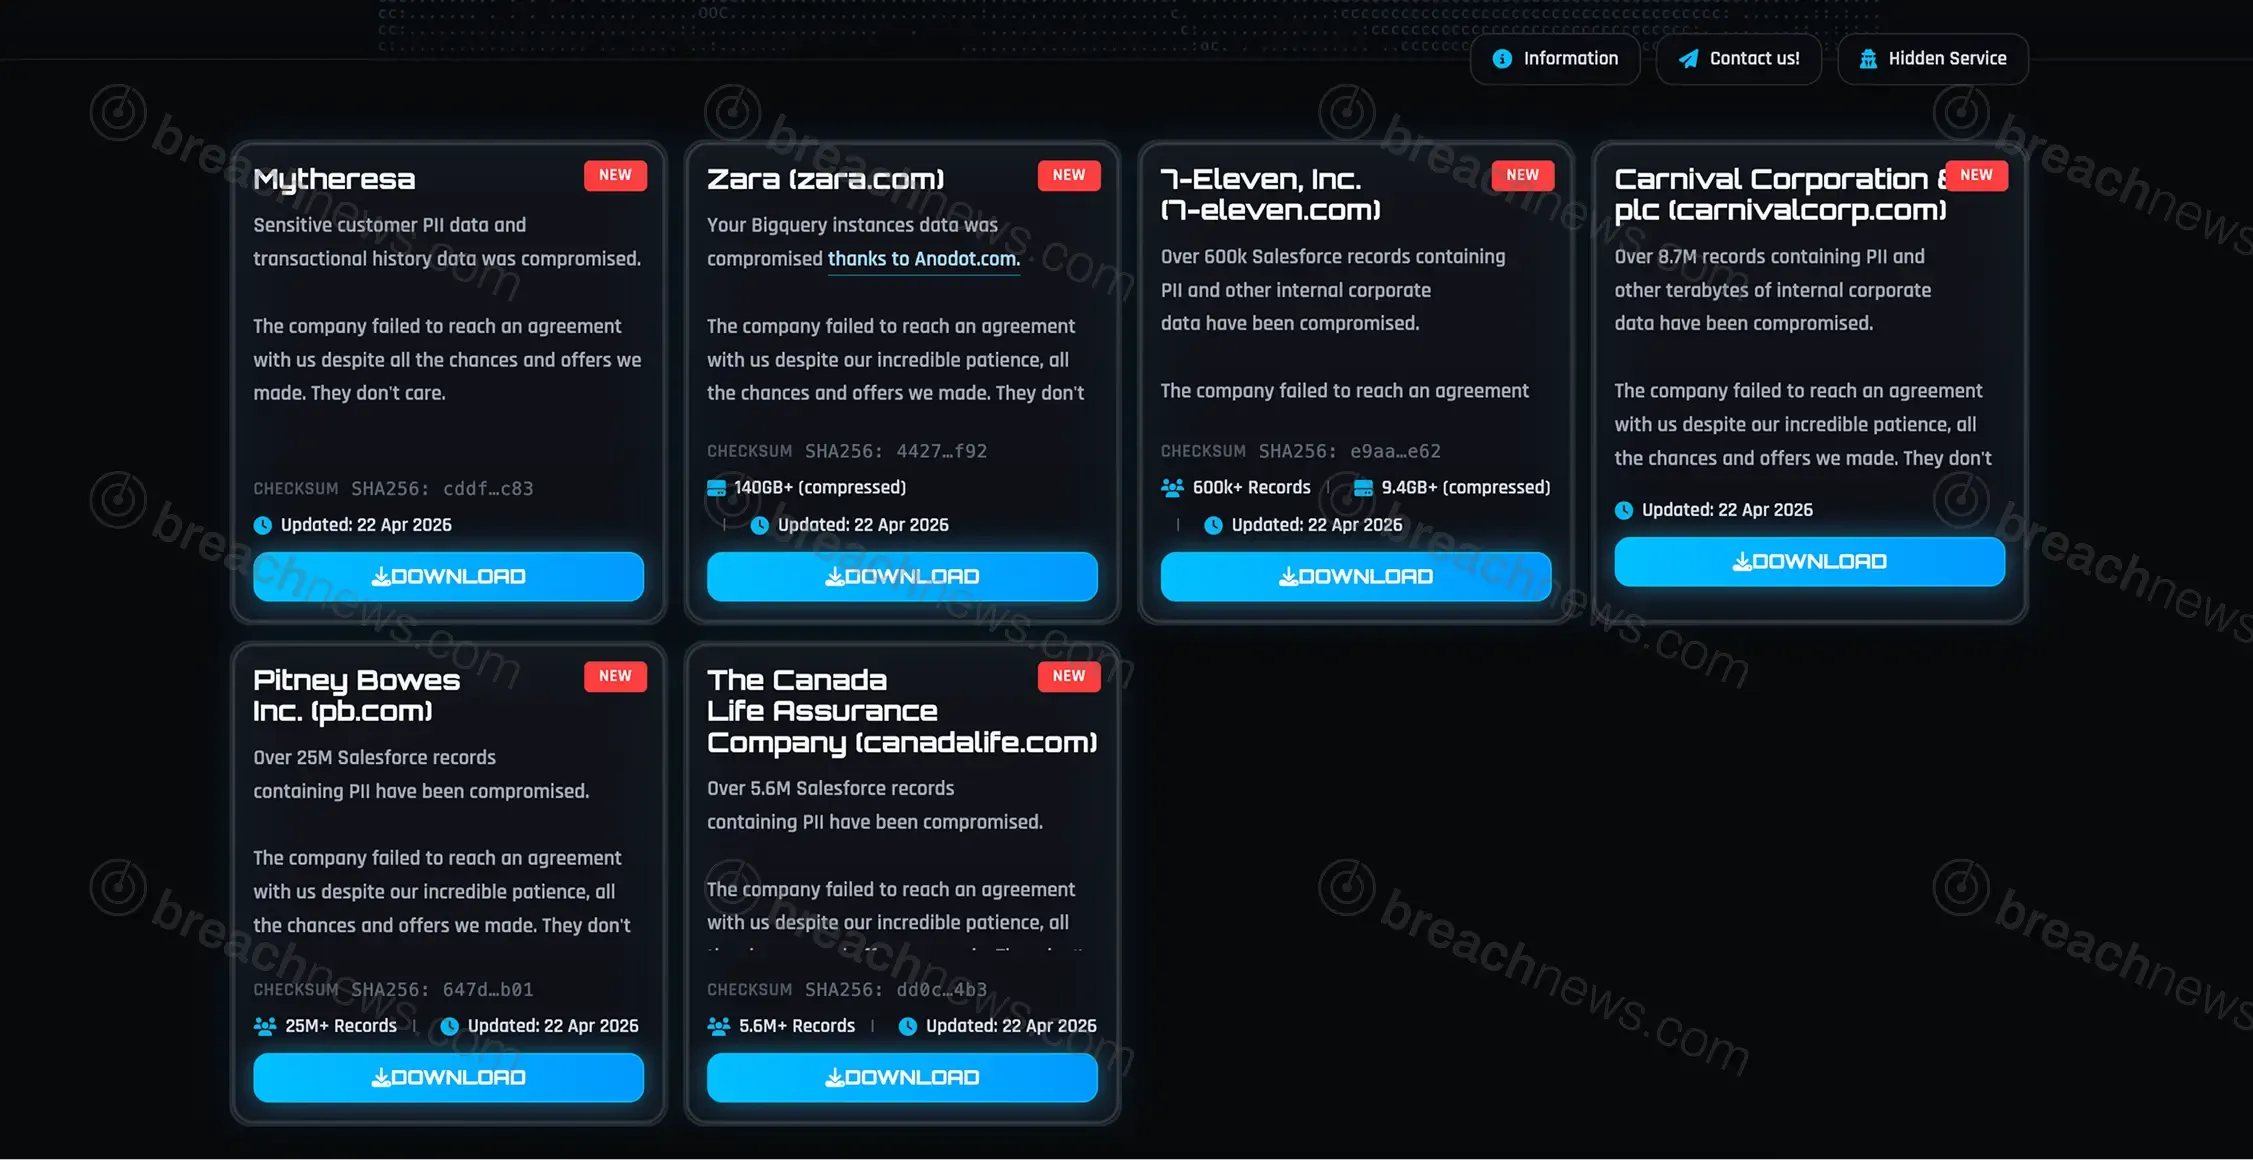
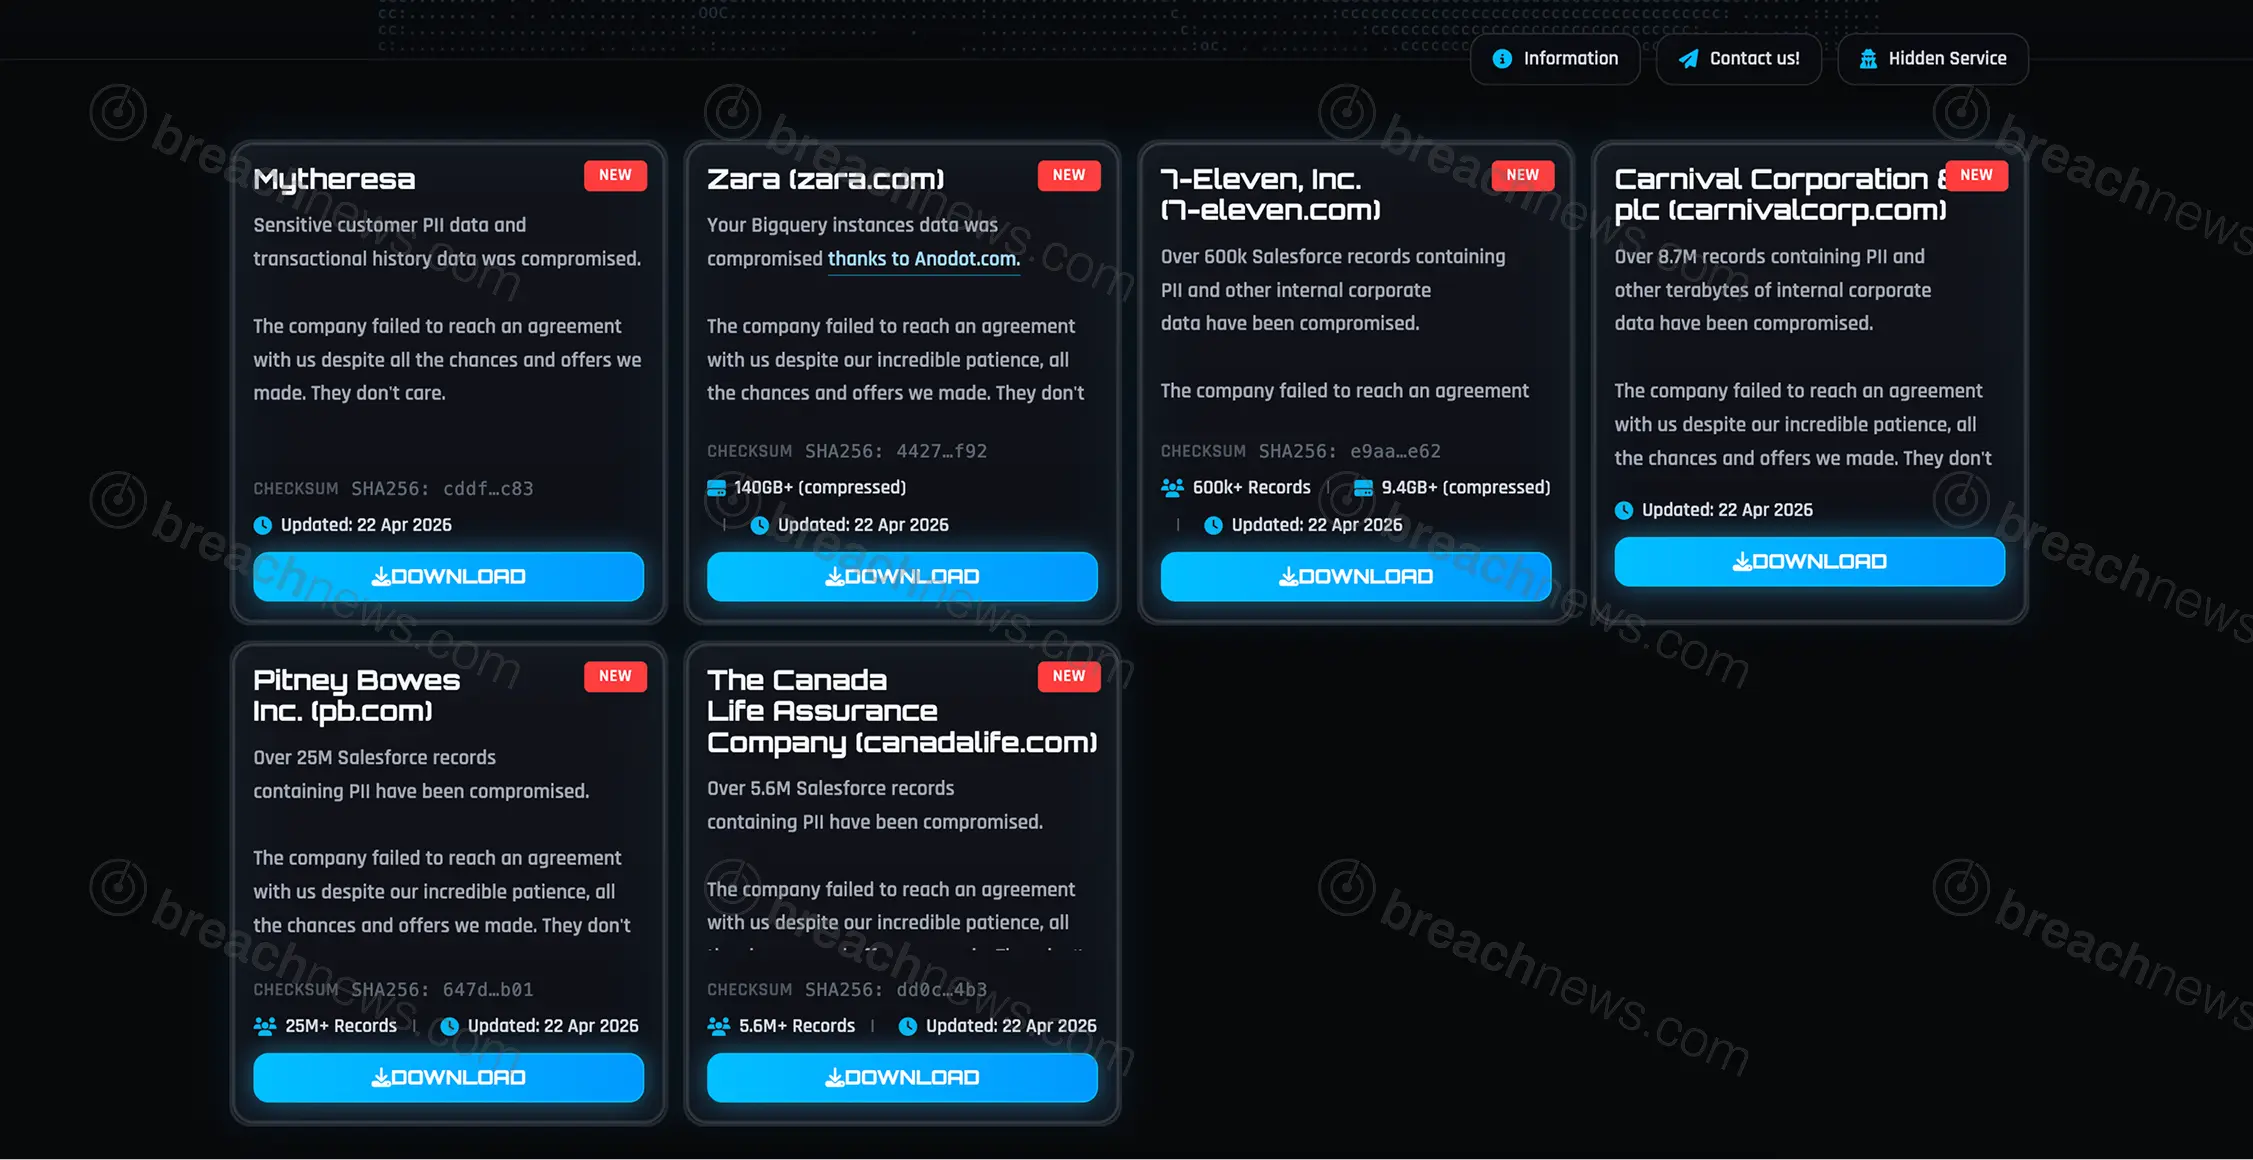
On April 22, ShinyHunters released data belonging to multiple organizations including Carnival Corporation, Zara, 7-Eleven, Pitney Bowes, and more. Several of the organizations are associated with the groups previous compromise of Salesforce environments. The site claims each company “failed to reach an agreement” leading to ShinyHunters releasing their data. The datasets are said to include a combination of personally identifiable information, transaction records, and internal corporate data. In multiple instances, ShinyHunters highlighted Salesforce-related records, reinforcing a pattern seen in earlier campaigns linked to misconfigured cloud environments. Read more here.

A repository that briefly reached #1 on Hugging Face platform was found delivering information-stealing malware to Windows users. “The repository had typosquatted OpenAI’s legitimate Privacy Filter release, copied its model card nearly verbatim, and shipped a loader.py file that fetches and executes infostealer malware on Windows machines,” states HiddenLayer’s Research Team. The ‘loader.py’ script was designed to look innocent, but behind the scenes, it bypassed security checks, contacted a hidden external server, and ran unauthorized commands on the system. The repository was downloaded over 200K times before being removed. Read here.

5. China-Linked Hackers Target Asian Governments, NATO State, Journalists, and Activists – The Hacker News

China-linked hackers have conducted an espionage campaign against government and defense sectors in South, East, and Southeast Asia, as well as a European NATO member. Sharing network overlap with CL-STA-0049, Earth Alux, and REF7707, the threat cluster is being tracked as “SHADOW-EARTH-053”. This group takes advantage of known, already-patched vulnerabilities in internet-facing Microsoft Exchange and IIS servers to gain initial access. Once inside, they install web shells (GODZILLA) to maintain control over the system. They then deploy more advanced malware, such as ShadowPad, using DLL sideloading techniques that hide malicious code inside legitimate, signed programs. Learn more.

6. GlassWorm malware attacks return via 73 OpenVSX “sleeper” extensions – Bleeping Computer

The Glassworm campaign has begun targeting the OpenVSX ecosystem with 73 “sleeper” extensions that become “malicious after an update”. Socket researchers claim 6 of the extensions have been activated and deliver malware, with the other 67 are currently dormant. The latest wave indicates a shift in the attacker’s approach. Instead of embedding malicious code directly within extensions, they first submit seemingly harmless versions to a single ecosystem, then introduce the malicious payload in a later update. Socket also found that the 73 extensions involved in the most recent GlassWorm campaign are clones of legitimate listings, intended to deceive developers who rely primarily on visual cues rather than closely examining the details. Read full article.

7. Azerbaijani Energy Firm Hit by Repeated Microsoft Exchange Exploitation – The Hacker News

FamousSparrow, a Chinese affiliate threat group, has been linked to a “multi-wave intrusion” targeting an Azerbaijani oil and gas company from December 2025 to February 2026. Leveraging a vulnerable Microsoft Exchange server the threat actor was able to swap backdoors during each re-entry. The attack enabled the staged deployment of two separate backdoors across three infection waves: Deed RAT (also known as Snappybee), a ShadowPad successor leveraged by several China-linked espionage groups, and TernDoor, a malware strain recently identified in campaigns targeting telecommunications infrastructure in South America. Read full article.

8. US charges suspected Dream Market admin arrested in Germany – Bleeping Computer

The main administrator of the now defunct darknet marketplace, Dream Market, has been indicted by a federal grand just on money laundering charges. Owe Martin Andreson was charged with “six counts of international concealment money laundering and six counts of concealment money laundering” and with each charge having a possible 20-year prison sentence. Operating under the handle, “Speedstepper”, Andresen accessed dormant Dream Market wallets and moved millions of dollars to other accounts. German authorities have arrested Andresen and charged him with additional charges of concealment money laundering. The DOJ claims that in total Andresen is “alleged to have laundered over $2 million between August 2023 and April 2025.” Learn more.


Make sure to register for our weekly newsletter to get access to what our analysts are reading on a weekly basis.

Social Engineering in 2026: When Deception Stops Looking Suspicious

May 27, 2026

For years, social engineering followed a familiar pattern. The messages were generic, the grammar was questionable, and the urgency often felt forced. Most organizations trained their people to look for those signs, and for a while, that worked.

That version of social engineering still exists. It just isn’t what’s working anymore.

What has changed is not the goal, but the execution. Social engineering has shifted from isolated attempts at deception to a more refined, scalable, and deeply contextual approach. The result is something far more difficult to detect, not because it is more aggressive, but because it feels normal.

The original discussion in DarkOwl’s breakdown of social engineering trends focused on the foundations of deception. Today, those foundations are being layered with automation, intelligence, and precision in ways that remove the very signals defenders were trained to rely on.

Attackers are no longer guessing. They are building context.

Information pulled from previous breaches, public profiles, and even internal organizational structures is being used to craft messages that reflect real relationships and real work. Instead of broad outreach, the focus is on relevance. A message might reference a current project, a colleague, or a routine process that the recipient recognizes immediately.

This shift matters because it removes hesitation. When something looks familiar, it is far less likely to be questioned.

For a long time, poor grammar and awkward phrasing were reliable indicators of phishing attempts. That signal has largely disappeared.

AI-generated communication has raised the baseline quality of social engineering. Messages are now clear, structured, and context-aware. More importantly, they can evolve. Attackers are no longer limited to a single message. They can sustain conversations, respond in real time, and adapt their tone based on how the target engages.

The absence of obvious mistakes does not indicate legitimacy anymore. It simply reflects the tools being used.

Social engineering is no longer confined to one channel. It often unfolds as a sequence.

An email might introduce the request, followed by a text message that reinforces urgency, and then a message in a collaboration platform that makes the interaction feel internal. In some cases, a phone call completes the chain, adding a human element that builds trust.

Each step supports the next. By the time a request is made, it no longer feels like an isolated interaction. It feels like part of an ongoing conversation.

Impersonation has also evolved. It is no longer limited to copying a name or an email address.

With minimal source material, attackers can replicate voices and, in some cases, create convincing video interactions. This is particularly effective in environments where quick decisions are expected, and verification processes are informal. A familiar voice, paired with urgency, is often enough to override hesitation.

The difference now is not just who attackers claim to be, but how convincingly they can present that identity.

One of the more subtle shifts is how attackers are interacting with security controls themselves.

Rather than bypassing protections like multi-factor authentication, they are manipulating user behavior around them. Repeated approval requests, well-timed prompts, and framing actions as routine system activity all create pressure to comply.

What was designed as a safeguard becomes part of the attack path. The decision is no longer technical. It is behavioral.

At its core, social engineering has always relied on human response. What has changed is the level of precision behind it.

Instead of broad emotional triggers, attackers are aligning their approach with the context of the target. A finance employee may receive a time-sensitive payment request, while someone in HR might see a message framed around employee issues. The tone, timing, and framing are chosen intentionally.

These interactions are designed to feel appropriate, not alarming. And that is what makes them effective. The triggers themselves are familiar:

  • Urgency – often tied to deadlines or financial transactions
  • Authority – presented through executive or leadership requests
  • Curiosity – framed as internal documents or updates
  • Empathy – commonly used in HR or personal scenarios

These are not new concepts. What is new is how accurately they are applied.

Attackers are not operating in isolation. Techniques that work are shared, refined, and reused.

Across darknet communities, successful approaches are discussed openly. Messaging templates, engagement strategies, and bypass techniques circulate quickly, allowing others to replicate and improve them. This creates a cycle where effective methods do not stay niche for long.

Social engineering is no longer just a tactic. It is an evolving system.

The most important change is not the technology being used. It is the disappearance of friction.

Older attacks relied on the target making a mistake. Modern attacks are designed to feel like the correct action. They align with expectations, mimic normal workflows, and remove the cues people were trained to question.

That makes detection less about spotting something obviously wrong and more about recognizing when something is subtly off.

And that is a harder skill to teach.

As social engineering continues to evolve, the challenge is no longer just awareness. It is adaptation. Because the most effective attacks are no longer the ones that look suspicious.

They are the ones that don’t.


Stay tuned for best practices. Follow us on LinkedIn.

What are Basic Web Application Attacks?

May 21, 2026

Cybersecurity might as well have its own language. There are so many acronyms, terms, sayings that cybersecurity professionals and threat actors both use that unless you are deeply knowledgeable, have experience in the security field or have a keen interest, one may not know. Understanding what these acronyms and terms mean is the first step to developing a thorough understanding of cybersecurity and in turn better protecting yourself, clients, and employees. 

In this blog series, we aim to explain and simplify some of the most commonly used terms. Previously, we have covered bullet proof hosting, CVEs, APIs, brute force attacks, zero-day exploits, doxing, data harvesting, IoCs, credential stuffing, ransomware as a service, and push bombing. In this edition, we dive into basic web application attacks.

A basic web application attack is an attempt to exploit vulnerabilities in a website or web app to gain unauthorized access, steal data, or disrupt service.

As organizations continue to migrate their operations to the cloud and rely heavily on web-based interfaces, the surface area for potential cyber threats has expanded significantly. Web applications power everything from online banking to internal business tools. Without proper fortification, they remain primary targets for malicious actors. Attackers are focusing their efforts on exploiting the applications themselves. Basic web application attacks are some of the most common methods threat actors use to compromise systems, steal data, and gain unauthorized access – and they don’t have to be complex. They exploit vulnerabilities in the application’s code, logic, or database connections.

These attacks often exploit vulnerabilities outlined by organizations like the OWASP, which tracks the most critical web security risks. The goal of these attacks varies, ranging from the theft of sensitive customer data and intellectual property to the total takeover of the administrative backend.

Understanding the fundamental methods attackers use to compromise these systems is the first step in building a resilient security posture. While there are dozens of techniques, let’s review the most common:

  • SQL Injection (SQLi): The attacker targets the server’s database and inserts malicious SQL code into an input field (like a login form or search bar). If the application does not properly sanitize this input, the malicious code is executed by the backend database, allowing the attacker to query, modify, or delete data directly from the database.
  • Cross-Site Scripting (XSS): The attacker targets the application’s users and injects malicious JavaScript into a webpage that other users then load. When a victim visits the compromised page, their browser executes the script, which can be used to steal session cookies, log keystrokes, hijack account credentials, or redirect the user to a fraudulent website. This works when applications don’t properly validate or escape user-generated content.
  • Broken Access Control: Access control ensures that users cannot act outside of their intended permissions. A failure in these controls—such as allowing a standard user to access an administrative URL or view another user’s private files—is known as Broken Access Control. This is a critical vulnerability that often leads to unauthorized information disclosure and data modification.
  • Broken Authentication: An attacker exploits weak passwords, session tokens, or login mechanisms to impersonate legitimate users — often through credential stuffing or brute force. This is made possible by oor password policies, lack of MFA, or predictable session tokens.
  • Cross-Site Request Forgery (CSRF): Attackers trick a logged-in user’s browser into making an unwanted request to a site they’re authenticated on. For example, while a user is authenticated in their banking app, they might click a malicious link in a different tab that triggers a hidden request to transfer funds. Because the user is already authenticated, the web application treats the request as legitimate. This can happen when applications trust requests from authenticated sessions without verifying their origin.

Basic web application attacks continue to persist and are so effective because they exploit fundamental weaknesses that are common across many organizations. Every internet-facing application represents a potential target for attackers, significantly expanding the available attack surface. Many of these attacks are also relatively simple to execute, often requiring minimal tooling and allowing threat actors to automate exploitation at scale. Despite their simplicity, the impact can be severe—even a single vulnerability may expose sensitive databases, compromise user accounts, or disrupt critical services. In many cases, these risks are amplified by human and development-related factors, including rushed deployment timelines, misconfigurations, and the absence of secure coding practices throughout the software development lifecycle.

Most web application attacks follow a predictable lifecycle that allows threat actors to efficiently identify and exploit vulnerabilities. The process typically begins with reconnaissance, where attackers scan applications for exposed endpoints, login forms, APIs, and user input fields that may reveal potential weaknesses. Once areas of interest are identified, attackers move into vulnerability identification by testing inputs and application behavior for flaws such as injection points or insecure configurations. After discovering a viable weakness, the exploitation phase begins, during which attackers execute the attack by injecting malicious code, bypassing authentication controls, or hijacking user sessions. Successful exploitation is often followed by post-exploitation activity, including data exfiltration, privilege escalation, lateral movement, or establishing persistence within the environment. Because this process is structured and repeatable, web application attacks can be easily scaled across large numbers of targets.

The consequence of a successful web application attack includes: technical downtime, account takeover, data breaches, reputation damage, and financial loss.

Equifax

One of the most well-known examples of a web application attack occurred in 2017, when attackers exploited a vulnerability in the Apache Struts web application framework used by Equifax. The flaw allowed remote code execution through a vulnerable web application component. The breach exposed personally identifiable information (PII) of ~147 million individuals, including names, social security numbers, and birth dates. The incident highlighted how unpatched web application vulnerabilities can become entry points for large-scale data breaches.

Progress Software

In 2023, attackers exploited a SQL injection vulnerability in the MOVEit Transfer managed file transfer platform, allowing unauthorized access to sensitive data stored by thousands of organizations worldwide. The vulnerability was leveraged by the Clop ransomware group to extract data from government agencies, healthcare providers, universities, and financial institutions. The campaign ultimately impacted more than 2,000 organizations and exposed the data of nearly 100 million individuals, demonstrating how a single web application flaw can create widespread downstream impact.

Microsoft

In 2024, researchers identified a serious cross-site scripting (XSS) vulnerability in on-premises deployments of Microsoft Dynamics 365. The flaw allowed attackers to inject malicious JavaScript into application pages through improperly sanitized input fields. If exploited, attackers could execute scripts within victim browsers, potentially leading to session hijacking, credential theft, or unauthorized actions performed under legitimate user accounts. The incident reinforced that XSS remains one of the most persistent and commonly exploited web application vulnerabilities.

In many cases, it’s not advanced techniques that cause the most damage— it’s the fundamentals done poorly. To defend against a web application attack, organizations need to reduce risk with a combination of secure development practices and defensive controls:

  • Input Validation and Sanitization: Never trust user input—validate and sanitize everything. Implement strict validation rules to ensure only the expected data types are processed.
  • Use Parameterized Queries: Prevent SQL injection by separating code from data. Using parameterized queries (prepared statements) is the most effective way to prevent SQL injection.
  • Implement Output Encoding: Protect against XSS by properly escaping content. A strong CSP (Content Security Policy) can significantly reduce the risk of XSS by restricting the sources from which scripts can be loaded.
  • Enforce Strong Authentication: Use MFA, secure session management, and robust password policies.
  • Regular Patching and Updates: keep frameworks, libraries, and servers up to date.
  • Security Testing and Audits: Conduct frequent vulnerability scans and manual penetration testing to identify and remediate flaws before they can be exploited by threat actors. Incorporate static and dynamic analysis, penetration testing, and vulnerability scanning.
  • Follow Established Frameworks: Leverage guidance from OWASP, including the OWASP Top 10.

Curious to learn more about dark web monitoring? Contact us.

Inside the Arabic Darknet: Cryptocurrency, Charities and What Investigators Need to Know

May 19, 2026

The intelligence community’s understanding of Arabic-language activity on the dark web has lagged significantly behind research focused on English-speaking environments.

A newly published, prestigious ‘Scopus Q1’ study is beginning to close that gap, and the findings carry direct operational implications for government investigators, law enforcement agencies, and cybersecurity analysts working the MENA (Middle East and North Africa) region and beyond.

The study is written by Dr. Mohammad Shadi Alhakeem, Assistant Professor of Cybersecurity & Digital Forensics, College of Forensic & Investigative Sciencesat the Naif Arab University for Security Sciences (NAUSS). This blog is based on peer-reviewed research published in IEEE Access: “Investigating Cryptocurrency-Enabled Illicit Activities on the Arabic Deep/Dark Web” by Prof Mohammad Shadi Alhakeem.

The Arab world’s digital footprint is enormous and growing fast. Internet penetration across the region has reached approximately 70%, with countries like Saudi Arabia exceeding 99%.

Meanwhile, the Middle East and North Africa ranked seventh globally in on-chain cryptocurrency value received in 2024 — roughly $338.7 billion in a single twelve-month period.

That’s not just economic activity.

It’s a substantial attack surface.

The combination of widespread internet access, high cryptocurrency adoption, and anonymizing technologies like the Tor network has created fertile conditions for illicit activity — much of it conducted in Arabic and largely invisible to investigators relying on English-language intelligence sources. This study is one of the first systematic efforts to document what’s actually happening in this space.

The researchers used DarkOwl Vision as the primary tool for identifying and analyzing Arabic-language content containing cryptocurrency addresses. DarkOwl Vision indexes one of the world’s largest databases of dark web content, spanning Tor, I2P, ZeroNet, Telegram, and Discord, without requiring investigators to directly access dangerous or illicit networks themselves.

Figure 1: Sample of a finding from the Arabic Darknet containing Monero Donation Address, Source: DarkOwl Vision

This matters operationally. Standard OSINT approaches often require analysts to navigate anonymization networks directly, exposing them to harmful content and operational risk.

DarkOwl automatically and anonymously indexes this content, sanitizes explicit material, and presents results in plain text — protecting the analyst while delivering the intelligence. Its filtering capabilities allowed the team to narrow more than 3.1 million initial results to actionable data by applying filters for language, cryptocurrency entity type, network source, and crawl timeframe.

From that starting pool — spanning July 2024 through June 2025 — the team identified 4,711 results containing cryptocurrency addresses. After de-duplication, that yielded 95 unique addresses tied to illicit activity, each analyzed for type, linked activity, source network, appearance frequency, and total funds received.

The resulting 95 addresses were classified across six categories:

Unverified Humanitarian Aid Solicitations (UHAS) — Campaigns soliciting cryptocurrency donations, primarily framed around aid to Gaza, with no affiliation to any recognized humanitarian organization. This category accounted for the largest number of unique addresses and the largest volume of funds received. More than 85% of all tracked payments — including one address that received approximately $50,000 — flowed to UHAS addresses, reflecting sophisticated exploitation of public sympathy.

Dark Web Marketplaces (DWM) — Platforms facilitating the trade of illicit goods, including drugs, within the Tor ecosystem.

Cyber Threat Actors (CTA) — Entities conducting malicious cyber operations, predominantly affiliated with pro-Iranian hacktivist groups including 313 Team and LulzSec.

Terrorism Financing (TF) — Activity directly linked to financing terrorism, with specific ties to ISIS. Despite representing fewer unique addresses, this category generated the highest frequency of appearances across DarkOwl’s dataset.

Child Sexual Abuse Material (CSAM) — Multilingual onion sites serving as platforms for uploading and distributing CSAM.

Dark Web Blogs and Forums (DBF) — A catch-all for political discussions, sexual content, and other material from onion sites outside the five primary categories.

One of the study’s most operationally significant findings is the behavioral distinction between actors using pseudonymous cryptocurrencies like Bitcoin (BTC) and Tether (USDT) versus those using privacy coins like Monero (XMR) and Zcash (ZEC).

BTC and USDT dominated by volume and appeared predominantly on Telegram.

Privacy coins were concentrated almost exclusively on Tor-based Onion sites.

The platform choice wasn’t random — threat actors are deliberately matching their anonymity tools, pairing privacy coins with the Tor network for maximum operational security.

For investigators, BTC and USDT transactions leave traceable blockchain records. Specialized tools like Crystal Expert, TRM Labs, and Chainalysis Reactor can analyze transaction histories, identify clustering patterns, and link addresses to real-world entities.

Monero and ZCash are a different problem entirely. Their cryptographic design obscures transaction details at the protocol level, and the study was unable to determine the volume of funds received by any privacy coin address. Given that these addresses are disproportionately linked to Terrorism Financing and CSAM, that blind spot is not a minor inconvenience — it’s a critical investigative gap.

None of the 95 addresses appeared on both Telegram and the Tor network. The platform separation was absolute — a clear sign of deliberate compartmentalization designed to prevent de-anonymization. These actors understand the forensic trail that cross-platform address reuse creates, and they’re avoiding it. Some Monero addresses had first appearances in DarkOwl’s dataset dating back to early 2022, indicating operations that have run continuously for years.

Telegram is where the volume is, but the Tor network is where the most serious crimes are concentrated.

Agencies with limited resources should weigh their coverage accordingly. Unverified humanitarian solicitations deserve coordinated public awareness efforts — the financial flows are substantial, and these campaigns risk eroding public trust in legitimate aid organizations. For terrorism financing and CSAM cases, traditional blockchain analysis won’t be sufficient where privacy coins are involved: acquiring darknet monitoring, forensic tools and building relationships with Virtual Asset Service Providers is essential.

This research was made possible through DarkOwl, and the capabilities it demonstrates aren’t limited to the research context — they’re what DarkOwl delivers to government agencies, law enforcement, and intelligence teams every day.

DarkOwl Vision’s combination of breadth across platforms, depth of historical data, and analyst safety makes it the tool of choice for exactly the kind of cross-platform, multilingual, cryptocurrency-focused investigations this study documents.

The Arabic dark web is no longer uncharted territory. Mapping it accurately — and keeping that map current — requires the right intelligence infrastructure. DarkOwl is where that work happens.


Curious to see more? Contact us.

Stolen, Weaponized, and Sold: Real Stories of Data Extortion Attacks

May 14, 2026

Data theft extortion, as the name suggests, occurs when a hacker unlawfully gains access to an organization’s sensitive data or systems and then demands payment in exchange for restoring access or halting the attack. More broadly, extortion encompasses any scenario in which a threat actor demands compensation to cease malicious activity.

Organizations can fall victim to these attacks in several ways, including data breaches, exploitation of system vulnerabilities, and social engineering tactics that deceive employees into granting unauthorized access. While companies continue to strengthen their defenses, attackers are simultaneously evolving their methods, often becoming more sophisticated and escalating their tactics.

This blog explores several well-known data theft extortion incidents, examining how they were carried out and how organizations responded.

In October 2020, hackers contacted 40,000 patients from the Finnish psychotherapy provider Vastaamo, demanding €200 in bitcoin within 24 hours, followed by €500 within an additional 48 hours, threatening to release their personally identifiable information (PII) and therapy records if they refused to pay. Prior to the emails, Vastaamo had refused to meet the hackers’ demand when they received a ransom of €450,000 in bitcoin. In the initial response, the hacker posted 300 patient transcripts in a public forum. Eventually, a 10-gigabyte data file appeared on dark web sites containing private notes between at least 2,000 patients and their therapists.

The information was obtained due to the company’s inadequate security practices. Sensitive data belonging to patients was not encrypted or anonymized. Records were first accessed in 2018, and the security flaws were not fixed until March 2019.

In October 2022, the National Bureau of Investigation identified the suspect in the breach as 25-year-old Aleksanteri Kivimäki. He was subsequently charged in absentia at the Helsinki District Court with multiple offenses, including aggravated data breach, attempted aggravated extortion, aggravated distribution of information violating private privacy, blackmail, breach of confidentiality, and falsification of evidence. He was eventually convicted and sentenced to six years in prison. The attack prompted the Finnish government to implement enhanced security measures to safeguard citizens’ data, while also providing support to victims and introducing new legislation addressing data theft and extortion.

In late 2024, the threat actor group Scattered Lapsus$ Hunters (SLH) gained access to corporate Salesforce data by using social engineering techniques, specifically vishing (voice phishing). Between March 2025 and June 2025 attackers gained access to Salesloft’s corporate GitHub account. Salesloft is a sales engagement platform featuring an AI chatbot, Drift, which integrates with Salesforce and other applications. After compromising the GitHub account, the attackers downloaded content from multiple repositories, created their own user within the organization, and established custom workflows.

On October 03, 2025,SLH launched a data leak Tor site extorting 39 companies that were impacted by the Salesforce breaches. The companies extorted in the link include Disney/Hulu, FedEx, Google, McDonald’s and more. A separate entry on the site requested that Salesforce pay a ransom to prevent impacted customers (approximately 1 billion records containing personal information) from being released. The group set an October 10 deadline for Salesforce to pay the ransom, or for potentially affected companies to contact the group to secure their data. Salesforce refused to negotiate with the threat actors, believing their threats were unsubstantiated and offered support to any of their affected clients.

While the group had threatened to release all information if their demands were not met, eventually they only leaked data from six companies. The victims included Albertsons, Engie Resources, Fujifilm, Gap, Qantas, and Vietnam Airlines. Qantas and Vietnam Airlines each had more than five million customer records exposed.

The automobile manufacturer, Jaguar Land Rover (JLC), disclosed in September 2025 that they had been victim to a cyberattack that “severely disrupted production activities”. The attack began on August 31 leading JLC to halt production the following day, and by September 22 the disruption had forced a complete shutdown of its production lines for three weeks, with employees instructed to remain at home.

The threat actor Scattered Lapsus$ Hunters (SLH) took responsibly for the attack via a Telegram channel. JLC has not released details on how the information was compromised, but SLH has typically used social engineering campaigns to attack its victims.

The type of extortion used by SLH has not been released to the public but eventually the UK Government had to step in and loan JLR £1.5 billion. Without the loan, the government claimed that people will be “laid off in the thousands”. Based on the latest financial results released by JLR, the cyberattack had a substantial impact on its profitability. The company reported a loss before tax and exceptional items of £485 million in Q2 and £134 million for the first half, compared with profits of £398 million and £1.1 billion, respectively, during the same period last year. The government later referenced the attack and loan when outlining reasons for the country’s weak GDP in Q3 2025.

Corporate executives experienced an extortion campaign following Oracle E-Business Suite’s (EBS) data breach. The ransomware group Clop sent emails to multiple executives claiming their data was stolen from Oracle’s EBS systems. In the email the group claims they successfully infiltrated the system and exfiltrated sensitive data. Their email begins with a blunt introduction, identifying themselves and suggesting the victim verify their reputation online.

The group goes on to state that they have copied “a lot of documents,” including private files and other confidential information, which they now claim to control. Rather than focusing on system disruption alone, the attackers emphasize data possession. The threat escalates if payment is refused. The group warns that stolen data will be distributed, either sold to other malicious actors or publicly released through their own channels, including blogs and torrent platforms. This dual-threat approach (financial loss combined with reputational damage) is a hallmark of modern ransomware campaigns.

Organizations affected by the attacks included Logitech, Harvard, Envoy Air, the United Kingdom’s National Health Service and The Washington Post. Clop is known for carrying out large-scale, carefully coordinated extortion campaigns that target organizations across multiple industries and regions, aiming to exploit vulnerabilities and extract data from many victims simultaneously rather than focusing on a single sector or location.

If your business was victim to a data breach or extortion incident, consider taking the following steps:

  1. Secure Operations
    Act quickly to contain the breach by securing systems, fixing vulnerabilities, locking affected physical areas, and mobilizing a response team with forensics, legal, and technical experts to investigate the cause and scope. Stop further data loss by taking affected equipment offline (without powering down), monitoring access points, replacing compromised systems if possible, and updating all credentials to prevent continued unauthorized access.
  2. Fix Vulnerabilities
    Work with forensic experts to assess the breach: check encryption, review backups and logs, identify who had and still has access, and limit it if unnecessary. Determine what data was compromised, how many people were affected, and whether you can contact them. Examine who (within and outside) your organization has access to information and examine if privileges need to be changed.
  3. Notify Appropriate Parties
    Determine legal requirements as some states have specific laws and regulations regarding who needs to be notified. Additionally, law enforcement can aid in the investigation process and should be notified shortly after initial discovery.

Curious how DarkOwl can help? Contact us.

Copyright © 2026 DarkOwl, LLC All rights reserved.
Privacy Policy
DarkOwl is a Denver-based company that provides the world’s largest index of darknet content and the tools to efficiently find leaked or otherwise compromised sensitive data. We shorten the timeframe to detection of compromised data on the darknet, empowering organizations to swiftly detect security gaps and mitigate damage prior to misuse of their data.